


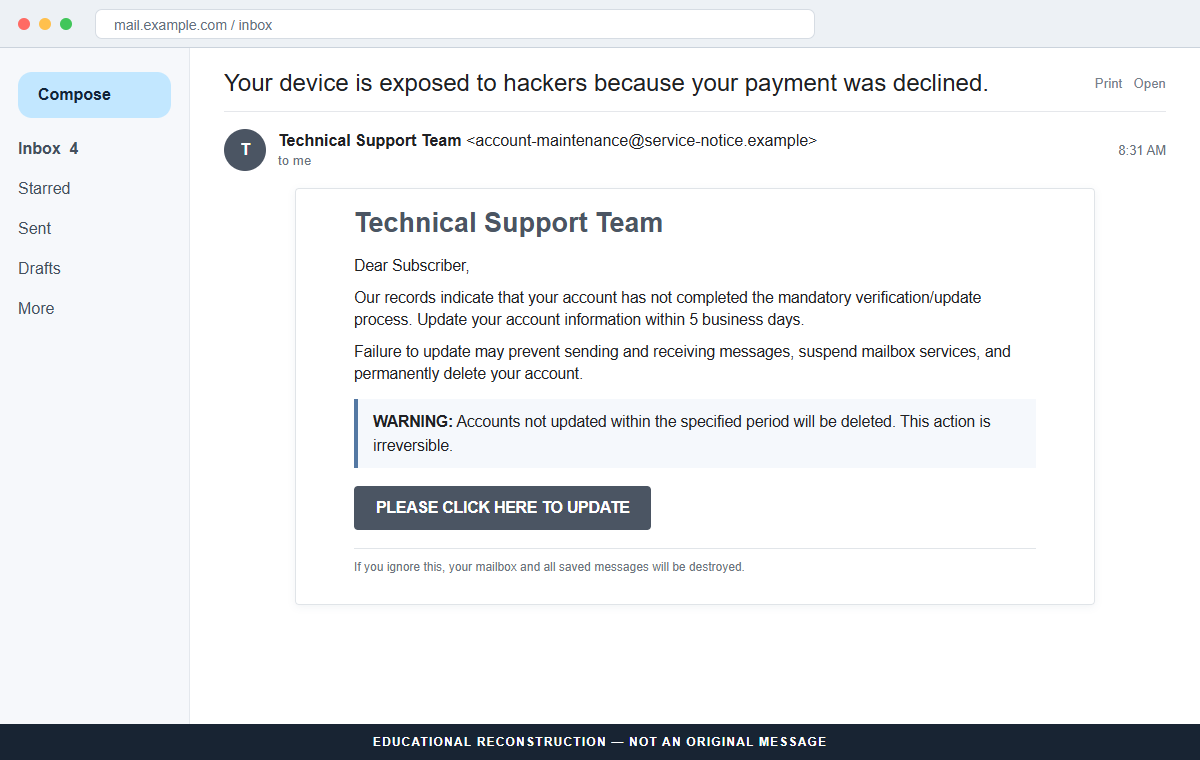
An alarming subject says your device is exposed to hackers because a payment was declined. Open the message, however, and the problem suddenly becomes an unfinished mailbox-verification process.
That contradiction is the first clue. The Mandatory Verification email scam uses a five-business-day deletion threat to drive recipients toward an adaptive fake login page where every submitted password goes to criminals.
Overview
The email combines two unrelated emergencies
The subject claims a declined payment has exposed the recipient's device to hackers. The body never explains that payment and instead says the email account has not completed a mandatory verification and update process.
This mismatch suggests that a subject from one campaign was paired with a body from another. The goal is emotional impact, not a coherent account notice that can be matched to a real provider event.
A five-day deadline threatens irreversible deletion
The recipient is told to update account information within five business days. Supposed consequences include losing the ability to send or receive messages, mailbox suspension, permanent deletion, and destruction of all stored messages.
The button says PLEASE CLICK HERE TO UPDATE. No specific provider, account policy, support case, storage limit, or independently verifiable administrator is identified before the recipient is asked to follow that route.
The destination adapts its fake login to the victim
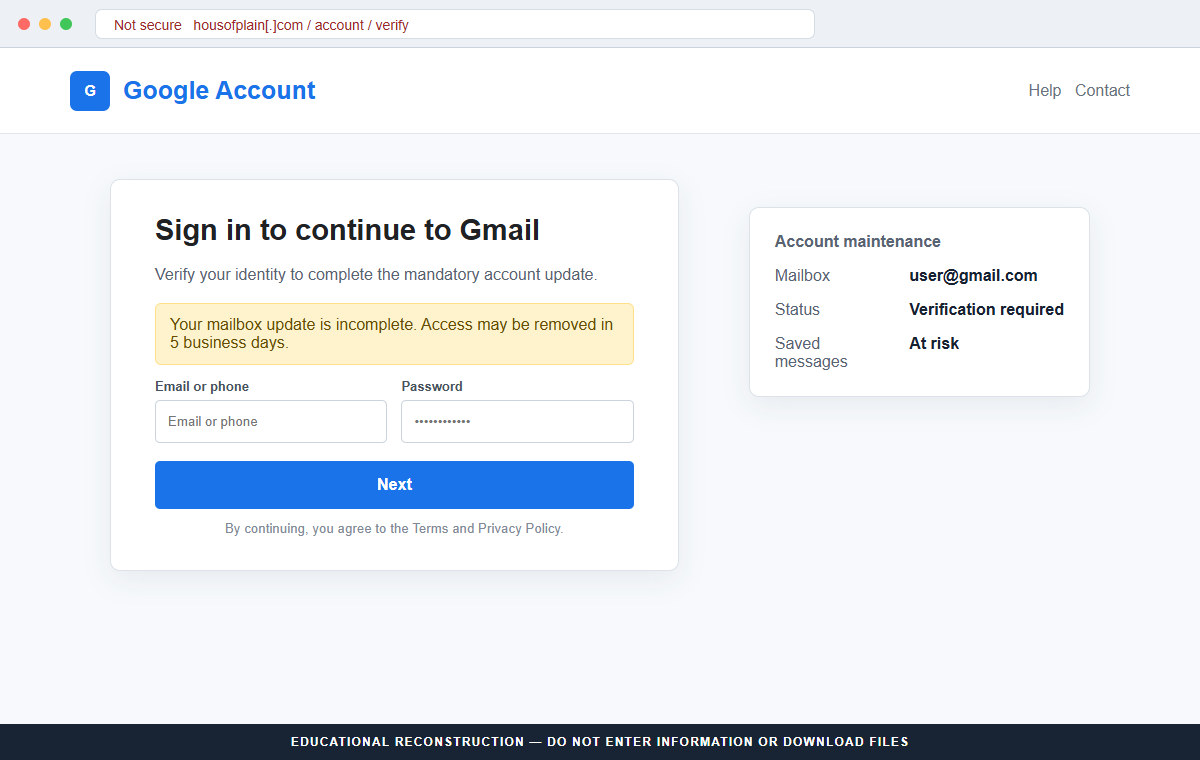
Analysis found that the link opened housofplain[.]com, where a fake Gmail form was overlaid on a Gmail-style sign-in page. The form requested an email address and password.
The phishing kit may change branding based on the address embedded in the link or entered by the visitor. Seeing the expected provider logo means the page selected a template, not that the provider authenticated the site.
- The payment and hacker warning in the subject does not match the body.
- A generic Technical Support Team claims verification is mandatory.
- The recipient receives only five business days to act.
- The message threatens suspension, deletion, and loss of saved mail.
- The update button opens housofplain[.]com rather than the email provider.
- The page can adapt its branding to Gmail or another service.
- Submitted credentials can be used for mailbox and account takeover.
Why the Contradictory Subject Is More Than a Typo
A legitimate security notice is generated from a defined event. Its subject, body, account, date, and recommended action should describe the same problem. A payment failure cannot logically become an email-verification deadline without any connecting explanation.
Mass campaigns are often assembled from reusable components. An attacker may rotate subjects to test which one gets more opens while leaving the same body and phishing link behind it.
The words hackers, declined, mandatory, irreversible, and destroyed cover several fears at once. Even if one claim feels irrelevant, another may persuade the recipient to click simply to learn what is happening.
Email accounts deserve caution because they act as recovery channels for banks, stores, social networks, cloud files, and workplace services. The scam uses the value of the mailbox to make an unexplained verification request feel urgent.
A real provider gives the user a route that begins inside its official account or help center. The provider does not need an unrelated website to collect the same password it already authenticates.
What the Fake Page and Google Guidance Establish
The campaign was analyzed on August 13, 2026 and classified as phishing. Its test page at housofplain[.]com collected an email address and password and had no connection with Google or another legitimate mail provider.
Google's phishing guidance says users should not enter a password after clicking a link in a message. A suspected Google security notice can be checked directly through the Google Account security-notifications page.
Google also recommends reviewing recent security events, devices, recovery information, forwarding rules, and unfamiliar account activity when a Gmail or Google Account may be compromised.
The FTC advises people to contact an organization through a website, application, or telephone number known to be genuine instead of using information in a suspicious message. That independent route breaks the attacker's control over the interaction.
A later version can replace the domain, deadline, subject, and provider logo. The stable evidence is the mismatched story, generic administrator, outside login, deletion threat, and request for credentials.
How the Mandatory Verification Email Scam Works
Step 1: A frightening subject wins the inbox click
The campaign begins with a warning that a declined payment exposed the device to hackers. It does not need to match the recipient's real account because fear encourages opening before analysis.
Sender names can resemble technical support, billing, or security teams. Display names are ordinary text and do not establish who sent the message.
Step 2: The body replaces the payment story with verification
After opening the email, the recipient learns that the supposed problem is an incomplete verification and update process. The earlier payment issue disappears completely.
This abrupt change is a useful detection clue. A real service would identify the transaction, account, security event, and precise policy that requires action.
Step 3: A five-business-day deadline threatens the mailbox
The email lists escalating consequences: blocked sending, blocked receiving, suspension, permanent deletion, and destruction of saved messages. The list is meant to make verification feel safer than waiting.
No genuine support case is supplied. The deadline exists only inside the message and should be checked against the official account reached separately.
Step 4: The update button moves the victim off the provider
The visible call-to-action hides a link to housofplain[.]com. Words such as update, secure, account, and login can appear in a path without changing who controls the registrable domain.
Redirects may briefly pass through other services. The final page requesting credentials still must belong to the correct provider.
Step 5: The phishing kit chooses familiar branding
The page can receive the email address in a URL parameter or request it first. It then loads a Gmail, Microsoft, cPanel, or other provider-themed form.
That adaptation reduces the visual mismatch that exposes generic phishing pages. It is a template decision made by the attacker, not proof of a live connection to the account.
Step 6: The password is sent to the criminal
When the victim submits the form, the credentials can be transmitted immediately. The page may show an error and ask again, which helps the criminal collect a corrected or alternate password.
A redirect to the genuine login page can follow. Because the real account still works, the victim may assume the update succeeded.
Step 7: The mailbox unlocks secondary attacks
A stolen password can expose private messages, recovery links, contacts, cloud files, and connected applications. Attackers may add forwarding rules or delete security alerts to maintain access.
They can also send phishing from the compromised account. Messages from a real contact are more persuasive, allowing one captured password to expand the campaign.
Company and Checkout Checks
The support team has no verifiable provider identity
“Technical Support Team” is a role, not a legal organization or account administrator. The email should identify the service, tenant, support case, and official route where the policy can be reviewed.
Contact the provider or workplace administrator through a saved bookmark, application, or known directory. Do not reply to the generic sender to ask whether it is genuine.
The sender and link domains must agree with the account
Expand the From and Reply-To fields, then inspect the final link destination. A Gmail-themed page on housofplain[.]com fails this check even if its layout is accurate.
Sender authentication can add evidence, but it is not a reason to ignore an unrelated login domain. Compromised mailboxes and forwarding services can still deliver phishing.
The official account is the source of truth
Open the provider independently and review security notices, subscription information, storage, recent events, and active sessions. A genuine restriction should appear in the account or be confirmable with its administrator.
If the official account shows no matching verification task, do not create one by entering credentials on the email's destination.
An adaptive login page is still an outside checkout
A page that knows the email provider may simply parse the text after the @ symbol. Logos, background images, progress indicators, and error messages can all be copied.
Treat the password field as a checkout for account access. If the registrable domain is wrong, the transaction fails before the password is entered.
Warning Signs to Check Before You Act
- A declined-payment subject has nothing to do with the message body.
- The sender identifies only as Technical Support Team.
- No provider, policy, case number, or account portal is clearly named.
- The email threatens irreversible deletion within five business days.
- The update button opens housofplain[.]com or another outside domain.
- A Gmail-style page appears on a site that is not Google.
- The form asks for the current mailbox password.
- An error invites the recipient to submit the credential again.
- The same message can display different provider branding.
- No matching warning exists in the official account.
The unmatched subject and body show that the notice is not describing one real account event. Do not let the deletion language repair that contradiction. Close the link and check the provider through an independently opened account.
What to Do if You Have Fallen Victim to This Scam
- Change the exposed mailbox password immediately. Use the provider's official app or a manually entered address on a trusted device. Create a unique password and update every service where the same or a similar password was used.
- Enable stronger multi-factor authentication. Choose a passkey, hardware security key, or authenticator app when available. Review existing methods and remove unknown devices, telephone numbers, recovery addresses, and app passwords.
- Revoke sessions and connected applications. Sign out unfamiliar devices and inspect OAuth access, legacy mail clients, browser sessions, and third-party applications. A password change may not invalidate every token already issued.
- Inspect forwarding rules and mailbox filters. Remove unknown forwarding addresses, delegates, filters, automatic replies, and rules that hide security notices. Review sent mail, trash, deleted messages, and account-recovery changes.
- Secure accounts that use this mailbox for recovery. Prioritize banking, payment services, cloud storage, shopping, social media, workplace tools, and the recovery email. Look for password resets or profile changes you did not initiate.
- Scan the device if the page downloaded anything. Run Malwarebytes or another trusted security scanner if a file, extension, or remote-support program was installed. Update the operating system and browser, then remove unfamiliar software.
- Add a blocking layer for future attempts. AdGuard or another reputable DNS and content blocker can prevent some known phishing pages and malicious advertisements from loading. New domains can appear before blocklists update, so continue checking addresses.
- Report the phishing message. Use the email provider's Report Phishing feature and notify a workplace or school security team. Preserve the full message and headers before deleting it, especially if several users received the campaign.
- Warn contacts if the account was used. Tell contacts through another channel that recent messages may be fraudulent. Ask them not to open links, share credentials, approve payments, or trust password-reset requests sent during the compromise window.
- Reject unsolicited recovery assistance. A caller or email sender who claims to restore the account for payment may be extending the scam. Work only through the provider, employer, bank, police, or a verified incident-response professional.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the Mandatory Verification email genuine?
No. The documented campaign uses a contradictory notice and a fake login on housofplain[.]com to steal email credentials.
Why does the subject mention a declined payment?
The subject appears unrelated to the verification body, likely because reusable scam components were combined. A genuine notice would describe one consistent account event.
Can an email provider require account verification?
Providers can request security actions, but the task should be visible inside the official account or confirmable with a known administrator. Do not use an outside login link.
How does the page know I use Gmail?
The link may contain your address, or the page may ask for it first. A phishing kit can use the domain to select Gmail-style branding automatically.
What if I clicked but entered nothing?
Close the page and report the message. If no file downloaded and no credential was submitted, account theft is less likely, but review browser downloads and security alerts.
What if I submitted the password twice?
Assume both entries were captured. Change the password, revoke sessions, enable stronger authentication, inspect forwarding rules, and secure connected accounts immediately.
The Bottom Line
The Mandatory Verification email scam does not survive a basic consistency check. Its subject describes a declined payment and exposed device, while its body invents an unrelated five-day mailbox-verification deadline.
The link to housofplain[.]com is not made safe by Gmail branding or an adaptive login form. Open the real provider independently and treat any password entered on the fake page as compromised.
Fast action can contain the damage. Change credentials, revoke access, inspect mailbox rules, protect recovery accounts, and report the campaign before the stolen inbox becomes the sender of the next scam.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.