


An unsolicited email offers to connect your business or project with carefully vetted lenders around the world. The sender sounds professional, asks for a business plan, and promises competitive low-interest financing.
For someone searching for capital, the message can feel like a lucky introduction. It may instead be the beginning of identity theft or an advance-fee loan scam.
Overview
The email uses a polished business funding pitch
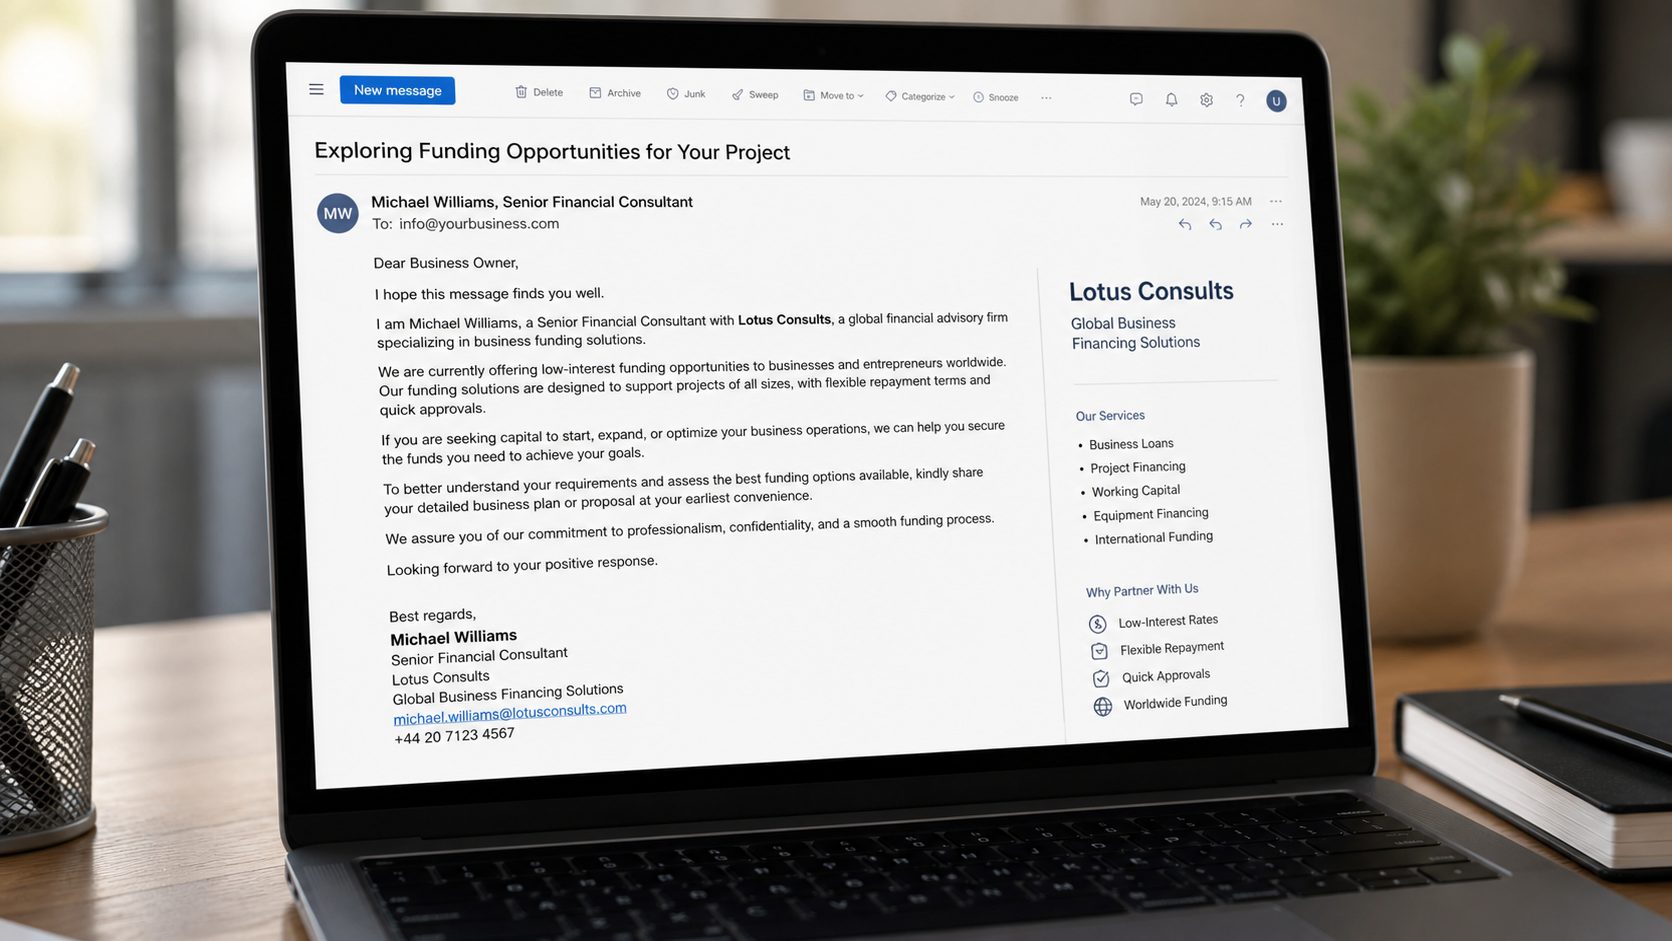
The Michael Williams Lotus Consults scam email claims to come from a “Senior Financial Consultant.” One reported version uses michael.williams@lotusconsults.org and the subject “Exploring Funding Opportunities for Your Project.”
The message says Lotus Consults connects high-caliber clients with vetted lenders and offers financing for personal, business, and project needs. It invites the recipient to send a business plan and executive summary.
The language is broad enough to fit almost any entrepreneur. It contains no meaningful evidence that the sender reviewed the recipient, project, credit, revenue, or repayment ability before making contact.
The requested documents contain valuable intelligence
A business plan may reveal names, addresses, telephone numbers, signatures, bank relationships, revenue, customers, intellectual property, budgets, and future transactions. That information can support targeted fraud even before money is requested.
Warning signs include:
- An unsolicited offer of worldwide low-interest financing
- No clear explanation of how the sender found your project
- A generic consultant title without verifiable licensing
- A request for confidential plans before basic due diligence
- No specific lender, legal entity, address, or credit terms
- Promises that appear stronger than the underwriting performed
- Fees requested before any real funding is delivered
The offer can develop into an advance-fee scheme
After receiving a response, the supposed consultant may promise approval and introduce processing, insurance, legal, compliance, transfer, or registration fees. Each charge is presented as the last obstacle before release of a much larger loan.
The lender and financing do not exist. The victim loses the fees, while submitted documents may be reused for impersonation, business-email compromise, fake invoices, or new credit applications.
Do not reply or send documents. Verify the company, lender, registration, domain, address, and representative through sources that the email did not provide.
What the Reported Email Says
The message identifies “Michael Williams” as a Senior Financial Consultant at Lotus Consults. It says the organization specializes in connecting clients with vetted lenders worldwide.
It offers competitive low-interest solutions tailored to projects and asks the recipient to share a business plan and executive summary. The promise remains vague about loan size, annual rate, collateral, jurisdiction, repayment, and the actual lender.
A professional tone does not verify the sender. Names can be invented or copied, domains can be registered quickly, and financial terminology can be taken from genuine consultancy websites.
The reported email address should not be trusted simply because the local part contains the sender’s name. The important questions are whether the legal business exists, whether the domain belongs to it, and whether the person is authorized.
How the Michael Williams Lotus Consults Scam Email Works
Step 1: Bulk outreach finds businesses that need funding
The email may be sent to addresses collected from company websites, directories, registrations, conference lists, social media, and breached databases. A recipient’s business name can be inserted automatically.
Criminals do not need to know who currently needs a loan. Sending enough offers eventually reaches someone preparing a launch, managing cash flow, or seeking investors.
Step 2: Formal language creates an image of selectivity
Terms such as “high-caliber clients,” “carefully vetted lenders,” and “funded realities” imply an established network. The recipient is invited to believe the project may qualify for privileged access.
No evidence of selection is supplied. The same template can be delivered to thousands of unrelated recipients.
Step 3: The victim sends a business plan
The first request may not involve payment. Asking for familiar business documents lowers suspicion and gives the fraudster detailed information for the next message.
The scammer can quote revenue, milestones, and names from the plan to make a fabricated approval look personally reviewed.
Step 4: A lender or investor appears
A second person may contact the victim as an underwriter, legal officer, bank representative, or private investor. Multiple participants make the transaction feel as though it passed through real departments.
Websites, letters of intent, approval certificates, and account statements may be created to support the story. None replaces verification with a regulator and the supposed institution.
Step 5: Approval is granted unusually quickly
The project is accepted with little challenge, sometimes for an amount larger than requested. The favorable terms encourage the victim to focus on closing rather than question how risk was assessed.
Legitimate lenders examine identity, credit, cash flow, collateral, business history, and legal documents. A guaranteed approval before this process is a serious warning.
Step 6: An advance fee blocks release of the funds
The supposed loan cannot be transferred until the victim pays for insurance, processing, taxes, compliance, legal review, or an international transfer. Payment may be requested by wire, crypto, or to an unrelated company.
Once paid, another issue appears. The promised funding remains visible in fake paperwork but never reaches the victim’s usable account.
Step 7: Stolen documents support additional fraud
Business and identity records can be sold or reused. Criminals may impersonate the company, target its customers, redirect legitimate invoices, or approach employees with convincing internal details.
The victim may later receive a recovery offer that requests another fee. Knowledge of the original application makes the second approach sound credible.
How to Verify a Business Funding Offer
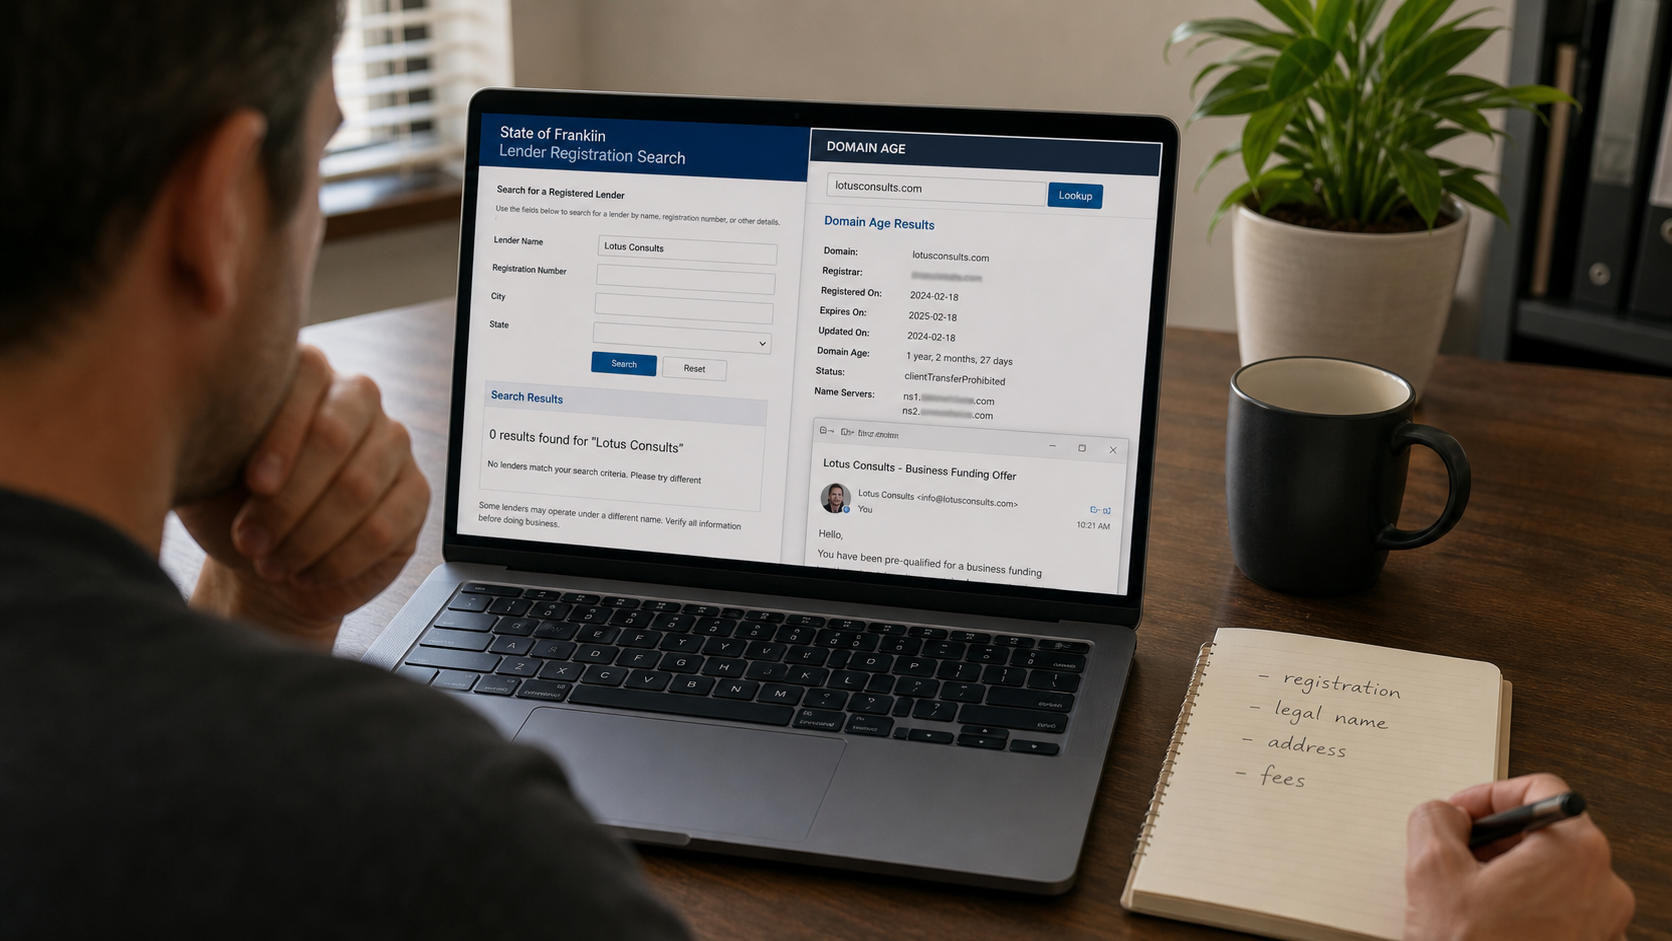
Ask for the lender’s full legal name, physical address, registration number, lending jurisdiction, written terms, and the identity of the entity that will provide funds. Do not accept a consultant’s own website as the only confirmation.
Check the lender with the banking or financial-services regulator in the relevant state or country. The FTC advises borrowers to confirm that a lender is registered where it does business.
Contact the institution using a number in the regulator’s record. A fraudster may copy a real lender’s name, so confirming that the exact representative, domain, and offer are authorized is essential.
Have an independent attorney or accountant review the documents. The consultant should not choose or control the professional who evaluates the deal.
Why You Should Not Send a Business Plan Yet
An executive summary can contain enough detail for social engineering. Remove personal identifiers, account information, signatures, customer lists, and confidential technology before sharing even with a verified contact.
Use a staged disclosure process. A legitimate funder can explain its identity, mandate, privacy practices, and initial requirements before receiving the most sensitive documents.
Mark confidential material, control access, and record who received each version. If the offer arrived without a prior relationship, verify it before opening attachments or replying.
Tell employees about the contact. A scammer who knows the project may email finance staff later and request a payment while impersonating an executive.
Documents a Fake Funder May Send
A letter of intent can look formal while making no enforceable commitment. Check the legal name, governing law, signatory, lender registration, and contact channel before relying on it.
An approval certificate may include stamps, seals, reference numbers, and signatures. These visual details can be created in ordinary editing software and do not prove underwriting occurred.
A bank statement or proof-of-funds letter may be altered or entirely fabricated. Verify it with the named institution through a channel you locate independently.
Insurance documents can introduce another impersonated company. Contact the insurer and regulator directly, and confirm the policy number, insured parties, and payment instructions.
A confidentiality agreement may be used to discourage discussion with lawyers, banks, or employees. Confidentiality does not prevent a recipient from obtaining independent professional advice about a proposed transaction.
International transfer forms often create a reason for taxes or clearance charges. A displayed transfer pending in a portal controlled by the sender is not available funding.
Never judge a financing package by the number of documents. A coordinated fraud can produce an entire file in which every company, official, and signature is controlled by the same group.
How to Protect Your Company After Sending a Plan
Tell finance, legal, leadership, and information-security teams what was disclosed. A shared timeline helps the company recognize later messages that reuse the project’s details.
Notify customers or partners only when their information is affected and follow applicable legal advice. Do not let embarrassment delay a measured incident response.
Add verification requirements for changes to invoices, bank accounts, and executive payment requests. Use a known telephone number rather than replying to the suspicious thread.
Monitor newly registered domains resembling the company name when exposure is serious. Criminals may use copied documents to create a convincing supplier or investor impersonation.
Review bank-account changes and large outbound payments with a second person for the following months. Information stolen today may be saved until a believable project milestone creates the right moment for fraud.
Keep the original email in a protected evidence folder rather than forwarding it widely. Security staff can preserve headers without exposing more employees to attachments and links.
One extra word is not enough protection, but one independent telephone call can expose an entire fabricated financing operation.
Company, Address, and Fulfillment Checks
The legal entity must exist in the claimed jurisdiction
Search official business registries and financial regulators. A similar name is not enough; compare registration numbers, officers, status, and permitted activities.
The domain should belong to the verified company
Compare the email domain with the address in official records. Lookalike spelling, recent registration, hidden ownership, and unrelated infrastructure deserve caution.
The physical office needs independent confirmation
A prestigious address may be a virtual office or copied from another firm. Contact building management or the verified institution without using details in the email.
The actual funding path must be documented
Identify which regulated entity supplies the money and where fees go. Do not wire funds to individuals, intermediaries, or unrelated companies.
What a Legitimate Lender Does Differently
A real lender explains costs and underwriting rather than guaranteeing approval. It provides written disclosures, verifies the borrower, and answers questions about regulation and complaints.
Some legitimate applications include appraisal or application costs, but paying a fee never guarantees credit. The FTC warns that a demand for payment before promised funds is a central advance-fee scam sign.
- Terms identify the legal lender and borrower
- Interest, fees, repayment, and collateral are clear
- The lender checks credit and repayment ability
- Payments go to verified business accounts
- The borrower can obtain independent advice
- Questions do not trigger threats or artificial deadlines
Walk away when the promised loan exists only in emails, certificates, or a dashboard controlled by the sender.
What to Do if You Have Fallen Victim to This Scam
- Stop all communication and payments. Do not send a final insurance, tax, processing, or release fee.
- Contact the bank or payment provider. Report fraud and ask whether a wire, card charge, transfer, or crypto purchase can be stopped or traced.
- Preserve the entire offer. Save emails with headers, attachments, domains, telephone numbers, contracts, recipient accounts, wallet addresses, and transaction records.
- Assess the disclosed business information. List every person, account, customer, signature, document, and confidential detail exposed, then notify affected teams.
- Secure email and financial systems. Change passwords, enable strong two-factor authentication, inspect forwarding rules, and alert staff to possible invoice impersonation.
- Scan devices that opened attachments. Use Malwarebytes to check for credential stealers, remote-access tools, and other malware delivered with the funding documents.
- Block malicious domains. AdGuard can reduce access to reported phishing sites and deceptive redirects, but it cannot recover documents already shared.
- Report the scheme. File at ReportFraud.ftc.gov and IC3.gov, and notify financial regulators and local police when money was lost.
- Reject recovery solicitations. An unexpected person promising guaranteed reimbursement for another fee is likely continuing the fraud.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Michael Williams a real financial consultant?
The name in an unsolicited email does not verify a person. Confirm identity, authorization, and licensing through official records and independently obtained company contacts.
Is lotusconsults.org a verified lender website?
Do not assume that it is because the address appears professional. Verify the legal entity, registration, domain ownership, and lender behind the offer before interacting.
Why does the sender want my business plan?
The information can personalize a false approval and support identity theft, invoice fraud, or attacks against employees and customers.
Are all upfront loan fees illegal?
Some legitimate applications have disclosed costs, but no fee guarantees approval. Unexpected demands to release promised funds are a strong scam warning.
What if I replied but sent no documents?
Stop contact and expect follow-up attempts. The sender now knows your address is active and may tailor a second offer to your response.
What if I opened an attachment?
Do not enable macros or install software. Scan the device, change exposed passwords from a trusted system, and monitor email and financial accounts.
The Bottom Line
The Michael Williams Lotus Consults email uses an attractive funding story to obtain business information and open the door to advance fees. Professional wording is not evidence of a real lender.
Do not reply or send a business plan until the legal company, representative, lender, domain, and payment path have been confirmed independently.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.