


An email says your Shopify account is frozen just as you are trying to keep orders moving. A payment update suddenly seems urgent.
Before reaching for a card, check whether the notice matches what is happening inside your actual store account.
Overview
The message makes a business interruption feel immediate
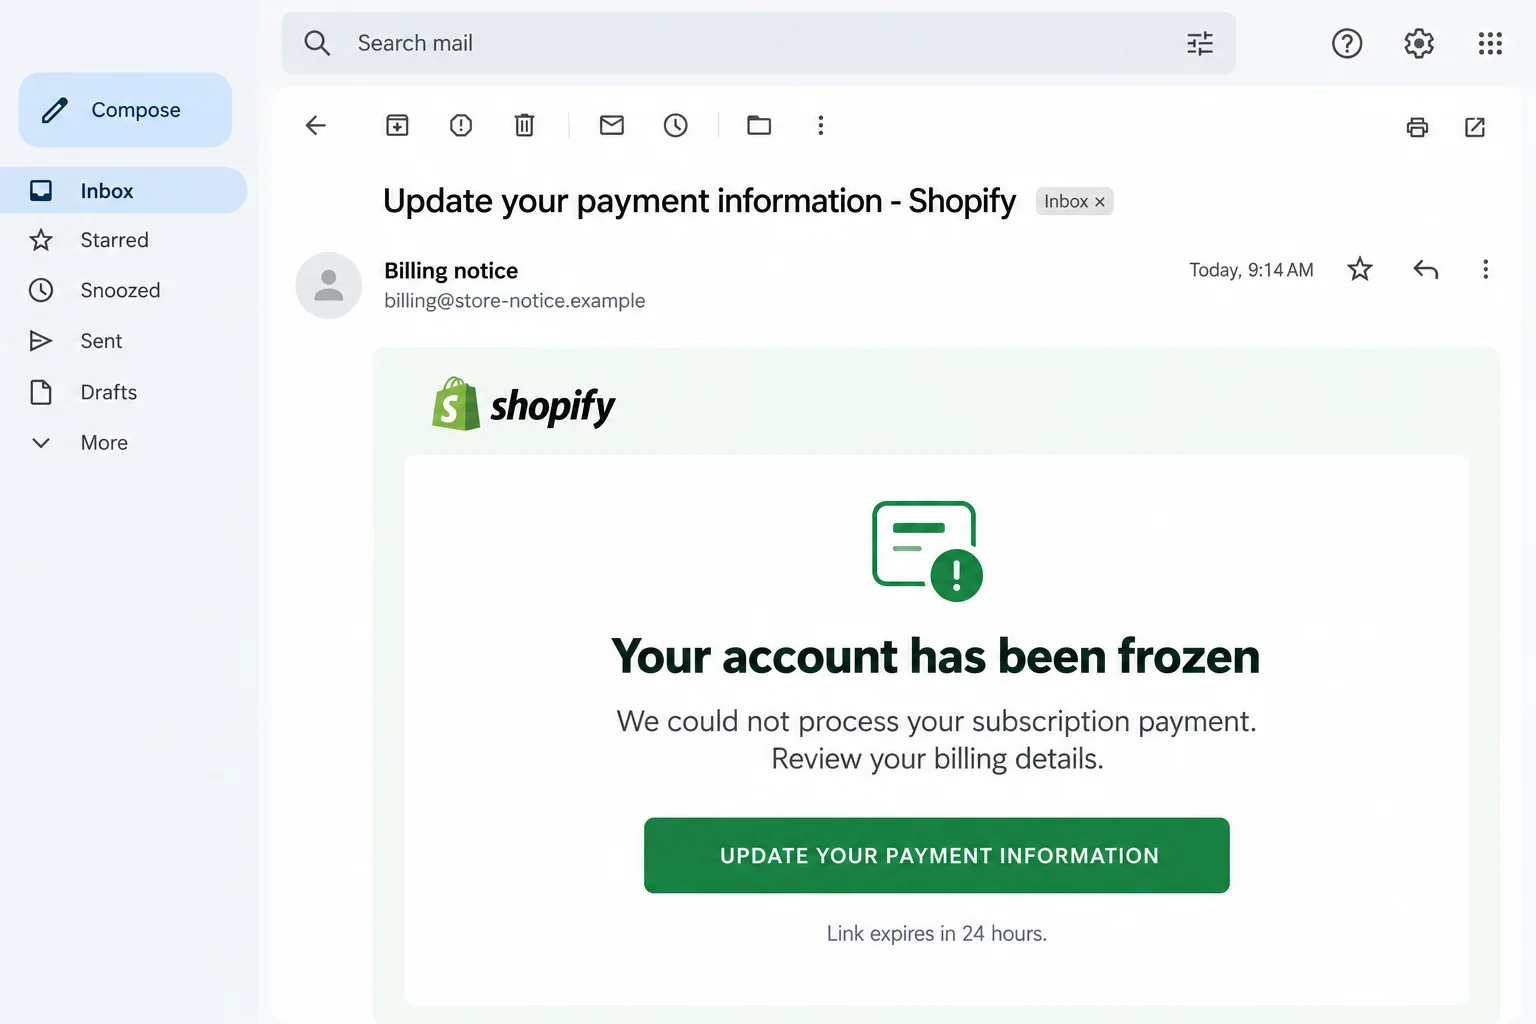
The reported phishing email claimed that repeated subscription payment failures had frozen the recipient’s Shopify account. It suggested that products and store access were affected.
Its requested solution was a payment-information update through an emailed button, with a 24-hour expiration adding pressure to act.
That story targets a merchant’s understandable fear of lost sales. When orders, customers, and advertising are involved, a billing warning can feel difficult to postpone.
A real billing problem does not authenticate this email
Shopify can genuinely freeze a store because of unpaid charges. The existence of that policy makes the impersonation more believable, not more trustworthy.
Before treating a notice as an instruction, compare these details:
- Does the billing issue appear when you open Shopify admin independently?
- Can the store owner or an authorized billing user verify the outstanding charge?
- Does the message identify a store and account you actually manage?
- Are you being asked to enter information at an independently confirmed destination?
The answer should come from your account and established support channels. A button in an unsolicited email should not determine where you enter credentials or card details.
The landing page’s exact behavior remains unconfirmed
The reported email’s destination was unavailable during its analysis. A credential-harvesting page was suspected, but its exact forms and subsequent actions were not established.
Do not assume this particular version displayed a verified card form or stole a session. Those possibilities require separate evidence from an actual interaction.
The image above is a fictional email illustration with sample sender details. It shows the billing-pressure setup without presenting an invented landing page as evidence.
How the Shopify Account Frozen Email Scam Works
Step 1: The notice arrives as an apparently routine billing task
The subject presents the message as a payment-information update associated with Shopify. That sounds administrative, something a busy merchant might normally handle without much discussion.
Instead of beginning with an extravagant promise, the email begins with a problem that could plausibly occur. Cards expire, banks decline charges, and subscriptions need attention.
The danger is treating plausibility as proof. A genuine reason for a company to contact merchants does not establish that this sender represents that company.
Consider who normally manages billing for your store. A message reaching another staff member may be using the brand name to bypass the person who knows the account.
Step 2: The supposed failed payments become a threat to store access
The reported version referred to three unsuccessful payment attempts and claimed that the account had already been frozen. That moves the issue from routine maintenance to business disruption.
A merchant may start thinking about abandoned purchases, delayed orders, or wasted advertising spend. Those concerns can crowd out a slower check of the sender.
But the email itself cannot establish your store’s status. Open your usual admin route and inspect the account rather than accepting the message’s diagnosis.
If the store is operating normally and no corresponding billing issue appears, do not create a payment problem by entering details into the emailed route.
If there is a genuine outstanding bill, resolve that bill from the real account. A coincidental real issue does not make an unsolicited payment button safe.
Step 3: A short expiration window discourages independent checking
The email gives its link a limited lifetime. A 24-hour window can make verification feel like a luxury you should skip until the store is restored.
That reverses the sensible order. You need to establish who is asking before deciding whether their deadline matters.
Do not confuse an emailed link’s expiration with a verified billing deadline. The sender controls what the message says about its own button.
If several people manage the business, tell them you are checking the notice. Otherwise, a second person may act on the same email while you investigate.
A short internal message can prevent that: identify the subject, ask staff not to use its link, and name the person verifying billing through admin.
Step 4: The payment button shifts the decision to an outside destination
The button asks the recipient to update payment information. Its wording makes clicking seem like the final administrative step rather than a new trust decision.
What matters is where the browser goes and who receives any information entered there. The visible button label cannot answer either question.
In this case, the unavailable destination limits conclusions about its exact payload. It is still unsafe to follow an unverified payment route under an impersonated billing warning.
A counterfeit destination could ask for a password, card data, or another account action. Respond according to what you actually supplied, not a generic worst-case story.
Do not test the destination with real credentials to see whether it works. Even a page that returns an error may have received submitted information.
Step 5: Any exposed access can create a wider store incident
A stolen merchant login may matter beyond the account’s next subscription bill. Depending on permissions, an intruder could reach business settings or sensitive operational information.
That does not mean every successful login exposes every store feature. The actual user’s role and the account’s protections determine the scope.
The practical response is to involve the store owner early. They can coordinate access review, contact support, and stop several staff members from making contradictory changes.
If card details were entered, the card issuer also needs to know. Securing a Shopify password and protecting a payment card are separate tasks.
A normal-looking store after the event is reassuring but incomplete. Check account changes and account access instead of relying only on the storefront’s appearance.
How to Verify a Genuine Shopify Billing Notice
Use admin as the source of billing truth
Shopify’s frozen-store guidance explains the genuine unpaid-billing process. Check it through the help center rather than a contact supplied by the suspicious email.
The store owner, or a user with the appropriate billing permission, should examine the relevant bill. A staff member without that access should escalate internally.
Write down what admin actually shows: the bill, its status, and any notice associated with it. Compare those details with the email without using its button.
If the account cannot be accessed, reach Shopify support through an independently opened official channel. Do not hire a recovery specialist promoted in replies to your complaint.
Sender checks require more than one familiar word
Inspect the full sender details, not just a display name saying Shopify. A copied name or logo is easy to place in a message.
However, do not invent a rule that every legitimate Shopify message must have exactly the same domain. Providers may use documented sending and routing services.
Shopify’s phishing guidance lists legitimate examples and reporting advice. Use that reference instead of guesses based on a screenshot alone.
Even a plausible sender should not replace checking the actual account. Mail can be forwarded, accounts can be compromised, and familiar presentation can be misleading.
Keep billing decisions away from customer-facing pressure
A merchant worried about orders may be tempted to fix anything quickly. Set a simple internal rule: unexpected billing changes are verified by the owner first.
Keep approved support contacts and the usual admin route available to staff. This reduces the temptation to use the fastest phone number or link in an alarming message.
Do not announce a customer-data breach merely because a suspicious email arrived. Establish whether access occurred, then follow the appropriate incident process if information was exposed.
What to Do If You Responded to the Shopify Email
Stop using the emailed payment route. Save the message and tell the store owner whether you clicked, entered a password, supplied a card, or approved anything.
If you only read it, report it as phishing and verify billing normally. Receiving a frozen-account warning does not itself compromise the store.
If a page opened, record its address from existing browser history where safe. Avoid revisiting it just to take another look.
Secure any login information entered outside the verified service. Change the affected password through Shopify’s normal account process on a trusted device.
Replace reused passwords on other affected accounts, especially the email account controlling recovery. Review available sign-in protections and strengthen them where appropriate.
If you approved an unexpected authentication request, tell support that detail. A password-only response may not describe the whole exposure.
Have the owner coordinate an account review. Inspect access, users, and material store changes using official account controls and support guidance.
Focus on settings the exposed account could reach, including billing or payout-related information where applicable. Preserve suspicious changes before correcting them.
Do not remove legitimate collaborators at random. Record which access is unrecognized and ask Shopify support for help if ownership or access is disputed.
Contact the card issuer if payment details were submitted. Explain that the details went to a suspected impersonation page rather than an authenticated Shopify billing screen.
Ask whether the card should be locked or replaced and how to dispute any unauthorized charge. Keep the case reference and follow the issuer’s instructions.
A card replacement does not secure a merchant login. Complete both responses if both credentials and payment information were disclosed.
Report the message through the proper channels. Shopify identifies phishing@shopify.com for suspicious-message reports. Preserve the original email where possible so technical details remain available.
Your workplace may have a separate security-reporting process. Use it too, particularly if the message reached shared billing or support mailboxes.
Include a short factual timeline. Do not send account passwords, authentication codes, customer exports, or full payment-card details as evidence.
Check for software or browser changes if you followed extra instructions. A downloaded helper or newly installed extension creates a different concern from a billing email alone.
Malwarebytes can help investigate malicious software. For a managed business computer, involve IT before making changes that could destroy useful incident evidence.
AdGuard may reduce some malicious-ad and redirect exposure. It cannot restore store ownership, reverse a card charge, or replace checking your actual Shopify account.
Watch for a second approach pretending to fix the first. Recovery messages may claim that your frozen store needs a fee paid outside Shopify.
Do not share admin access or authentication codes with someone who contacts you unexpectedly. Continue only through support conversations you initiated from verified channels.
Tell other administrators when the incident is contained. Clear communication prevents a later copy of the same warning from restarting the problem.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
When a Real Bill and a Fake Email Arrive Together
A genuine billing problem can coexist with a phishing message. Attackers do not need perfect timing to reach someone whose card has recently changed.
Handle the two issues separately. Pay a verified outstanding bill through admin, and report the unrelated impersonation without following its requested route.
Keep the real receipt and the suspicious email in different records. Otherwise, a legitimate payment confirmation may later be mistaken for proof that the phishing link was safe.
If you are unsure which account a notice concerns, check all stores you actually manage through your usual account. Do not create a new login through the notice.
For agencies, identify the merchant responsible for the store before changing billing. A convincing email should not shortcut the normal agreement about who can authorize payments.
Once the issue is resolved, explain the specific lesson to staff: the store’s real billing state matters more than the urgency of a message about it.
Frequently Asked Questions
Can Shopify genuinely freeze a store over unpaid bills?
Yes. A real unpaid-billing process exists. Confirm the situation inside the account rather than treating that fact as authentication for this email.
Does the 24-hour link expiration prove the notice is real?
No. The sender can put an expiration claim in the message. Verify any actual billing obligation through admin or independently reached official support.
Was a fake credit-card form confirmed for this version?
No. The reported destination was unavailable, so its exact fields were unconfirmed. Treat any information you actually entered as the basis for your response.
What if my store really is inaccessible?
Use Shopify’s established support and account-recovery routes. A real access problem still does not make an unsolicited email’s payment destination trustworthy.
Should I change my password after merely reading the email?
Reading the notice alone does not establish credential theft. Change exposed credentials if you entered them elsewhere or have another concrete reason to suspect compromise.
Is this a warning against using Shopify itself?
No. The issue is a billing impersonation targeting merchants. Verify and resolve real Shopify charges through the genuine service, not the suspicious message.
The Bottom Line
Do not update payment information through this frozen-account email. Check the store’s billing state in Shopify admin and resolve any genuine issue there.
If you already supplied information, secure the exposed login or card and involve the store owner. A rushed payment should not become a wider business incident.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.