Advanced Plus Security  (From forum thread)dronefox1166's PC Security Config

Current configurationWindows 11
Version 1Updated
74 replies

Copied from dronefox1166's forum thread – not yet confirmed as current by the owner

Detailed suggestions and alternatives welcome
Staff assessment Advanced Plus Security· From forum thread

Taken from the forum thread's label. The reviewer and date were not recorded, and staff have not re-checked it against the current setup.

Device & operating system

, 4 answers
Operating system
Windows 11
OS version and support details
Home x64
Main use of this computer
For home and private use
Usage and exposure
Visiting familiar websites, Visiting unknown or untrusted websites, Working from home, Making audio/video calls, Opening email attachments, Online shopping and card payments, Logging into my bank account, Downloading software and files from reputable sites, Requesting and accepting remote access, Gaming, Streaming audio/video content from trusted sites or paid subscriptions, Streaming from untrusted sites, Coding and development

Protection & updates

, 13 answers
Real-time protection
Windows Defender + simplewall portable + ConfigureDefender + FirewallHardening
Device firewall
Microsoft Defender Firewall with Advanced Security
On-device encryption
Not applicable
Device sign-in security
Windows Hello PIN or biometric sign-in (face / fingerprint / Touch ID)
Security updates
Allow security updates and latest features
Update channels
Allow stable updates only
User Account Control (UAC)
Notify me only when programs try to make changes to my computer (do not dim my desktop)
Smart App Control
On
Network firewall
Enabled
Custom security settings
Windows Defender + Safing Portmaster + H_C (no agressive)
---
WIN 11 privacy tweak :
- BloatyNosy
- ChrisTitus Tech
main telemetry off
Periodic malware scanners
- Malwarebytes
Malware sample testing
I do not participate in malware testing
Environment for malware testing
/

Browsing, accounts & privacy

, 4 answers
Browsers and extensions
Firefox, Chrome, Brave, Ungoogled Chromium (used), Edge, Ungoogled Chromium (not use for the moment) :

search : Duckduckgo

extensions FF : uBlock Origin, Decentreleyes, Language Tool, Bitwarden, Keepa, Fakespot (for Amazon), h264ify (for Youtube), IDM extension, DarkReader, BetterRYM, cat-catch, AutoTabDiscard
Secure DNS
NextDNS (into Portmaster)
Desktop VPN
/
Password and passkey manager
Bitwarden (2FA authentification)

Backup & recovery

, 2 answers
File and photo backups
"Synology DS720+" NAS and cloud like 'MEGA(.nz)", "Amazon Photos" (unlimited with "Prime"), "OneDrive", "Google drive", "Proton drive", "MEGA.nz", "KDrive", "Filen", "Twake", "pcloud"...
System recovery
N/A

Apps, specs & notes

, 5 answers
Maintenance tools
BleachIt, PatchMyPC, Windows Repair Toolbox, HiBit Uninstaller portable + UniGetUI
Subscriptions
None
Computer specs
Motherboard : msi-b550m-pro-vdh-wifi-micro-atx-am4-motherboard
CPU model : amd-ryzen-5-5600g-39-ghz-6-core-processor
GPU model : to CPU
RAM :
G.Skill Flare X Black (2x8 GB) DDR4-3200 CL16 Memory
storage : 1 Tb SAMSUNG 990 EVO Plus (Win 11 system)
1 Tb HDD 2,5' WD (storage)
1 Tb SSD M.2 CRUCIAL P3 Plus (Storage)
Notable changes
add some changes

VT4Browser, Shoptimate... extension ...

UAC minimum notify

HiBit Uninstaller portable

06/2022 : new material and Win 11

12/2022 : new NAS DS720+

04/2023 : Portmaster free​


09/2023 : AdGuard Home

10/2023 : custom security : Hard_Configurator

12/2023 : Kaspersky Free, ScreenWings add to security software, BloatyNoisy, Windhawk, Wireguard, DefenderUI...
+ new materiel : SSD 1 Tb Crucial P3 Plus, WIngetUI

01/2024 : HitmanPro Alert

01/2024 : Malwarebytes anti exploit and uninstalled HitmanPro Alert

11/01/2024 : MB anti ransomware + OSArmor 1.4.3 replace HitmanPro Alert and MB anti exploit...

10/02/2024 : removed osarmor and mb premium
add SpyShelter Pro

07/2024 : remove SpyShelter, remove AdGuard Home

11/2024 : NextDNS and H_C removed (only ConfigureDefender and FirewallHardening from H_c tools)

- Fort Firewall and HostsMan

- Office 365

12/2024 : AdGuard DNS, PrivaZer Pro...

01/2025 : NextDNS

03/2025 : Portmaster add and Fort Firewall removed

06/2025 : Fort Firewall, SimpleWindowsHardening added

06/2025 : Fort Firewall removed, simplewall portable added

02/2026 : Add Portmaster, remove Office 365,
Feedback preference
Detailed suggestions and alternatives welcome
Community rating

Community rating

How members rate the shared configuration. This is community feedback, not a security test.

Not rated yet
An open invitation for useful feedback.

Sign in to rate this setup

Go to discussion

Copied from the member's forum thread. This is a configuration record, not a device scan.

One of 211 member setups in the Security Setup Hub. Browse setupsGet yours checked

Original discussion fields (as posted in the thread)
Thread details
Last updated
Jun 9, 2025
Main use of this computer
For home and private use
Operating system
Windows 11
OS version and support details
Home x64
On-device encryption
Not applicable
Device sign-in security
    • Windows Hello PIN or biometric sign-in (face / fingerprint / Touch ID)
Security updates
Allow security updates and latest features
Update channels
Allow stable updates only
User Account Control (UAC)
Notify me only when programs try to make changes to my computer (do not dim my desktop)
Smart App Control
On
Network firewall
Enabled
Real-time protection
Windows Defender + simplewall portable + ConfigureDefender + FirewallHardening
Device firewall
Microsoft Defender Firewall with Advanced Security
Custom security settings
Windows Defender + Safing Portmaster + H_C (no agressive)
---
WIN 11 privacy tweak :
- BloatyNosy
- ChrisTitus Tech
main telemetry off
Periodic malware scanners
- Malwarebytes
Malware sample testing
I do not participate in malware testing
Environment for malware testing
/
Browsers and extensions
Firefox, Chrome, Brave, Ungoogled Chromium (used), Edge, Ungoogled Chromium (not use for the moment) :

search : Duckduckgo

extensions FF : uBlock Origin, Decentreleyes, Language Tool, Bitwarden, Keepa, Fakespot (for Amazon), h264ify (for Youtube), IDM extension, DarkReader, BetterRYM, cat-catch, AutoTabDiscard
Secure DNS
NextDNS (into Portmaster)
Desktop VPN
/
Password and passkey manager
Bitwarden (2FA authentification)
Maintenance tools
BleachIt, PatchMyPC, Windows Repair Toolbox, HiBit Uninstaller portable + UniGetUI
File and photo backups
"Synology DS720+" NAS and cloud like 'MEGA(.nz)", "Amazon Photos" (unlimited with "Prime"), "OneDrive", "Google drive", "Proton drive", "MEGA.nz", "KDrive", "Filen", "Twake", "pcloud"...
Subscriptions
    • None
System recovery
N/A
Usage and exposure
    • Visiting familiar websites
    • Visiting unknown or untrusted websites
    • Working from home
    • Making audio/video calls
    • Opening email attachments
    • Online shopping and card payments
    • Logging into my bank account
    • Downloading software and files from reputable sites
    • Requesting and accepting remote access
    • Gaming
    • Streaming audio/video content from trusted sites or paid subscriptions
    • Streaming from untrusted sites
    • Coding and development
Computer specs
Motherboard : msi-b550m-pro-vdh-wifi-micro-atx-am4-motherboard
CPU model : amd-ryzen-5-5600g-39-ghz-6-core-processor
GPU model : to CPU
RAM :
G.Skill Flare X Black (2x8 GB) DDR4-3200 CL16 Memory
storage : 1 Tb SAMSUNG 990 EVO Plus (Win 11 system)
1 Tb HDD 2,5' WD (storage)
1 Tb SSD M.2 CRUCIAL P3 Plus (Storage)
Notable changes
add some changes

VT4Browser, Shoptimate... extension ...

UAC minimum notify

HiBit Uninstaller portable

06/2022 : new material and Win 11

12/2022 : new NAS DS720+

04/2023 : Portmaster free​


09/2023 : AdGuard Home

10/2023 : custom security : Hard_Configurator

12/2023 : Kaspersky Free, ScreenWings add to security software, BloatyNoisy, Windhawk, Wireguard, DefenderUI...
+ new materiel : SSD 1 Tb Crucial P3 Plus, WIngetUI

01/2024 : HitmanPro Alert

01/2024 : Malwarebytes anti exploit and uninstalled HitmanPro Alert

11/01/2024 : MB anti ransomware + OSArmor 1.4.3 replace HitmanPro Alert and MB anti exploit...

10/02/2024 : removed osarmor and mb premium
add SpyShelter Pro

07/2024 : remove SpyShelter, remove AdGuard Home

11/2024 : NextDNS and H_C removed (only ConfigureDefender and FirewallHardening from H_c tools)

- Fort Firewall and HostsMan

- Office 365

12/2024 : AdGuard DNS, PrivaZer Pro...

01/2025 : NextDNS

03/2025 : Portmaster add and Fort Firewall removed

06/2025 : Fort Firewall, SimpleWindowsHardening added

06/2025 : Fort Firewall removed, simplewall portable added

02/2026 : Add Portmaster, remove Office 365,
Feedback preference

Detailed suggestions and alternatives welcome

Can I use "Malwarebytes Anti-Exploit" instead of OSArmor free version ?
Yea, and I wouldn’t use an old version of OSArmor to keep it free.

You can always try out Malwarebytes Premium and see how it behaves. High resource usage isn’t always indicative of poor performance unless you are limited on something like RAM or your CPU can’t handle it.
 
From the setup owner View current setup
Yea, and I wouldn’t use an old version of OSArmor to keep it free.

You can always try out Malwarebytes Premium and see how it behaves. High resource usage isn’t always indicative of poor performance unless you are limited on something like RAM or your CPU can’t handle it.
Yes I have already a licence key payed for MBAM. But I don't use I have few ressource RAM. Because FF and Chrome takes some of RAM.
 
Yes, I think. I mean, I use VB codes, etc. And one option delete all, I restore that, and it work fine now.
Do you use H_C in the current settings? If you allow macros, then you need to apply custom settings. What version of MS Office do you use?

You can also use MS Office as a non-default application to open only your documents (documents will be opened from MS Word, Excel, etc.). As a default application that can open office documents, you can configure Excel, Word, and PowerPoint mobile versions from Microsoft Store. The mobile versions do not allow macros and active content, but you can copy the content and print documents.
 
From the setup owner View current setup
Do you use H_C in the current settings? If you allow macros, then you need to apply custom settings. What version of MS Office do you use?

You can also use MS Office as a non-default application to open only your documents (documents will be opened from MS Word, Excel, etc.). As a default application that can open office documents, you can configure Excel, Word, and PowerPoint mobile versions from Microsoft Store. The mobile versions do not allow macros and active content, but you can copy the content and print documents.
Office 2019 Pro Plus
 
From the setup owner View current setup
What security do you use to mitigate MS Office vulnerabilities, exploits, and fileless malware related to MS Office?
Nothing I guess...

If I configure H_C it broke delete all my vb codes so I don't protect that anymore except with OSArmor free I see, he don't delete anything

How I have to do ? If you have idea...

The files which I download on Excel-downloads are safe.
 
@sypqys
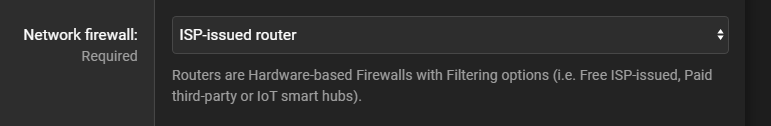
You should also change for "Network Firewall" that means simply your router:

264461-aa90c4a30cade9119c98349df47305e2.jpg
 
Nothing I guess...

If I configure H_C it broke delete all my vb codes ...
What do you mean by vb codes? Are they related to VBA features of MS Office (Macros, Add-ins, etc.)?
Do the original documents work differently after disabling H_C restrictions?

How I have to do ? If you have idea...

The files which I download on Excel-downloads are safe.

Most people infected via MS Office thought that the downloaded files were safe. Most of them were infected via MS Office macros or MS Office Add-ins. There are many other ways that can be adopted by the attackers in the near future to bypass the AV protection by using MS Office.
I do not have a convenient solution for you. Most security applications that protect MS Office use parent-child process monitoring, which is insufficient when you allow macros. I can only advise what I already posted:
  1. Use a safe application as the default program to open documents. So when you open the document, template, Add-in, etc., from the Desktop or Explorer (file explorer) it is not opened/installed via MS Office.
    This can be done by the custom configuration of default applications via Windows Settings >> Apps & features >> Default apps >> Set defaults by app. Next, choose MS Office Word, Excel, PowerPoint, and change the default application that can open the listed file types to a safe application.
  2. You can still open your documents by opening the MS Office application and using File >> Open from the application menu.
  3. If you must edit an unsafe document, then do not do it at once. Check it online and if it looks clean, then open it in MS Office after one or more days.
  4. You can additionally use Defender with ASR rules or anti-exploit solutions related to MS Office.
  5. Harden your firewall to block LOLBins' connections or use H_C to block popular LOLBins.
  6. Learn to recognize phishing attempts.
Be safe.(y)
 
Last edited:
From the setup owner View current setup
What do you mean by vb codes? Are they related to VBA features of MS Office (Macros, Add-ins, etc.)?
Do the original documents work differently after disabling H_C restrictions?


Most people infected via MS Office thought that the downloaded files were safe. Most of them were infected via MS Office macros or MS Office Add-ins. There are many other ways that can be adopted by the attackers in the near future to bypass the AV protection by using MS Office.
I do not have a convenient solution for you. Most security applications that protect MS Office use parent-child process monitoring, which is insufficient when you allow macros. I can only advise what I already posted:
  1. Use a safe application as the default program to open documents. So when you open the document, template, Add-in, etc., from the Desktop or Explorer (file explorer) it is not opened/installed via MS Office.
    This can be done by the custom configuration of default applications via Windows Settings >> Apps & features >> Default apps >> Set defaults by app. Next, choose MS Office Word, Excel, PowerPoint, and change the default application that can open the listed file types to a safe application.
  2. You can still open your documents by opening the MS Office application and using File >> Open from the application menu.
  3. If you must edit an unsafe document, then do not do it at once. Check it online and if it looks clean, then open it in MS Office after one or more days.
  4. You can additionally use Defender with ASR rules or anti-exploit solutions related to MS Office.
  5. Harden your firewall to block LOLBins' connections or use H_C to block popular LOLBins.
  6. Learn to recognize phishing attempts.
Be safe.(y)
I recognize I don't understand all the answer, but thanks
 

Join the discussion

Write your reply below. You'll create a free account or log in before it's posted.

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top