FileFix in the wild! New FileFix campaign goes beyond POC and leverages steganography
Acronis' Threat Research Unit discovered a rare in-the-wild example of a FileFix attack — a new variant of the now infamous ClickFix attack vector.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
Thanks for the insight mate however i am concerned rn about shulud.This method fails when PowerShell is set to Constrained Language Mode or prevented from making outbound connections. Both methods will block PowerShell from downloading the JPG payload. For example the below crucial CmdLines are forbidden in Constrained Language:
[System.Text.Encoding]::UTF8.GetString.Invoke('')
[System.Convert]::FromBase64String.Invoke('')
View attachment 290975
They are used used in this ClickFix attack to decode the first stage Base64 encoded payload.
Thanks for the insight mate however i am concerned rn about shulud.
View attachment 290976
![]()
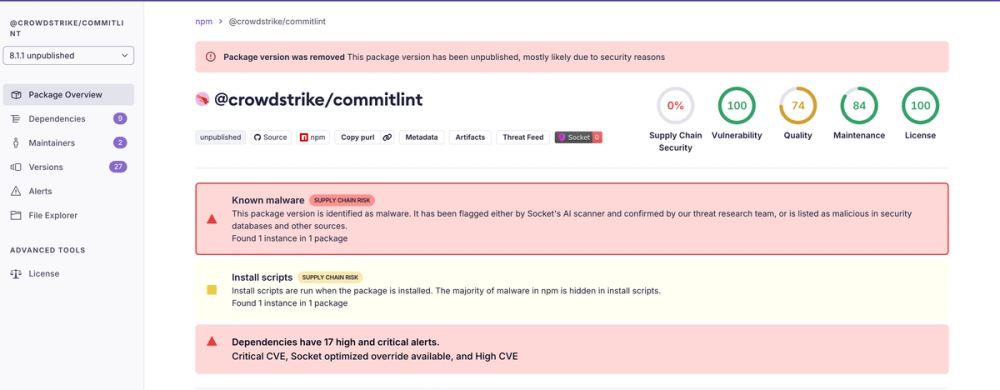
Ongoing Supply Chain Attack Targets CrowdStrike npm Packages...
Socket.dev found compromised various CrowdStrike npm packages, continuing the "Shai-Halud" supply-chain attack that previously hit `tinycolor`.socket.dev
![]()
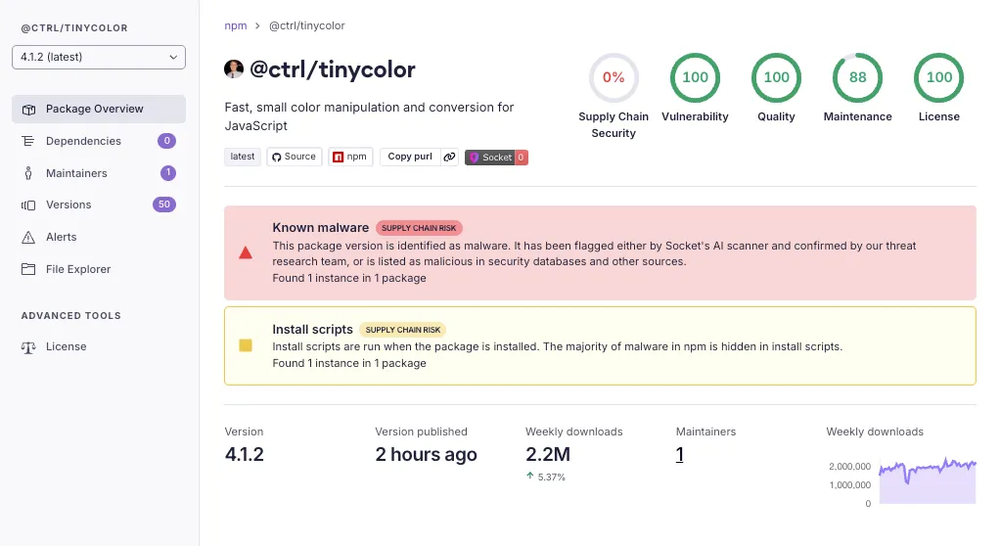
Popular Tinycolor npm Package Compromised in Supply Chain At...
Malicious update to @ctrl/tinycolor on npm is part of a supply-chain attack hitting 40+ packages across maintainerssocket.dev
- Khushal
- Replies: 2
- Forum: News Archive
Members who viewed this thread in the last 5 minutes