It's good to see you posting here. I miss your posts about 360 at Wilders.Any new updated Custom/Verdict cache to download?


The MalwareTips app
Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
- Home Screen access
- Optional push alerts
- Your community
You're ready to explore.Explore what's new
Installation instructions
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Keep up with your conversations
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
New Update Huorong Internet Security (Updates)
-
 Thread starter
Petrovic
- Start date
- 413 Replies
- 166,881 Views
I appreciate your most kind words. I exist everywhere but I'm mostly silent and read only.It's good to see you posting here. I miss your posts about 360 at Wilders.
Latest release (5.0.58.0 - 22/02/2021)
Dear Tinder users:
Hello! Thank you for using Tinder Security 5.0.
Following is today's update:
New features:
1. Add repairable items for system repair
Program defect repair:
1. Fix the problem of incorrect translation of Traditional Chinese in horizontal penetration protection .
2. Fix the problem that there is no animation effect when the horizontal penetration protection function switch is clicked to open or close .
3. Fix the problem that the USB flash drive protection cannot recognize the USB flash drive without a serial number .
4. Fix the U disk protection setting and ask me, the first time I connect the U disk, it will not prompt the problem of repairable items when a virus is detected .
5. Fix the problem that the password does not need to be entered when the password protection is turned off after the second password is set .
6. Fix the problem that the protection range of password protection does not check the " Protection Center Configuration " , and the password protection does not need to be entered when the password protection is turned off .
7. Fix the problem that VisualStudio compilation will slow down when real-time monitoring of files is turned on .
8. Fix the problem that the infection type annie fails to be cleaned .
9. Fix the issue of kb4565633 in Tinder's vulnerability repair scan when there is no patch in the system update scan .
10. Fix the problem that after entering the file name in the path of the protected object of the custom protection rule, select the corresponding file in the file list below, and the other selected files will be displayed .
11. Fix the problem that the " open tray message " is ticked off in the tray program settings, and the restart message after the automatic upgrade will still appear in the tray message .
12. Fix the problem that cleanup items without junk files will still be displayed after scanning the garbage .
13. Fix the problem that the scan status of other items except the local disk item is displayed abnormally after selecting the quick scan and scan, and then select the full scan and scan to scan .
14. When the DPI is set to 175 , the network protection - malicious URL blocking text is not displayed completely .
15. Fix the problem that the sort arrow in the program name column of the flow monitoring function view all the connection interface will be covered by text .
16. Fix the problem that the year of the copyright statement of "About Us" is incorrectly displayed .
17. Fix the problem that the language of the title of the preview image of the security log window does not change when switching languages.
With your help, Tinder is improving every day, thank you for your support!
Tinder operation team
February 22, 2021
Source: 5.0.58.0版本升级公告【2月22日】 - 火绒产品公告 - 火绒安全软件
There have been some releases before, however the logs are hard to find, so i missed them out.
Dear Tinder users:
Hello! Thank you for using Tinder Security 5.0.
Following is today's update:
New features:
1. Add repairable items for system repair
Program defect repair:
1. Fix the problem of incorrect translation of Traditional Chinese in horizontal penetration protection .
2. Fix the problem that there is no animation effect when the horizontal penetration protection function switch is clicked to open or close .
3. Fix the problem that the USB flash drive protection cannot recognize the USB flash drive without a serial number .
4. Fix the U disk protection setting and ask me, the first time I connect the U disk, it will not prompt the problem of repairable items when a virus is detected .
5. Fix the problem that the password does not need to be entered when the password protection is turned off after the second password is set .
6. Fix the problem that the protection range of password protection does not check the " Protection Center Configuration " , and the password protection does not need to be entered when the password protection is turned off .
7. Fix the problem that VisualStudio compilation will slow down when real-time monitoring of files is turned on .
8. Fix the problem that the infection type annie fails to be cleaned .
9. Fix the issue of kb4565633 in Tinder's vulnerability repair scan when there is no patch in the system update scan .
10. Fix the problem that after entering the file name in the path of the protected object of the custom protection rule, select the corresponding file in the file list below, and the other selected files will be displayed .
11. Fix the problem that the " open tray message " is ticked off in the tray program settings, and the restart message after the automatic upgrade will still appear in the tray message .
12. Fix the problem that cleanup items without junk files will still be displayed after scanning the garbage .
13. Fix the problem that the scan status of other items except the local disk item is displayed abnormally after selecting the quick scan and scan, and then select the full scan and scan to scan .
14. When the DPI is set to 175 , the network protection - malicious URL blocking text is not displayed completely .
15. Fix the problem that the sort arrow in the program name column of the flow monitoring function view all the connection interface will be covered by text .
16. Fix the problem that the year of the copyright statement of "About Us" is incorrectly displayed .
17. Fix the problem that the language of the title of the preview image of the security log window does not change when switching languages.
With your help, Tinder is improving every day, thank you for your support!
Tinder operation team
February 22, 2021
Source: 5.0.58.0版本升级公告【2月22日】 - 火绒产品公告 - 火绒安全软件
Latest release (5.0.57.0 - 21/01/2021)
Dear Tinder users:
Hello! Thank you for using Tinder Security 5.0.
Following is today's update:
New features:
1. The file shredding tool supports multiple selection of files/folders.
Program optimization:
1. Access control-website content control-online shopping website optimization blocking rules.
2. The security log content of multiple functions is adjusted.
3. Adjust the description displayed by the pop-up interception tool when manually intercepting the window.
Program defect repair:
1. Fix the problem of trusted zone-after entering less than 3 characters and clicking save, the added URL will disappear.
2. Fix the problem that the main interface will crash when exiting.
3. Fix the problem that the virus database date displayed on the tray may not be synchronized after the automatic upgrade.
4. Optimize the repair processing logic for some worm-like viruses.
5. Fix the problem that no password is required to modify the settings of horizontal penetration protection after password protection is set.
6. Fix the problem that it will be blocked by the camera protection function when using AnyDesk to connect to the XP system remotely.
7. Fix the problem that the junk cleaning tool is very slow to clean up the junk of the Chrome project when using the Chrome browser to visit the webpage.
8. Fix the problem that the IPV4 address in the IP protocol control rules cannot be intercepted when CIDR is used.
9. Fix the problem that the contents of the cleanup log of the garbage cleanup tool display abnormally when the file size of the recycle bin is too large.
10. Fix the problem that the name of the USB flash drive is not fully displayed in the pop-up window that prevents access to the USB flash drive usage control.
11. Fix the problem that the virus files packed by themida cannot be checked and killed.
12. Fix the problem that the URL content will show garbled characters when adding a long trusted URL to the trusted zone.
13. Fix the problem of abnormal security service after installation when the installation path contains ";" and "$".
14. Fixed the problem that the historical traffic page did not update the program category status of the program in time when the flow monitoring tool canceled the program speed limit.
15. Fix the problem that the real-time file monitoring does not prevent the running of the program and the script file when running the virus program in the compressed package and running the script virus file.
16. Fixed the problem that real-time file monitoring in certain scenarios could not intercept virus files in wsf format.
17. Fix the problem that in the function settings that need to enter the IP address, only enter ";" and "," and save without prompting the format error.
18. Fix the problem that the data item content of the traffic monitoring list does not display the complete content when the mouse is placed on it.
19. Fix the problem that if the name of the trusted USB flash drive used to control the USB flash drive is too long, it will not be able to be edited.
20. Fix the problem of incorrect English translation of software security interception and download protection settings.
21. Fix the problem that the same virus file will only be reported when the folder created in the system32 and syswow64 directories is selected for scanning at the same time.
22. Fix the bug that the bug fix tool will scan until the 4593175v1 patch.
23. Fix the problem that custom protection cannot import some rules.
24. When the interface language is switched to English, some interface texts are displayed incompletely and incorrectly.
25. When the interface language is switched to Traditional Chinese, some texts of the horizontal penetration protection settings are displayed in English.
26. Fix the problem that the interface language of the tray cannot be synchronized with the main interface when Tinder is installed without restarting the system.
27. Fix the problem that the red dot on the tray icon needs to be restarted twice to disappear when the system needs to be restarted for automatic upgrade.
28. Fixed the problem that the floating window of the U disk is not displayed after some mobile hard disks and U disks are inserted, and the U disk use control function fails.
29. Fix the problem that the text and icon size of the startup item list in the startup item management interface of the other display screen display abnormally when one of the two different DPI displays is turned off in the optimization details interface of the startup item management tool.
With your help, Tinder is improving every day, thank you for your support!
Tinder operation team
January 21, 2021
Source: 5.0.57.0版本升级公告【1月21日】 - 火绒产品公告 - 火绒安全软件
Latest release (5.0.56.0 - 22/12/2020)
Dear Tinder users:
Hello! Thank you for using Tinder Security 5.0.
Following is today's update:
New features:
1. Added the "Horizontal Penetration Interception" function to block the intranet horizontal transmission behavior that can be used by malicious code.
Program optimization:
1. Added a new startup item prompt in "Startup Item Management".
2. Added "Advanced Protection" prompt that the corresponding protection switch is not turned on.
3. Newly added "Flow Monitoring-Speed Limiting Program" the function of customizing and editing the speed limit after the speed limit.
4. Optimized the content of the prompt pop-up window of "Access Control-Internet Time Control".
5. Optimization of the processing method of "infectious virus, macro virus, AutoCAD virus, Maya virus".
6. Added prompts to take effect after restarting the protection items of "Network Protection Project", "Camera Protection Function", and "Write Disk Reserved Sector".
Program defect repair:
1. Fix the problem that the security service process will occupy the 1080 port.
2. Fix the issue that IPV4 and IPV6 addresses in the IP blacklist do not support CIDR.
3. Fix the problem of junk cleaning up the URL saved by the infinity plugin.
4. Fix the problem of incomplete display of the registry of Tinder Sword viewing 360 speed browser.
5. Fix the problem that the Tinder Sword driver interface cannot be sorted correctly after clicking the column name sorting.
6. Repair the system to repair the problem that the project name and repair location of individual repair items are inconsistent.
7. Fix the problem that the tray message is not recorded after the pop-up window prompting to restart after the automatic upgrade disappears.
8. Fix the problem of KB3185319 being repeatedly scanned by Win7 system after setting custom protection rules.
9. Fix the problem that traffic monitoring-view all connection interfaces using the ctrl+c shortcut key can not copy the entire line of information.
10. Fix the problem that the function of shutting down after checking the virus check and killing will not take effect when the system is not restarted after installing Tinder.
11. Fix the problem that there is no pop-up window when the mail monitoring function is triggered when the mail monitoring processing mode is selected to record only.
12. Under XP system, after installing Google browser, use junk cleaning scan, junk cleaning will report an error and crash.
13. Fix the problem that the serial number of individual USB flash drives in the control interface of the USB flash drive displays garbled characters after opening the access control-U flash drive control.
14. Fix the problem that the setting menu of the system process in the traffic monitoring interface is not disabled, and the setting menu of other system processes is disabled.
15. Fix the problem that the module name in the security log and the tray message box of the log related to the brute force attack protection function is inconsistent.
16. Fix the problem that when the security log records too much, the tinder tray icon will not be displayed when the boot is turned on, and the protection center functions are all displayed and turned off.
17. Fix the problem that the trusted zone list is not updated in time after adding trusted files through virus scanning when the trusted zone interface is open.
18. Fix the problem that the way to switch the focus with the keyboard can turn on/off the function switch of the protection center without triggering the password protection.
19. Fix the problem that after installing Tinder on Windows to go made by U disk and turning on the ransomware trapping function, it will prompt a repair item every time it is turned on.
20. Fix the problem that the wrong proxy server address is filled in the upgrade settings. After clicking upgrade, unchecking the proxy server and clicking upgrade will prompt the problem that the upgrade cannot be performed.
21. Fix the problem that the shortcut keys displayed on the setting interface and the shortcut keys in effect are inconsistent when setting the shortcut keys for manual interception in pop-up interception.
With your help, Tinder is improving every day, thank you for your support!
Tinder operation team
December 22, 2020
Source: 5.0.56.0版本升级公告【12月22日】 - 火绒产品公告 - 火绒安全软件
Latest release (5.0.55.0 - 17/11/2020)
Dear Tinder users:
Hello! Thank you for using Tinder Security 5.0.
Following is today's update:
New Requirements:
1. Network intrusion interception adds support for interception of CVE-2020-16898.
2. Web service protection adds support for interception of CVE-2020-14882.
3. Traffic monitoring-view the number of connections interface IPV6 connection does not display "X" (that is, close the connection button).
4. The content of the IP blacklist log increases the offending action, showing the link in and link out.
5. The number of custom protection rules is increased to show the number of opened rules and the number of all rules.
Program optimization:
1. Optimize the display of the "Functional Vulnerability Patch" and "Patch Not Recommended" of the security tool-vulnerability repair when it is not scanned.
2. Optimize the description of the blast attack protection function displayed in the protection center.
Program defect repair:
1. Fix the problem of network control rules after selecting the system program, the network mode selects "Allow Networking" and still prompts whether to disable it.
2. Fix the problem that when the system permission of the virus sample file is all denied, the scan will not report the virus.
3. Repair security tools-vulnerability repair When no vulnerability patch is selected, the problem that the selected item is not disabled is ignored.
4. Repair the problem that the virus sample was processed successfully, but the result page and log showed that the processing failed.
5. Fix the problem that Tinder can be installed on Win10 1507 (version number 10240) system after modifying the compatibility mode.
6. Fix the problem that the scan items that can be scanned without files in the specified format will show that the engine is being initialized when the scan items that can be scanned for files in the specified format are checked in the full scan and kill settings.
7. Fix the problem that the scheduled task cache item used to execute powershell commands in the registry of driving life cannot be scanned and processed.
8. Repair the problem that the results of checking and killing the macro virus files in the rar format compressed package are not displayed correctly.
9. Fix the problem that the pop-up window interception, garbage cleaning and bug fixes can coexist the desktop shortcuts created when the Tinder interface language is different.
10. Fix the problem that the right-click management does not have the right-click menu items of Caiyun.
11. After the repair software is uninstalled, the remaining right-click menu items can be seen in the security tool-right-click management.
12. Fix the problem that Tinder's traffic monitoring and network control fail after using the network repair function of Wonder Accelerator.
13. Fix the problem that when the content of the hosts file exists in Chinese, the security tool-network disconnection repair scan will crash.
14. Fix the problem that the Tinder log file content triggers Tinder to report the virus, and the Tinder security log cannot be opened after processing.
15. Fix the problem that the scan time will also change after modifying the system time.
16.Fix the problem that HbuilderX cannot install the built-in browser plug-in when the real-time monitoring level of the file is the default level (scanning during execution and modification), npm fails to package using electron-builder, and VS 2017 cannot compile the project.
With your help, Tinder is improving every day, thank you for your support!
Tinder operation team
November 17, 2020
Source: 5.0.55.0版本升级公告【11月17日】 - 火绒产品公告 - 火绒安全软件
Last edited:
I like the Huorong's UI a lot. The English translation is perfect, it has a nice clean look and is highly configurable. You can for example you can configure it to ask on threat detection, rather than auto quarantining and this is individually configurable for real-time protection, scans and behavioural detection. There is also a choice between three scan modes for real-time protection, with varying levels of system impact.
It's just a shame about the poor detection rate.
It's just a shame about the poor detection rate.
The GUI could be a bit fancier in colours / look similar to Tencent in colour scheme IMO, but hey, this is actually a security product and not a car.I like the Huorong's UI a lot. The English translation is perfect, it has a nice clean look and is highly configurable. You can for example you can configure it to ask on threat detection, rather than auto quarantining and this is individually configurable for real-time protection, scans and behavioural detection. There is also a choice between three scan modes for real-time protection, with varying levels of system impact.
It's just a shame about the poor detection rate.
Overall my impression is good, that keeps me coming back again and again.
No useless bloat like in another chinese AV, which becomes more of a do-it-all, look super-fancy (although it’s cloud seems to be one of the best out there).
I like the possibility to write own rules to cover weaknesses a lot, they keep adding useful features, and the built-in Firewall is simply awesome.
Ask for everything when on, with rating and save answer.
As for the signatures, they‘re indeed weak, however I did not expect any detection in the last two tests, it is hopefully improving slowly but steady.
The product also is light on my machine.

@Der.Reisende @roger_m
From your experience, how is support? 360 customer support was nonexistent and I hope it is not the case with this product.
From your experience, how is support? 360 customer support was nonexistent and I hope it is not the case with this product.
I did contact a member registered here too once, however although he forwarded my request regarding BB action against Netwalker, it hasn‘t been implementet yet.@Der.Reisende @roger_m
From your experience, how is support? 360 customer support was nonexistent and I hope it is not the case with this product.
Maybe it’s difficult to do, from what I‘ve learned it injects from Powershell to Explorer, so blocking Explorer would crash Windows most likely.
Almost none of the AVs i tested could handle it yet (K7 support told me they implementet but doesn‘t work).
I did not post on their forum, however reading there it seems they are interested in feedback, and fix a lot with each new release (see logs above).
As for 360, i confirm that experience.
Also with SUD, I cannot tell whether they add the samples, I regularly got messages like they could not open attachment, or cryptic like „fail in security found, add to Whitelist if necessary“.
Note that I always got a message the submission was successful (and the archive was def not broken).
I've never contacted support. I just have it running on a test computer and have never used it as my main antivirus. When I opened a support ticket with 360, a few years ago they did reply.@Der.Reisende @roger_m
From your experience, how is support? 360 customer support was nonexistent and I hope it is not the case with this product.
In my experience Panda and 360 support are nonexistent. I was a paid customer of Panda.I've never contacted support. I just have it running on a test computer and have never used it as my main antivirus. When I opened a support ticket with 360, a few years ago they did reply.

Just wondering did you have the "custom"rule set HIPs on or was it default ?I did contact a member registered here too once, however although he forwarded my request regarding BB action against Netwalker, it hasn‘t been implementet yet.
Maybe it’s difficult to do, from what I‘ve learned it injects from Powershell to Explorer, so blocking Explorer would crash Windows most likely.
Almost none of the AVs i tested could handle it yet (K7 support told me they implementet but doesn‘t work).
I did not post on their forum, however reading there it seems they are interested in feedback, and fix a lot with each new release (see logs above).
How would you rate the HIPs(custom rule set) component compared to ESET or Comodo ?
Regards Eck

Last edited:
I had the same experience with Panda.In my experience Panda and 360 support are nonexistent. I was a paid customer of Panda.
Long time since I have tried this. Does it use machine learning yet?Most likely no."The Tinder anti-virus engine with independent property rights has been polished and matured after 6 years of hard work. Based on the unique "virtual sandbox" technology, it can deeply analyze the essential characteristics of various malicious codes and effectively solve code-level malicious confrontations such as encryption and obfuscation. At the same time, the engine can also perceive static code-level threat information in real time, as well as dynamic file-level threat behavior information, which is the main functional module of terminal threat probes.Tinder engine has powerful general scanning, general unpacking and code behavior analysis capabilities, as well as lightweight design, supports multiple platforms and rich file formats, and has high decoding, checkout and code repair capabilities. Therefore, tinder products have the characteristics of ultra-low false alarm rate, fast detection and killing speed, and small size and resource occupation."
Haven't tested HIPS of both in detail.Just wondering did you have the "custom"rule set HIPs on or was it default ?
How would you rate the HIPs(custom rule set) component compared to ESET or Comodo ?
Regards Eck
I bet Comodo will cover almost everything by default sandboxing alone.
Just wondering did you have the "custom"rule set HIPs on or was it default ?
Yes, it's tweaked a lot:
Action on threat detection: clean (instead of ask)
Behavior Based Detection: Enable Ransomware Trapping
HIPS: File / Registry / Sensitive action: all possible rules enabled (default action is still "ask")
HIPS: Enable Network Access Control (kinda outbound Firewall, colour indicator green and orange - safe or not)
Installation Detection: Automatically block recognized installations of unlisted softwares
Firewall: Lateral Movement Protection - Remote MMC and Remote WMI also o
Network Access Control on (=two-way Firewall)
Advanced: Enable custom rules
Imported custom rules shared by user JerryLin - v4.24_1 - Update - Huorong Internet Security (Stable)
Note I disable the Powershell rules whenever I don't run #Netwalker, because no Powershell would (most likely, no guarantee) run at all.Source:
C:\Windows\WinSxS\amd64_microsoft-windows-powershell-exe_31bf3856ad364e35_10.0.19041.1_none_1f070c37a19029ff\powershell.exe
C:\Windows\WinSxS\amd64_microsoft-windows-gpowershell-exe_31bf3856ad364e35_10.0.19041.1_none_ee822d264112a470\powershell_ise.exe
C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe
C:\Windows\System32\WindowsPowerShell\v1.0\powershell_ise.exe
C:\Windows\SysWOW64\WindowsPowerShell\v1.0\powershell.exe
C:\Windows\SysWOW64\WindowsPowerShell\v1.0\powershell_ise.exe
Target:
File rules: *.ps1 --- Create / Read / Modify / Delete --- all set to "Deny" as default verdict
Note that without that Powershell tweak, #Netwalker would trash the system easily, not getting even noticed by Huorong. You could create protected folders via HIPS, but I experienced them to not always be protected by HIPS.
Yes I see, very tweaked indeedy
At least the other big players are having a problem dealing with Netwalker also but I hope Huorong listen and act upon your feedback and advice.
Although the sigs aren`t very good(yet) and HIPS need some work, the firewall component with it`s superb outbound protection still makes it a great companion to WVStopX, imho. Plus it`s light and sure looks purdy.
Thanks for the detailed response Der.Reisende
Regards Eck
Last edited:
Hi where is the download for latest version?

Hi where is the download for latest version?
Going to try this with Wisevector.

I had the same experience with Panda.
I tried Panda a few months ago to retry it because I used it probably 3 years ago when it was quite good. Now it has gone to absolute garbage, especially the free version. There have been no program version updates in over a year, full of bugs, no technical support, also no way to report false positives because they don't seem to get checked. I posted a false positive about 2 months ago and still no reply, also did a bug report and no reply too. I wouldn't recommend Panda anymore even the free version. It used to be very good and light. Very disappointing, seems it went downhill ever since the WatchGuard company bought them out.In my experience Panda and 360 support are nonexistent. I was a paid customer of Panda.
Latest release (5.0.58.1 - no log yet)
Scan engine has been overhauled, apart from that, the usual database updates.
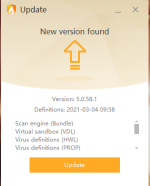
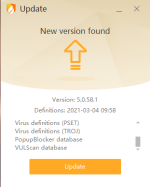
Scan engine has been overhauled, apart from that, the usual database updates.
I find there are not enough thingd to customize on our own ,I might be wrong.
Recently browsing
Members who viewed this thread in the last 5 minutes
You may also like...
-

-
S
New Update McAfee R135
-

-

-
