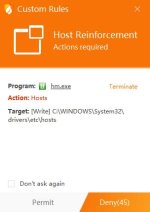
+My HIPS rules for Huorong
Check out if you're interested: GitHub - JerryLinLinLin/Huorong-ATP-Rules: 一款火绒增强HIPS自定义规则
Trojan.StartupFolderMalDropper.A
*\Users\*\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\*.js?
like *.jse


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
 Thread starter
Petrovic
+My HIPS rules for Huorong
Check out if you're interested: GitHub - JerryLinLinLin/Huorong-ATP-Rules: 一款火绒增强HIPS自定义规则

No plans yet.There are currently no plans for rules for IP Firewall?
++
Trojan.StartupFolderMalDropper.A
*\Users\*\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\*.js?
like *.jse

Hello can you pls tell me what this article means? tyscan engine.
Hello can you pls tell me what this article means? ty

Host file is already covered by the default rules.
Any samples/references of real-world malware that are doing that?+
*.wsf
_CH8576394.wsf (MD5: 8E0FD927F008AD42FB07B4A8B20A8098) - Interactive analysis - ANY.RUNAny samples/references of real-world malware that are doing that?
v0.1.6My HIPS rules for Huorong
Check out if you're interested: GitHub - JerryLinLinLin/Huorong-ATP-Rules: 一款火绒增强HIPS自定义规则
 github.com
Defence driver
Scan engine (Bundle)
Scan engine (XSSE)
Scan engine (Cobra)
Log program
Tray program
Netflux program
UI resource (Main)
UI resource (Log)
UI resource (HRConfig)
UI resource (NetFlow)
UI resource (FileShred)
UI resource (VULScan)
Virtual sandbox (DAT)
Virus definitions (PROP)
Virus definitions (PSET)
Virus definitions (TROJ)
Behavior analysis definitions
Malicious website definitions
VULScan database
Scan engine (XSSE)
Virtual sandbox (DAT)
Virtual sandbox (TDL)
Virus definitions (PROP)
Virus definitions (PSET)
Virus definitions (TROJ)
Defence database
Behavior analysis definitions
Malicious website definitions
Application reinforcement database
PopupBlocker database
VULScan database
Defence driver
Virtual sandbox (DAT)
Virus definitions (PROP)
Virus definitions (PSET)
Virus definitions (TROJ)
Defence database
Behavior analysis definitions
Malicious website definitions
please add AI to HuorongMy HIPS rules for Huorong
Check out if you're interested: GitHub - JerryLinLinLin/Huorong-ATP-Rules: 一款火绒增强HIPS自定义规则
github.com
Added new group category Telemetry, the default state is off
The following rule groups have been added:
Suspicious.AppCertDLLs
Suspicious.AppInitDLLs
Suspicious.NetDebugger
Suspicious.NetWinAppXRT
Telemetry.ActiveSetup
Telemetry.CredentialProviders
Telemetry.LSAConfig
Telemetry.PowerShell
Telemetry.ReadBrowserData
Telemetry.TerminalServer
Other ruleset adjustments
Firewall driver
Defence driver
Scan center
Scan engine (libcodecs)
Scan engine (Bundle)
Scan engine (XSSE)
Main program
Tray program
Security service
UI resource (HRConfig)
Uninstaller
SysRepair program
Virtual sandbox (DAT)
Virus definitions (PROP)
Virus definitions (PSET)
Virus definitions (TROJ)
Behavior analysis definitions
Website control database
UI resource (SysClean)
Virtual sandbox (DAT)
Virus definitions (PROP)
Virus definitions (PSET)
Virus definitions (TROJ)
Malicious website definitions
Website control database
Firewall driver
Defence driver
Virus definitions (PROP)
Virus definitions (PSET)
Virus definitions (TROJ)
Members who viewed this thread in the last 5 minutes