



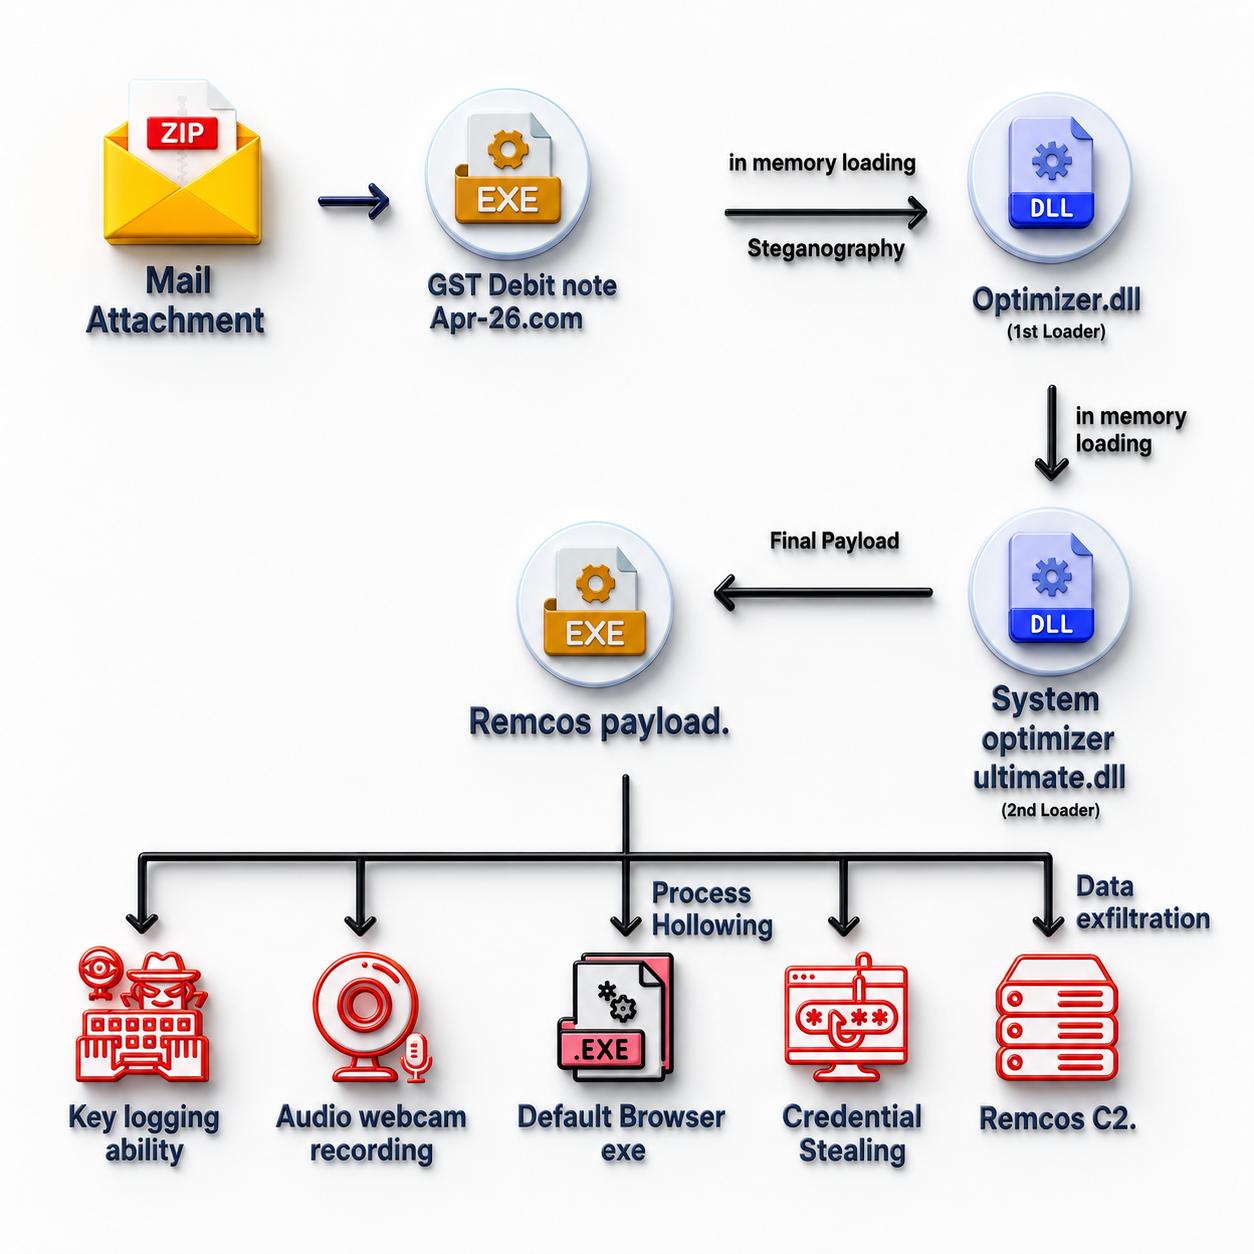
Analysis revealed that the payload was a variant of the Remcos RAT malware family, distributed via a phishing campaign as an archive attachment. One notable characteristic of this infection chain was its reliance on in-memory execution techniques / fileless malware & Steganography. By avoiding disk-based artifacts, the threat reduces forensic evidence and increases its ability to evade traditional security tools and signature-based detection methods.

A Multi-Stage Steganographic Loader Campaign Deploying Diverse Payloads Globally - K7 Labs
During the routine telemetry monitoring, we identified a detection on a suspicious file named “GST Debit Note Apr_26.com”, based on […]labs.k7computing.com
