Saw everything. Thanks. See you soon.I hope you have all the information you wanted. I have to leave early tomorrow morning so I'm going to bed. See you soon friend


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
Saw everything. Thanks. See you soon.I hope you have all the information you wanted. I have to leave early tomorrow morning so I'm going to bed. See you soon friend

They need intelegent execution control like Kaspersky, voodooshield and others. I can't wait.I started to retest ZAESNG:
Version number: 4.2.121.19549
Anti-Ransomware: 4.2.77.19549
Antivirus version: 3.85
Signature version: 202307121001
Engine version: 86.72.12
Firewall version: 8.68.72.3
Anti-Bot version: 8.68.72.14
Definitely the App Control is a step forward.
However, the default seems to be "allow all", and the user needs to deny manually. I don't like it. But ZA can easily improve that, if they add a simple general "allow all", "deny all" and "automatic". Also it'll be nice if ZA adds another option, allowing the user (manually) to choose in advance which apps are going to be allowed/blocked.
The Firewall control improvement, also is positive.
However, IMHO, it's wrong to mix App Control with Firewall. Mainly because firewall functions are not restricted to apps!
IMHO, Firewall control should be separated (allowing not only to control apps, but also to control any other connection).
And again, the App Control default seems to be "allow all", therefore the Firewall default seems to be "allow all" too... and that's bad!
I don't think ZA designed a bad App + Firewall Control because they want to keep the minimalist layout. I remember that WiseVector had separated controls for Apps and Firewall, and both worked like a charm. And WiseVector was minimalist. So, I think ZA still needs to improve both, App Control and Firewall. The current App Control is not adding security layers. And the current Firewall Control, the same. I don't think both controls need lot of improvements, but I do believe both need to be separated, and both need small improvements.
Changing subject, the RAM consumption dropped a lot, around -35% compared to two months ago version.
But the Beta version is a little unstable, and has small bugs.
This weekend I'll try to test some malwares against this new ZA version.
But at first glance, I like to see that ZA is working, I recognize progress, new features, and I hope ZA will keep adding new improvements.
PS: I sent them a message sharing with them my impressions.
@Decopi in my opinion Application Control is just where it belongs, part of firewall. It is the firewall job to manage connections.
The firewall already applies a series of rules. It has few allow rules and the last one is called “Cleanup Rule” where all traffic not allowed goes and is blocked. The application control takes care of limiting the apps. Together, they ensure connection not desired by the user and not needed are not initiated.
What must be done from here:
-I believe firewall should automatically apply blocks to apps not classified as safe (the Check Point ThreatCloud network knows what’s safe and what’s not).
-Perhaps user prompt so user can decide
-Option to terminate apps, not just to block their connection (that’s in Harmony Endpoint).
Option to add apps in advance (as mentioned by Decopi).
Nevertheless, app control indeed is a positive improvement. Also, I hope before final release, engines will be updated to 86.80 as well and not 86.72.

Yeah, the thing is ZoneAlarm for years was this bloated, geeky, nerdy software. I remember their “malware detected” notification which was a whole window, Symantec-Endpoint-Protection-style.I can imagine a scenario, where ZA says: "Let's build the most minimalist software, where almost everything behaves automatically".

Kind of liked that old school look and removal windows actuallyYeah, the thing is ZoneAlarm for years was this bloated, geeky, nerdy software. I remember their “malware detected” notification which was a whole window, Symantec-Endpoint-Protection-style.
So how do you break free from this image?

Yeah, the thing is ZoneAlarm for years was this bloated, geeky, nerdy software. I remember their “malware detected” notification which was a whole window, Symantec-Endpoint-Protection-style.
So how do you break free from this image?
You start all over and you build something that is extremely simplistic. Then upon re-adding components, you do it carefully, not go back to the previous experience.
The user is paying to take decisions instead of them (majority of users). So you harness powerful endpoint engines and do everything automatically.
So in this case, firewall applies triple filter:
First, Application Control decides what apps and processes can connect.
Second, already allowed apps and processes are subject to the rules list.
Third, already allowed apps, processes and traffic is subject to URL filter. Traffic will be allowed only if it’s not to a known C&C and the Check Point network handles C&Cs very well.
Again back to Symantec and Norton (as Check Point has always been inspired by Symantec in everything they do and I guess for them Norton/Symantec are the absolute leaders and Gil was always friends with Gary Hendrix), SEP/Norton firewall is controlled by reputation. Similar thing could be done in ZoneAlarm where firewall automatically blocks never-before-seen executables. User can opt to block LOLBins from connecting.
I think similar setup is coming to ZoneAlarm as well.
@NormanF on a corporate environment it’s totally different.
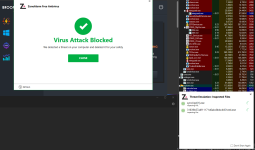
But that's not a real-world scenario anyway.When I decompress the sample package, if there are multiple samples, there will be a lot of independent pop-up windows instead of merging pop-up windows, which is very inconvenient.

Quarantine files cannot be deleted.,any way to deleted it?But that's not a real-world scenario anyway.

ZoneAlarm free doesn’t use reputation (Threat Cloud) lookups though. It has a much lower detection rate.


Kaspersky gives me a warning(program bundled with other, which I hit ignore) Gdata and Malwarebytes also, at least in the past didn't like iobit driver booster eitherOn my computer, Zonealarm extreme security does not like iobit driver booster which I have known and used for years but I can easily restore the file and it is excluded afterwards. Zonealarm extreme security works very well for me without any noticeable slowdown of the computer.
Members who viewed this thread in the last 5 minutes