


With billions of users, Facebook is a magnet for cybercriminals looking to exploit innocent people. One common scam tactic is sending phishing messages about impending account deactivation due to policy violations. If you receive this message, here’s what you need to know to avoid being tricked into compromising your account.

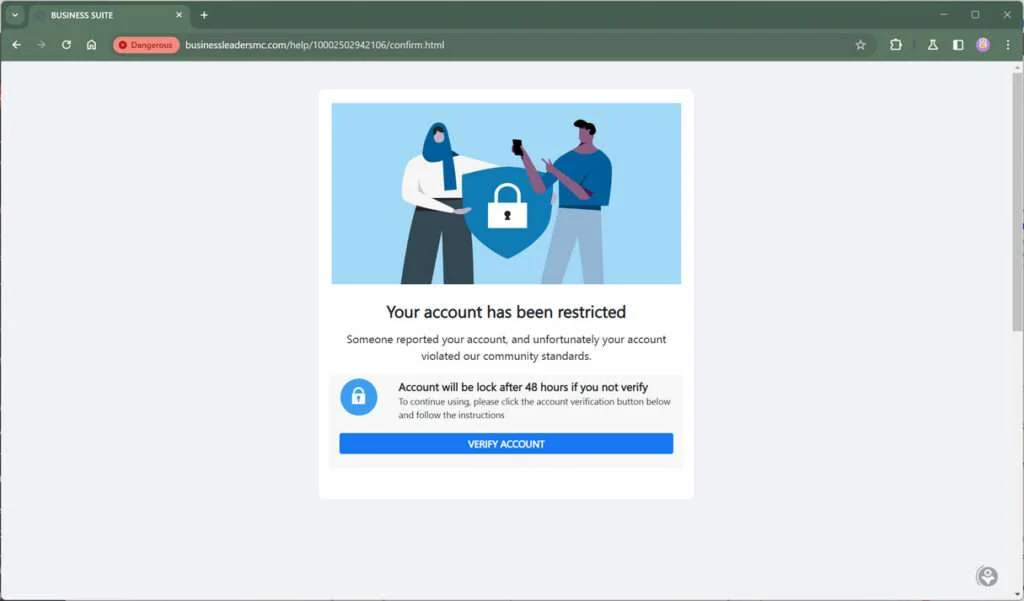
Overview of The “Account Deactivation” Facebook Scam
The “Account Deactivation” phishing scam typically starts with targets receiving an unsolicited Facebook message stating their account is about to be deactivated. The message claims various policy violations have been reported and the only way to avoid deactivation is verifying your identity via an external link.
However, in reality there are no legitimate violations or risk of deactivation. This is a completely fabricated alert designed to trick unsuspecting Facebook users into handing over their login credentials.
Once you click the link and input your username and password on the fake login page, malicious actors immediately gain full access to hijack your real Facebook profile. From there, they can exploit it to:
- Impersonate you and message contacts
- Post dangerous misinformation or spam
- Access personal data and photos
- Take over your Facebook Groups or Pages
- Spread viral scams to your network
- Delete your profile entirely
Essentially, falling for this scam hands over complete control of your digital identity. It enables serious identity theft, privacy breaches, spreading of malware, and financial fraud through compromised connected accounts.
Who is Behind the Scam?
This scam is perpetrated by individual cybercriminals and organized hacking groups who mass message potential targets using harvested inboxes and contact data.
Their aim is to cast as wide a net as possible, knowing even a 1% success rate can provide thousands of hijacked accounts. These become tools to build out botnets, steal info, distribute malware, and execute additional phishing campaigns.
The online underground marketplace also allows them to sell hacked accounts to the highest bidder, adding another lucrative revenue stream.
Examples of Typical Phishing Messages
- “Our system detected multiple violations on your account. Confirm your identity via our verification link within 24 hours or your account will be deactivated.”
- “Several users have reported inappropriate content posted from your account. Verify yourself immediately through the provided link to avoid permanent deletion.”
- “You have repeatedly violated our community standards. You must validate your account ownership or your profile will be removed tonight.”
Who Does This Scam Target?
This scam predominantly targets two groups:
1. Administrators of Popular Facebook Pages
The scammers are hoping to hijack pages with large followings so they can use the brand and reach to run additional scams. A page with an established audience is very valuable to them.
2. Everyday Facebook Users
While not the primary target, regular Facebook users could also receive these scam messages. The scammers likely mass message users hoping some will fall for it. They will take over any account they can compromise.
How Does The “Account Deactivation” Facebook Scam Work?
While specifics may vary slightly, here is the general sequence of events used to carry out this phishing scam:
1. You Receive a Message About Account Deactivation
Out of the blue, you receive an unsolicited message in your Facebook inbox stating there have been violations reported on your account. It claims these violations require you to verify your identity to avoid deactivation.
Of course in reality, there have been no actual violations and your account is not facing removal. This is complete fabrication to panic you into clicking their phishing link.
2. The Message Includes a Link to Verify Your Account
A key identifier is that the message includes an external link you must click to confirm your identity and avoid deactivation.
The link may seem legitimate, but actually directs to a fake Facebook login page on a different domain. Common examples include:
- account-validation.facebook.com
- myaccount-appeal.com/facebook
- fbviolationappeal.verification.co
3. You Click The Link and Land on a Fake Login Page
When you click the provided link, it takes you to a page imitating Facebook’s login screen. However, the URL clearly shows it is not actually Facebook.
You’ll be prompted to enter your username and password within a short timeframe to avoid the stated deactivation. But in reality, this just captures your credentials.
4. Scammers Use Your Login Info to Access Your Account
Once you input your credentials, the scammers immediately use them to access and takeover your actual Facebook account. They can now impersonate you, post content, message friends, view private data and even delete your profile.
They may also change your password to lock you out, remove trusted devices so only they retain access, or attach the account to a new email under their control.
5. Scammers Leverage Your Account for Further Attacks
With control of your profile, scammers can leverage it to execute additional scams and attacks, thanks to your perceived credibility as the actual account holder.
They may scam your friends list by impersonating you asking for money or info. Or use your account to spread fake news, compromised links, harvest user data via polls/quizzes or take over management of your Pages.
Your account provides immense power for the scammers to harm you, steal your info, and target your network of connections.
6. You Lose Access With No Way to Recover It
Meanwhile, you are completely shut out and unable to access your account. With your password changed and devices revoked, you have no way to retake control or delete the fraudulent posts and messages.
Until Facebook Support intervenes, you are essentially helpless while scammers do untold damage impersonating you and accessing your private data. This makes falling for the scam extremely risky.
How to Identify The “Account Deactivation” Scam on Facebook
It takes vigilance to recognize phishing attempts on the world’s largest social network. When it comes to the prevalent “Account Deactivation” scam, there are distinct indicators to watch for that reveal it as a deception aimed at stealing your login credentials.
Sender Profile Appears Suspicious
Take a close look at where the message is coming from. These scam warnings usually come from random accounts not known to you personally with generic names.
For example, the sender may be named something vague like “Facebook Support” or use a series of numbers in their profile name. Legitimate notifications only come directly from Facebook’s official verified channels.
Links Go to Outside Websites
A major red flag is if the message contains any external link you must click to avoid deactivation. Scammers use misleading URLs that appear to be Facebook domains on first glance.
However, hovering over or clicking the link shows it actually goes to a different website entirely. Examples include “account-deactivateappeal.com” or “fb-loginverification.co” which are not real Facebook sites.
Aggressive Threats and False Urgency
Watch for urgent threats of immediate permanent deactivation if you don’t act quickly. Phrases like “Confirm identity in 24 hours” or “Last chance to verify before removal” aim to startle you into reacting hastily without thinking.
Facebook’s real notifications about policy violations have an informative tone – not aggressive threats or unrealistic ultimatums.
Strange Grammar, Spelling Errors
Low-quality phishing messages often contain awkward grammar, misspellings and typos. If a deactivation warning looks poorly written, it likely did not come from Facebook’s professional team.
Facebook’s legitimate alerts are meticulously translated and edited with proper language conventions.
Requests Login Credentials
Any message asking you to provide your Facebook password or login details is a huge red flag. Facebook will never direct you to input security credentials on random third-party websites to “verify” your identity.
This immediate request for sensitive information signals a phishing attempt to steal your account access. Stay vigilant for these signs to protect yourself from scams on the world’s most used social platform. Scrutinizing every message thoroughly is key.
What to do if You Get Scammed
If you submitted your login info through the phishing link, take these steps immediately to regain access:
Step 1: Report the Compromised Account to Facebook
Contact Facebook Support and explain your account was hacked through a phishing message. Provide details of any concerning posts or messages. Reporting unauthorized access prompts Facebook to investigate and helps regain access.
Step 2: Try Resetting Your Password
Attempt resetting your password directly through Facebook.com. Scammers sometimes don’t change it immediately, allowing a reset.
If successful, create a new complex password to revoke the scammer’s access. Enable two-factor authentication for added security.
Step 3: Remove Suspicious Posts, Friends and Admins
If you regain entry, check for any unknown admins added to Pages you manage, and delete dubious posts/messages to limit damage. Unfriend suspicious new connections.
Step 4: Secure Connected Accounts
If your Facebook was linked to other apps/sites, change your passwords there as well. Prioritize sites containing financial data or personal info. Enable two-factor authentication where possible.
Step 5: Watch for Suspicious Login Activity
Routinely check Settings > Security > Login Activity and review devices accessing your account. Remove any unknown or suspicious sessions.
Step 6: Warn Connections About the Scam
Once your account is restored, alert your friends list about the “account deactivation” phishing scam. Explain the threat so they can protect themselves from becoming victims too.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About The “Account Deactivation” Facebook Scam
This frequent phishing tactic fools many Facebook users. Here are detailed answers to common questions about how it works and how to stay secure:
What exactly is the “Account Deactivation” Facebook scam?
This scam sends a phishing message claiming your account faces imminent permanent deactivation due to policy violations. It includes an urgent call to action to “verify your identity” by entering your Facebook login credentials on an external website. In reality, it’s a deception aimed at stealing your account access.
Why does this scam message claim my account is being deactivated?
By citing violations and deactivation, the scam message creates a sense of fear that your access is about to be lost forever. This panic causes some users to click the phishing link recklessly in hopes of saving their account without considering it may be a scam.
Who sends these “Deactivation” scam messages?
Individual cybercriminals and hacking groups distribute these en masse by the thousands. They obtain target inboxes through data leaks, malware attacks, bot networks, and purchases on the dark web. Even a low success rate still gives them a trove of hijacked accounts.
How do scammers benefit from taking over my Facebook account?
Your account provides immense power through your identity, personal data, connected apps, Pages you manage, and network of trusting friends ripe for targeting. Scammers can impersonate you, spread malware, scam your connections, access financial accounts, steal info and more once in your profile.
What are some clear signals this is a phishing scam?
Dead giveaways include suspicious links, threats of immediate deactivation, poor grammar/spelling, requests for login credentials, unfamiliar sender profiles, and scam pages mimicking Facebook’s design with different URLs.
What should I do if I entered my password through the scam link?
If you were tricked into providing your login info, take immediate steps like changing your Facebook password, removing suspicious posts or friends, and contacting Facebook to report unauthorized access and regain control of your account. Also secure any other accounts linked to the compromised Facebook.
How can I better avoid this scam moving forward?
Carefully scrutinize messages, avoid unverified links, use strong unique passwords, enable two-factor authentication, check sender profiles, watch for poor grammar/spelling, and never provide your login credentials through third-party websites.
Can I block or report these fake deactivation messages?
Definitely report any phishing attempts to Facebook as spam/fraud. You can also adjust your account privacy settings to filter messages to friends only. Turn on login approvals as another barrier to account takeover.
Does Facebook really deactivate accounts without warning?
No, Facebook sends advance warnings well before applying temporary restrictions or disabling accounts. The threats of immediate permanent deactivation with no chance to appeal are a manipulation tactic used in this scam.
Staying informed is key to avoiding this frequent phishing scam. Recognizing the warning signs protects you and your sensitive account access credentials.
The Bottom Line
The supposed imminent account deactivation notice is a common phishing ploy to trick you into compromising your own login details out of fear. But armed with knowledge of this scam, you can ensure you never become a victim.
Scrutinize the claims of any messages about account violations, check sender profiles, avoid external links, and never provide your password outside of Facebook.com. Keeping your credentials secured eliminates the scammer’s power.
With proper precautions, you can confidently ignore these fake warnings about impending deactivation. Staying informed is the key to locking down your account and protecting your online presence.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.