


A revised contract is exactly the sort of document people expect to move quickly. The DocuSign Approval Email Scam uses that familiar workflow, adds a 24-hour deletion threat, and sends the recipient to a password-stealing imitation. The pressure feels procedural rather than theatrical, which makes the trap unusually effective.
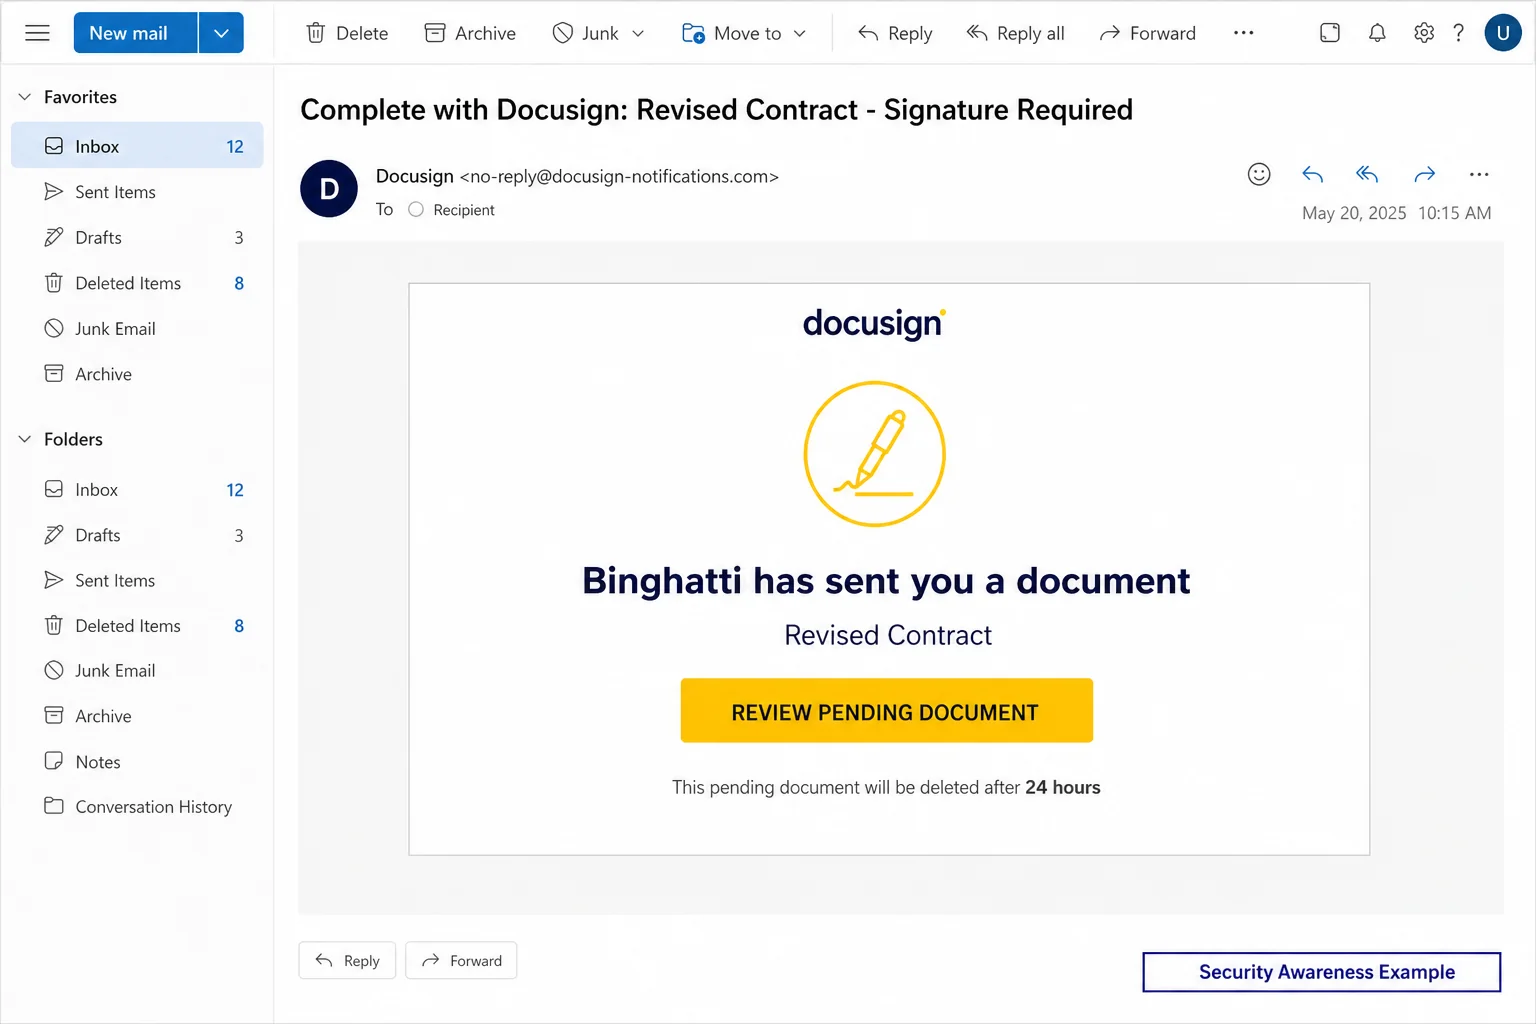
The subject reads “Complete with Docusign: Revised Contract – Signature Required.” Inside, the message claims Binghatti shared a revised contract and presents a large “REVIEW PENDING DOCUMENT” button.
A warning says the pending document will be deleted after 24 hours. That deadline is meant to make recipients review first and verify later, especially when contracts, property, procurement, or employment decisions may be time-sensitive.
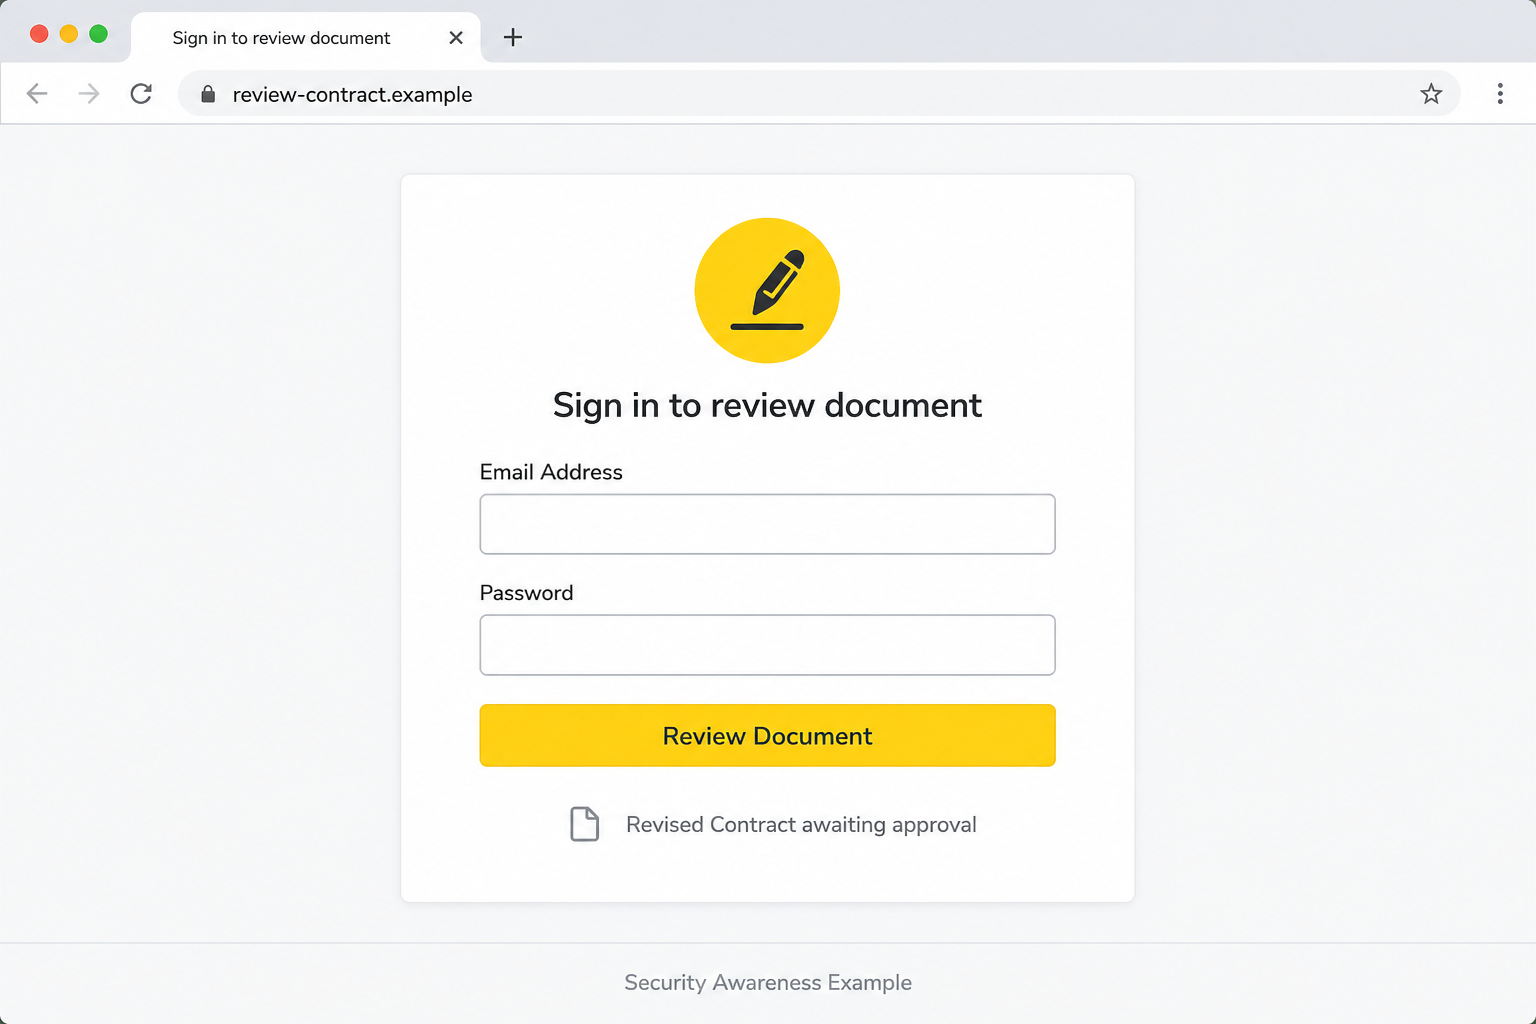
The analyzed button led to mail87[.]lookaware[.]top, not an official Docusign domain. The landing page closely imitated an electronic-signature login and requested an email address and password before showing any real contract.
Overview
A Familiar Contract Workflow Creates Trust
The subject resembles a normal electronic-signature request and describes a Revised Contract rather than a random file. That wording implies a business history the recipient may assume a colleague already knows.
Naming Binghatti gives the request a recognizable counterparty, while the lack of project details keeps the lure flexible. The recipient sees just enough context to wonder whether the agreement belongs to another department.
The claimed 24-hour deletion window discourages that department check. A contract can affect money, property, employment, or deadlines, so waiting to ask a question may feel riskier than opening it immediately.
The 24-Hour Deadline Blocks Verification
REVIEW PENDING DOCUMENT leads to mail87[.]lookaware[.]top, not to docusign.com or docusign.net. The copied signing interface begins only after the browser has already left the legitimate service.
The page asks for an email address and password before showing verifiable agreement details. A contract title carried in the phishing link can personalize the screen without any connection to a genuine Docusign envelope.
The Fake Login Can Expose Real Agreements
A stolen login may expose real agreements, parties, addresses, and signature history. If the password was reused for webmail, the intruder may also gain the conversations that explain what those documents mean.
That combined access supports convincing contract amendments, payment changes, and new signature requests. The fake revised contract is therefore a doorway into both document fraud and broader business impersonation.
Contract platforms also contain relationships that are difficult to reconstruct after an incident. A criminal who sees who signs, who reviews, and which projects are active can tailor later messages to the exact people most likely to approve a sensitive request. The attacker learns the approval chain before targeting it carefully.
- Subject used: Complete with Docusign: Revised Contract – Signature Required.
- Claimed sender: Binghatti.
- Document: Revised Contract.
- Button: REVIEW PENDING DOCUMENT.
- Pressure: the pending document will supposedly be deleted after 24 hours.
- Observed destination: mail87[.]lookaware[.]top, not an official Docusign domain.
How to Separate a Real Docusign Request From This Lure
The Domain Must Belong to the Expected Service
Docusign advises users to examine the sender and destination and to treat messages from unofficial domains cautiously. Official notification routes use Docusign-controlled domains, not arbitrary lookalike addresses. This check remains useful even when the message is beautifully formatted.
A copied logo or matching button color cannot repair the lookaware[.]top mismatch. The address bar is independent evidence that the recipient has left the genuine signing service. Review it before typing an email address, not after a password has been submitted.
Unexpected Documents Need Sender Verification
Even a technically genuine electronic-signature notification can contain an unwanted or abusive document. The recipient should know who sent the agreement and why approval is expected before opening it. Colleagues should also know which person owns the approval decision.
Contact Binghatti or the named business through an existing contract, saved contact, or official website. Do not use a telephone number or reply address supplied only by the questionable email. A short independent call can prevent a much longer account-recovery process.
A Security Code Offers a Safer Route
Docusign says recipients can open its official site directly and use the unique security code found in a legitimate notification to access a document. This avoids relying on the embedded review link and keeps the browser on a known domain.
Docusign also accepts suspicious impersonation emails at verify@docusign.com. Forwarding the message as an attachment preserves details that a screenshot or ordinary forward can lose, including routing information useful during verification.
How the DocuSign Approval Email Scam Works
Step 1: A Contract-Themed Notification Arrives
The campaign copies the rhythm of an electronic-signature email and uses a subject beginning Complete with Docusign. That familiar construction can pass a quick visual check.
The named sender, Binghatti, may be relevant to some recipients and meaningless to others. Broad campaigns count on curiosity, while targeted versions can select companies that fit the victim’s industry.
Step 2: A Revised Contract Suggests Existing Business
Calling the file Revised Contract implies there was an earlier negotiation, even when none occurred. Recipients may assume a colleague handled the first version or that the request belongs to another department.
The wording avoids specific clauses, parties, or project identifiers that could be disproved. The promised document remains hidden until after the recipient follows the attacker’s route.
Step 3: A 24-Hour Deletion Threat Forces the Pace
The DocuSign Approval Email Scam says the pending file will disappear after 24 hours. A reader may fear delaying a deal or asking an embarrassing question about a contract they should recognize.
Docusign safety guidance warns that urgency and unexpected documents are phishing indicators. A legitimate business partner can resend or confirm an agreement through a known channel.
Step 4: The Review Button Opens lookaware.top
Selecting REVIEW PENDING DOCUMENT moves the browser to mail87[.]lookaware[.]top. The presence of words such as mail or document would not make this an official signing host.
On mobile, the full domain can be easy to overlook. Expanding the address bar before entering anything reveals that the contract page is outside Docusign’s controlled domains.
Step 5: A Copied Sign-In Screen Requests Credentials
The landing page resembles a Docusign authentication form and asks for an email address and password. It may include a contract title so the transition from email feels continuous.
No real agreement is required for the page to display those details because they were already embedded in the phishing link. Submitting the form sends the credential to the scammer.
Step 6: The Page Hides Theft Behind an Error or Redirect
The imitation may claim the password is wrong, show a loading screen, or redirect to the real Docusign homepage. Each ending makes the interaction look like a temporary document problem.
A second password entry can help the operator correct a typo. A redirect to the real brand does not undo the transmission that occurred on the unrelated host.
Step 7: Stolen Access Fuels Document and Email Fraud
The attacker may test the credential against Docusign and the victim’s email provider. Reuse is especially dangerous because access to both services provides documents and the communication context around them.
Criminals can send fraudulent agreements, replace payment instructions, collect signatures on deceptive files, or use exposed identity details in later impersonation. The impact can extend well beyond one missing contract.
Company, Address, and Fulfillment Checks
Company: Confirm Binghatti Independently
Ask whether the recipient has a current relationship, named contact, and expected revised contract with Binghatti. Use contact details from existing records or the company’s official site.
If nobody can identify the request, do not treat the brand name as proof. A real organization can be impersonated without its systems being involved.
Address: Use Docusign’s Official Domains
Inspect both the sender address and link destination. Docusign identifies docusign.com and docusign.net as official domains and warns about lookalike links.
The observed lookaware[.]top host fails that check. Report it rather than attempting additional passwords or trying alternate buttons on the same page.
Support: Verify or Report the Email
Forward a suspicious Docusign impersonation email as an attachment to verify@docusign.com. Business users should also notify their internal security team so other recipients can be protected.
For a legitimate notification, open docusign.com directly and use the Access Documents feature with the security code from the email. This creates a safer path than the embedded link.
Fulfillment: Match the Agreement and Parties
A real revised contract should match an earlier draft, project, counterparty, and approval process. Ask the contract owner to confirm the version and expected signer.
The phishing page cannot provide that evidence before authentication. Its password form is not contract fulfillment; it is the point where the attacker collects access.
Warning Signs in a Fake DocuSign Approval Email
Electronic-signature phishing can be visually accurate. The strongest checks are whether the agreement is expected and whether the domain remains within Docusign’s real service.
- The recipient was not expecting a revised contract from Binghatti.
- The email threatens deletion after 24 hours to discourage verification.
- REVIEW PENDING DOCUMENT leads to lookaware[.]top or another unofficial domain.
- The landing page asks for credentials before showing verifiable agreement details.
- The sender address differs subtly from docusign.com or docusign.net.
- No project owner, counterparty, or earlier contract version can confirm the request.
- The message lacks a usable security code for access through the official Docusign site.
Do not approve a contract merely because the interface looks familiar. A real agreement has people, history, and a known business purpose that can be confirmed without the email’s button.
What to Do if You Have Fallen Victim to This Scam
If the imitation sign-in page received your password, act before the attacker can open real envelopes or test the same credential elsewhere. Use official sites and known support channels only.
- Change the affected Docusign or email password. Open the official service manually and choose a unique replacement. Explain that the DocuSign Approval Email Scam captured the previous credential.
- Revoke sessions and connected applications. Sign out other devices, remove unfamiliar integrations, and check whether the account created or sent any envelopes you do not recognize.
- Enable strong multifactor authentication. Prefer a passkey or security key when supported. Reject unexpected prompts and remove recovery methods or authenticators added by someone else.
- Review exposed agreements and recipients. Identify documents opened, downloaded, changed, or sent after the click. Notify contract owners and counterparties through verified channels if confidentiality or signature integrity may be affected.
- Secure the connected mailbox. Change its password if reused, revoke mail sessions, and inspect forwarding rules, delegates, and OAuth applications. Email access can let the criminal reset the Docusign account again.
- Warn finance, legal, and procurement teams. Require independent confirmation for contract amendments, bank-detail changes, and urgent approvals. Provide the campaign subject and defanged destination.
- Run Malwarebytes if anything downloaded or installed. The observed page targeted credentials, but a variant may add a file or extension. Update Malwarebytes, perform a full scan, and retain the results.
- Use AdGuard as an additional web defense. AdGuard may block known phishing hosts, ads, and redirectors. It cannot revoke submitted credentials or guarantee detection of a new lookalike domain.
- Report the impersonation to Docusign. Forward the complete email as an attachment to verify@docusign.com or use Docusign’s Report Abuse process. Notify internal security as well.
- Preserve a complete incident record. Keep headers, URLs, screenshots, access logs, affected envelope IDs, and support case numbers. Report financial loss or identity misuse to the appropriate authorities and insurer.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Docusign connected to this revised contract email?
No. The campaign impersonates Docusign and sends users to an unrelated lookaware[.]top host. The legitimate company did not create the phishing page described here.
Can a real Docusign document expire?
Envelope access and sender settings can vary, but an unexpected 24-hour warning must be verified. Open docusign.com directly or contact the sender through a known channel.
Which domains does Docusign use for official email and links?
Docusign advises users to look for its official docusign.com and docusign.net domains. Similar spelling, extra words, or another ending should be treated cautiously.
How can I open a document without clicking the email button?
Go directly to docusign.com and use Access Documents with the unique security code found in a legitimate notification. If no usable code or expected request exists, verify with the sender.
Where should I report a suspicious Docusign message?
Forward the email as an attachment to verify@docusign.com or use the Report Abuse option. Business recipients should also alert their security team.
What if the password was reused for my email account?
Change both accounts immediately from a clean device, revoke sessions, and review the mailbox for forwarding rules and password-reset activity. A reused credential expands the incident.
The Bottom Line
The DocuSign Approval Email Scam uses a believable revised-contract workflow and a 24-hour deletion warning to move recipients onto an unrelated login page. The business name and copied interface are not substitutes for an expected agreement and official domain.
Confirm the sender and contract through known records, or access a legitimate document from docusign.com with its security code. If lookaware[.]top or another imitation received your password, revoke access and report the campaign immediately.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.