

A message announcing that your mailbox has been restricted can turn an ordinary morning into an urgent problem. Missing one important email suddenly feels expensive.
The notice offers a convenient verification button, but convenience is exactly what deserves scrutiny. Real account problems can be checked without following an unsolicited warning.
Overview
The warning presented to the recipient
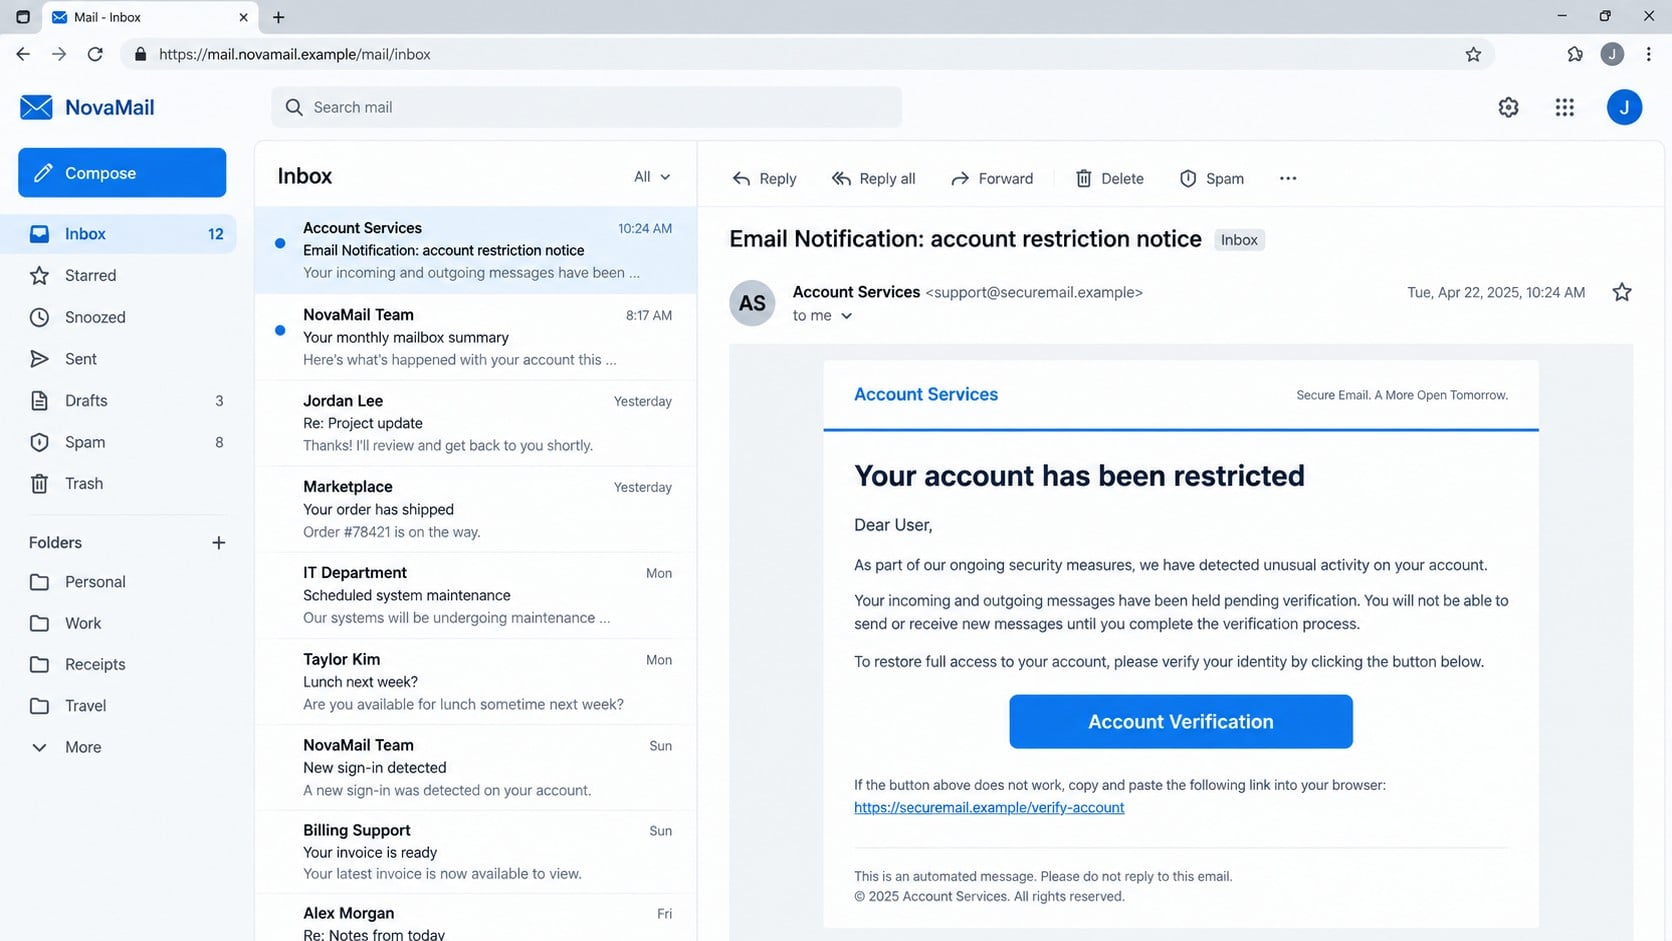
The phishing email says the recipient’s account has been placed on restriction. It claims both incoming and outgoing messages are being held.
An observed version used the subject “Email Notification: account restriction notice” with extra punctuation intended to make the warning appear urgent.
The body instructs the user to complete verification before normal delivery resumes. A button labeled “Account Verification” provides the supposed remedy.
No meaningful explanation is provided for the restriction. The message depends on the recipient worrying about unseen mail rather than asking what triggered the action.
The credential page hidden behind the button
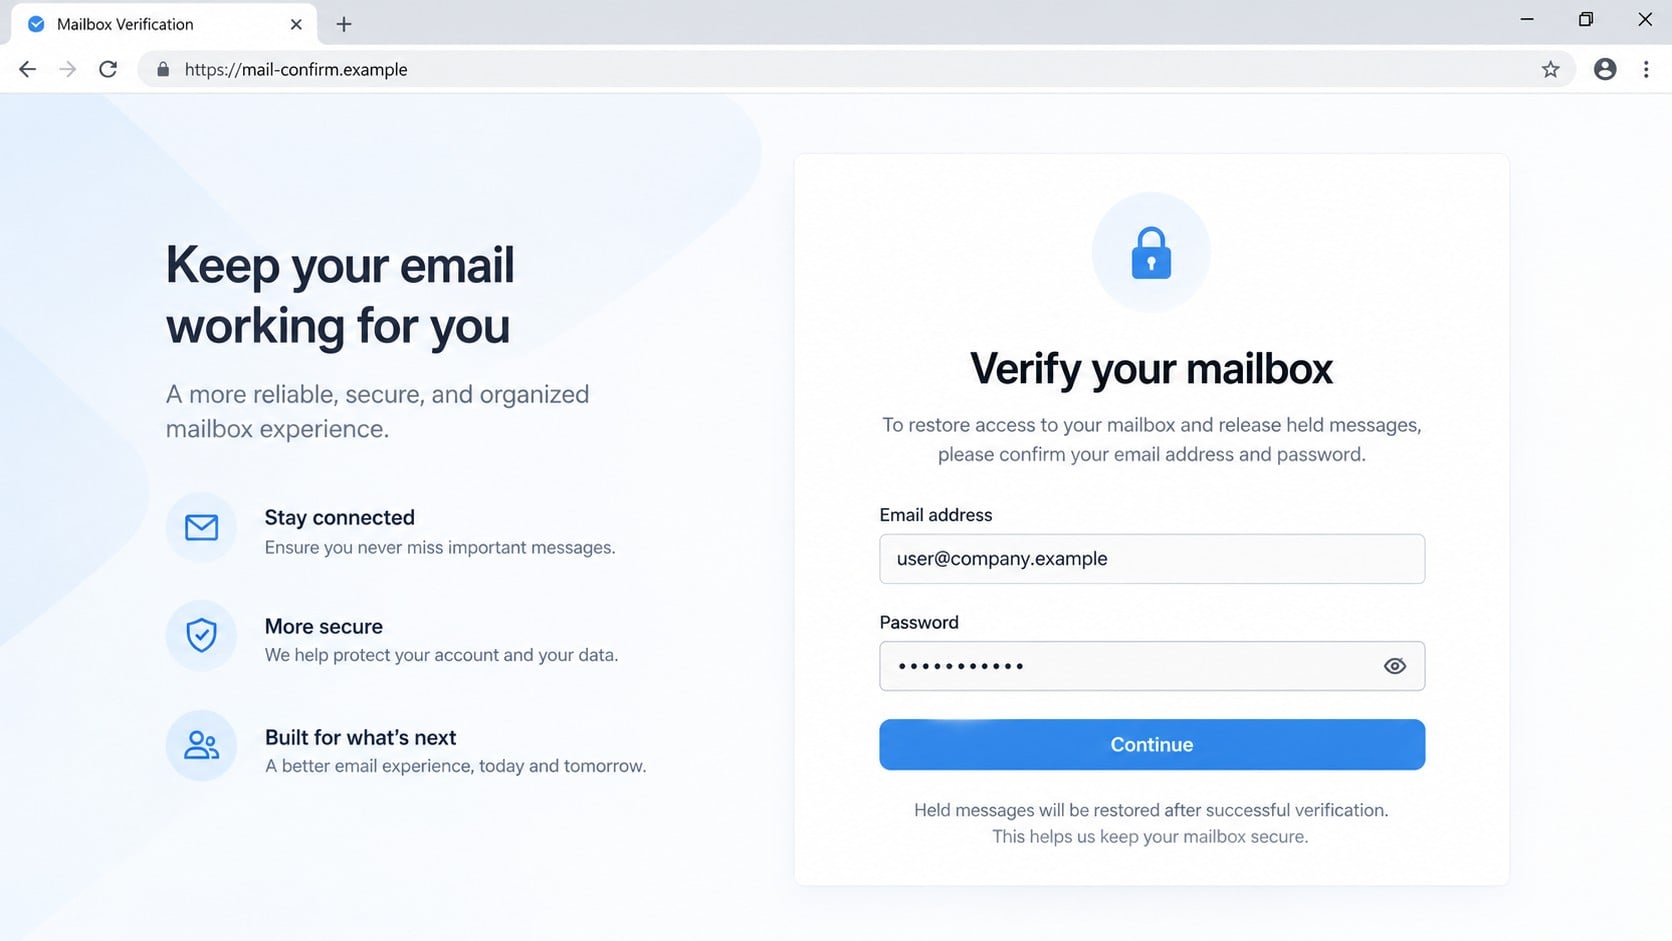
The button does not open a recognized email provider. In the analyzed campaign, it led to a compromised food-related website hosting a counterfeit settings portal.
That unrelated domain had no legitimate role in managing the recipient’s mailbox. Its presence was decisive evidence that the verification story was false.
The page displayed the email address automatically and asked for its password. Prefilling one field made the portal look connected to the account.
Any password submitted there could be collected by the operator. The form was not repairing delivery, releasing messages, or confirming ownership with a real provider.
Clues that the restriction notice cannot be trusted
The email uses broad administrative language so it can target many providers. It avoids naming a specific policy violation, quota, server, or support case.
- The warning arrives unexpectedly and threatens disruption to everyday communication.
- The sender domain does not match the organization managing the mailbox.
- The message cannot identify which emails were supposedly held.
- The verification link opens an unrelated or compromised website.
- The page asks for a mailbox password outside the provider’s login domain.
- The footer offers no verifiable support channel or account-specific reference.
A restriction is an account state, not something established by an email graphic. The authenticated provider dashboard remains the authoritative place to check it.
Why the Held-Mail Claim Creates So Much Pressure
Email is tied to work approvals, reset codes, orders, travel details, medical messages, and family communication. A delivery interruption can affect several parts of life.
The scam exploits uncertainty rather than showing a concrete loss. Recipients cannot see which incoming messages they might be missing.
That ambiguity lets the imagination do the persuading. A worker thinks about a client response, while a shopper remembers an order confirmation.
The message also presents one immediate route back to normal service. Clicking feels faster than locating the provider’s real support area.
Unlike a dramatic account-closure threat, “restriction” sounds temporary and administrative. That softer wording can pass beneath a user’s usual scam defenses.
The promise to release held messages makes password entry seem procedural. In reality, email services do not restore delivery through forms on unrelated websites.
Attackers can reuse the same layout with different provider names. Only the sender line, colors, and button destination need to change.
Compromised legitimate sites are useful hosts because their domains may be older than newly registered phishing addresses. Age still does not make the inserted page trustworthy.
How Real Mail Restrictions Usually Differ
Legitimate providers can limit sending after unusual activity, spam complaints, failed billing, policy violations, or storage exhaustion. Their notices contain usable account context.
A storage warning normally shows the current quota and directs users into existing account settings. It does not ask for a password on another business’s website.
A security lock may require identity recovery. The process begins on the provider’s established domain and uses known recovery methods, not a generic embedded form.
Business mail restrictions often generate an administrative ticket or alert visible to IT staff. The help desk can inspect service status without needing the employee’s password.
Sending limits can produce specific error codes. Those codes help administrators diagnose reputation, authentication, or rate problems with the outgoing server.
By contrast, the scam gives no server name, policy event, affected time, or error identifier. Vagueness allows one template to fit every recipient.
Real support teams should never ask users to disclose their current password. Verification can occur through reset links, multifactor challenges, and authenticated support sessions.
Providers also publish incident dashboards. When many users experience disruption, a status page can confirm a service problem without interacting with suspicious mail.
Small organizations using hosted email may route notices through an administrator. Staff should know the approved channel and recognize deviations from it.
A warning that combines outgoing restrictions with held incoming messages sounds comprehensive. Technically broad claims often conceal the absence of any genuine diagnostic detail.
The phrase “account verification” is equally nonspecific. It fails to explain what identity evidence is missing or why normal authentication suddenly became insufficient.
Recipients can compare the message with earlier legitimate provider alerts. Differences in sender domain, terminology, footer, and account references become easier to see.
Organizations should maintain an internal page describing common mail alerts and reporting steps. Familiar procedures reduce the appeal of an attacker’s convenient button.
When an employee reports the phish, administrators can search for the same link and subject across mailboxes. Rapid removal limits further credential submissions.
They should also examine whether the hosting site is compromised. A legitimate site owner may need notice so the inserted phishing content can be removed.
Users do not need to determine why the page exists before rejecting it. A domain with no authority over the mailbox is enough reason to stop.
This approach avoids guessing from design quality. A crude page and an excellent copy both fail when their origin cannot manage the claimed account.
Independent account access turns an emotional warning into a testable statement. If normal mail works and no portal alert exists, the email’s story collapses.
How the Scam Works
Step 1: A generic security notice lands in the inbox
The recipient sees a brief message claiming the mailbox has limited functionality. It may arrive at a personal address or an employee account.
The display name can resemble “Account Services,” “Webmail Administrator,” or “Email Support.” Those labels describe roles but identify no accountable organization.
Automated delivery allows the campaign to reach many domains. Generic wording prevents obvious contradictions when different recipients use different providers.
Step 2: The email invents held incoming and outgoing mail
The warning says messages are waiting or cannot leave the account. It offers no headers, senders, timestamps, or administrative event supporting that assertion.
This invisible queue is impossible to evaluate from the email. The user must either believe the notice or inspect the real account elsewhere.
Scammers expect urgency to win. People who depend on email for work may prioritize restoring service before examining the technical details.
Step 3: The verification button crosses into an unrelated domain
The call-to-action points away from the mail provider. A redirect may briefly pass through another page before reaching the credential form.
In one documented route, the fraudulent portal appeared under a domain associated with food rather than email. That mismatch had no reasonable service explanation.
A padlock in the browser does not fix the mismatch. Encryption can protect a connection to a criminally controlled or compromised webpage.
Step 4: A fake settings portal requests the password
The landing page imitates a neutral webmail control panel. It may use envelope icons, blue buttons, and language about mailbox synchronization.
The recipient’s address may already appear in the form because it was encoded in the link. This simple feature creates an illusion of account awareness.
The password field is the real objective. Entering it sends valuable authentication data to an unauthorized party.
Step 5: The page conceals a successful theft
After submission, the portal may show “incorrect password,” spin indefinitely, or claim that verification completed. None of those messages reflects the real mailbox.
Requesting the password twice can help capture a corrected version. Redirecting afterward can prevent the victim from noticing that the original domain was unrelated.
The supposed held messages never appear because there was no mail queue connected to the page.
Step 6: The attacker enters the real account
Captured credentials can be tested against common email platforms. If multifactor authentication is absent, the operator may gain immediate mailbox access.
Once inside, criminals can read private conversations, reset other accounts, locate financial records, or identify people likely to trust a follow-up.
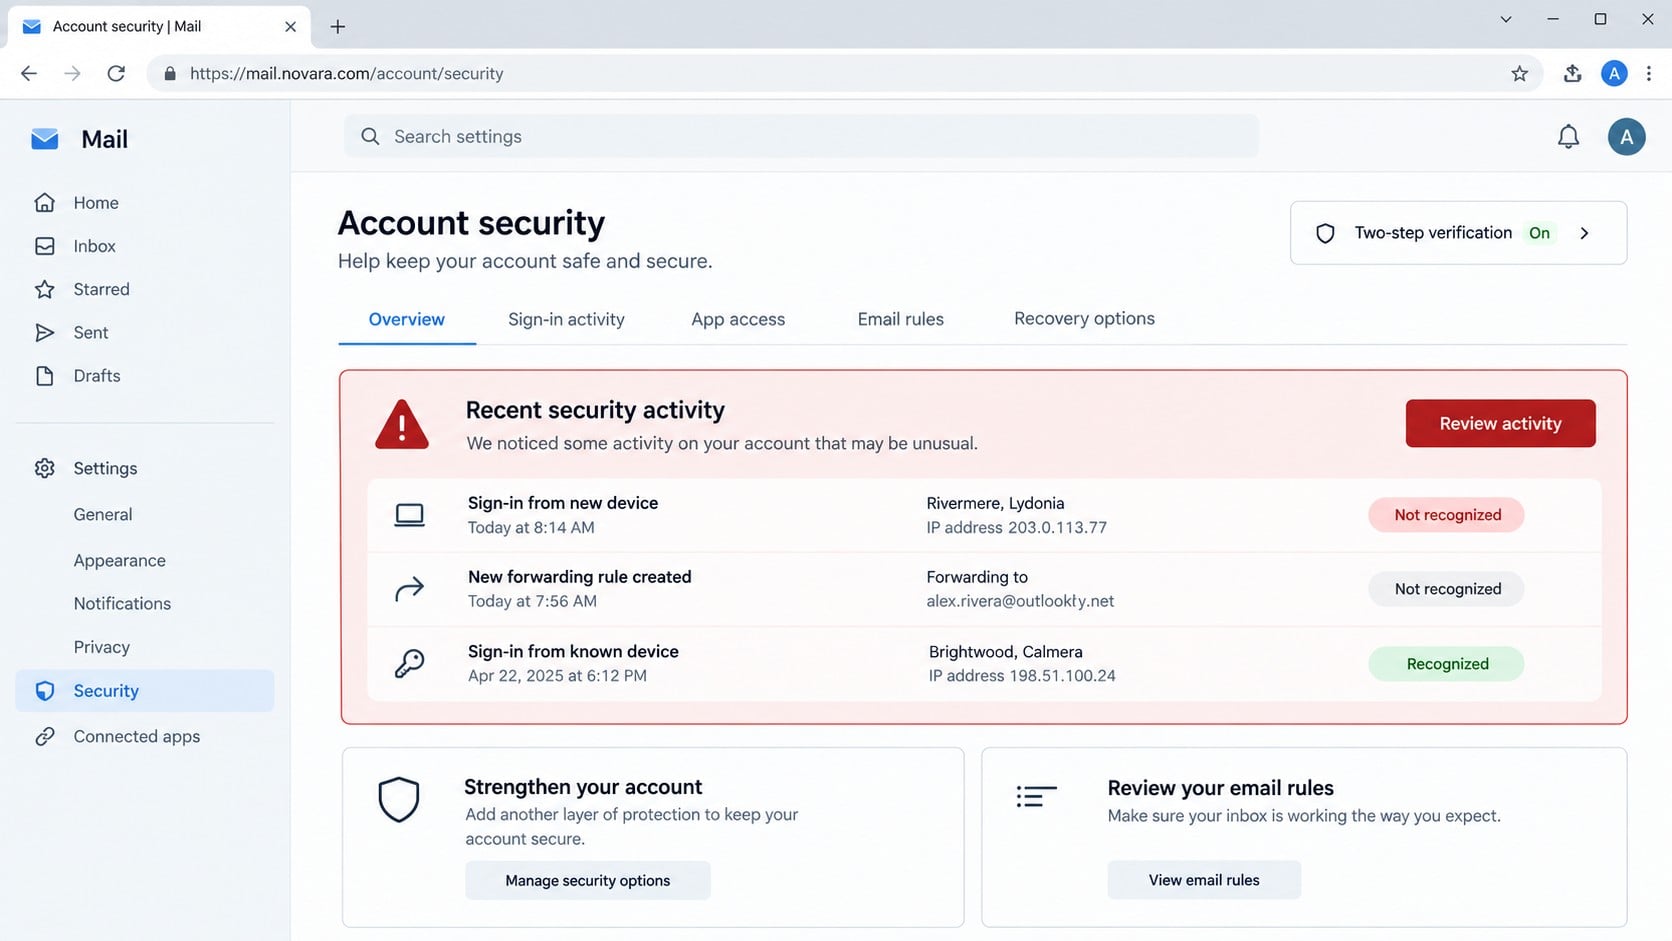
They may establish persistence through forwarding rules, app passwords, recovery changes, connected applications, or active sessions.
Step 7: Mailbox control enables secondary fraud
A compromised account can request invoice changes, send malicious files, steal reset codes, or impersonate the owner during an active conversation.
Attackers sometimes watch quietly before acting. They wait for a payment discussion or sensitive request where one believable message can produce greater value.
The original restriction email may disappear into deleted items. The lasting risk comes from the access and settings changes created afterward.
Provider, Mailbox, Domain, and Login Verification Checks
Check service status from the provider’s real portal
Open the email service through a bookmark, official application, or manually typed address. Do not use the notification’s button.
Look for banners, quota notices, security alerts, and administrative messages inside the authenticated account. A genuine restriction should be visible there.
Business users can ask their IT help desk whether any policy or service incident affects the mailbox. Use a known internal number or portal.
Review the mailbox behavior directly
Send a harmless test message to a trusted account and ask that person to reply. Do not use sensitive content during this check.
Inspect the outbox, sent folder, and any provider error details. Actual delivery failures usually generate specific codes rather than vague warnings.
Storage limits can affect mail, but the solution belongs inside account settings. A third-party website should never receive the password.
Compare sender and destination domains
Reveal the full sender address and inspect the button destination without opening it. Both should make sense for the organization providing the service.
Misspellings, extra subdomains, unrelated businesses, and raw numerical addresses are serious warning signs. Branding cannot compensate for an incorrect domain.
If the link uses a compromised legitimate site, search its visible purpose. A restaurant or retail domain cannot verify a corporate mailbox.
Use a known login route and password manager
Password managers associate credentials with specific origins. Refusing to autofill on a page can expose a domain change that visual imitation hides.
Still inspect the address manually. Users can override autofill, and a compromised device or malicious extension can create additional risks.
When uncertain, close the page completely. Starting from the official service is faster than recovering an account after credential theft.
What to Do if You Have Fallen Victim to This Scam
- Leave the fraudulent portal. Close the page and avoid entering additional information. Record its address only if you can do so safely.
- Reset the mailbox password officially. Use a trusted device and the provider’s real account page. Choose a unique credential unrelated to previous passwords.
- Sign out other sessions. Remove unfamiliar devices and terminate active browser sessions so captured credentials cannot support continuing access.
- Activate multifactor authentication. Prefer a passkey, hardware security key, or authenticator application. Never approve an unexpected sign-in prompt.
- Audit every mailbox setting. Inspect forwarding, inbox rules, delegates, aliases, connected apps, recovery details, and app passwords for unauthorized additions.
- Check account activity and sent mail. Identify messages opened, deleted, forwarded, or transmitted during the exposure window. Save evidence before removing suspicious changes.
- Contact workplace security. Administrators can revoke tokens, examine audit records, block the campaign, and assess whether organizational information was accessed.
- Secure accounts using the same password. Replace reused credentials immediately, starting with recovery, financial, social, and cloud-storage services.
- Run a device health check. If downloads or additional prompts appeared, perform a complete Malwarebytes scan and follow up on every verified detection.
- Add a protective filtering layer. AdGuard can stop many known phishing destinations and malicious redirects, while cautious independent verification remains essential.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Can an email provider really restrict an account?
Yes, providers can limit accounts for security, storage, billing, or policy reasons. Confirm the status inside the official account portal, not through an unsolicited link.
Are messages actually being held by this email?
The phishing notice cannot hold mail. Its claim is invented to create pressure, and the counterfeit page has no connection to the mailbox queue.
Why was my address already shown on the page?
The sender can place an encoded address in each link. The landing page reads that value and displays it without accessing your account.
Does HTTPS mean the verification portal is safe?
No. HTTPS encrypts traffic between you and the site. Phishing operators can obtain certificates for their own domains or abuse compromised HTTPS websites.
What if I entered a password but multifactor authentication is enabled?
Change the exposed password anyway, deny unfamiliar prompts, review sessions, and inspect connected applications. Some attacks attempt to capture approval codes or session tokens.
Will deleted phishing mail remove the danger?
Deleting the message prevents another click, but it cannot undo submitted credentials or account changes. Complete the security steps before considering the incident resolved.
The Bottom Line
The email account restriction notice invents a delivery problem, then directs worried recipients to an unrelated website designed to capture mailbox passwords.
Check restrictions from the provider’s real portal and involve IT when appropriate. Mail access should never be restored through a password form reached from an unexpected email.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.