


An unexpected confidentiality agreement can feel important enough to interrupt your day. The message may even resemble an ordinary document notification from a colleague.
That professional appearance deserves a careful second look. A single detail outside the email often reveals whether the file invitation belongs in your workflow.
Overview
What the NDA Agreement email claims
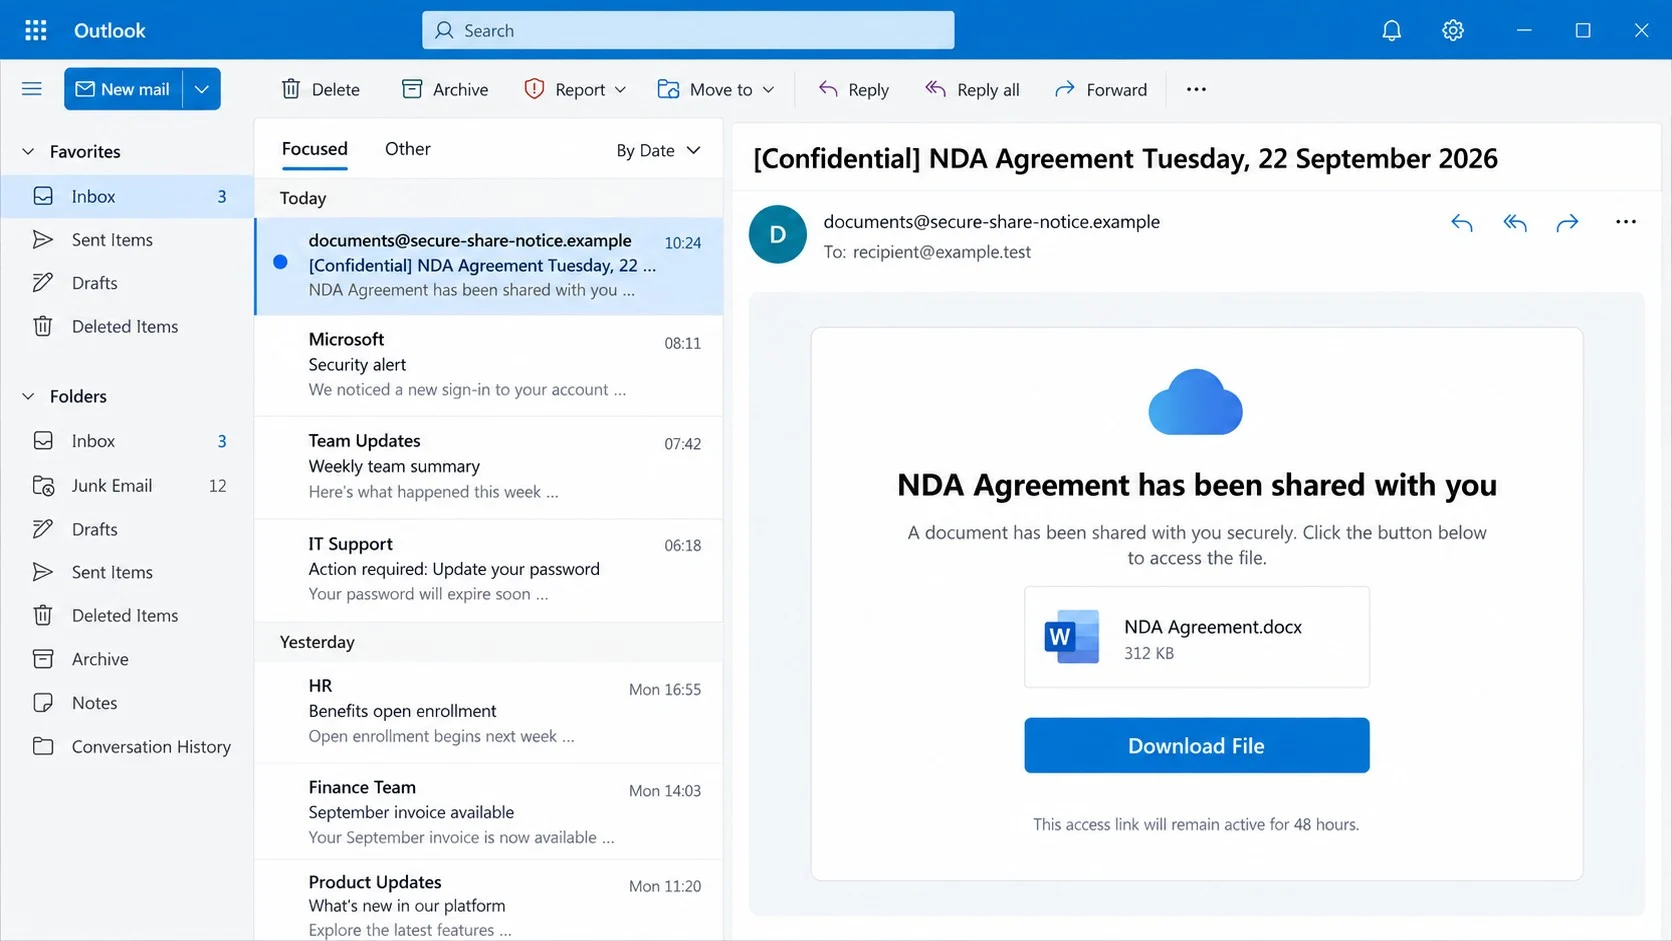
The message says someone has shared a confidential nondisclosure agreement with you. It presents the file as a Word document requiring prompt review.
One observed version used the subject “[Confidential] NDA Agreement” followed by a date. The body described a 312 KB file named “NDA Agreement.docx.”
The invitation also claimed its access link would remain active for 48 hours. That deadline quietly discourages recipients from checking the request independently.
A polished card, familiar document icon, and restrained business language make the email look routine. Nothing in the design initially resembles an obvious lottery scam.
What the sender is really trying to obtain
The file notice is bait. Its link can lead to a counterfeit document portal that asks for Microsoft, Google, or company email credentials.
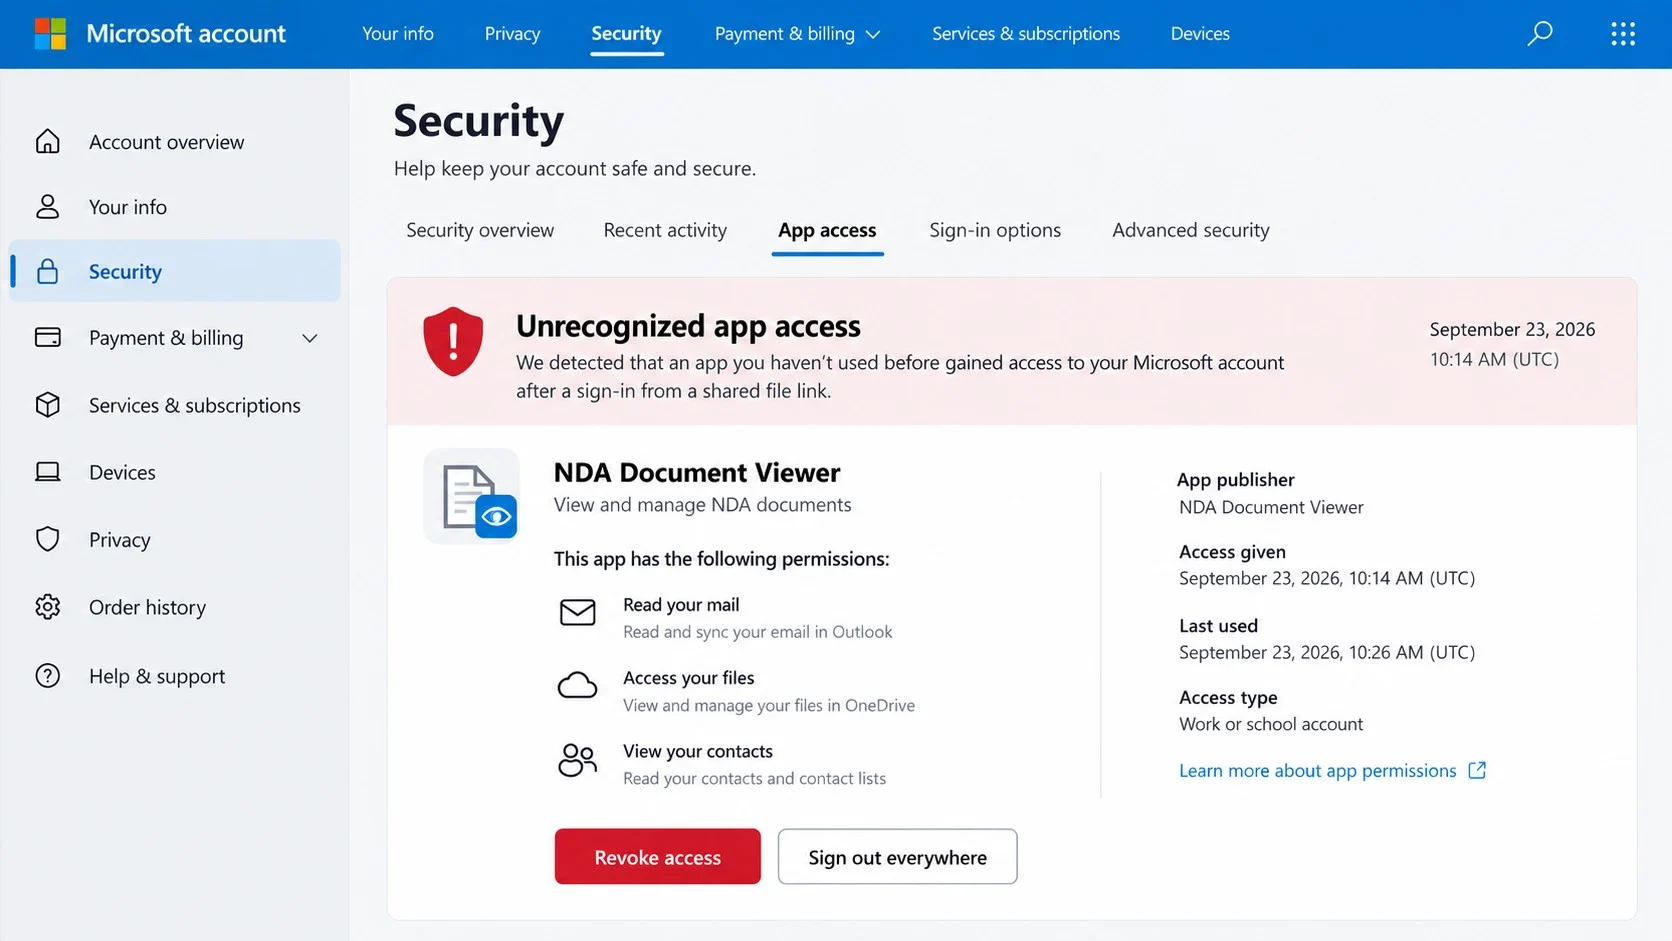
Some campaigns instead request permission for a rogue cloud application. Granting that access can expose mail, contacts, files, and other connected information.
The exact destination may vary between deliveries. One recipient can see a password form while another encounters a consent screen or redirected login.
That flexibility lets criminals replace blocked pages quickly. The business pretext remains recognizable even when the underlying phishing infrastructure changes.
Warning signs worth noticing immediately
A genuine NDA normally follows a conversation, negotiation, hiring process, or vendor relationship. A document arriving without that context should be treated cautiously.
- The sender is unfamiliar or uses a domain unrelated to the supposed organization.
- The greeting does not identify the project, company, or person who requested the agreement.
- The access link expires quickly and creates pressure to act before confirming the request.
- The button leads away from the document service named in the message.
- The page asks for a password after the account is already signed in elsewhere.
- The consent screen requests broad mailbox, contact, or cloud-file permissions.
Any one clue deserves verification. Several appearing together strongly suggest the invitation was assembled to capture access rather than deliver a legal document.
Why a Confidential Document Is Effective Bait
Nondisclosure agreements carry social weight. Recipients may worry that ignoring one could delay employment, a contract, a partnership, or an internal assignment.
Confidentiality also discourages casual discussion. A target might hesitate to ask coworkers about a document labeled private, giving the scammer more room to operate.
The file name sounds ordinary enough to avoid suspicion. Unlike a prize notice, an NDA fits naturally into many professional inboxes and shared-document systems.
The scam does not need an elaborate story. It only needs the recipient to believe that opening the document is a normal part of business.
Attackers sometimes research public job titles or company pages before sending these messages. A legal, sales, finance, or human-resources employee becomes a plausible target.
Other deliveries are broad campaigns with generic language. They rely on chance, knowing that many organizations exchange agreements every week.
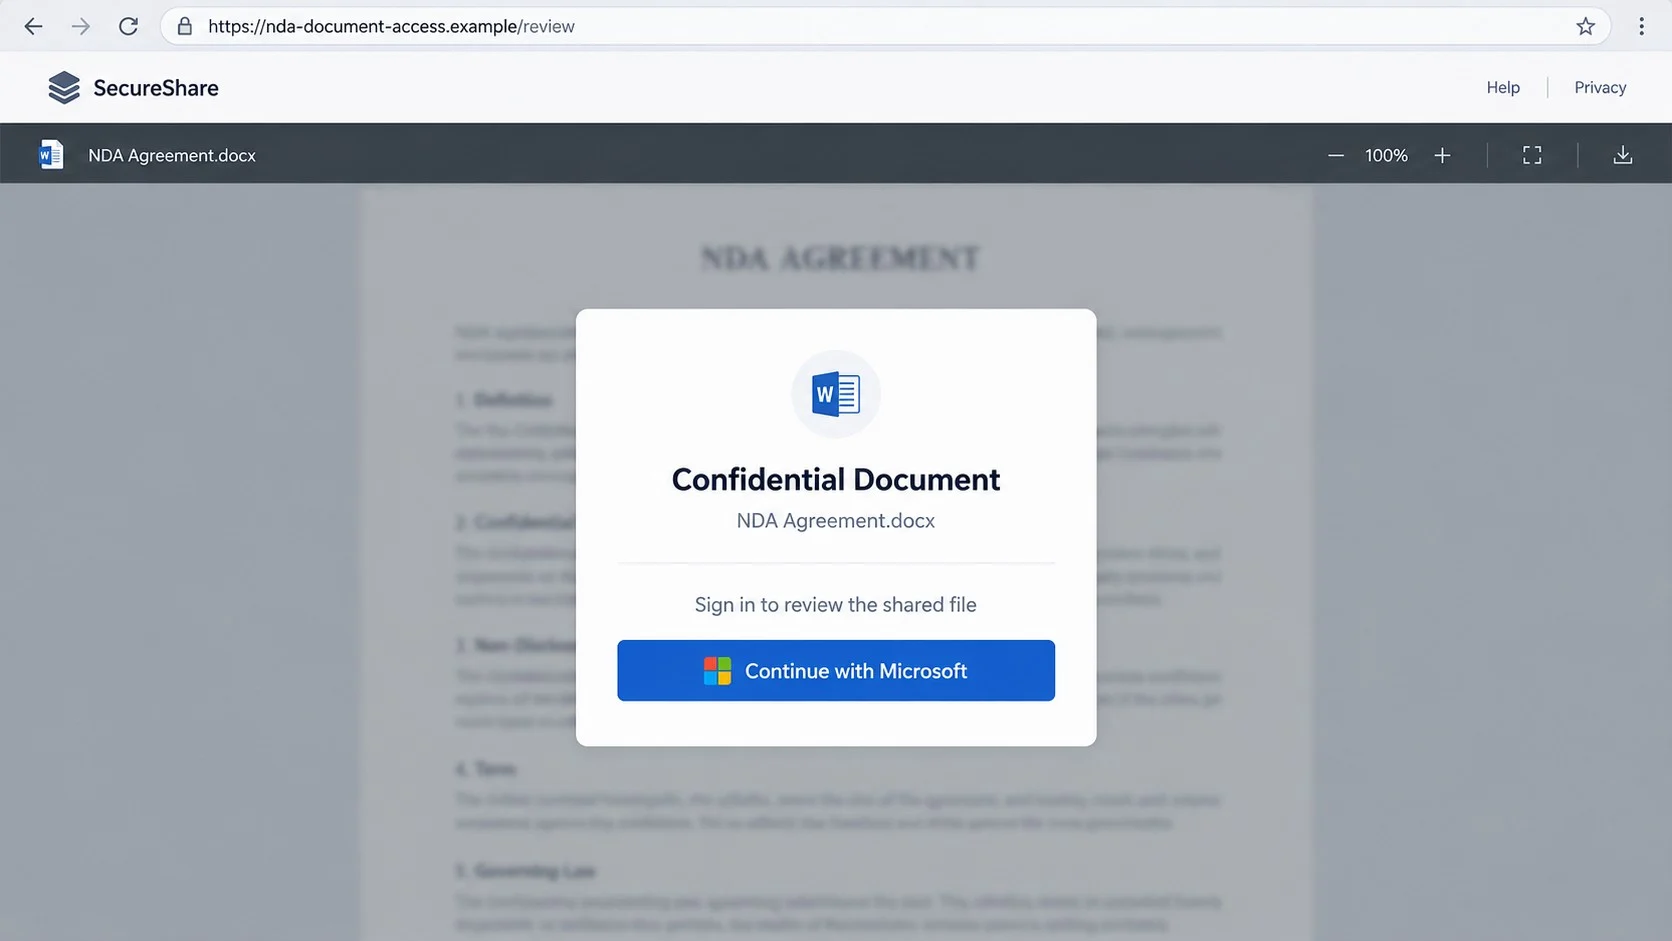
The label “confidential” makes a blank preview seem reasonable. It also provides an excuse for placing an authentication wall in front of the supposed file.
Real document services may require sign-in, so the presence of a login page alone proves little. The domain and sign-in path provide the meaningful evidence.
Different Login Paths Used by NDA Phishing Campaigns
Not every copy ends at an identical form. Campaign operators test several authentication stories and keep whichever version avoids filters longest.
A basic page presents two empty fields and a Microsoft-style button. The submitted address and password travel directly to infrastructure controlled by criminals.
A more polished version first asks which email provider the recipient uses. Selecting one changes the colors and branding on the next screen.
Another version displays a genuine identity-provider window but requests authorization for an unfamiliar application. The danger lies in the permissions being granted.
Consent phishing can succeed without collecting the current password. An approved application receives tokens that permit actions listed on the authorization screen.
Read-mail permission can expose conversations. Send-mail permission can turn the account into a convincing distribution point for additional NDA invitations.
Offline access may allow the application to continue operating when the user is not actively signed in. That scope deserves particular scrutiny.
Some pages request a one-time authentication code after the password. Entering that code can help an attacker complete a live sign-in.
Others display a QR code and claim scanning is required to unlock the document. The code may initiate device registration or another authentication flow.
These variations explain why memorizing one screenshot offers limited protection. The stable elements are the unexpected agreement, urgency, and unverified authentication request.
A legitimate document owner can explain the signing platform and resend access safely. Scammers avoid independent conversation because it breaks their manufactured context.
Organizations should document which signing services they approve. Employees can then recognize when an NDA arrives through a platform outside established legal workflows.
Conditional-access policies can reduce exposure by blocking risky sign-ins and unapproved applications. They still depend on staff reporting the original lure quickly.
Administrators should preserve message headers, destination addresses, application identifiers, and sign-in logs. Together, those records show which attack path actually occurred.
Victims should describe precisely what they entered or approved. A password submission, consent grant, code entry, and file download require different containment actions.
That distinction matters more than the page’s logo. Incident response should follow observed actions and account evidence, not assumptions about a familiar-looking screen.
How the Scam Works
Step 1: A businesslike NDA notification reaches the inbox
The campaign begins with an email that resembles an automated file-sharing alert. Its wording is brief, neutral, and designed to avoid classic spam signals.
The sender may use a stolen mailbox, a recently registered domain, or a display name that hides the real address until expanded.
The subject often emphasizes confidentiality. It may include the current date, a document reference, or a familiar phrase such as “shared with you.”
Those details give the message administrative texture without proving that any legal agreement actually exists.
Step 2: The invitation creates a narrow window for action
The recipient is told that access expires within 24 or 48 hours. This artificial limit makes postponing the task feel risky.
A workplace user may click quickly to avoid appearing unresponsive. The scammer benefits whenever urgency replaces a direct call or separate message.
The email may also imply that the sender can see whether the document was opened. That suggestion adds subtle pressure without making an explicit threat.
Step 3: The document button leads away from the expected service
The visible button might say “View Agreement,” “Open Document,” or “Review NDA.” Its destination is the critical detail hidden beneath the label.
A shortened link can pass through tracking services before reaching a phishing site. Redirects make the final address harder to recognize from the email.
On a desktop, hovering may reveal the destination. On mobile, holding the link can show a preview, but opening it remains unnecessary for verification.
Step 4: A counterfeit viewer displays a protected-file prompt
The landing page imitates a cloud document portal. It may show a blurred agreement, page thumbnails, or a lock icon behind the sign-in box.
The visual preview exists to complete the story. It does not prove that the promised NDA is stored behind the prompt.
Some pages prefill the victim’s email address from information embedded in the link. That personalization can make the fraudulent form seem connected to the mailbox.
Step 5: The victim enters credentials or approves permissions
A password form sends the submitted details to the operator. It may then report an error and redirect to a legitimate website.
That redirect reduces immediate suspicion. The recipient may assume the document failed to load while the stolen password is already being tested.
An OAuth-style version works differently. It asks the user to authorize an application rather than directly typing a password into an unfamiliar form.
Approving broad permissions can give the application continuing access. Changing the account password alone may not remove that authorization.
Step 6: The stolen access is used inside the mailbox
Criminals may search messages for invoices, payroll details, contracts, tax documents, or conversations that can support a more targeted fraud.
They can create forwarding rules, hide security notices, or send new phishing messages from the compromised account to trusted contacts.
A real mailbox makes the next NDA invitation far more persuasive. Recipients recognize the sender and may see genuine conversation history around the malicious reply.
Step 7: The campaign expands through trusted relationships
Compromised accounts can be used for business email compromise, invoice redirection, payroll changes, or additional document-sharing attacks.
The original NDA may never be mentioned again. Its purpose was simply to obtain a foothold that criminals can monetize in several ways.
Organizations can therefore see multiple victims from one initial click. The damage grows when stolen access is treated as an isolated password mistake.
Sender, File, Domain, and Permission Verification Checks
Inspect the complete sender address
Expand the sender details instead of trusting the display name. Compare every character in the domain with the organization’s verified website.
A free mailbox or unrelated domain is a strong warning. A familiar domain is not absolute proof because legitimate accounts can be compromised.
Contact the supposed sender through a phone number, chat, or email thread you already trust. Do not reply using contact details supplied by the invitation.
Confirm that the agreement belongs to a real transaction
Ask which project requires the NDA, who requested it, and which legal entity is involved. A genuine sender should answer those basic questions clearly.
Check internal contract systems or speak with legal staff before opening anything. Unexpected confidentiality documents should have a traceable business reason.
If the sender claims to be a recruiter, verify the vacancy on the employer’s official careers page and contact that employer independently.
Examine the link and document path
A legitimate sharing link should use the documented domain of the relevant service. Misspellings, extra words, and unrelated hosting domains are not cosmetic differences.
Do not rely on a padlock icon. HTTPS only encrypts the connection to the site; it does not certify that the operator is trustworthy.
Open the real cloud service from a saved bookmark or typed address. If the document is genuine, it may appear within your authenticated account.
Read every permission request before approving it
A viewer should not need unrestricted access to read mail, send messages, manage contacts, or browse unrelated files.
Check the application name, publisher status, requested permissions, and verified domain. Cancel when those elements do not match the expected document provider.
Organization administrators should review enterprise application grants. A rogue app can remain useful to an attacker after the victim changes a password.
What to Do if You Have Fallen Victim to This Scam
- Disconnect from the phishing page. Close its tabs and stop interacting with any downloaded document. Do not submit another password after an error message.
- Change the affected password from a clean device. Use the provider’s official website, choose a unique replacement, and update every account where the old password was reused.
- Revoke suspicious application access. Review connected apps, OAuth grants, mailbox add-ins, and active sessions. Remove anything you do not recognize before assuming the account is safe.
- Turn on multifactor authentication. Prefer an authenticator app, security key, or passkey. Save recovery codes somewhere separate from the email account.
- Inspect mailbox rules and recovery settings. Delete unknown forwarding rules, delegates, filters, recovery addresses, and phone numbers. Check sent and deleted folders for activity.
- Notify your organization quickly. Security staff can review sign-in logs, revoke tokens, warn contacts, and determine whether confidential documents or shared drives were accessed.
- Warn people who received messages from your account. Tell them the NDA invitation may be fraudulent and ask them not to open its links.
- Scan the device if anything was downloaded. Run a full Malwarebytes scan and quarantine confirmed threats. Keep the detection report for your IT team.
- Block repeat phishing pages. AdGuard can filter many known malicious domains and intrusive redirects, but it should complement careful link verification, not replace it.
- Monitor related accounts and business activity. Watch for password resets, invoice changes, unusual cloud sharing, or new sign-ins connected to the compromised mailbox.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is every unexpected NDA email a scam?
No. Legitimate organizations send agreements electronically, but an unexpected request should be confirmed through a separate, trusted communication channel before opening its link.
Can a real coworker’s address send the phishing message?
Yes. A compromised mailbox can send convincing invitations to existing contacts. Familiar sender information lowers suspicion, so context and independent confirmation still matter.
Why does the page already know my email address?
The address can be embedded inside the unique link. Prefilling a form is simple personalization and does not prove that the page belongs to your provider.
Is changing my password enough after approving an app?
Not always. A previously authorized application may retain tokens or permissions. Revoke suspicious app access, end active sessions, and ask an administrator to review grants.
What if I opened the email but never clicked?
Simply reading the message is usually not the damaging step. Delete or report it, and avoid loading attachments, following links, or replying with sensitive information.
Should I send the suspicious NDA to legal staff?
Use your organization’s approved reporting method. Forwarding normally can activate links or spread attachments, while a dedicated phishing-report button preserves safer technical details.
The Bottom Line
The NDA Agreement shared-file email uses familiar business pressure to steer recipients toward a fake viewer, credential form, or dangerous permission request.
Verify the sender and transaction outside the message. A genuine agreement will survive a short confirmation; a phishing campaign depends on preventing one.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.