


Have you received a shocking message on Facebook Messenger about a friend passing away? Beware – it could be the “It Won’t Be The Same Without Him” Facebook scam.
This scam aims to steal Facebook accounts by tricking users into clicking malicious links. Once clicked, these links can compromise your account and allow scammers to access your personal information.
In this article, we’ll break down exactly how the “It Won’t Be The Same Without Him” scam works, what to watch out for, and most importantly, how to protect yourself.
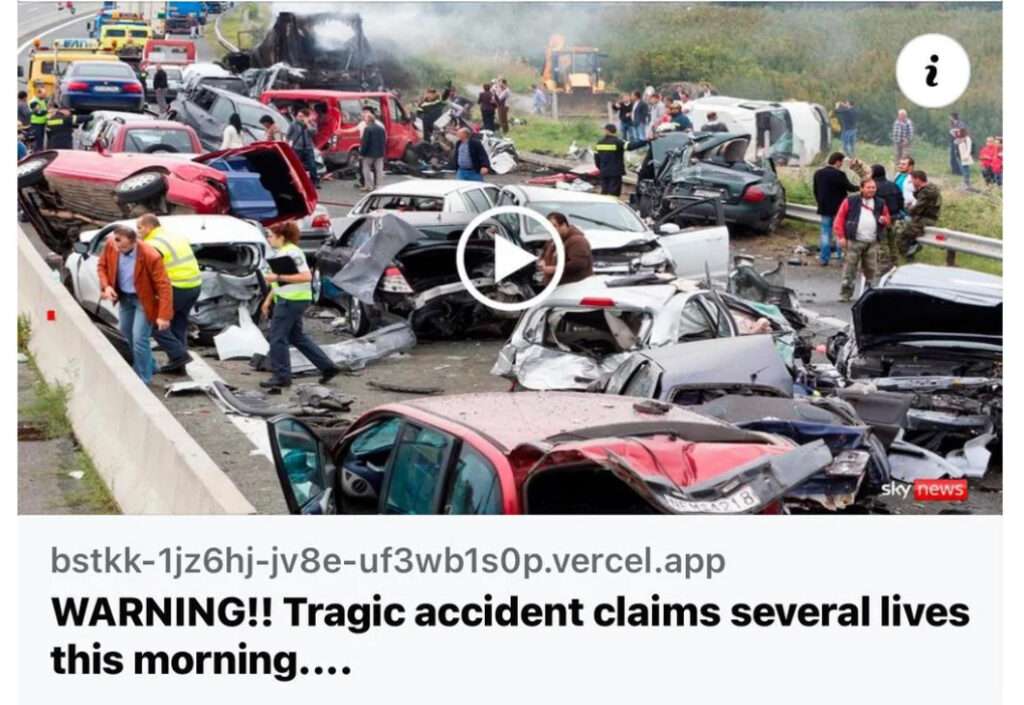
Overview of the Scam
The “It Won’t Be The Same Without Him” scam is a dangerous Facebook phishing scam aimed at stealing users’ login credentials and taking over their accounts. This sinister scam has exploded in popularity recently, and thousands of unaware victims have had their personal information compromised, accounts hacked, and identities stolen.
How the Scam Spreads
The scam starts when hackers take over accounts of real Facebook users through phishing or malware. They then use the hacked accounts to send fake messages to that person’s friends containing shocking headlines and links about deaths or tragic accidents.
These concerning messages seem to come from a real friend or family member. The scammers exploit this trust factor to manipulate victims into urgently clicking links without thinking them through. They use emotional manipulation tactics to override critical thinking in the victims.
For example, you may receive a message seemingly from your Aunt Jenny saying “I can’t believe he died, I’m so devastated.” This compels you to instantly click the link to find out what happened to Jimmy, playing into the scammer’s trap.
Malicious Links That Steal Login Info
The links in these messages don’t lead to real news articles. Instead, they route to sophisticated phishing sites mimicking Facebook’s login page. When users enter their usernames and passwords, these credentials go straight to the scammers instead of Facebook.
Armed with thousands of Facebook login details, the hackers perpetuate the scam by impersonating users and sending more fake messages. They also access personal information, photos, messages, and friend lists in the accounts. This supports further criminal activity like identity theft, online extortion, and recruitment for scams or cults.
Scammers are constantly evolving the scam with new headlines and links to avoid detection. Recent examples include:
- “Our dear old friend Dave died in a horrible skydiving accident. I can’t believe it”
- “Breaking news: Jennifer’s tour bus crashed leaving 38 dead and 12 critically injured”
- “I’m devastated. Little Timmy collapsed and died during the school marathon.”
These shocking fake headlines compel users to click without thinking, especially when the message seems to come from a close friend or relative. But those clicks deliver your login credentials directly into the hands of hackers.
Damaging Consequences for Victims
Once scammers access your Facebook account, the consequences can be severe. They gain access to your personal photos and posts, private messages exchanged with friends and family, your contacts list, and any other private information you store on Facebook.
This gives them the keys to steal your identity and exploit you as a victim of fraud. They could sell your information on the dark web, use it themselves to open credit cards or apply for government benefits, or threaten you into sending them money.
The scammers also leverage your account to send more phishing links to your friends, spreading the scam to more and more victims. Each compromised account gives access to hundreds more in their friend networks.
Even worse, if you reuse the same email and password combo on multiple sites, the scammers can access your accounts on those sites too. Imagine if they got into your bank account, email, or credit cards using stolen Facebook credentials.
Spreading Like Wildfire
Facebook estimates that fake accounts and hacking scams compromise millions of accounts every year. The “It Won’t Be the Same Without Him” scam in particular has spread exponentially due to its ability to manipulate human emotion and bypass users’ defenses.
Security experts have called it one of the most dangerous Facebook scams currently circulating due to how quickly it spreads and the sensitive personal data it exposes. Law enforcement has also struggled to trace the scammers, many of whom operate out of foreign countries and hide behind layers of fake accounts and IP addresses.
This scam has left countless victims with compromised personal information, damaged reputations, and struggles to regain access to their accounts. Staying vigilant and recognizing the signs of this scam is crucial to protect yourself and your community. Don’t become the next victim of this devastating identity theft trap.
How the Scam Works
The creators of the “It Won’t Be the Same Without Him” scam use social engineering tactics to progressively trick unsuspecting Facebook users. They exploit human emotions like shock, urgency, and panic to lead victims through a carefully crafted sequence ending in stolen login credentials.
Here is an in-depth, step-by-step look at exactly how this scam unfolds:
Stage 1: Gaining Access to a Facebook Account
The first step for scammers is gaining control of a real Facebook user’s account. They achieve this through two primary methods:
Phishing: The scammers create a fake Facebook login page and send links to it in Facebook messages or emails. When users try to login, their credentials go to the scammers instead of Facebook.
Malware: The scammers create apps, games, or files containing malware to infect users’ devices. This malware can steal passwords, install keylogger programs, or gain remote access to take over accounts.
Once scammers gain access to even one account, they can begin perpetuating the scam.
Stage 2: Crafting Emotional Messages
After hacking into accounts, the scammers impersonate the users and start sending messages to friends and family members.
They craft the messages to contain shocking, emotional headlines about accidents, disasters or deaths. Some examples:
- “I can’t believe our old college friend Ashley died in a river rafting accident. Here’s the story of what happened…”
- “Horrible news. Over 50 killed in a train derailment outside the city. Thoughts are with the families.”
- “Little Jeremy was hit by a car riding his bike. I’m devastated. He didn’t make it.”
These messages seem to come from a trusted friend. The scammers exploit this to override critical thinking and get users to click urgently.
Stage 3: Directing Users to Fake Articles
Each emotional message contains a link, supposedly to a news article about the tragic story.
The headlines promise details about what happened and the full story:
- “Click here for the developing story on the rafting accident that claimed Ashley’s life”
- “Coverage of the devastating train derailment and rescue efforts”
- “More details emerge on the car accident that killed young Jeremy”
The urgency and emotion compelled by the headlines prompts users to click the links immediately without hesitation. But this is the fatal mistake that starts them down the path to being scammed.
Stage 4: Sending Users to Fake Login Pages
Instead of news articles, the links redirect users to sophisticated fake Facebook login pages. These pages precisely mimic the real Facebook site with logos, colors, fonts, and formatting.
Most users don’t notice small abnormalities that would indicate the site is fake. They see the familiar Facebook design and don’t suspect the urgent news link contains a trap.
Stage 5: Harvesting Users’ Login Credentials
Without realizing the page is fake, users enter their Facebook username and password into the scam site.
Instead of logging them into Facebook, these credentials are captured directly by the scammers running the phishing site in the background.
Users expect to be redirected back to their Facebook feeds. But they are actually giving full access to their accounts directly to the scammers.
Stage 6: Spreading to Friends
Now able to impersonate the user, the scammers send more phishing links to friends in that user’s network. This allows them to harvest more credentials and take over more accounts.
Each compromised account gives access to hundreds of friends, allowing the scam to spread at an exponential rate. This results in an avalanche effect of compromised accounts flooding the platform.
Stage 7: Stealing Private Data
Finally, the scammers leverage their access to steal personal information from the accounts. This includes private messages, photos, location check-ins, contacts, interests, and any other sensitive data.
They may sell this data on the dark web, use it themselves for identity theft, or exploit victims through extortion and ransom demands. The victims’ lives are turned upside down.
As this step-by-step breakdown shows, this scam leverages complex social engineering tricks and preys on human psychology. But recognizing the techniques at each stage makes users far less susceptible. Stay vigilant to protect yourself and your sensitive data from this chain of manipulation.
Warning Signs of the Scam
Here are key signals that a concerning Facebook message could be the “It Won’t Be The Same Without Him” scam:
- It comes from a friend you haven’t heard from in a while. Scammers hack accounts to impersonate real friends.
- The message has spelling and grammar errors. Scammers often come from non-English speaking countries.
- It includes an unbelievable headline about a tragedy. Scammers use shock factor to get you to click.
- The linked article is hosted on a dubious domain instead of a reputable news site.
- Login pages have slight abnormalities like different fonts or logos.
- Your friend would likely contact you directly if they had urgent news.
Stay vigilant for these signs so you can protect both yourself and your friends from this insidious scam.
What to Do If You Fell for the Scam
If you suspect your Facebook account has been compromised by the “It Won’t Be The Same Without Him” or similar scam, act quickly:
- Reset your Facebook password – This locks the scammers out of your account. Enable two-factor authentication for extra security.
- Check privacy settings – Ensure your profile and posts are only visible to friends, not public.
- Remove suspicious friends – Delete any new friends you don’t recognize who could be scammers.
- Alert your real friends – Let them know your account was hacked so they can watch for suspicious messages from you.
- Monitor your account closely – Keep checking to make sure no unauthorized posts appear from scammers.
- Run antivirus software – Check your devices for spyware or keyloggers installed by fake login pages.
- Change passwords on other accounts – If you reused your Facebook password elsewhere, update those as well.
- Contact Facebook – Report the scam to help Facebook identify and shut down malicious links.
Take these steps as soon as possible to secure your account and personal information after being tricked. And learn how to spot similar scams moving forward.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About the “It Won’t Be the Same Without Him” Facebook Scam
1. What is the “It Won’t Be the Same Without Him” Facebook scam?
This is a phishing scam where hackers send Facebook messages pretending a friend has passed away. The message links to a fake login page to steal your credentials.
2. How does the “It Won’t Be the Same Without Him” scam work?
Scammers gain access to accounts, then message friends with fake tragic headlines and article links. The links go to phishing sites mimicking Facebook’s login to steal credentials.
3. What are some examples of the fake headlines used in this scam?
- “I can’t believe he’s gone, I’m gonna miss him so much”
- “Our dear friend Dave died in a horrible accident”
- “Little Timmy collapsed and died during the school marathon”
4. What are the warning signs of this Facebook scam?
- Spelling/grammar errors
- Shocking/emotional headlines
- Suspicious links
- Message from inactive friend
5. What should I do if I clicked the link in the message?
Immediately change your Facebook password and enable two-factor authentication. Check your privacy settings. Report the scam to Facebook.
6. How can I protect myself from the “It Won’t Be the Same Without Him” scam?
- Don’t click links in suspicious messages, even if from friends. Confirm tragic news directly with the person.
- Look for odd spelling/grammar, URLs, formatting in messages.
- Hover over links to see the URLs before clicking.
- Use strong unique passwords for each account.
- Enable two-factor authentication.
7. What should I do if my Facebook account is compromised?
Reset your password, remove suspicious friends, alert real friends of hacking, monitor account activity, run antivirus scans, and change passwords on other accounts that may be compromised.
8. How can I report this scam to Facebook?
Go to Facebook’s phishing scam reporting page. Provide details on the scam message, links, and impacted accounts.
9. How widespread is this Facebook phishing scam?
Security experts say it has exploded in popularity due to manipulating human emotion. Millions of accounts are compromised by these scams annually.
10. Who typically runs these types of scams?
They often originate overseas using networks of fake accounts and proxies to hide identities. Multiple groups leverage phishing kits available online.
The Bottom Line
The “It Won’t Be The Same Without Him” Facebook scam is a prime example of social engineering – manipulating human emotions to bypass security. By recognizing the tricks and tactics scammers use, we can avoid falling into their traps.
Be skeptical of shocking messages from friends, especially those containing links. Report any scams you encounter to help protect the Facebook community. And use strong passwords unique to each account to minimize the damage from any credential compromise.
Staying alert and using common sense is our best defense against losing our online identities and security to underhanded scammers. Don’t let them catch you off guard with fake tragedies tailored to exploit your emotions.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.