

A mail notice says nine messages never reached your inbox. Two subject lines look important, while seven more remain hidden.
The review button offers a quick way to release everything. First, consider what a real mail system would know and where it would ask you to sign in.
Overview
The notification fabricates a delivery queue
The Review Pending Messages email scam claims a mail server is holding messages that require the recipient’s attention.
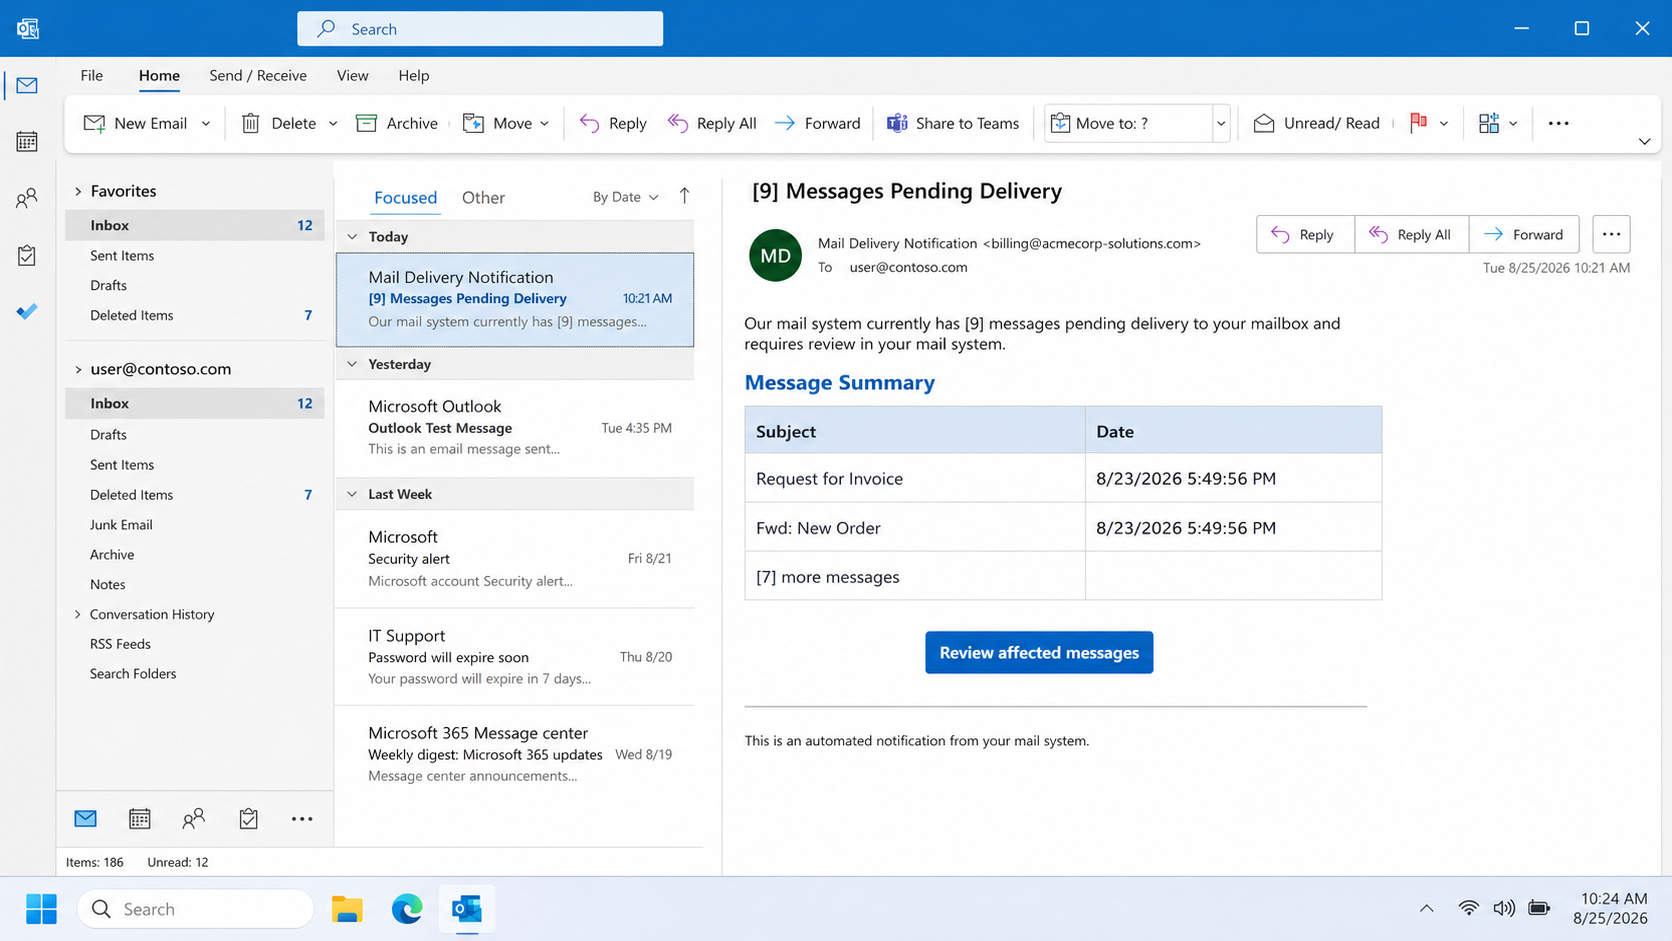
A 2026 version used the subject “[9] Messages Pending Delivery” and presented itself as an automated Mail Delivery Notification.
Its summary listed “Request for Invoice,” “Fwd: New Order,” and seven additional messages.
Those subjects are chosen for workplace relevance. Accounting, sales, purchasing, and management staff may worry that normal business has stopped.
The listed messages do not prove a queue exists. They are text inside the lure, not records retrieved from the recipient’s server.
The button leads outside the real mailbox
The email tells the recipient to review affected messages on a mail portal.
Older versions threaten deletion after a fixed period, while newer versions emphasize immediate delivery review.
Campaign infrastructure changes frequently. The important mismatch is any review page located outside the organization’s genuine webmail or security service.
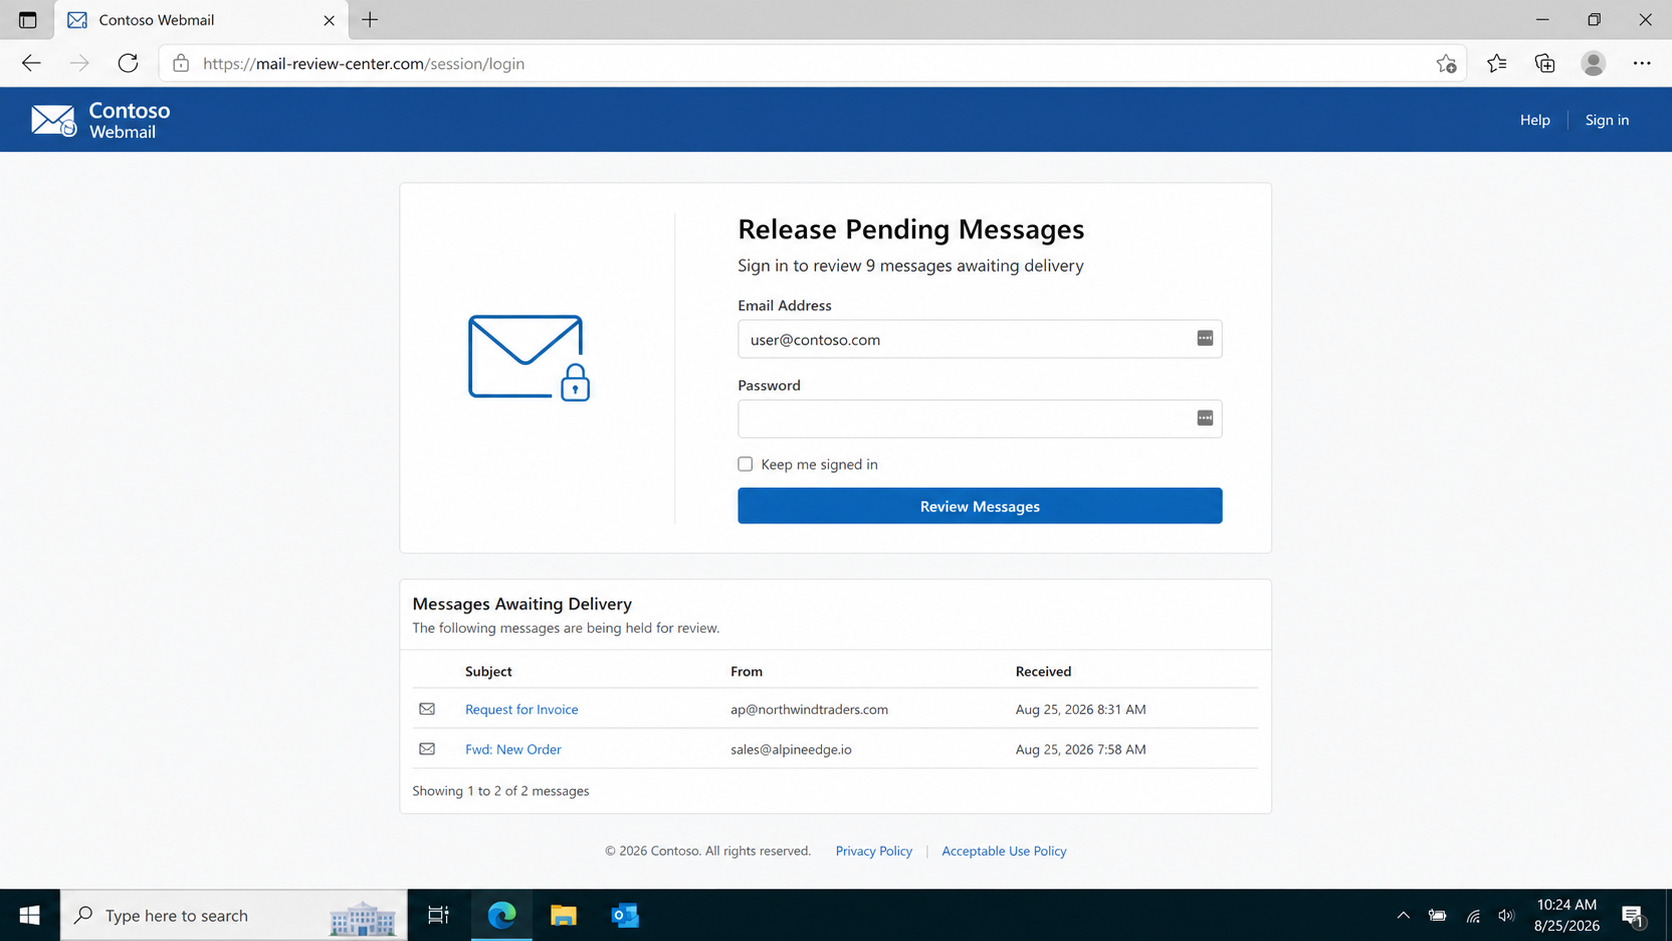
A copied portal can display the recipient’s address and the same invented subjects carried in the link.
That continuity is easy to program. It does not require access to the inbox or quarantine system.
The supposed review becomes a password collection form
The fraudulent page asks the user to authenticate before pending mail can be released.
Anything entered can be recorded and sent to the operator rather than a legitimate email provider.
The form may imitate Microsoft 365, generic Webmail, Gmail, cPanel, or branding associated with the recipient’s domain.
Once criminals obtain the password, they can read mail, create rules, reset other accounts, and impersonate the victim.
Several details expose the deception:
- The recipient cannot see the alleged queue through their normal mailbox.
- Invoice and order subjects create business urgency without identifiable senders.
- The message uses a generic automated identity.
- The review button can leave the organization’s approved portal.
- The landing page asks for an existing mailbox password.
- A prefilled address creates familiarity without proving account access.
- The warning provides no administrator, ticket, or independently verifiable event.
Receiving the notice does not mean messages are actually delayed. It also does not show that the mailbox is already compromised.
The immediate danger begins when the recipient visits the external form and submits a password.
Why Invoice and Order Subjects Are Chosen
A generic “hello” might be ignored. An unpaid invoice or new order can affect revenue, suppliers, customers, and deadlines.
The lure shows only enough information to trigger concern. Hidden senders and incomplete details push the recipient toward the review button.
Different roles find different reasons to investigate. Finance sees a missing invoice, while sales sees a possible customer order.
Employees also know that spam filters make mistakes. Legitimate messages occasionally enter quarantine, making the basic story plausible.
The scam abuses that real possibility without proving it occurred.
A proper quarantine portal should already be known to the organization and reachable from established account or security tools.
Staff should not learn its address for the first time through an unsolicited message from an unverified sender.
When important mail is genuinely missing, administrators can confirm queue records without asking users to authenticate through a stranger’s page.
How The Scam Works
Step 1: The campaign reaches addresses that depend on timely email
Attackers send the notice to individuals, shared business inboxes, public departments, and addresses gathered from older breaches.
Accounting, sales, support, and purchasing mailboxes are attractive because delayed messages carry obvious operational consequences.
The campaign can personalize the domain or address automatically while leaving the rest of the message unchanged.
A matching domain may look administrative, yet it can simply be inserted from the recipient portion of the email list.
No insider knowledge is necessary to guess that a business values invoices and orders.
Step 2: A believable message count creates a manageable problem
Nine pending messages sound serious but not impossible. The number suggests a specific server event rather than broad service failure.
Some versions use four or five messages instead. Operators can change the count without altering the credential theft behind it.
The notice may imply that messages will expire, be deleted, or remain unavailable until reviewed.
That framing makes the recipient responsible for preventing loss.
A real provider should expose the queue through the user’s existing account, not only through one email button.
Step 3: Fabricated subject lines produce urgency and curiosity
“Request for Invoice” suggests money is waiting. “Fwd: New Order” suggests a customer expects action.
The email omits enough context to prevent independent confirmation.
Without a sender or full preview, the recipient cannot call the customer, search the inbox, or compare a known transaction.
The promised seven additional messages create a second layer of uncertainty.
Curiosity and workplace responsibility now point toward the same action, opening the fraudulent portal.
Step 4: The review control hides a domain change
Button text describes releasing messages, but the underlying URL controls the destination.
Recipients can hover over it on desktop systems or preview it with a long press on many mobile devices.
An unrelated host, URL shortener, free page builder, compromised website, or recently created domain should stop the process.
Encryption does not prove ownership. HTTPS only protects traffic sent to the server named in the address bar.
Legitimate quarantine tools should match a provider or service explicitly documented by the organization.
Step 5: The landing page borrows the user’s mail identity
The phishing page may display a familiar logo, organization name, email address, and list of supposedly held messages.
Values can be passed through the link when the email is created.
Prefilling the address reduces effort and makes the form appear connected with live server data.
The user sees one remaining field, the password, and may complete it without reconsidering the domain.
No genuine authentication occurs. The form’s purpose is to collect what the user types.
Step 6: The stolen credential is used quietly
Operators can test the password against the provider associated with the address soon after submission.
They may avoid changing the password because silent access is more valuable than immediately locking out the owner.
Forwarding rules, inbox filters, application passwords, and connected-app permissions can provide persistence.
An attacker may search for payroll, banking, invoices, identification, travel, tax records, and password resets.
Reused credentials widen the exposure to other services even when the mailbox uses additional protection.
Step 7: The genuine mailbox makes later fraud convincing
Messages sent from the victim’s account can appear inside existing conversations with coworkers, customers, and suppliers.
Criminals may introduce another document, request gift cards, change bank details, or imitate an urgent executive instruction.
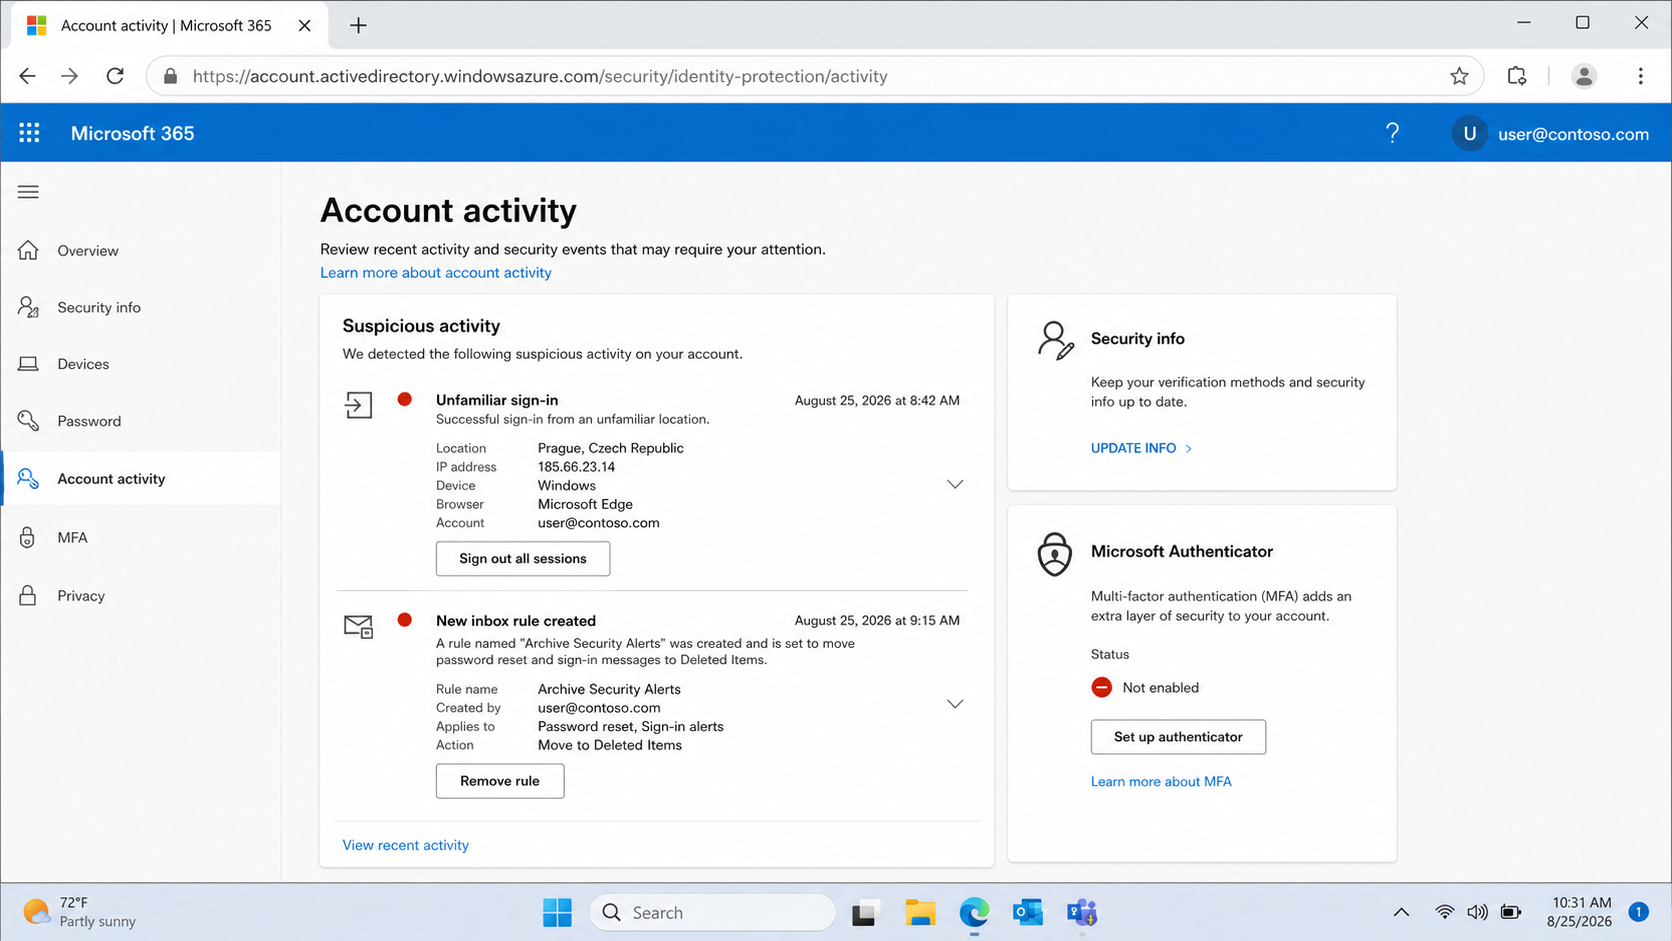
Hidden rules can move replies and security alerts away from the normal inbox.
Password recovery links for connected services may be intercepted before the owner notices them.
One fake queue can therefore lead to payment fraud, broader phishing, privacy loss, and identity misuse.
Quarantine Notifications Are Real, but They Follow Rules
Organizations often use spam quarantine, attachment filtering, and message moderation. A warning about held mail is not automatically fraudulent.
The difference lies in identity, infrastructure, and consistency.
Legitimate notices come from an approved provider or internal system that administrators can name.
Employees should receive documentation explaining where quarantine lives, how often summaries arrive, and which actions are available.
Scheduled digests usually arrive at predictable intervals and use a design employees have encountered before.
The portal commonly offers release, block, preview, and report controls tied to real filtering events.
Message counts change as administrators or users act. A live dashboard should agree with the notification when both are opened.
Some providers use signed one-time links, but those links still resolve to infrastructure identified in the organization’s documentation.
Time zones and timestamps can vary, yet the server should retain auditable records for every held item.
An administrator can explain why a message was quarantined, which rule triggered, and whether another employee received the same campaign.
Mobile previews sometimes hide long destinations. Wait for a safer device instead of guessing which host a shortened display represents.
A new vendor or changed portal deserves internal notice before employees are expected to trust it.
The portal should be reachable through bookmarks, a company dashboard, or provider settings without relying on the new message.
A real queue also matches server records. Administrators can identify message IDs, filtering reasons, senders, and timestamps.
Users should never provide a mailbox password to a site that the IT team cannot recognize.
If your organization has no known quarantine service, the unsolicited review notice requires even greater skepticism.
Sender, Queue, Domain, and Mailbox Checks
Identify the system that supposedly holds the mail
Ask which provider, gateway, or internal server generated the notification.
Compare the sender with earlier legitimate security summaries and documentation from the IT team.
A vague label such as Mail Delivery Notification is not an accountable system identity.
Providers should be confirmable through the normal mailbox or organizational support channel.
Search for evidence without using the button
Open the known quarantine portal directly, check spam and junk folders, and search for the listed subjects.
Ask administrators whether nine items are actually awaiting release.
Contact the alleged invoice or order sender independently if other records identify them.
An invented queue disappears under checks that do not depend on the attacker’s chosen page.
Compare every domain in the chain
Expand the From and Reply-To addresses, preview the button, and read the final address bar after redirects.
Each domain should have a documented relationship with the email provider or organization.
A copied logo, valid certificate, or prefilled address cannot explain an unrelated host.
When redirects obscure the endpoint, close the page and let security staff analyze the link safely.
Look for persistence beyond the password
Inspect active sessions, recent sign-ins, recovery methods, forwarding addresses, inbox rules, delegated access, and application permissions.
Delete malicious rules only after recording them when an incident response team needs evidence.
Review Sent, Deleted, Drafts, and Archive for activity the owner did not create.
Business accounts may require tenant-wide searches because the same campaign often targets several employees.
What to Do if You Have Fallen Victim to This Scam
- Leave the false portal. Close every related tab and avoid resubmitting credentials after an error or supposed release failure.
- Change the email password. Use a known-clean device and navigate through the provider’s official application or saved address.
- Remove hidden access. End other sessions and inspect forwarding, rules, recovery options, app passwords, delegated accounts, and connected services.
- Replace repeated passwords. Secure any financial, shopping, cloud, social, or workplace account using the same credential.
- Add robust verification. Configure an authenticator or hardware security key and refuse login approvals you did not begin.
- Contact workplace administrators. They should review sign-in logs, preserve the lure, find other recipients, and block related infrastructure.
- Check financial conversations. Confirm invoices, payment changes, payroll requests, and supplier instructions through established contacts.
- Scan suspicious devices. Run Malwarebytes if the page delivered files, opened unusual prompts, or caused unexpected browser behavior.
- Limit repeat redirects. AdGuard can block many known phishing pages, although it cannot revoke sessions or stolen mailbox credentials.
- Report the message. Use the provider’s phishing control and send relevant evidence to organizational and appropriate external reporting channels.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Are nine messages really waiting for delivery?
The email itself cannot prove that claim. Check the established quarantine portal or ask the email administrator directly.
Invented counts and subjects are common because they make the notice feel connected with server data.
Why does the notice list an invoice and new order?
Those subjects create commercial urgency and appeal to several workplace roles.
They can be typed into the template without any knowledge of genuine messages.
Can legitimate quarantine emails contain review buttons?
Yes, but the sender and destination should match a documented provider or internal security system.
Reach the portal independently whenever a new notice or unfamiliar domain appears.
What if I clicked but entered no password?
Close the page and remove unexpected downloads. Your credential generally remains private when nothing was typed or submitted.
Scan if the browser installed anything, displayed software prompts, or began redirecting unexpectedly.
Is a password change enough after submission?
Not always. Existing sessions, forwarding rules, application passwords, and permissions may survive the change.
Review the entire security configuration and involve an administrator for managed accounts.
Does receiving the notice mean my address was targeted personally?
Usually not. Campaigns distribute the same template to large address lists and automatically insert recipient details.
Even broad spam deserves care because one submitted password can still create a personal compromise.
The Bottom Line
The Review Pending Messages email scam invents a mail queue and uses invoice and order subjects to create workplace urgency.
Its review control leads toward a counterfeit sign-in page where the recipient’s mailbox password can be collected.
Verify quarantined mail through known systems and administrators. Never let an unsolicited notice introduce the only portal that can supposedly solve the problem.
If credentials were entered, secure every access path, inspect business communications, update reused passwords, and scan devices that showed additional suspicious activity.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.