


A Steer-branded page says a token allocation is available. If you have followed the project, the invitation can look like a routine community update.
The familiar name is only the starting point. Before opening your wallet, check which site is making the offer.
Overview
A lookalike address presents a false STEER allocation
The Steer Finance token allocation scam uses the project’s identity to promote a false reward claim. The reported impersonation appeared at claim-steer[.]finance.
That address is distinct from steer.finance, the genuine project domain. Adding a claiming-related word does not turn a separate registration into an authorized project page.
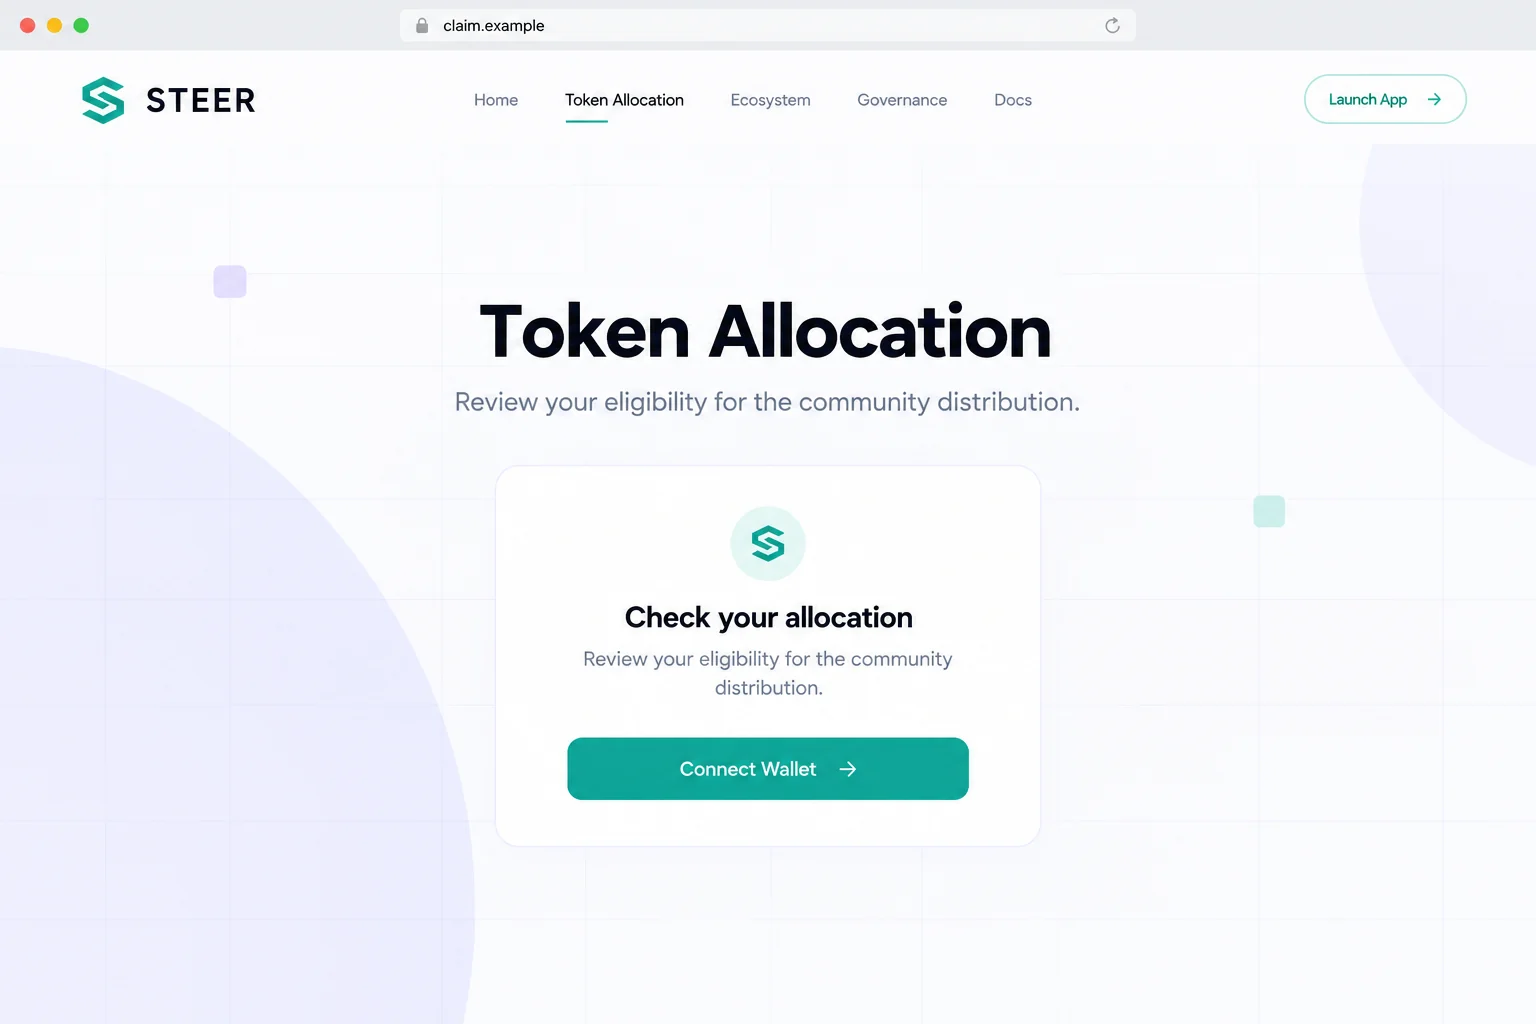
The lead image is an explanatory illustration using a nonfunctional address. It is not an authentic capture of the historical claim site.
The impersonation is separate from legitimate Steer rewards
Steer Protocol has genuine documentation describing reward campaigns and allocations. The existence of those features is part of what makes an imitation claim believable.
It does not validate this offer. The false page borrows project familiarity to encourage wallet interaction, with a reported cryptocurrency-draining objective.
No wallet request was signed or contract tested here. The exact authorization used by this campaign remains unverified, and the reported domain was unavailable for a current capture.
What to establish before touching a wallet prompt
- Confirm the announcement through a project route you independently recognize.
- Check the actual registered domain, not just the logo or page heading.
- Identify why your account would qualify for that particular reward.
- Read the network and action requested inside the wallet.
- Keep project verification separate from deciding whether an individual permission is appropriate.
The warning concerns the counterfeit allocation, not the genuine protocol. Do not treat every Steer-related reward as fraudulent because someone has impersonated the project.
Why a Real Rewards Program Helps an Impersonator
A completely unfamiliar giveaway needs to explain itself from scratch. An imitation of a known project can rely on what readers already believe.
If you remember seeing token distributions discussed, an allocation page may seem like the next step in a process you vaguely recognize.
The attacker benefits from that partial familiarity. You may recognize the token name while missing that the website asking for access belongs to someone else.
Even an accurate description of the project would not authenticate the claim. Public information about genuine services can be copied onto a malicious destination.
Likewise, knowing that wallets are routinely connected to decentralized applications does not settle whether this particular application deserves a connection.
The safest approach is to verify the exact program and route before assessing its requests. Do not let a plausible project background stand in for those checks.
How the Steer Finance Token Allocation Scam Works
Step 1: The invitation borrows the project’s identity
The lure presents the allocation as a Steer opportunity. Branding and a familiar token name encourage readers to associate the offer with the genuine protocol.
A link can arrive through several channels, including a forwarded recommendation or promotional message. The available case does not establish one universal distribution method.
If someone you know shares the link, ask where they verified it. A good-faith recommendation is not the same as an authenticated project announcement.
Do not seek confirmation from a support account that appears only after you question the offer. Verify support identities through the established project channels.
The same applies to comments claiming successful rewards. A stranger’s screenshot can describe a real transaction, a different program, or an invented result.
Step 2: The near-match domain makes claiming sound official
The reported address combines a claiming verb with the project name. That wording suggests a special-purpose distribution site while remaining a separate domain.
Compare claim-steer.finance with docs.steer.finance. The latter is a subdomain under the genuine parent; the former is not.
Sharing the .finance ending does not create an organizational relationship. It is a public domain extension available to unrelated registrants.
A secure connection also has a narrower meaning than many people assume. It protects communication with the displayed host, not the truth of its affiliation claims.
Do not follow the suspicious address just to compare its logo. Begin at the project location you already know and locate the relevant announcement from there.
If a third-party claim service is genuinely involved, its role should be independently verifiable. The third-party page cannot grant itself legitimacy by displaying a project name.
Step 3: The promised allocation leads toward a wallet request
The page encourages the reader to use a wallet in pursuit of the alleged STEER distribution. That brings an account containing real assets into the process.
Some legitimate claims require wallet interaction, which is why a connection button is not conclusive evidence on its own. The site identity remains essential.
Once a request reaches the wallet, read it as a separate decision. Does it concern the expected account and network, and what authority would it actually create?
A page describing an incoming reward does not justify an unrelated outgoing transfer or broad spending permission. Stop when the requested action does not match the purpose.
A request for your seed phrase is a more direct danger. That secret is not an eligibility code, and a claim page does not need it.
Do not accept instructions to disable security warnings or install an unfamiliar extension to continue. A broken claim is not an emergency that overrides basic account protection.
Step 4: An authorized action can outlast the claiming session
A malicious permission can remain useful after you close the page. The effect depends on what was authorized, not how long the claim screen stays open.
For compatible token systems, an allowance can permit another party to move covered assets. A simple site disconnection may leave that spending authority unchanged.
Other requests may have different effects. There is no verified contract trace here that supports describing a single identical theft transaction for every visitor.
Connecting without further authorization is not universally an instant drain. But signing something you do not understand is not made safe by calling it verification.
After an interaction, use the wallet’s own history and trusted explorer records. A claim-page error or congratulations message is not the final account-security check.
If assets have moved, preserve the public transaction record promptly. The destination and network matter more to a responder than the page’s marketing explanation.
Check a Real Reward Without Validating a Fake One
Find the actual campaign, not merely a page about rewards
The genuine Steer reward-claiming documentation distinguishes pending rewards from published rewards that can be claimed.
That is useful context, not confirmation that any particular reader has an allocation. Your eligibility needs to follow the rules of an identifiable genuine campaign.
Do not interpret a general help article as approval of a link from an unsolicited message. The help article describes a system, not every page using its terminology.
Similarly, a pending-looking balance on a false site may be drawn entirely by that site. It is not proof of published rewards or a claimable token balance.
Keep the network consistent with the real task
The official instructions mention checking the correct chain when troubleshooting claims. That does not mean accepting any network switch suggested by an imitation website.
Confirm which campaign and network you are using before responding to a wallet prompt. A multichain application can show several unrelated accounts.
If the request involves a different asset or chain than expected, decline it and investigate. Do not bridge funds or purchase tokens merely to satisfy an unverified claim.
No fixed fee or required deposit is established for this impersonation. A later payment demand needs separate scrutiny, not acceptance as part of a verified program.
Verify the route before asking strangers for technical help
A claiming problem can make an unsolicited support offer seem welcome. Scammers may exploit that moment with supposed wallet validation or account synchronization.
Start with the established project website and its independently verified support route. This is an identity check, not an endorsement of an investment.
Do not give anyone remote control of your computer to collect an allocation. Do not paste commands, install a repair tool, or share recovery words.
If genuine support needs a transaction reference, provide the public identifier only. That is different from giving it the secret used to sign transactions.
What to Do if You Have Fallen Victim to This Scam
End the false claim attempt. Reject outstanding wallet prompts and avoid further interaction with claim-steer.finance. Do not make another payment to complete the process.
Note the account and network involved. Record whether you connected, signed, approved token access, transferred assets, or disclosed recovery information.
Review the actual wallet state. Check recent activity through the trusted wallet application and appropriate explorer. Save relevant transaction hashes before contacting support.
Do not conclude that everything is safe because a reward never appeared. An unsuccessful-looking claim can still have involved a completed authorization.
Check permissions independently of the connection. For relevant accounts, follow MetaMask’s token-approval guidance or your provider’s network-specific instructions.
Removing an allowance can limit future access, but it does not reverse prior transfers. Confirm that you are reviewing the affected account, asset, and chain.
Escalate any exposed recovery secret. A disclosed phrase or private key requires a different response from an unwanted dapp connection.
Use an unaffected device and trusted provider guidance to plan a new wallet. Replacing an app password cannot make a leaked recovery phrase private.
Report suspicious transfers promptly. Use official exchange or wallet-support channels, and report financial losses to the relevant authorities.
Include the false domain, timestamps, destinations, and public transaction records. Do not invent an attacker identity or assume the recipient address identifies a real person.
Investigate added software or device access. Tell a trusted responder if you installed an extension, ran commands, or let someone control the computer.
Malwarebytes can help check for malicious software. AdGuard may reduce some deceptive web exposure. They do not revoke on-chain permissions or recover lost tokens.
Avoid guaranteed-recovery offers. Keep your signing secrets private and reject people who approach you demanding a fee to reverse the loss.
Useful help begins with the actual exposure and its limits. It should not require believing another unverified promise because the first one went wrong.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
When the Counterfeit Site Has Disappeared
A claim page becoming unavailable can feel like the end of the incident. It may simply mean that one delivery route stopped working.
It does not revoke a permission already granted or replace a secret already disclosed. Those remain account-level issues even when the website cannot be reached.
You can still prepare a useful report from wallet history, saved messages, and existing screenshots. Do not hunt for a replacement claim page to recreate the event.
Be careful with replacement links posted by strangers. A new address presented as a migration or repaired portal can expose you to another unverified request.
Project impersonation can reappear under different names or domains. The durable defense is a verified announcement route plus careful authorization review, not memorizing one blocked address.
If someone else finds the old page online again, that does not make it safer. Availability is a hosting fact, not proof of affiliation or a legitimate allocation.
If You Already Use the Genuine Protocol
Keep the counterfeit claim separate from your existing activity. A false allocation page is not, by itself, evidence that the genuine protocol’s contracts were compromised.
Review which account interacted with the impersonation and what it authorized. Do not rely only on searching your history for the STEER ticker.
For example, a request advertised as a STEER reward could concern a different asset. The label on the webpage cannot limit authority you actually granted elsewhere.
This is a reason to inspect the transaction details, not a finding that this particular campaign used a specific asset or permission.
Do not move existing positions through a replacement link offered by an unsolicited helper. Verify any genuine account-management action through your established application and trusted support.
A careful review should identify the exposure without turning a counterfeit promotion into unsupported claims about unrelated holdings or the project itself.
Frequently Asked Questions
Is claim-steer.finance part of the genuine Steer Protocol?
The reported domain is an impersonation used for a false token allocation. It is separate from the genuine steer.finance domain and should not receive wallet authorization.
Does this mean Steer’s real rewards system is a scam?
No. The real protocol has reward documentation. This warning concerns a counterfeit distribution page, not a finding that the genuine project’s reward features are fraudulent.
Why does adding claim to the name matter?
It makes the address sound purpose-built while remaining a different registered domain. A familiar word and matching domain extension do not establish project ownership.
Is connecting a wallet always enough to steal its assets?
No. Identify the subsequent requests and permissions. Connection, signatures, token approvals, transfers, and exposed recovery secrets are distinct events with different consequences.
Can an approval remain after I leave the website?
Yes, applicable on-chain permissions can persist. Review them using the wallet provider’s trusted guidance instead of assuming that closing the page cancels spending access.
What should I do if the claim website no longer loads?
Do not seek another version. Review existing wallet activity and exposed access, preserve your evidence, and contact legitimate support or authorities about actual losses.
The Bottom Line
Do not use claim-steer.finance to collect STEER tokens. The allocation is an impersonation lure, and familiar project branding does not justify its wallet requests.
If you already engaged, investigate the permissions, transactions, or secrets actually exposed. Verify genuine rewards independently and reject anyone promising guaranteed recovery for another fee.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.