

An Apple email gives you 48 hours to confirm an address. The design is quiet and familiar, and the requested action sounds reassuringly small.
You may remember verifying accounts before and reach for the button automatically. This time, pause long enough to check what the message is asking you to trust.
Overview
The email turns an account-security promise into a deadline
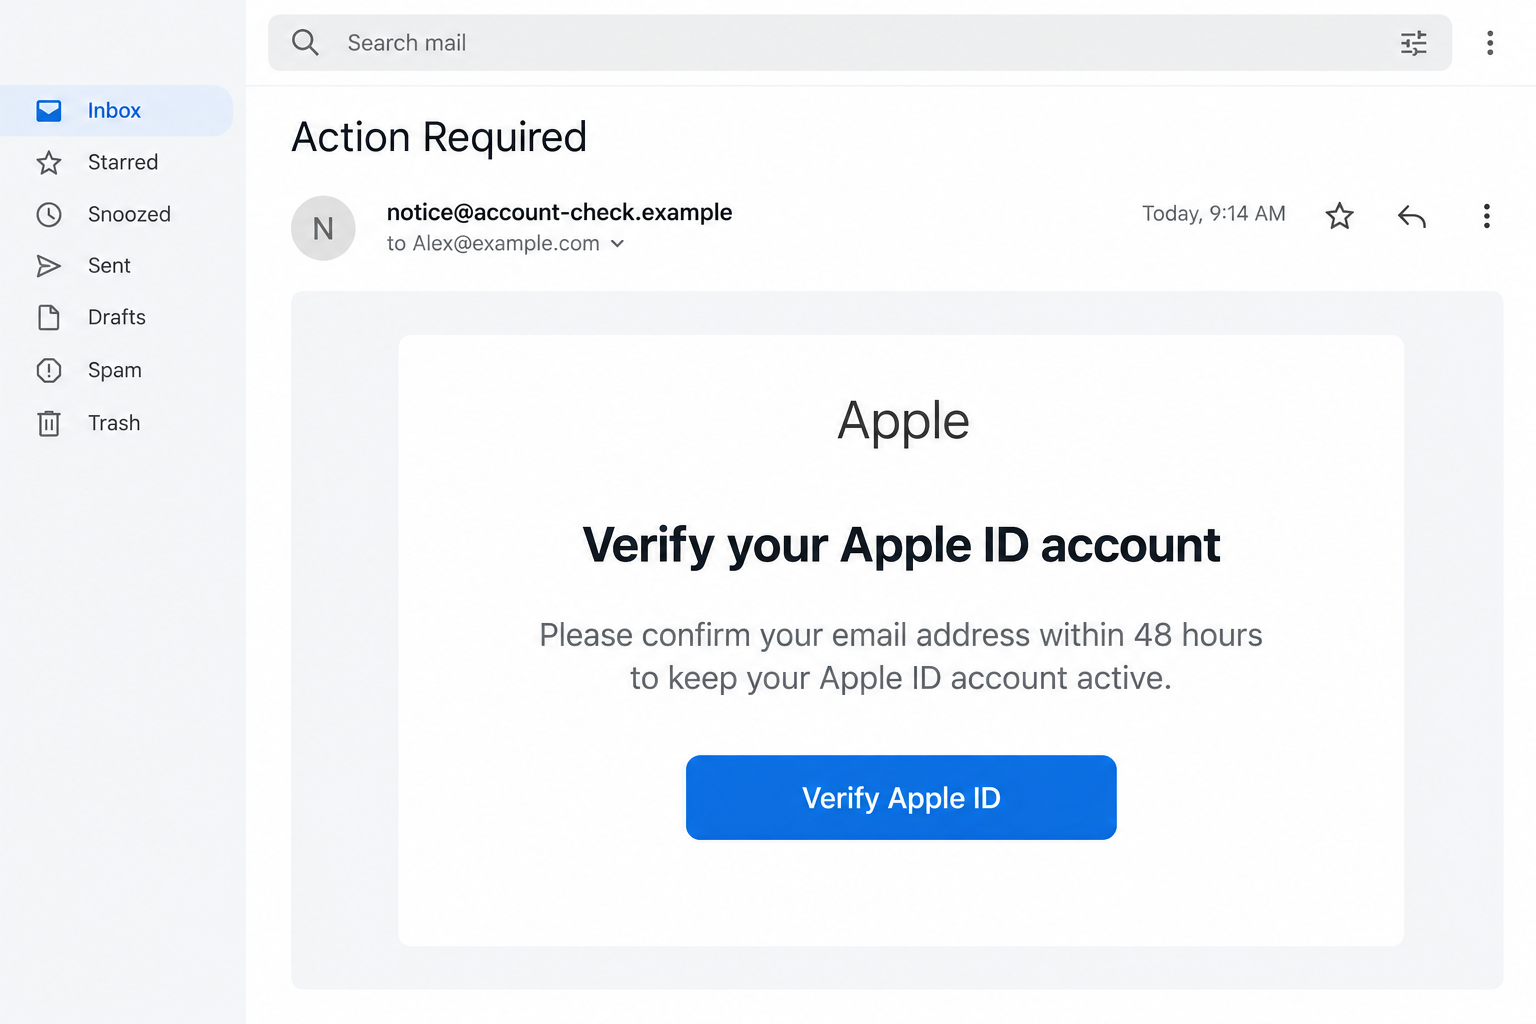
The Verify Your Apple ID email scam asks recipients to confirm their email address within 48 hours. Its security language encourages quick cooperation with an imitation.
The circulated message uses an Action Required subject and a verification button. It copies Apple branding and a company-address footer to look official.
Apple is being impersonated. A copied corporate address does not demonstrate that the company sent the email or authorized its destination.
The button leads to a hosted sign-in imitation
The reported destination is vrf-apple-3p0ps6whhc-1d15c007bfb0.herokuapp[.]com. Apple-related words at the beginning do not make that hosted address an Apple account service.
The documented first screen asks for an email address or phone number. A later password request is suspected, but the entire collection sequence was not independently completed.
That distinction matters. Supplying an identifier is an exposure, but it is not equivalent to giving away a password, verification code, or trusted-device approval.
Check your account without using the emailed verification route
Open your existing Apple device settings or independently reach the genuine account service. Don’t let this message select where you authenticate.
- Ignore the counterfeit 48-hour deadline.
- Keep passwords, device passcodes, and verification codes private.
- Reject unexpected sign-in approvals you did not initiate.
- Review the real account if credentials were disclosed.
- Use Apple’s established recovery process if access is lost.
A Familiar Verification Task Can Lower Your Guard
Many genuine services ask people to verify contact details during account setup or a requested change. The email borrows that ordinary administrative task.
It doesn’t need a dramatic accusation or large fake bill. A short statement about keeping data protected can make a button seem like helpful housekeeping.
The deadline adds a reason not to postpone. You may think confirming now is easier than discovering an account problem later.
But confirming an address and submitting credentials to an unknown page are different actions. The friendly explanation should not hide that difference.
Ask whether you requested a relevant change and whether the genuine account needs attention. Check outside the email before following its chosen process.
If you did recently create or modify an account, coincidence can make this notice feel connected. Match the actual change through your established service route.
If you made no change, don’t start one just to resolve the message. An unsolicited instruction is not a verified task assigned by Apple.
How the Verify Your Apple ID Email Scam Works
Step 1: The message makes verification sound protective
The opening frames cooperation as a way to maintain account security. That is a persuasive reason for someone who wants to do the responsible thing.
The phrasing points toward a small step rather than an important disclosure. Readers may think they are confirming contact information, not deciding who receives sensitive data.
Don’t measure the risk by how short the email looks. A single button can send you to an entirely different service.
Likewise, a personalized recipient address does not authenticate the sender. It shows where the message was delivered, not who authorized it.
Open the genuine account yourself if concerned. You can investigate a possible security issue without accepting an unsolicited route for doing so.
Step 2: The 48-hour window discourages independent checking
A deadline makes inaction feel like a choice with consequences. The reader may worry that an ignored notice will later explain a missing service or locked account.
The sender has not established that authority. A stated time limit cannot make its verification page genuine.
Do not call a number or open a support link supplied by the same disputed email to ask whether its deadline is real.
Use support you reach separately, preferably from an existing device or a saved genuine account route. That creates an independent check.
If you encounter a real account restriction elsewhere, handle it with Apple directly. A genuine problem does not validate the phishing notice that happens to mention one.
Step 3: Branding hides the move to another site’s sign-in page
The button’s wording describes an intention, not its destination. The reported link opens a hosted imitation with Apple-like account prompts.
Read the address as an address, not a sentence. Apple text inside a hostname can be chosen by an unrelated page operator.
The hosting service provides infrastructure. Its name on the address doesn’t prove that it created the lure or endorsed the page’s account claims.
A lock symbol and HTTPS do not settle this either. An encrypted connection can still deliver information to a recipient you should not trust.
The initial form requests an identifier. Stop there rather than supplying more information to see how convincingly the rest of the page behaves.
Don’t enter a spare account as a test. Verifying a suspect site should not require giving it useful personal information.
Step 4: Further account requests can deepen the exposure
The lure is designed for credential theft. A later password or code prompt would create a different and more serious disclosure than an address alone.
Do not assume a code makes the interaction safe. A code can belong to a real sign-in the attacker initiated while explaining it as verification.
Read authentic security prompts carefully and reject approvals you didn’t request. Keep protections enabled instead of following instructions to disable them.
Potential access to account data or purchases depends on what was captured and whether access succeeded. It is not proven by the first identifier field.
If you already supplied something, stop at the last completed action. You don’t need to finish the sequence in order to respond appropriately.
Apple ID Versus Apple Account Is Not the Deciding Clue
Apple now uses Apple Account for the service previously called Apple ID. Readers may still encounter the older name in familiar instructions and conversations.
The older wording alone is not enough to declare a message fraudulent. Scammers can update terminology just as easily as they can copy a logo.
The stronger questions concern the sender, destination, task, and information requested. Does the genuine account independently confirm that action?
Similarly, a perfect-looking footer isn’t authentication. A real postal address, legal name, or copyright line can be copied without access to Apple’s systems.
Don’t rely on spotting a grammar mistake either. Well-written phishing exists, and this technique would still be dangerous with every sentence corrected.
Use a known route as the anchor. A process reached through your actual account is more useful than judging the email’s visual polish.
For a family member who is worried, help them reach that route. Avoid turning the conversation into an argument about whether the logo looks convincing.
What Apple’s Own Guidance Recommends
Apple’s social-engineering guidance warns about impersonators seeking passwords, security codes, and access through familiar company identities.
It recommends contacting the company directly about unexpected requests. It also identifies reportphishing@apple.com as the reporting address for suspicious emails pretending to be from Apple.
Reporting the email doesn’t itself recover an account. Keep that step separate from changing exposed credentials and reviewing unauthorized access.
Apple’s compromised-account instructions explain password recovery, reviewing security information, and removing devices you don’t recognize.
They also address control of the email addresses and phone numbers associated with the account. Those recovery channels deserve attention if changes are unfamiliar.
If you cannot regain access through ordinary password recovery, follow the genuine account-recovery process. A waiting period may apply.
Don’t pay someone who claims they can bypass that process because they sent the verification notice. An unsolicited helper has not earned access to your account.
Decide What Was Exposed Before Choosing the Remedy
If you only read the email, don’t assume someone obtained your Apple password. Receiving a phishing message does not demonstrate account takeover.
If you opened the page but entered nothing, close it. Check whether any download, permission, or additional request appeared.
If you supplied an email address or phone number, expect more targeted approaches. That disclosure alone doesn’t demonstrate access to iCloud or a linked payment method.
If you typed a password, treat it as exposed even if the form failed. A page doesn’t have to acknowledge success to retain information.
If you shared a code or approved a sign-in, tell genuine support exactly that. Don’t reduce the incident to a simple link click.
Keep the wording of the real alert if available. A request to sign in, reset a password, or change security details can imply different account actions.
Don’t repeat an approval to capture a better screenshot. Existing messages and your recollection are enough to begin asking genuine support for help.
If software or a configuration change was requested, record it separately. Account recovery and device assessment solve different parts of the problem.
The reported hosted address currently shows a generic empty application page. The original sign-in flow could not be independently reproduced at that root address.
The lead image is a fictional illustration, not an original email capture. No real identifiers, passwords, or codes were submitted to complete the suspect flow.
What to Do if You Have Fallen Victim to This Scam
Leave the verification page and reject further requests. Don’t retry its form or use its unsubscribe and support links. Preserve the email for reporting.
Note the information you entered and any code or approval involved. An accurate account is more useful than assuming the worst or minimizing the interaction.
Change an exposed Apple password through Apple’s genuine process. Use a trusted device and a unique replacement. Don’t send the new password to anyone.
If you cannot sign in, follow official recovery. Never give an unsolicited recovery contact your device passcode or verification codes.
Review the account’s security information and devices. Look for changes you don’t recognize and follow Apple’s instructions for unauthorized devices or contact details.
Keep two-factor authentication active. Confirm you control the associated email and phone service, especially after unexpected changes or missing security messages.
Check actual purchases and other account activity. Use genuine account records and support rather than claims from the email. Preserve relevant dates and transaction references.
Contact the card issuer or payment provider if financial information or unauthorized payments are involved. Account recovery doesn’t automatically reverse a charge.
Replace reused credentials and secure related recovery accounts. A password shared with another service should be changed there too, through its own established route.
Don’t change unrelated accounts indiscriminately while overlooking an exposed recovery mailbox. Prioritize the credentials and access methods actually involved.
Assess any software the page persuaded you to install. Use protection appropriate to the affected platform, such as Malwarebytes where supported, and obtain qualified help if needed.
A browser visit doesn’t establish malware infection. Scanning also cannot cancel a code you supplied or restore account control by itself.
Report the impersonation and reduce follow-up pressure. Follow Apple’s phishing-report instructions and mark the message as junk. Remove unwanted browser-notification permissions.
AdGuard can reduce some misleading ads and redirects. It doesn’t authenticate Apple notices, and no blocker justifies approving an unexplained sign-in.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Helping Someone Who Is Afraid of Being Locked Out
The 48-hour warning can make a relative feel they must act immediately. Start by helping them open the genuine account, not by criticizing the click.
Ask what happened on each screen. They may remember an address field, a password, or an approval more clearly than a technical description of the incident.
Keep recovery information private while helping. Screenshots shared with family groups can expose details to more people than necessary.
If the account is restricted, use the real recovery route together. Don’t let impatience with that process push them back toward the sender offering instant help.
Frequently Asked Questions
Must I verify through this email within 48 hours?
No. The described deadline belongs to a counterfeit notice. Check genuine account tasks independently instead of using its verification button.
Does the Apple address in the footer authenticate it?
No. Public company details can be copied into an email. The actual sender, destination, and verified account process matter more.
Is every message using Apple ID rather than Apple Account fake?
No. The terminology alone doesn’t determine authenticity. This case concerns an impersonation and hosted login lure, not merely an older name.
Did entering my email address expose all my iCloud data?
Not by itself. An identifier, password, code, and successful account access are different things. Respond according to what you actually disclosed.
Should I approve a code to cancel the verification?
No. Reject requests you did not initiate through a trusted process. A stranger’s cancellation explanation doesn’t determine what a genuine security approval does.
Can antivirus software recover my Apple Account?
Device protection can investigate relevant software threats. Account recovery, trusted devices, passwords, and security details must be handled through Apple separately.
The Bottom Line
Do not verify your account through this false Apple ID notice. Its 48-hour window and familiar footer don’t authenticate the hosted sign-in page.
If you supplied credentials or codes, use Apple’s genuine recovery and security controls now. Report the email without continuing the sender’s verification process.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.