


Your inbox seems unusually quiet. Then an email arrives saying your mailbox hit a snag, and suddenly there’s an explanation for the messages you might be missing.
It offers one quick step to get things moving again. Before using that shortcut, it helps to understand what you’re being asked to repair.
Overview
A mailbox restriction the sender wants you to accept
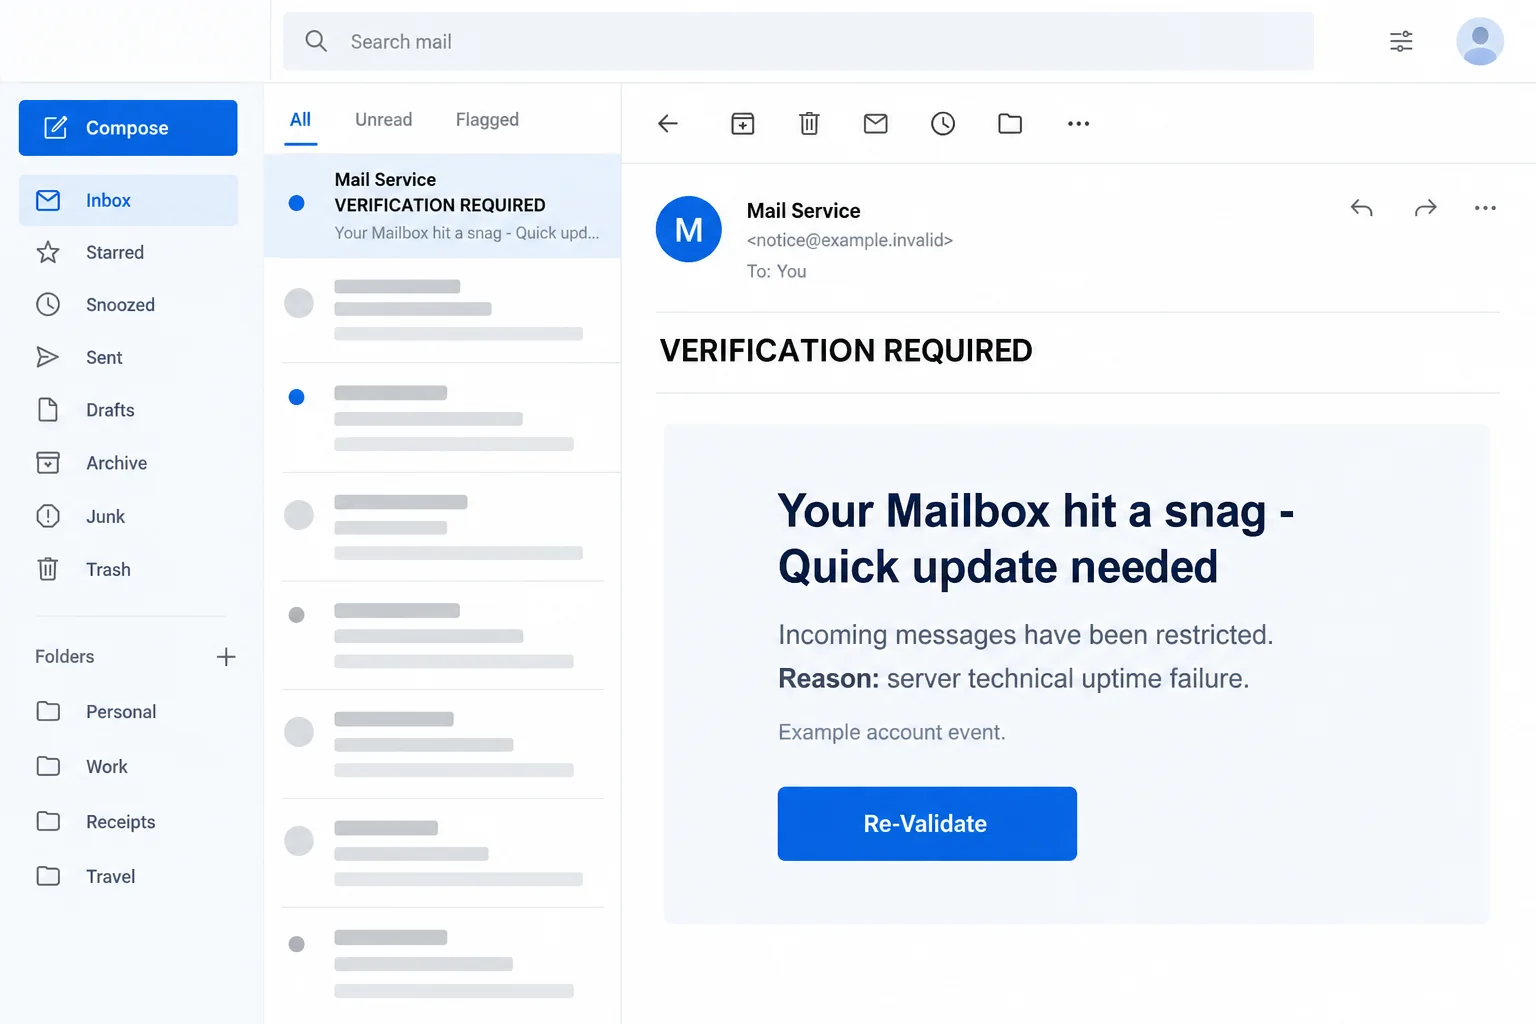
The Your Mailbox Hit a Snag email scam claims that incoming messages stopped because of a server problem. Its proposed solution is a credential-verification link.
The reported version uses a verification-required subject, a precise restriction timestamp, and the explanation “server technical uptime failure.” A Re-Validate button promises to fix it.
That combination makes the message feel like an automated service notice. But technical language isn’t an authenticated diagnosis of your mailbox.
The linked page is reported as an imitation login intended to collect email credentials. No working final destination or original message headers were available for direct testing.
Why missing mail is such an effective worry
You can’t immediately inspect a message you never received. That uncertainty gives the warning more room to work than a claim about something already visible.
A quiet afternoon might mean nobody wrote. It might also mean a real filter, forwarding setting, sender error, or service issue needs attention.
The email turns those possibilities into one confident explanation, then puts its own button between you and a supposedly restored inbox.
- An exact time doesn’t prove that the sender has server records.
- A claim about missing messages should be checked with the genuine provider.
- A password entered on a copied login may be exposed even if the page reports an error.
- Checking mail delivery and securing a disclosed password are separate tasks.
What to do with the warning
Don’t use its repair link. Open the mail service through your usual app, saved bookmark, or independently located provider website.
If you already entered credentials, protect that account without waiting to discover missing correspondence. An apparently normal inbox doesn’t make an exposed password safe.
This warning concerns the deceptive message, not a claim that legitimate providers never send account notices or that every delivery problem is imaginary.
The Detail That Makes the Email Feel More Convincing
A timestamp can seem like the one detail a random sender couldn’t invent. In reality, adding seconds to a date is easy.
What matters is whether an independently accessed account or support team confirms a matching event. Precision and accuracy are different things.
Imagine you’re waiting for a document from a client. Nothing arrives, and this notice appears shortly afterward. The explanation feels tailored to your day.
Yet the sender may know nothing about the client. Your own expectation has supplied the connection between the message and a real concern.
Before accepting that connection, contact the client using an established conversation or number. Ask whether the document was sent and whether any error came back.
That gives you something concrete to investigate. It doesn’t require sharing an inbox password with the website suggested by an unrelated notice.
How the Your Mailbox Hit a Snag Email Scam Works
Step 1: A general service problem becomes your personal emergency
The message announces a restriction rather than asking whether you’re having trouble. This makes the sender’s diagnosis the starting point.
You may begin counting important things that could be waiting: an invoice, application response, password reset, or family message.
That mental list increases the pressure without the email providing evidence of a single missing item. The possible consequences come from your own circumstances.
A familiar sender label can reinforce the impression. But a display name resembling technical support doesn’t establish a relationship with your actual mail host.
Don’t reply with your password or account information to clarify the problem. Verification should start outside the disputed communication.
Step 2: The error explanation makes a login seem like maintenance
The message connects the supposed delivery restriction to a technical failure. It then presents account validation as a quick repair.
This is where two different issues are blurred. A server’s availability and a customer’s credentials are not interchangeable explanations for interrupted mail.
A legitimate service might require you to sign in to see account information. That doesn’t authenticate a particular sign-in form delivered through unsolicited email.
The helpful question is not whether providers ever need authentication. It’s whether you reached the real provider through a route you independently trust.
You don’t have to interpret the technical phrase perfectly. An uncertain diagnosis is a reason to ask your provider, not a reason to surrender credentials.
Step 3: The repair button introduces a counterfeit sign-in
The reported destination imitates a mail-service login. A reader expecting maintenance may accept a password request as the final step toward receiving messages again.
A copied form can use familiar colors, a prefilled address, masked password characters, and ordinary error handling. Those details aren’t exclusive to the genuine service.
Prefilling your address is particularly misleading. A page can receive it through the invitation link without having authenticated you or accessed your account.
Likewise, an encrypted connection says nothing about whether the recipient of your password is your provider. It can protect a connection to an impostor.
Leave the form rather than experimenting with passwords to see which screen appears next. Real account recovery should happen through your established service.
Step 4: An exposed password creates risks beyond delayed mail
Someone who obtains valid credentials may try to access the genuine account. Additional authentication can interrupt that attempt, but the password should still be replaced.
Access to an inbox can reveal conversations, receipts, personal documents, and the services tied to that address. It can also make later impersonation more convincing.
Those are possible consequences, not a finding that this happened to every recipient. Respond to the information you actually gave and any access you can identify.
A reused password widens the exposure. An attacker doesn’t need a second fake notice if the same secret also opens another account.
If the form shows a failure, don’t take that as reassurance. It may have received your information before presenting the error.
Step 5: Normal-looking mail can delay discovery
The account may continue sending and receiving messages. That can make the supposed repair seem successful even if nothing needed repairing in the first place.
Continued access also doesn’t rule out someone else having access. Look at security activity and settings, not just whether today’s inbox loads.
If a work account is involved, tell the organization promptly. Administrators may be able to examine relevant access or revoke sessions you cannot manage yourself.
Don’t wait for a colleague to receive a suspicious message from you. Early reporting can limit the opportunity for a stolen account to be abused.
Keep the original notice available for reporting, but don’t follow it again to confirm whether the page still works.
How to Check Whether Mail Is Actually Missing
Start with a specific message, not the email’s broad claim
Identify something you genuinely expected. Ask the sender to confirm the recipient address, sending time, and whether a delivery failure arrived.
A typed address error and a server rejection require different responses. The supposed outage notice can’t resolve that distinction for you.
For sensitive correspondence, don’t ask the sender to resend private attachments to a new address supplied by the warning. Use an established contact method.
Check the real mailbox before changing settings
Open webmail independently and look at the relevant folders, searches, and filters. A message outside the inbox isn’t necessarily undelivered.
If your mail app and webmail show different results, report that difference to the provider. Don’t assume the suspicious notice explains it.
Review unfamiliar forwarding or filtering changes after a credential exposure. Preserve suspicious settings for your administrator rather than making broad, unexplained configuration changes.
Google’s missing-mail guidance covers searches and settings for Gmail. Other services have their own recovery and delivery tools.
For Gmail, search beyond the inbox, including Spam and Trash. Check storage through the real account too; a genuine capacity problem needs its own remedy.
Don’t immediately delete old correspondence to make room. Confirm the storage issue first, and preserve messages you may need for records or recovery.
If another mail client also accesses the account, mention it to support. Changes made through one connected application can affect what you see elsewhere.
A list of older downloaded messages doesn’t establish that new mail is arriving. Compare a specific recent example in the independently opened service.
Keep those checks limited and deliberate. The email’s broad repair claim is not a reason to reset every mail application or erase local messages.
Give support a useful record
Supply the affected address, approximate time, and a real example of missing correspondence. Use the provider’s verified support channel, not the notice’s reply route.
Tell support whether you entered credentials on another page. Delivery troubleshooting alone may overlook the need to investigate account access.
Don’t publish complete mail headers or private attachments in a public forum without checking for sensitive information. A provider can explain how to share evidence safely.
What to Do if You Have Fallen Victim to This Scam
- Stop trying to complete the validation.
Close the linked form and reject unexpected permission requests. Don’t enter another password because the first attempt supposedly failed.
Note whether you clicked, typed credentials, approved a code, downloaded a file, or installed anything. That timeline helps determine the right response.
- Replace any password you disclosed.
Use the genuine provider from a trusted device. Choose a new, unique password and replace the old one anywhere else you reused it.
If access is lost, start the provider’s official recovery process. Don’t pay someone who claims to restore the account through a private connection.
- Check for ongoing account access.
Review recovery details, recent sign-ins, sessions, forwarding, and unfamiliar mail rules. Remove unauthorized access through the provider’s security controls.
For a managed mailbox, involve IT. Changing a password may be only part of the response when sessions or other access mechanisms remain active.
- Protect important conversations.
Inspect sent mail for messages you didn’t send. If contacts received suspicious instructions, warn them through a separate, established communication route.
Pay particular attention to active invoices or payment conversations. Ask the legitimate sender directly before acting on any unexpected change of banking details.
- Report the attempted impersonation.
Use your email service’s phishing-report option. Gmail’s phishing guidance explains reporting and independently checking suspicious security requests.
Keep a copy if your administrator or provider requests it. Then remove the deceptive message from the inbox so you don’t return to its button.
- Investigate software only if there was software exposure.
If you opened an unexpected download or installed a supposed repair tool, run Malwarebytes and seek trusted help for any suspicious findings.
AdGuard may reduce harmful advertising exposure. Neither product restores mail-server operation or invalidates a password already sent to someone else.
- Verify the actual delivery issue separately.
After securing the account, return to the specific missing-message example with your real provider. Don’t assume account recovery automatically resolves an unrelated delivery problem.
For a personal Microsoft account, Microsoft’s recovery instructions offer a starting point. Workplace accounts should follow the organization’s own support process.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Don’t Hand the Sender a Second Chance
A later message may say validation remains incomplete or your previous attempt didn’t save. That isn’t a reason to revisit the form.
If the genuine provider needs action, you can find it through the real account or ask independently. The suspicious sender doesn’t need another opportunity to direct you.
A caller quoting the restriction time isn’t independently confirming it. They may simply be repeating the notice you already received.
Keep recovery codes and passwords out of chats offering quick help. An authentic-looking support profile can be copied just as easily as an email header.
If you’re helping a relative, ask what happened without turning it into an interrogation. Clear facts and prompt recovery are more useful than embarrassment.
Frequently Asked Questions
Is my mailbox really blocked because this email says so?
The message doesn’t establish a restriction. Check the real service and investigate a specific missing message instead of trusting the sender’s diagnosis.
Does the precise timestamp make the alert genuine?
No. Anyone can add a date and time to an email. A matching event needs confirmation through your independently accessed provider.
What if I was already waiting for an important email?
Contact its sender using details you already trust. Ask about the destination and any delivery error, then troubleshoot through the genuine mail service.
Do I need to change a password after only reading the message?
Reading it doesn’t by itself show credential exposure. Change credentials if you disclosed them or find evidence of unauthorized access, not merely because the notice arrived.
Can the account be exposed even if mail still arrives?
Yes. A working inbox doesn’t exclude another active session or an exposed password. Review access and settings after submitting credentials to an imitation.
Will scanning my computer release the missing messages?
No. Scanning addresses possible malicious software. Delivery questions belong with the mail provider, while stolen credentials require account protection.
The Bottom Line
Don’t use the mailbox-snag email’s Re-Validate button. Its repair story directs you toward a reported counterfeit login rather than a verified service fix.
Check mail through the genuine provider. If you submitted a password, secure the account now and investigate any actual missing correspondence afterward.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.