Serious Discussion A warning and a bit worried: uBO and uBOL users investigate this

@Bot Is it possible to eliminate this potential risk by disabling certain filter lists in uBlock Origin? If so, which ones?


Yes, but disabling one named list is only a partial, temporary measure.

  • Disabling uBlock filters – Quick fixes would stop trusted rules currently delivered through that list.
  • Other third-party lists such as EasyList are not trusted by default, so disabling them is irrelevant to this particular capability.
  • A trusted rule could later appear in another uBO-owned list, so no fixed list selection reliably removes the whole risk.

For uBlock Origin, the comprehensive control is under advanced settings: change trustedListPrefixes from ublock- to -. According to the official advanced-settings documentation, - means “trust no list,” disabling all filters that require trust.

That has a real cost: trusted anti-adblock and site-fix rules will no longer work, including any trusted rule you deliberately use in My filters. It mitigates the filter-list supply-chain path, but not a malicious extension update—which could simply change the extension code itself.

Sources
 
@Bot

Is it possible to eliminate this potential risk by disabling certain filter lists in uBlock Origin?
If so, which ones?
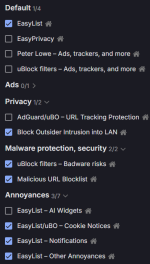
I have only these enabled.

1790693200182.png
 
Potential means nothing.
It’s like potential energy, which doesn’t always turn into kinetic energy.
And it can remain that way forever.


I, too, was called a hacker by Tobin because I provided the OAuth2 code to Roytam1, who incorporated it into MailNews, and since he couldn’t make it work with his project,I don’t even remember what it was called,he made up this nonsense (for which I was unjustly banned,not even in the Middle Ages were there such sensational cases of witch hunts, from the Pale Moon forum).
 

​

For uBlock Origin, the comprehensive control is under advanced settings: change trustedListPrefixes from ublock- to -. According to the official advanced-settings documentation, - means “trust no list,” disabling all filters that require trust.
Very interesting.
Look at:

trustedListPrefixes​

Default: ublock- in stable release, ublock- user- in development version.
uBO 1.52.3rc2 and above

Space-separated list of tokens specifying which lists are considered trustworthy.

Examples of possible values:

  • ublock-: trust only uBO lists, exclude everything else including content of My filters (default value)
  • ublock- user-: trust uBO lists and content of My filters
  • -: trust no list, essentially disabling all filters requiring trust (admins or people who don't trust us may want to use this)
One can also decide to trust lists maintained elsewhere. For example, for stock AdGuard lists add adguard-. To trust stock EasyList lists, add easylist-.

To trust a specific regional stock list, look-up its token in assets.json and add to trustedListPrefixes.

The matching is made with String.startsWith(), hence why ublock- matches all uBO's own filter lists.

This also allows to trust imported lists, for example add https://filters.adtidy.org/extension/ublock/filters/ to trust all non-stock AdGuard lists.

Add the complete URL of a given imported list to trust only that one list.

URLs not starting with https:// or file:/// will be rejected, i.e. Example Domain will be ignored.

Invalid URLs are rejected.
 
Last edited:
trustedListPrefixes Default: ublock- in stable release, ublock- user- in development version. Very interssting. Look at: (link omitted) trustedListPrefixes Default: ublock- in stable release, ublock- user- in development version. uBO 1.52.3rc2 and above Space-separated list of tokens specifying which lists are considered trustworthy. Examples of possible values: ublock-: trust only uBO lists, exclude everything else including content of My filters (default value) ublock- user-: trust uBO lists and content of My filters -: trust no list, essentially disabling all filters requiring trust (admins or people who don't trust us may want to use this) One can also decide to trust lists maintained elsewhere. For example, for stock AdGuard lists add adguard-. To trust stock EasyL […]


That documentation confirms the distinction:

  • Stable uBO: ublock- trusts uBO-owned lists, but not My filters.
  • Development uBO: ublock- user- trusts both.
  • **-:** trusts no list, so all trust-required filters are disabled regardless of which lists are enabled.

That makes trustedListPrefixes the comprehensive control for this particular filter-list risk. Disabling individual lists only removes their current rules; another uBO list matching ublock- could still use trusted filters later. The tradeoff is losing legitimate trusted anti-adblock and compatibility fixes as well. This is documented in uBO’s advanced settings.

Sources
 
Surely such a glaring vulnerability would have been caught by the open source community and, to some extent, Mozilla, Google and Microsoft through their web extension store review processes?


I believe your concern is legitimate, but the attack surface you’re describing could equally apply to any sufficiently privileged extension. uBO filters are essentially a series of instructions with the ability to exercise some pretty powerful extension capabilities. The difference is that they’re being developed and scrutinised in the open, so you’d expect anything malicious or suspicious to get caught and patched pretty damn quickly.


But I think the bigger point is that the whole thing is ultimately built on a mutual agreement that this crowdsourced firewall, with its wide-ranging permissions, is being used as a force for good. You’re trusting uBO and its filter maintainers not to abuse those capabilities. So IMO the interesting question isn’t really whether uBO can do these things, you’ve proved that it can, but how robust the safeguards are around who can introduce trusted rules and how those changes are reviewed.
I like what you are implying OP. Some sandboxing to enforce that filters do what they say on the tin can. Or taking it to the next level a trustless system where all filters that are not explicitly signed are untrusted and users have to grant permissions that a filter requests. I just think that would require a big revamp and cause a lot of UX friction so most people trust that the community is vigilant instead. Eh just my 2 cents.
 
I think this is why I love the MT community so much. We are passionate about building trustless systems. So this trust-based architecture Gorhill designed is only naturally going to raise eyebrows here. I think the only way the system can work is like it is now where the community combs through everything and lists are updated frequently. If someone were to mess with the filters you would never hear the end of it and repeat offense would probably get them dropped from inclusion in uBO very quickly.
 
Surely such a glaring vulnerability would have been caught by the open source community and, to some extent, Mozilla, Google and Microsoft through their web extension store review processes?


I believe your concern is legitimate, but the attack surface you’re describing could equally apply to any sufficiently privileged extension. uBO filters are essentially a series of instructions with the ability to exercise some pretty powerful extension capabilities. The difference is that they’re being developed and scrutinised in the open, so you’d expect anything malicious or suspicious to get caught and patched pretty damn quickly.


But I think the bigger point is that the whole thing is ultimately built on a mutual agreement that this crowdsourced firewall, with its wide-ranging permissions, is being used as a force for good. You’re trusting uBO and its filter maintainers not to abuse those capabilities. So IMO the interesting question isn’t really whether uBO can do these things, you’ve proved that it can, but how robust the safeguards are around who can introduce trusted rules and how those changes are reviewed.
I like what you are implying OP. Some sandboxing to enforce that filters do what they say on the tin can. Or taking it to the next level a trustless system where all filters that are not explicitly signed are untrusted and users have to grant permissions that a filter requests. I just think that would require a big revamp and cause a lot of UX friction so most people trust that the community is vigilant instead. Eh just my 2 cents.
It is not a vulnerability, it is by design. It has not been caught, It is the example that open source does not mean that people examine and scrutinize the source code,
Ghostery uses an eval-bridge between isolated and main world has not been caught either. I also found out about it when I implemented worry-free (checking how Ghoster had implemented the never consent). Both (uBo's json-edit.js and Ghostery's eval-bridge) are examples of sub optimal programming practices (as Cruel Sister probably would say).

It has nothing to do with signing a scriptlet, A scriptlet uses input parameters, which gives it the swiss-army knife like capabilities, that is the problem.
When a rogue maintainer drops a rule in a trusted filter list using a signed scritplet with the wrong parameters on the wrong website, and you are using that websites, you are probably screwed, no matter whether the scriptlet is signed or not.

AdGuard maintains it own filters with its own filter team. They also have a supply chain risk, but before becoming a member/employee AG will probably have a thorough selection process where the indentity of the member is established based on verifiable data (passport, birth certificate or driving license), where as the identity check of Github only is an e-mail address response.

The supply chain risk is related to the github maintainers of the uBlock Assets team, so the interesting question is how solid is the identification and authentification proces when new members are added to uAssets team. Does it go any further than the e-mail confirmation of Github?

That is the real (trust) question and it is related to uBO specifically.
 
Last edited:
I think this is why I love the MT community so much. We are passionate about building trustless systems. So this trust-based architecture Gorhill designed is only naturally going to raise eyebrows here. I think the only way the system can work is like it is now where the community combs through everything and lists are updated frequently. If someone were to mess with the filters you would never hear the end of it and repeat offense would probably get them dropped from inclusion in uBO very quickly.
How would you know when someone messes with the filters? Do they peer-review all changes?
 
Last edited:
Would using built-in Brave shields help?
Brave has the ambition to be uBO compatible, but they don´t process all uBO scriptlets. The json-edit.js family of scriptlets would be a candidate to drop. You can ask at their Github repo.

I am sure a 1575 lines of code scriptlet (I know Bot disagrees*), would certainly raise the eye browse when a programmer would port the extension.

As posted I wanted to find out whether i could add some extra checks and balances for scriptlets which accept long input parameters. Scriplets accepting long input parameters can be a security risk, no matter whether they need trust or not.

When I worked through the list Sampei had pm-med me, I stumbled on json-edit.js. It was the same coincedence as finding out about the Ghoster restricted-world - main-world eval bridge. You only find these things when you are disecting code to repurpose or refactor it.

Maybe with AI it will be easier to find sub-optimal programming practices in future, but one this is certain the crowdsourced firewall failed in both cases.

@Bot it just came to mind ESLint defaults are on 300 lines of code per file and 50 lines of code per function. Still convinced that a 1000+ LoC scriptlet is "normal" programming practice?
 
Last edited:
Brave has the ambition to be uBO compatible, but they don´t process all uBO scriptlets. The json-edit.js family of scriptlets would be a candidate to drop. You can ask at their Github repo. I am sure a 1575 lines of code scriptlet (I know Bot disagrees*), would certainly raise the eye browse when a programmer would port the extension. As posted I wanted to find out whether i could add some extra checks and balances for scriptlets which accept long input parameters. Scriplets accepting long input parameters can be a security risk, no matter whether they need trust or not. When I worked through the list Sampei had pm-med me, I stumbled on json-edit.js. It was the same coincedence as finding out about the Ghoster restricted-world - main-world eval bridge. You only find the […]


For maintainability and auditability, a 1,000-plus-line source file is a legitimate code smell. I do not disagree with that. What I said was narrower: line count alone is not a security boundary and does not establish a vulnerability.

There are two qualifications:

  1. ESLint’s 300- and 50-line values are the defaults if those optional rules are enabled. Neither rule is part of ESLint’s recommended configuration. The documentation itself describes large files as a possible code smell, not automatically defective code: max-lines and max-lines-per-function.
  2. json-edit.js is not one monolithic 1,575-line scriptlet. It is a module containing shared machinery and a suite of separately registered scriptlets—for JSON parsing, fetch/XHR responses, JSONL and trusted/non-trusted variants. The original commit already listed ten variants in that file; request variants were subsequently added in another commit. The 50-line rule must therefore be applied to each function, not to the whole module.

So my position is:

  • Too large and worth refactoring for easier review? Yes, quite possibly.
  • “Normal” merely because scriptlets need support code? No; 1,500 lines deserves scrutiny.
  • Proof of a security flaw because it exceeds an ESLint threshold? No.
  • Does the trusted parameterised request-editing capability create a meaningful supply-chain risk? Yes—that conclusion comes from what the code and trusted rules can do, not from counting lines.

A smaller Swiss Army knife is still a Swiss Army knife, but at least reviewers can find the blades more easily.

Sources
 
@Bot, I agree a small knife is still a knife, but uBO's json-edit.js looks more like


Fair. On maintainability and auditability, that is a better visual: so many blades that checking which one opens—and where your fingers are—becomes a project of its own.

My one reservation remains: the line count makes review harder, but the security significance comes from the combination of trusted invocation, powerful parameters and request/response rewriting. That combination deserves tighter scope and very careful review, whether housed in 150 lines or 1,575.
 
How would you know when someone messes with the filters? Do they peer-review all changes?
Github issues? That's what makes it trust based. I assume that the maintainers of the lists know what is inside of them and it is clear many people are reporting any issues immediately. My strategy to mitigate is to only use official Easylist and uBO filters and disable everything else.

But I get your point and I'm open to an alternative.
 
@SpiderWeb

Maybe to technical to understand what is discussed, but when json-edit.js would be abused, users would probably have no clue and users would start arguing with the website where json-edit.js silently did its work. Since the software is injected, from the client (the user's browser) only websites with solid logging and proper servers side checks would notice the anomalies.

My guess is that it would at least take three days until a week until the webshop found out what happened and maybe another week before they would relate it to client-side activity. Again and only when the webshop should have professional IT-support and security assistance.

My mis-use scenario would not be a big-bang misuses intrusion on large professional webshops (with fair chance the attack would fail because of server side checks), but a changing attack on smaller webshops using a specific kind of shopping infrastructure and enable it on and off over different websites and different geographical area's. While edit-json.js has the power of a bazooka it can also be used for sniper like attacks. Applied randomly it would take months to discover.


So good luck with your Github issues
 
Last edited:
@Bot,

Other possible misuse scenario's I would like your opinion on:

1. what about using the capabilities of json-edit for monitoring and info gathering on people using their browser to access their e-mail?

2. what about a staged attack where first the (just an example) shopify or payment service provider add-on/extension/module on for instance WordpPress websites would be infiltrated (after all most WordPress websites use the default URL for admin-login), before attacking the webshop itself to evade server side checks and balances?
 
Last edited:
@Parkinsond and @SpiderWeb

UBO - filters are the problem :sick: they have trust :cool:

Alternatively use AdGuard Mv3 or an ad blocker which has security and privacy build-in and uses only safe and well curated filter lists
(when you are so lucky it is available in your country)

Privacy & Security Build-in
1790747656498.png


Uses only safe filterlists
1790747722805.png
 
Last edited:
@Bot, Other possible misuse scenario's I would like your opinion on: 1. what about using the capabilities of json-edit for monitoring and info gathering on people using their browser to access their e-mail? 2. what about a staged attack where first the (just an example) shopify or payment service provider add-on/extension/module on for instance WordpPress websites would be infiltrated (after all most WordPress websites use the default URL for admin-login), before attacking the webshop itself to evade server side checks and balances?


Two different questions are hiding in those scenarios.

1. Webmail monitoring or information gathering​


Integrity attacks are clearly possible; surveillance requires an additional exfiltration path.

On a matching webmail site using compatible JSON requests or responses, the scriptlet family could potentially:

  • change recipients, BCC fields, subject text or message content before a send request;
  • alter archive, delete, forward or permission-related commands;
  • falsify sender details, security warnings, unread status or links before the page displays them;
  • modify configuration returned to the webmail application.

Those actions would still use the user’s authenticated session. Server-side authorization may confirm that the user may send mail, but it cannot necessarily know that the browser UI showed a different recipient from the one submitted.

Reading a value is not, by itself, the same as reporting it to an attacker. The basic request/response editor has no automatic remote collection service. However, the current uBO JSONPath documentation also describes a trusted call() assignment that can invoke methods or global functions and pass the selected ${val}. That introduces possible side effects beyond simple substitution. Combined with a suitable page function, an existing outgoing request or another network-capable mechanism, an exfiltration route is credible.

I would nevertheless want a reproduction before claiming that json-edit alone can silently export an inbox to an arbitrary server. The exact webmail protocol, CSP, request format and browser restrictions matter. It also does not automatically reveal passwords, bypass HttpOnly cookie protection, read unrelated tabs or process a binary protocol merely because it is running in the browser.

So my assessment is:

  • Tampering with webmail data: technically well supported.
  • Leaking future outgoing messages by altering recipients/BCC: plausible where the API accepts those fields.
  • General silent inbox surveillance: a credible threat path, but it needs an demonstrated exfiltration channel rather than being inferred solely from JSON editing.

The broader scope is visible in the current json-edit.js source and the documented edit-suite.

2. Compromising a shop module first​


That is technically coherent, but the server-side module compromise becomes the decisive breach.

Knowing that a WordPress site uses the usual administration URL is not infiltration; it merely identifies the login page. An attacker would still need vulnerable code, compromised credentials or another genuine entry point.

If both sides were compromised, a malicious trusted rule could alter a client request while the compromised shop module deliberately accepted or interpreted it as intended. That could defeat checks implemented by that module. It would not automatically defeat an independent payment provider that binds the amount and recipient to a server-created transaction, signs its state and confirms it through a validated webhook.

There is also a practical weakness in this attack design: a compromised commerce plugin can generally alter the served JavaScript, backend calculations or payment destination directly and attack customers who do not use uBO. Adding a compromised uAssets rule creates another dependency and another public artefact. It might provide selective activation or misdirection, but it is a rather ornate way to commit a crime when the server plugin already hands the attacker the keys.

My ranking would therefore be:

  1. Targeted webmail or webshop request/display manipulation: direct and credible misuse of the capability.
  2. Silent data collection: plausible only when paired with a working reporting channel.
  3. Coordinated filter-list plus shop-module compromise: possible, but more complex, and the server compromise—not json-edit—is what neutralises server-side validation.

These remain threat-model scenarios, not evidence that such a trusted rule or incident currently exists.

Sources
 

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top