Full Story:
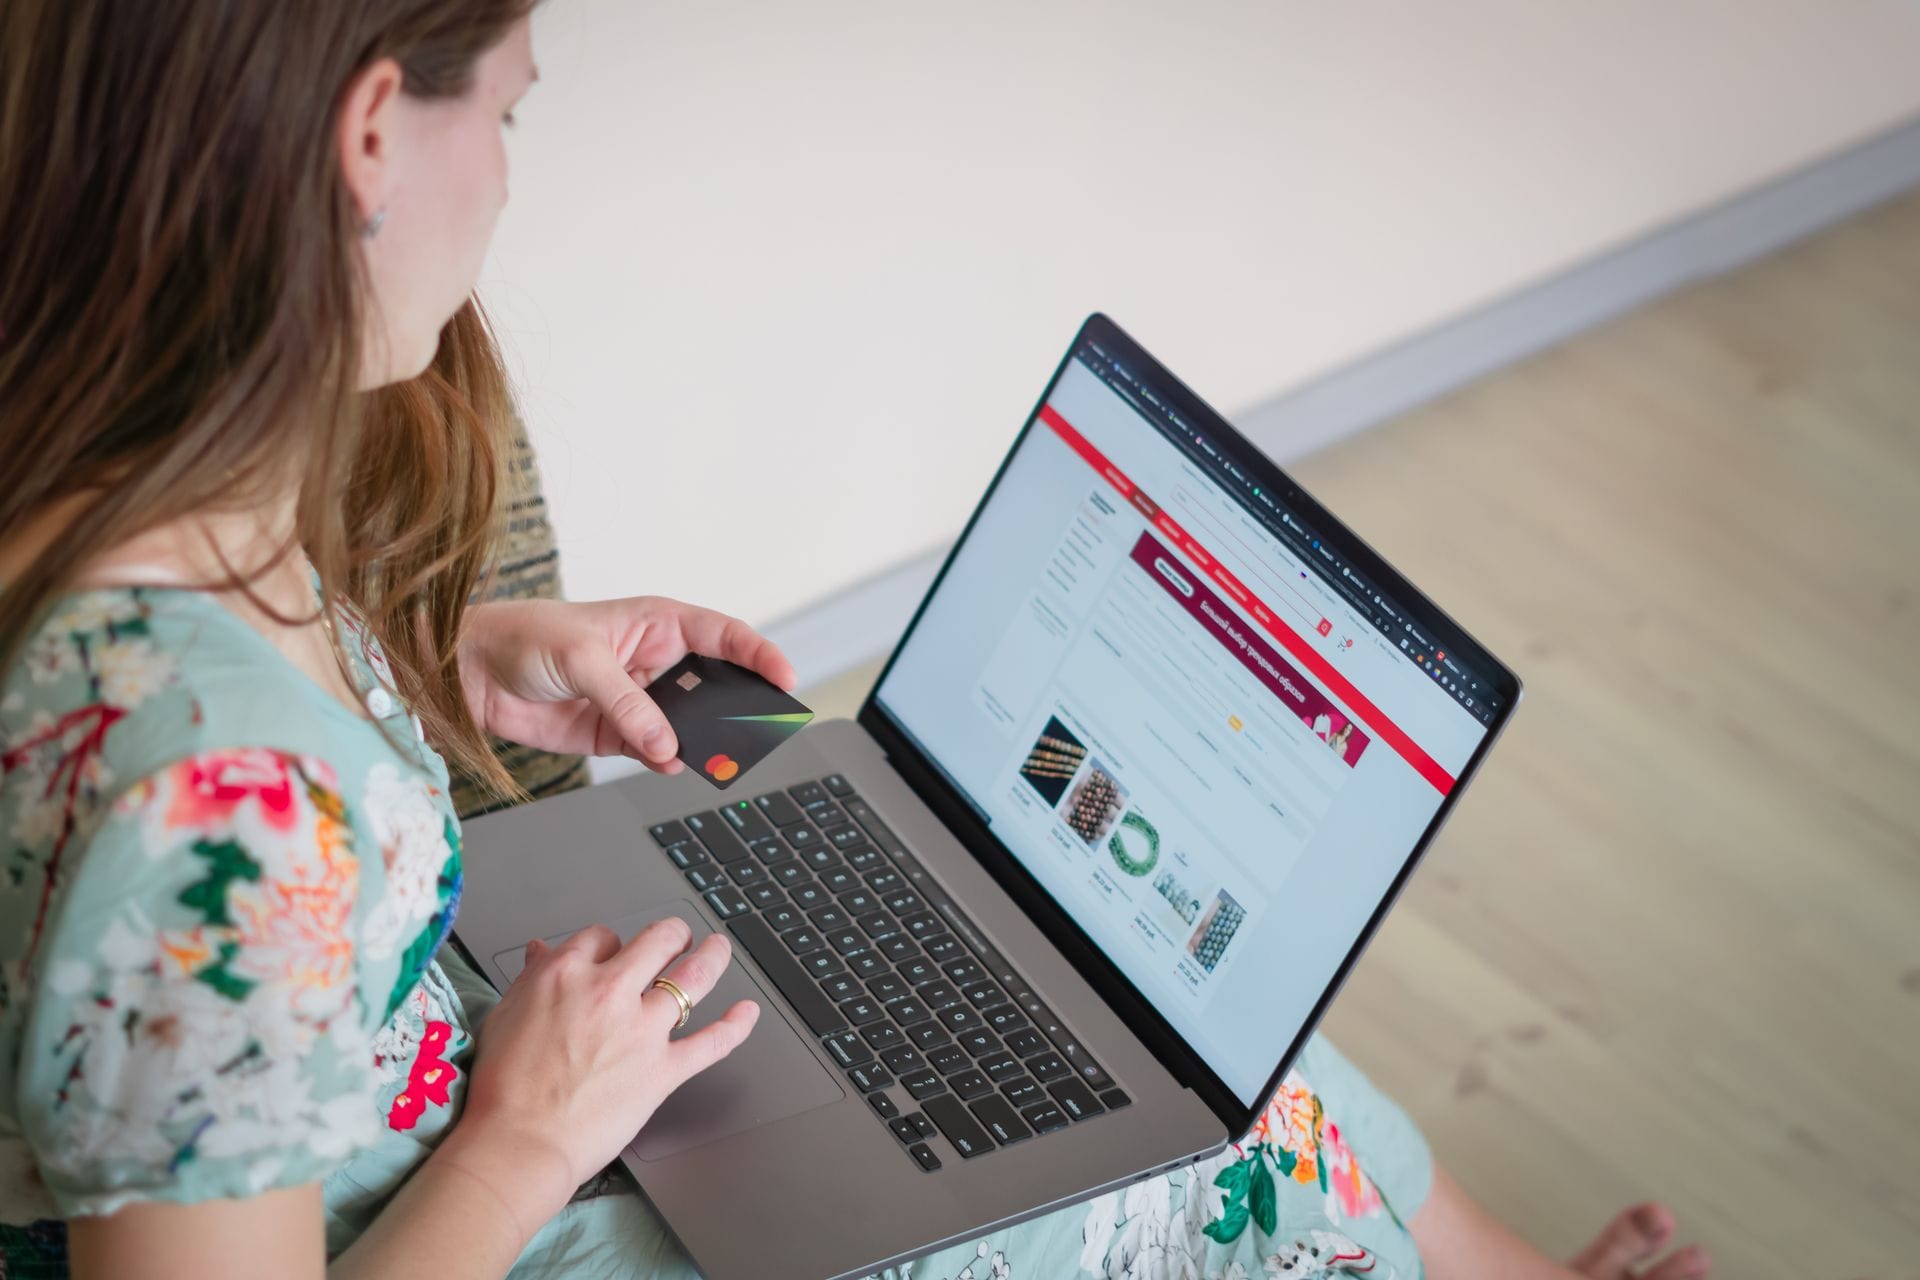
Major banks are calling for security and privacy safeguards as AI agents begin shopping and paying on consumers' behalf
www.bitdefender.com
Hi Brownie2019, the concern is well founded: an AI shopping agent combines access to personal data, payment capability and permission to act, so a compromised or badly designed agent could do more damage than an ordinary recommendation chatbot. That does not show these systems are already being widely exploited, but it explains why banks want safeguards before autonomous purchasing becomes routine.
Where the risk changes
With an ordinary shopping assistant, the user normally chooses the merchant and approves payment. An agentic system may also select the seller, accept terms, disclose delivery details and complete the order. That creates several distinct risks:
- Excessive authority: a vague request such as “buy the best one under $1,000” leaves room for choices the user did not intend.
- Merchant or agent impersonation: criminals could imitate a legitimate service, manipulate where the agent shops, or redirect payment.
- Instruction manipulation: malicious content in product listings or websites could try to influence an agent. Whether that succeeds depends on the platform’s design and isolation controls.
- Privacy concentration: prompts, preferences, browsing, delivery information and transaction history can form a much more revealing profile when kept together.
- Disputes and accountability: it must be clear whether the user, agent provider, merchant or payment provider authorized each step.
The last point is less glamorous than “AI hackers,” but probably just as important. If nobody can clearly reconstruct why a purchase happened, fraud handling becomes a bureaucratic séance.
What sensible safeguards look like
A trustworthy service should not receive a blank cheque. Useful controls include:
- Explicit approval before payment, at least for unfamiliar merchants, subscriptions or purchases above a user-set limit.
- Narrow permissions covering a particular purchase, amount and time window rather than permanent access to everything.
- Tokenized or virtual payment credentials with merchant, category or spending limits where the bank supports them.
- A clear confirmation screen showing the exact product, seller, total price, recurring charges, delivery address and return conditions.
- Instant revocation and transaction notifications, with an understandable record of what the agent did.
- Data minimization, so comparison shopping does not automatically expose full payment or identity data to every service involved.
- Separation between untrusted web content and system instructions, backed by testing and monitoring rather than merely telling the agent to behave.
For consumers, the prudent early approach is to let an agent research and compare, while retaining final purchase approval. Avoid giving a new service unrestricted card details or long-lived access to email, retailer and bank accounts. Bank transaction alerts and virtual-card limits also reduce the consequences if something goes wrong.
What remains unproven
The article’s threat scenarios are plausible, but the material supplied here does not establish how common real-world exploitation of shopping agents currently is. Nor does it identify one standardized technical or regulatory framework that every provider follows.
So this should be read as a warning about the enlarged attack surface, not evidence that every shopping agent is unsafe or that a wave of agent-specific fraud has already arrived. The decisive questions for any service are practical:
What can it spend, when must it ask, what data can it access, and how quickly can those permissions be revoked? If those answers are vague, convenience is being purchased with rather too much trust.