



- Content source
- https://gbhackers.com/armorsteal-malware-attack/
Read more on:ArmorSteal, a Python-based Windows malware kit. It steals credentials and crypto wallets, hijacks clipboard addresses, and runs a hidden Monero-style miner.
The miner shuts down whenever a user opens Task Manager or another monitoring tool. Zscaler ThreatLabz documented the family on 22 October 2026. The Seqrite sample is newer than that report and an earlier June 2026 build.
Victims searching for Chocolatey or the Microsoft Activation Scripts land on typosquatted pages.
These pages display a PowerShell command that installs the real tool and quietly drops the kit into C:\Windows\SystemHealth\Update.
The kit ships with its own Python 3.11 runtime. Every script is protected with the trial version of PyArmor 9.1.7.
Three scheduled tasks keep it alive: SysCheck2, SysCheckX and the newly observed SysHeal.
The two SYSTEM tasks have no author, which suggests the malware registered them itself.
It queries ipinfo.io and exits with a fake “Memory is insufficient” error if the network owner is Google, Amazon, Microsoft or Azure, which blinds many cloud sandboxes.
Seqrite recovered the code because trial PyArmor builds ship the decryption key inside the bundled runtime.
Seqrite Researchers said that, the controller, SysMon.py, builds a victim ID from the motherboard serial number. It then tries 11 C2 domains in priority order, so blocking datamons[.]org alone achieves little.
ArmorSteal Malware Attack
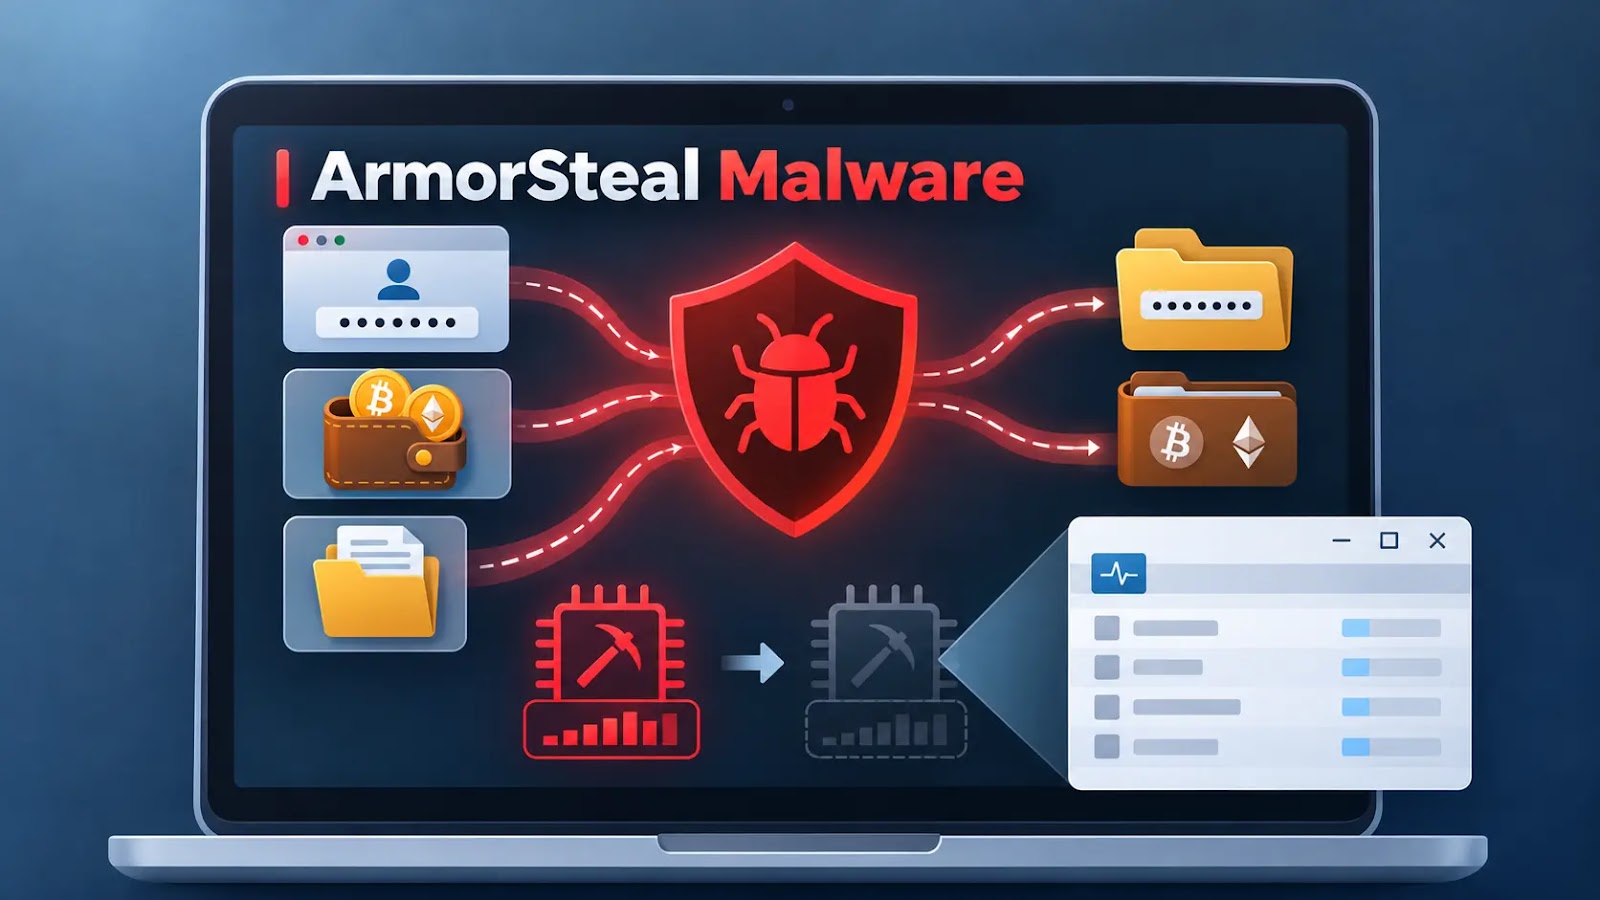
ArmorSteal Malware Steals Passwords and Crypto Wallet Data, Hides Mining When Task Manager Opens
ArmorSteal, a Python-based Windows malware kit. It steals credentials and crypto wallets, hijacks clipboard addresses, and runs a hidden Monero-style miner.
 gbhackers.com

