AVG AntiVirus Free - March 2021 Report

Please let me/us know where you got this information from ? You meant this for Avast/AVG only ?
Or also any official statement from other companies like Kaspersky, BitDefender, Symantec, etc. ?
I apologize for the delay in replying.
I speak obviously from personal experience, when I test an AV I also go to see how long it takes to respond positively to a "compromise".
Furthermore, I monitor both the sending of samples from the program itself and from the dedicated portal (if it is available).
AVG/Avast and Kaspersky are among the fastest. Also, Webroot but only with some exes.
 
Please everyone keep in mind, this thread is related to AVG tests only, so it's better to discuss never about different AVs otherwise all Hub-Report-Threads are looking like a mess... Forums-sections for any major Antivirus is available (link below), there everyone can asking and discussing:

 
Well, this time, at least, WebAV detected something... I know as WebAV blocked the connection, that blank mshta.exe form remained running, probably without any suspicious activity, probably Final System Status could be System Not Clean... but there is also the hidden registry key in Windows AutoRun section, so finally I had to consider tagging the System again as infected...
 
I think this topic is getting out of the way, polluted, it should be closed for comments, because someone always appears defending your favorite antivirus when the system was infected, as if the tester had done something wrong to explain the failure of your favorite antivirus, if the result is infected, it is because it was infected, they know more than anyone here how an infection works, this is already very annoying :rolleyes:
 
I think this topic is getting out of the way, polluted, it should be closed for comments, because someone always appears defending your favorite antivirus when the system was infected, as if the tester had done something wrong to explain the failure of your favorite antivirus, if the result is infected, it is because it was infected, they know more than anyone here how an infection works, this is already very annoying :rolleyes:
There is a discussion about the function of the AV that is relevant. A discussion that could lead to a better understanding for everyone. That’s part of the point of the thread. People have different feelings on different solutions. There is no requirement that you monitor this thread.
 
This latest Hub test is done to be true as always by @harlan4096 if anyone disagree it's fine but again here is no need to discuss about any test!

There is a discussion about the function of the AV that is relevant. A discussion that could lead to a better understanding for everyone. That’s part of the point of the thread. People have different feelings on different solutions. There is no requirement that you monitor this thread.

Why you believe to know what is the real purpose of this thread or any other Hub-Test-Report threads?

Just to inform everyone, endless discussions about Hub test results aren't acceptable and will be reported to Forums Staff!
 
Last edited by a moderator:
Why you believe to know what is the real purpose of this thread or any other Hub-Test-Report threads?
Apparently I stand corrected. I had seen such discussions in the past and found them informative. I have always trusted and appreciated @harlan4096 ’s testing and transparency. I don’t see a problem with someone having a differing conclusion, but you are correct that I did not design the purpose of the thread and misunderstood. In the end @harlan4096 made his determination and has stated his logical reasoning for such, which I am very appreciative of.
 
Let me try to explain a bit more about "testing procedure"
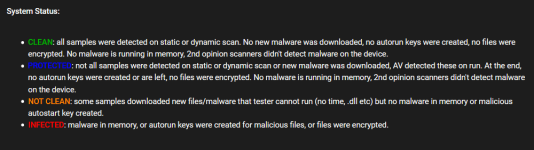
This sample was able to set an hidden autorun for mshta.exe (one of many legitimate LOLBins), that is a kind of bypass as AVG doesn't blocked nor detected this autorun, so we have two choices: either testing system would be Not Clean or Infected, but any working malicious autorun is more a sign for infected, according to the Hub testing rules (screenshot below):

HUB.png
 
Let me try to explain a bit more about "testing procedure"
This sample was able to set an hidden autorun for mshta.exe (one of many legitimate LOLBins), that is a kind of bypass as AVG doesn't blocked nor detected this autorun, so we have two choices: either testing system would be Not Clean or Infected, but any working malicious autorun is more a sign for infected, according to the Hub testing rules (screenshot below):

View attachment 255109

Wouldn't it be good if there is an added "attack chain suspended" status? Sometimes, like in this case, system is infected but the malware is not capable of doing it's malicious purpose.

By the way, where is my first message I posted just a while ago?
 
Read again the test :) ... for about 2 weeks now I enabled HM, but since probably most of standard users don't enable it, I 1stly tested with HM on and then also tested with MH off :)
My bad! I did not see this
Hardened Mode could not stop it and even enabling PUP detection in AVG -> not detected...
 

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top