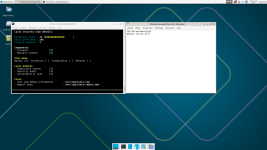
in Debian 12.13 = Hardening index : 68 [############# ]@simmerskool Whats your score?
in fedora 44 = Hardening index : 77 [############### ]
fedora_kinoite too hardened to lynis (just kidding...)


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Installation is optional. Your notification settings stay under your control.
in Debian 12.13 = Hardening index : 68 [############# ]@simmerskool Whats your score?

No. But in futureHave you used Zoho Vault?

How is your experience with fedora kinote?in Debian 12.13 = Hardening index : 68 [############# ]
in fedora 44 = Hardening index : 77 [############### ]
fedora_kinoite too hardened to lynis (just kidding...)
better & better, I'm liking it and not feeling that I need to boot fedora 44 / Gnome. I got bogged down with fedora_silverblue atomic (gnome) a couple of years ago because I was always updating the OSTree everyday, but immutable / atomic you do not really have to do that. update the flatpak software and maybe update OSTree once a week or interval that suits you. PS I tried the openSUSE kalpa atomic with discovered it's still Alpha and had immediate issues with my VMware, while regular Tumbleweed KDE Plasma was excellent. But liking the atomic-ness of KDE Plasma on fedora_kinoite.How is your experience with fedora kinote?

Excellent question that does need some elaboration, but I am far from a linux expert, I'm just a user, so I asked the deep thinker here chatGPT 5.5 (probably instant):@simmerskool I am interested in how you look at the security of Kinoite. I understand from immutable OSNix there has to be a directory that is writable for the OS to update itself. It is just that the OS mounts / as non-writable. So an attacker who obtained root can say hostnamectl and find out this is Kinoite and umount the / and do whatever he wants. If the attacker has Not obtained root, then he can't modify anything, in Kinoite or non-Kinoite. So what does this Kinoite gain via being immutable? It is just safer from update accidents, and gives you rollback capability. There is no stop-an-attacker-security gain.
Kernel Hardening:sudo nano /etc/sysctl.d/99-hardened.confInsert:net.ipv4.conf.all.rp_filter = 1net.ipv4.conf.default.rp_filter = 1net.ipv4.conf.all.accept_redirects = 0net.ipv6.conf.all.accept_redirects = 0kernel.dmesg_restrict = 1Stability: Command - sudo nano /etc/sysctl.confInsert:vm.swappiness=10
To make these settings take effect right away without rebooting.sudo sysctl --system

IP Spoofing ProtectionWhat does this do ?

I plugged it into ChatGPT 5.5 for its spin. generally favorable to this hardening with FYI "important Debian 13 wrinkle: do not use /etc/sysctl.conf as the main method. Debian 13 release notes say systemd-sysctl no longer reads /etc/sysctl.conf; use /etc/sysctl.d/*.conf instead." @Captain Awesomesudo nano /etc/sysctl.d/99-hardened.confInsert:net.ipv4.conf.all.rp_filter = 1net.ipv4.conf.default.rp_filter = 1net.ipv4.conf.all.accept_redirects = 0net.ipv6.conf.all.accept_redirects = 0kernel.dmesg_restrict = 1Stability: Command - sudo nano /etc/sysctl.confInsert:vm.swappiness=10
What does this do ?
Its all about order; actually latest 13.5 read in that order in a XFCE environnement :I plugged it into ChatGPT 5.5 for its spin. generally favorable to this hardening with FYI "important Debian 13 wrinkle: do not use /etc/sysctl.conf as the main method. Debian 13 release notes say systemd-sysctl no longer reads /etc/sysctl.conf; use /etc/sysctl.d/*.conf instead." @Captain Awesome

Added: Chkrootkit,rkhunter
So oldskool, do they even work anymore? It's been years.Members who viewed this thread in the last 5 minutes
Continue exploring the conversation.