Serious Discussion COMSS.TV Testing: Best Antivirus January-February 2024

How is Quickheal above Avira? I don't get it. (In the first result I mean)

translated_image_en (1).png
 
brambedkar59, Avira > files encrypted - NO.
QuickHeal > files encrypted - YES.
Their tests are very comprehensive.

YRi5wJD.png
Ahh ok, thanks. That was such a weird way of representing the results, could have just inserted one more column for file encryption in the first sheet. I thought there were 2 separate tests, first for all other malwares while second test just for ransomwares.
 
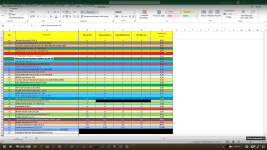
I downloaded his table, available here:
таблица результатов

And watched the ZoneAlarm review, here:


The reason it is blacked out, is because some sort of blocker (blocked his keyboard and stuff) was activated.
1724081797025.png

ZoneAlarm left 96 files not processed, he checked the hashes and they were matching, which means the security solution did not process them.

He bombarded ZoneAlarm with the remaining 96 malware files.
On the video it can be seen that it was processing many samples, he should have allowed some time.
Eventually, it would have been remediated, but given that a single one may take 1-1.5minutes to be properly removed, for all the samples he executed, it could have taken about 15-20 minutes.

In addition, all his malware files were executables, that downloaded one by one or dropped on disk by archiver, download manager, other malware, etc. will be locked and emulated.
As of the last 2 versions, ZoneAlarm allows files to manually be sent for emulation too.
 
Last edited:
What do you mean bombarded? Did he use a script to execute all the files at the same time?
Asking because I see that he executed the files one by one.
btw, he always tests on a real machine. if that matters.
Does it make any difference if it is tested on a real machine or a virtual machine?
edit: I read your edited post...he should have given the program a little more time to deal with the infection?
 
What do you mean bombarded? Did he use a script to execute all the files at the same time?
Asking because I see that he executed the files one by one.
btw, he always tests on a real machine. if that matters.
Does it make any difference if it is tested on a real machine or a virtual machine?
At one point I saw him selecting about 10 files and executing them at once, but before that, it was already processing and displaying alerts. ZoneAlarm has very slow and very thorough processing and generates a full forensics report that for every malware includes what was the damage, network connections, which country the servers are in, mitre ATT&CK matrix, what was remediated, VT lookups, etc. All this takes time and resources. In a real world scenario, all this malware will not be executed.

As to real vs virtual machine, yes. It does make difference as malware could detect the VM and refuse to deliver its real behaviour.

edit: I read your edited post...he should have given the program a little more time to deal with the infection?
Yes, first of all, all these files were not emulated. One of the ZoneAlarm powers is the real time emulation that sends to the sandbox. I don't even think that emulation will accept that many malware files, from his whole pack. Second, I saw anti-bot (extension to behavioural blocking) and other alerts already popping up. An alert from ZoneAlarm appears only once the infection is fully dealt with and the full forensics report is generated, not any earlier than that.

He should have just let ZoneAlarm deal with all that, after which, it would have asked for a restart. Then, he should have restarted the VM if he wants this blocker malware to go away.

1724082710154.png
 
Last edited:
Microsoft Defender beat both Bitdefender and Kaspersky???
There is this column before “Coefficient of infections” (last one) that says “damages in other areas of PC”. On Defender, it says yes. On Bitdefender it says “no”.

I don’t know, it’s very difficult to interpret.

The column before that says “damage in personal files”.
 
Well I speak Russian and still didn’t understand so there is that. I also didn’t understand that “coefficient of infections” which for Panda is over 200%.
The only way I can interpret this is that the infection was so severe that the malware that infected the original file was infected by other malware... :alien:
 
There is this column before “Coefficient of infections” (last one) that says “damages in other areas of PC”. On Defender, it says yes. On Bitdefender it says “no”.

I don’t know, it’s very difficult to interpret.

The column before that says “damage in personal files”.
Thanks for clarification, I didn't notice that because I don't understand Russian.

But I watched the Microsoft Defender video test and when he scanned with second opinion scanners both HitmanPro and Malwarebytes found nothing, nothing clear how he determined the results.
 

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top