

The MalwareTips app
Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
- Home Screen access
- Optional push alerts
- Your community
You're ready to explore.Explore what's new
Installation instructions
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Keep up with your conversations
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Crystal Security 3.5
-
 Thread starter
Kardo Kristal
- Start date
- 1,165 Replies
- 286,343 Views
- Status
- Not open for further replies.
N
NullByte
Hello,
I have a question about the product, I've seen this product perform very well and I'm wondering if I use the "dynamic shellcode injection" method on a safe file and insert a backdoor or any type of malware and I allow the "installer" that drops the malware will still infect the PC (the file is also digital signed as the installer, I copied the digital signature from the installer) ? Are the files still checked even if you allow them ?
Thanks

Uncheck "Start as Admin" solved this problem but is there any downside if it is set like this?
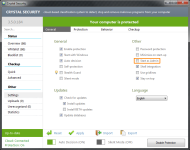

I personally unchecked "trust applications with digital signature"Hello,
I have a question about the product, I've seen this product perform very well and I'm wondering if I use the "dynamic shellcode injection" method on a safe file and insert a backdoor or any type of malware and I allow the "installer" that drops the malware will still infect the PC (the file is also digital signed as the installer, I copied the digital signature from the installer) ? Are the files still checked even if you allow them ?
Thanks
Interesting question

Me too @DardiMI personally unchecked "trust applications with digital signature"
Interesting question
 .....It is unchecked in all my security software that gives that as an option
Good behavior ! You could received soon an anonymous phone call (with my voice modified - er - from a unknown Peron) to be recruited !Me too @DardiM
Questions :
- Do you like penguins ?
- Do you like wearing costumes ?
- Can you Drive high technological vehicles ?
HaHaGood behavior ! You could received soon an anonymous phone call (with my voice modified - er - from a unknown Peron) to be recruited !
Questions :
- Do you like penguins ?
- Do you like wearing costumes ?
- Can you Drive high technological vehicles ?
Q1- I very much like Penguins (especially those that use Crystal Security)
Q2- No experience.It would depend on the specific costume,and the nature of the mission that requires it.
Q3- Only Automatic/Stick-Shift Cars ,& Reach/Counter-Balance Forklift Trucks at present..
(unless the Nostromo & Millennium Falcon count)
Apologies Kardo...
Back to Crystal Security..
Currently using 3.5.0.184..and all is working great

How to set CS to bypass UAC at startup?
Hi @Av Gurus,
Please try out the following method with Task Scheduler to disable UAC prompt for specific application: http://lifehacker.com/how-to-eliminate-uac-prompts-for-specific-applications-493128966
Uncheck "Start as Admin" solved this problem but is there any downside if it is set like this?
When program is elevated with limited rights then Self-protection and Stealth Guard will be disabled.
In Checkup mode some files are not analyzed because of the access rights.
Hello,
I have a question about the product, I've seen this product perform very well and I'm wondering if I use the "dynamic shellcode injection" method on a safe file and insert a backdoor or any type of malware and I allow the "installer" that drops the malware will still infect the PC (the file is also digital signed as the installer, I copied the digital signature from the installer) ? Are the files still checked even if you allow them ?
Hi @NullByte,
Thanks for the interest.
Yes. It is vulnerable in such way. It also depends on many factor. It can pick-up modified file in some cases.
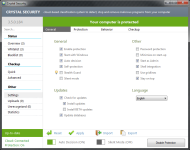
If you want highest protection then I suggest to enable Stealth Guard mode and disable Trust applications with Digital signature under Settings. You can also decrease suspicious and unsafe file detection ratio to improve 0-day malware detection.
Currently using 3.5.0.184..and all is working great
Hi @Logethica,
Thanks for the feedback.
Regards,
Kardo
N
NullByte
Thanks, when you can, change the icon it looks like it's fake security product and if you can add some type of checking in future that will be amazing.
and if you can add some type of checking in future that will be amazing.
Thanks, when you can, change the icon it looks like it's fake security product
@NullByte,
You are welcome and thanks for your suggestions.
If there is any issue, question or feedback then feel free to let me know anytime.
Regards,
Kardo
Change the icon ? Why !? I find it's a nice icon ... Have you seen the details (zoom)Thanks, when you can, change the icon it looks like it's fake security product

N
NullByte
It doesn't go well with the website or the product design (maybe he should change the colors). The product UI looks cool similar to ESET
The product UI looks cool similar to ESET
@NullByte
Thanks. UI is a mixture of ESET (gray bar) and Avast (left menu) and my own ideas.
Currently there is a plan to improve notifications (updated action buttons, visual improvements etc..) and probably I will make some changes in Checkup mode (based on the users feedback). After that I want to add multilingual support which is one of the most requested feature.
You can find preview of the notifications from here.
Regards,
Kardo
Last edited:
Crystal Security is awesome
Hi @techienerd1,
Thanks! I am glad you like it.
If you have any question, suggestion or feedback then please let me know.
Regards,
Kardo
N
NullByte
Hello,
If it's possible can you give me more info about:
Collective Cloud, Crystal Cloud, Internal Engine and Heuristic Engine (just some basic info that you can make public), BTW, I love the new notification.
If it's possible can you give me more info about:
Collective Cloud, Crystal Cloud, Internal Engine and Heuristic Engine (just some basic info that you can make public), BTW, I love the new notification.
Hello,
If it's possible can you give me more info about:
Collective Cloud, Crystal Cloud, Internal Engine and Heuristic Engine (just some basic info that you can make public), BTW, I love the new notification.
Hi @NullByte,
Thanks for the interest.
- Collective cloud - based on VirusTotal (API integration)
- Crystal cloud - based on feeds to collect malware information from several sources
- Heuristic engine - byte based detection
- Internal engine - hash based detection
Regards,
Kardo
Hi @NullByte,
Thanks for the interest.
Heuristic and Internal engines can work in offline mode. Crystal cloud engine stores latest malware information on your computer which is useful for offline usage. Crystal cloud checks feeds after some interval automatically.
- Collective cloud - based on VirusTotal (API integration)
- Crystal cloud - based on feeds to collect malware information from several sources
- Heuristic engine - byte based detection
- Internal engine - hash based detection
Regards,
Kardo
Tested CS with Collective cloud turn off , just a couple of malware, and system get very infected, no pop-ups from CS.
Tested CS with Collective cloud turn off , just a couple of malware, and system get very infected, no pop-ups from CS.
@Av Gurus,
Thank you for the feedback.
Probably it bypassed Internal and Heuristic engines. I guess that all other engines flagged file as clean and white-listed tested files automatically (without any notification). I believe that it is good to enable Stealth Guard mode while Collective cloud is disabled.
I'll try to improve other engines detection with newer versions.
Regards,
Kardo
H
hjlbx
@Kardo Kristal
CS 3.5
W10 Home
Bug Report
CS detects file as suspcious
In alert check detection
List of AV scan engines shows which scan engines detect
Overview
Analyze Selected (suspicious) File
Alert shows detected
Select Details
Entire list of AV scan engines shows no detection (all clean) - the detecting AV scan engines were absent from the list
After I enabled Stealth Guard and re-analyzed the file, the detecting AV scan engines reappeared in the list
I suspect alert display bug
I suspect display\alert bug
Last edited by a moderator:
- Status
- Not open for further replies.
Recently browsing
Members who viewed this thread in the last 5 minutes
You may also like...
-

-
 Advanced Plus Security harlan4096's PC Security Config
-
 Advanced Security Spartan's PC Security Config
-
 Software Review Avira Free Security 2026
-
