Advice Request Is there a way to scan a file using Eset's Liveguard?

Share practical recommendations that address the author's needs.
is there a way to scan files that are already existing on my pc using the liveguard feature? Would this feature be any different or special then running it with the normal scan? My main reason to do this is because I want to test malware that is currently not detectable by any antivirus and just curious if the liveguard can detect.
 
Well websites like this Hatching Triage | Behavioral Report
and https://analyze.intezer.com/analyses/c0af7722-0713-4bc9-acb5-f82ed0c9e7b9 tell me that it is a virus but all the antiviruses don't detect it.
You could try to analyze it on AnyRun and see its actions in real-time.


I am currently trying to download the sample but somehow it's progressing really slow. How big is the file size if I may ask?
 
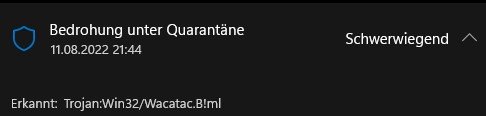
Instantly detected by Microsoft Defender. On VT however it's not detected.

Screenshot 2022-08-11 214526.jpg
 
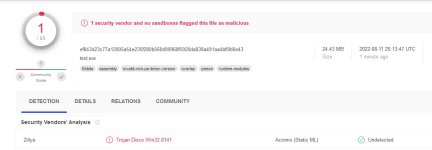
the one that has 0/71 on virus total. but apparently you ran the file that i sent you? and the guy that owns the file has your stuff bro
I can confirm that MD now also detects this sample. Seems like it was detected after execution and now everybody is protected through the Microsoft Defender Cloud. @SeriousHoax experienced the same. (y)
 
Was it the zip file or the file where you got this detection? My Defender doesn't detect. At the moment detected by G-Data on VT.
Also, off-topic Google has added an AI on VT today.
Just wondering if you talking about same hash of sample, VT first submission: 2022-08-09

8A6D1261-86D2-4B6B-8D3D-F5E04C30FCDD.jpeg
40B0A26F-CF0C-4CE9-B369-6732ACEB1C0F.jpeg
 
Last edited:
the one that has 0/71 on virus total. but apparently, you ran the file that i sent you? and the guy that owns the file has your stuff bro
Don't worry. Necessary steps were taken.
Just wondering if you talking about same hash of sample, VT first submission: 2022-08-09

View attachment 268517
View attachment 268518
Yeah, this one. As @SecureKongo said, now MD users are protected from this one.
It wasn't detected by MD on execution for me but 5 minutes later when I entered the folder, MD detected it as ""Trojan:Win32/Bearfoos.A!ml".
So metada/telemetry collected from my infected system helped MD AI/ML models to verify this as an actual malware. This is the demonstration of post-infection detection that @Andy Ful has talked about many times on the forum. This detection won't show up on VirusTotal.
But new users are protected from this particular sample now via MD Cloud.
The sample is a cookie stealer based on what I saw it doing.
 
Last edited:

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top