LinkedIn Is Illegally Searching Your Computer

News Archive
21 Replies 2,228 Views
Status
Not open for further replies.

[correlate]

Level 18
Verified
Top Poster
Well-known
Forum Veteran
Content source
https://browsergate.eu/

Microsoft is running one of the largest corporate espionage operations in modern history.​

Every time any of LinkedIn’s one billion users visits linkedin.com, hidden code searches their computer for installed software, collects the results, and transmits them to LinkedIn’s servers and to third-party companies including an American-Israeli cybersecurity firm.

The user is never asked. Never told. LinkedIn’s privacy policy does not mention it.

Because LinkedIn knows each user’s real name, employer, and job title, it is not searching anonymous visitors. It is searching identified people at identified companies. Millions of companies. Every day. All over the world.
 
Last edited by a moderator:
Although I am not a LinkedIn user, the firewall detail that has been mentioned is technically very interesting.

Normally, a website does not require local network rules unless it is attempting to establish a direct connection—such as using WebRTC for video calls—or trying to 'communicate' with local ports (localhost) to detect third-party software or automation tools.

Viewed objectively, it seems that the firewall alert is not an attempt to intrude upon the hard drive, but rather the result of a network interaction that is unusual for a social media platform. It is a good reminder that, sometimes, the security measures used by platforms can clash with our own system's security settings. 🔍🛡️🌐
 
When I was talking in a topic regarding Edge how it's literal spyware and that it shouldn't be used, some members of the forum reassured me I have nothing to worry about and that my data is safe with Microsoft.

Do we still think that's the case? Everyone saying "Google spies", but the fact is Microsoft and their products are literal spyware. Google at least allows you to stop data collection entirely, Microsoft doesn't allow you to do that. So I'd take Google "spying" every single day of the week. And Google products are functional, unlike Microsoft's that are filled with bugs.

Back when Windows 10 was released and there was a controversy regarding telemetry, Barnacules Nerdgasm (ex-Microsoft employee) stated multiple times that Microsoft collects different data from each of their products and then cross-connects it to build a thorough profile on you.
Beside, if anyone ever tried to read Microsoft's privacy policy, you could see that it has one general privacy policy for all of their products and services. Inside you couldn't find the exact data they are collecting just general "personal data".
 
When I was talking in a topic regarding Edge how it's literal spyware and that it shouldn't be used, some members of the forum reassured me I have nothing to worry about and that my data is safe with Microsoft.

Do we still think that's the case? Everyone saying "Google spies", but the fact is Microsoft and their products are literal spyware. Google at least allows you to stop data collection entirely, Microsoft doesn't allow you to do that. So I'd take Google "spying" every single day of the week. And at least Google products are functional, unlike Microsoft's that are filled with bugs.

Back when Windows 10 was released and there was a controversy regarding telemetry, Barnacules Nerdgasm (ex-Microsoft employee) stated multiple times that Microsoft collects different data from each of their products and then cross-connects it to build a thorough profile on you.
All are spying to different levels; data is the new coin.
 
Regarding the different behavior between browsers mentioned above, it likely comes down to how each browser handles extensions and internal connections.

In Chrome/Edge, extensions use a fixed, public ID. It appears LinkedIn tries to detect them by launching thousands of simultaneous requests; this massive and 'unusual' traffic is likely what triggers the Windows Firewall, as it might flag such activity as suspicious.

In Firefox, each extension is assigned a unique, random UUID (Universally Unique Identifier) for every user. Since LinkedIn cannot guess these IDs, it fails to perform the scan, which would explain why the firewall remains silent in this case.

It seems that while Chrome/Edge leave a trail that can be exploited for tracking, Firefox's architecture naturally hides it, potentially avoiding those security alerts. 🔍🔒💻
 
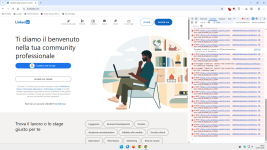
A recursive request appears that is completely blocked by uBo/AG (I haven't tried uBoL).
It doesn't happen with Firefox, but I can't say whether it's the same with the default Firefox settings.

I won't check any further since the privacy violation is blocked and I'm about to leave....;)

1.png
 
A recursive request appears that is completely blocked by uBo/AG (I haven't tried uBoL).
It doesn't happen with Firefox, but I can't say whether it's the same with the default Firefox settings.

I won't check any further since the privacy violation is blocked and I'm about to leave....;)

View attachment 296827
I get these blocked in Firefox as well, but the same script doesn't have to work equally in Chrome and Firefox. The site above mentions only Chrome is affected; probably because it's harder to do this in Firefox.
 
All are spying to different levels; data is the new coin.
I think you mean data is the new oil! But most of it's just advertising tracking 🚽:poop:

I actually find LinkedIn hilarious, started out like Facebook as a innocent social network platform but has become the biggest social engineering attack surface out there.

Everyone said and says 'create a LinkedIn' it's professional network for students and pro's, nah I'll be right.
 
Status
Not open for further replies.

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top