Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
- Content source
- https://youtu.be/zrpOzV-5ekM


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
That sounds good, I'll give it another try. The last time I used it, it was quite buggy and had performance issues.Thank you for performing this test and I wasn’t aware there is now emulation on demand. This has been added recently.

There is an update coming soon.That sounds good, I'll give it another try. The last time I used it, it was quite buggy and had performance issues.

What will it have. You wrote that like "Just wait and see". You've got me interested.There is an update coming soon.

In this case, the real-time protection and the file scan do not work after attack. But Zone Alarm cannot see it.
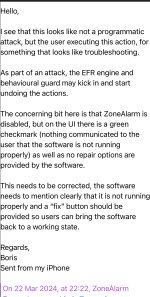
Yeah, I have escalated that with ZoneAlarm and will now escalate with Check Point as well, because Harmony Endpoint will be vulnerable too.Not only that, but ZA's settings interface gives no indication to the user that it's been crippled by malware.
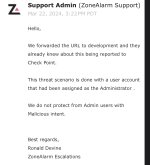
lol choose your admins wisely!The reply from ZoneAlarm is:
View attachment 282408

Speaking of that, it is what I proposed to Check Point as well.Additional context, such as policy compliance and device health
Speaking of that, it is what I proposed to Check Point as well.
Under “Compliance” a new rule to ensure software drivers are working correctly should be implemented. Upon computer startup, software should check drivers state.
If compliance is not met, it should be communicated to admins and they should be able to push a fix quickly.
That’s assuming that HEP, just like ZA, will be displaying green checkmarks when filter drivers are disabled.
ZoneAlarm or Check Point? Well they are the same company anyway. I’ve provided your email address to Check Point.It seems that Zone Alarm and Kaspersky staff are interested in taking a closer look at the attack method. So, I will send them the details.
I am not sure if that method will be covered, but I did my best.
ZoneAlarm or Check Point? Well they are the same company anyway. I’ve provided your email address to Check Point.
If the attack includes something they don’t monitor yet, they will need to update hooks and kernel drivers, most probably it will be fixed with the early March update. In Israel the working week starts from Sunday so they will probably review it today.Check Point asked about the details of the ZoneAlarm challenge.
Members who viewed this thread in the last 5 minutes