


A bond offer arrives with a familiar bank logo, a fixed interest rate, and a website presenting an Australian wealth management business.
The paperwork may look more convincing after a company search returns a matching name. Before treating those details as reassurance, check who actually stands behind the offer.
Overview
Macquarie has identified the bond approach as a scam
In its November 2026 warning, Macquarie identifies fraudsters pretending to represent CST CAPITAL PTY LTD and soliciting investments in fake fixed rate bonds.
The warning specifically includes Macquarie-branded bonds and lists six websites associated with the approach. This is an issuer warning about impersonation, not speculation based on website appearance.
The company name and the people contacting you are separate questions
An Australian Business Register entry exists for CST CAPITAL PTY LTD. Finding that record does not establish that the caller, website, or bond paperwork represents that company.
The warning concerns fraudsters falsely presenting themselves as the business. It should not become an accusation that every person connected to the registered company operates these websites.
The decision is to stop this investment process
Do not invest through the websites or contacts identified in Macquarie’s warning. Check any claimed Macquarie product through independently obtained bank contact details.
- Keep the original message and proposed investment documents together.
- Verify the issuer separately from the supposed intermediary.
- Contact your own bank immediately if money already moved.
- Preserve identity-document exposure details alongside the payment record.
The Websites and Phone Number in Macquarie’s Warning
Macquarie’s fixed rate bond scam alert names the following domains. Treat these identifiers as recognition details rather than places to visit or submit an application.
cstcapital-apply.comcstcapital-onlineaccount.comcstcapital-wm.comcstcapital-pty.comcst-clienthub.comcstcapitalglobal.com
The bank also lists +61 2 8424 7578 among contact details used by the scammers. Do not call that number to verify the offer.
A different spelling or newly supplied address does not establish safety. Compare the actual communication with the issuer’s warning and independently verify whoever is requesting money.
Macquarie asks people with suspicious Macquarie-branded correspondence to stop responding and forward it to scams@macquarie.com for review. Reach that instruction through the bank’s own website.
What the Public Website Adds to the Story
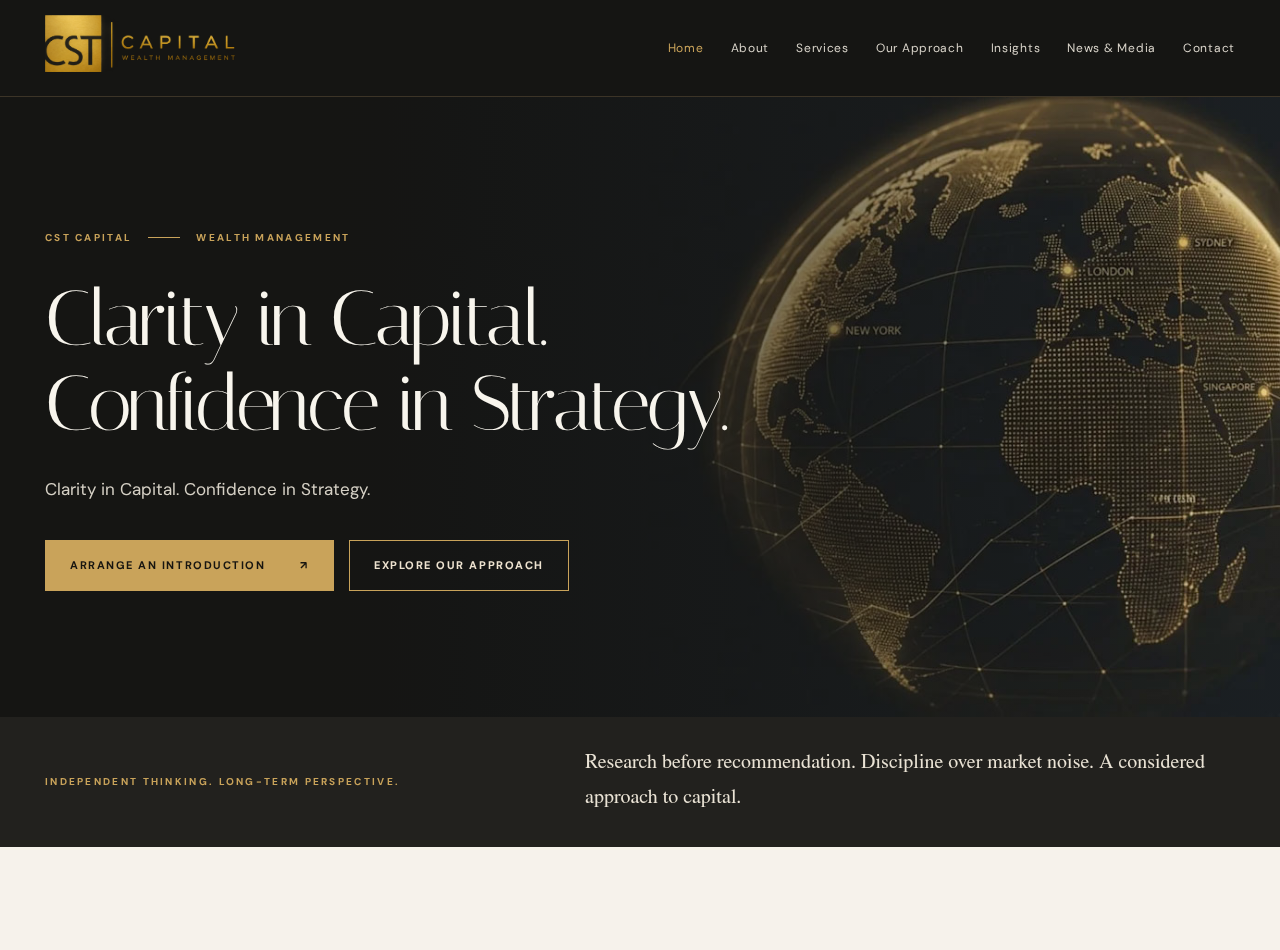
The cstcapitalglobal.com homepage presents CST Capital as a wealth management business. Gold branding, a global map, and financial language create an established professional impression.
Its services page presents capital strategy as considered, research-based work. That broad positioning can make an unexpected investment approach feel like a conversation with an adviser.
Neither presentation authenticates a particular Macquarie bond or the person sending an offer. The relevant connection is that Macquarie itself lists this exact domain.
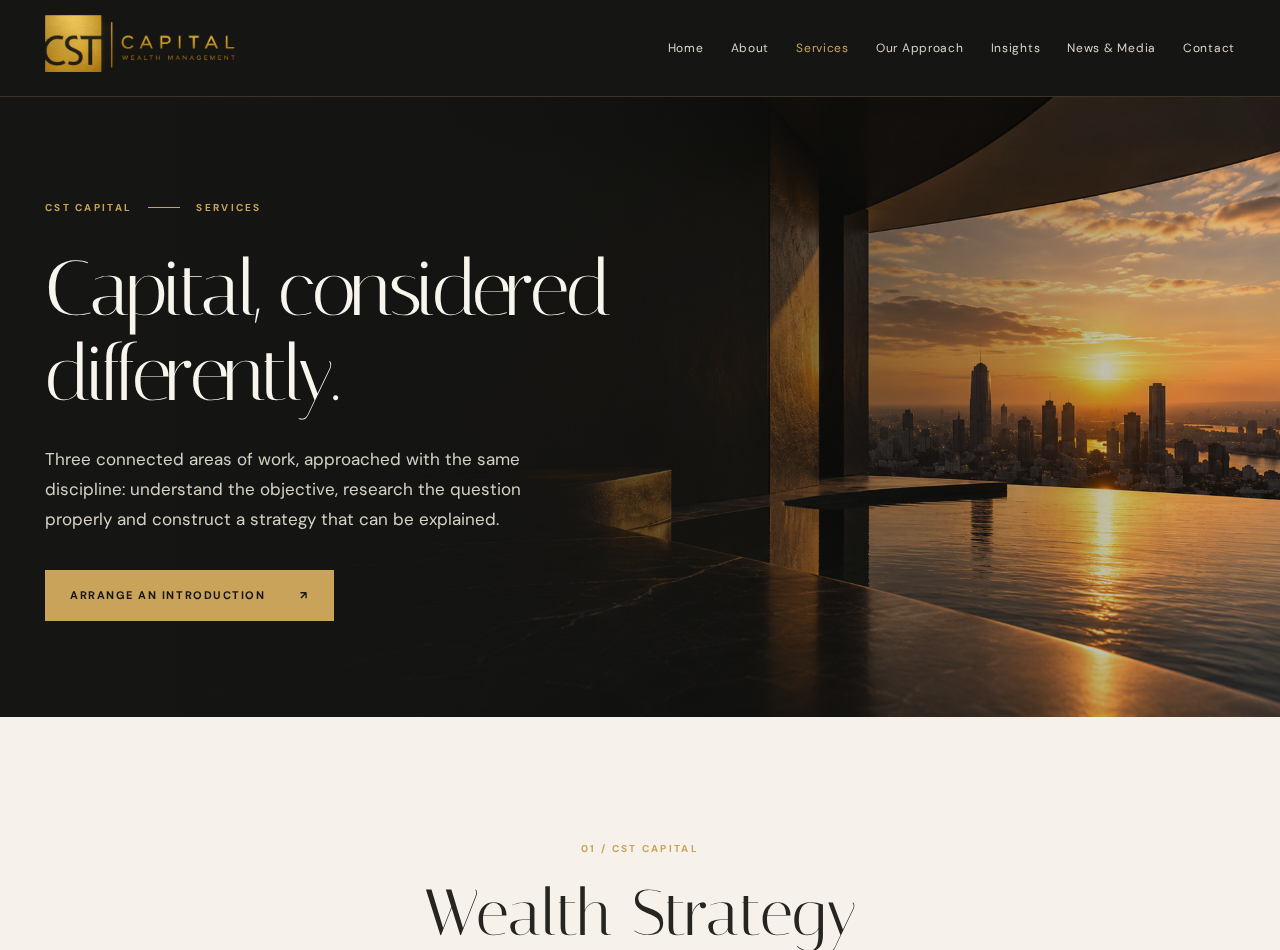
The services presentation does not show that somebody purchased or received a genuine security. An attractive introduction page and a valid investment transaction require different evidence.
Macquarie’s published examples include an earlier website presentation and a separate client sign-in screen. The public site shown here has different formatting from that earlier example.
Do not rely on a remembered layout to recognize the approach. The domain, claimed company, proposed issuer, and payment request matter more than unchanged colors or wording.
How the CST Capital Clone Bond Scam Works
Step 1: A recognizable financial identity opens the conversation
The approach claims a connection to CST CAPITAL PTY LTD while promoting fixed rate investments. A recognizable bank name supplies another layer of familiarity.
That combination offers two apparent ways to reassure yourself: look up the company and recognize the issuer. Neither check establishes that the people contacting you are authorized.
Keep the identities separate from the beginning. Ask who is selling the investment, who supposedly issues it, and which independently verified organization confirms the offer.
Step 2: Financial paperwork makes the proposal feel specific
A term sheet published within Macquarie’s warning advertises an 8.375% fixed coupon and a May 1, 2028 maturity, alongside a May 1, 2018 first issue date.
It includes a claimed issuer, currency, security identifier, and registration-related details. Those fields make the document resemble ordinary investment paperwork without establishing that the offer is authentic.
The decisive problem is Macquarie’s identification of the fraudulent approach. You do not need to prove that every printed number is invented before refusing it.
Step 3: A website and portal suggest an ongoing client relationship
The bank’s example of cst-clienthub.com asks for an email address and describes sending a one-time link and code for client sign-in.
A client portal can make a proposed investment feel administratively established. Its presence still does not confirm that a bank issued a bond or received your money.
Do not enter information merely to see whether a portal works. A login invitation is another part of the approach that needs independent verification.
Step 4: Registration details provide an answer to doubts
The bank’s earlier website example displays company and licensing identifiers. Someone checking only whether a company exists could mistake that result for verification of the entire offer.
A registry match answers a narrow question about an entity. It does not connect an unsolicited email, a particular website, or payment instructions to that entity.
Take the next verification step outside the offer’s own contact channels. Otherwise, the person selling the investment also controls the explanation of why you should trust it.
Step 5: The investment instruction becomes the point of loss
The offer ultimately asks you to treat money as invested in a bank-branded bond. Before any transfer, the recipient and transaction need their own authentication.
A document promising future interest does not establish where a payment will go. Neither does a portal balance establish that the displayed holding corresponds to a real investment.
If money already moved, focus on the actual recipient and transfer records. Those details can help your bank respond more effectively than the investment’s advertised name alone.
The Company Record, Claimed Offices, and Financial Credentials
A registered company is not proof of website control
The official ABN Lookup record lists CST CAPITAL PTY LTD under ABN 94 628 583 700 and ACN 628 583 700.
It records an active ABN from February 10, 2024, and a main business location of VIC 3000. Those details concern the registered entity.
They do not prove that the entity controls the warned-about domains. ABN Lookup itself directs readers dealing with investment providers to check financial-services licensing separately.
The addresses remain claims made on the website
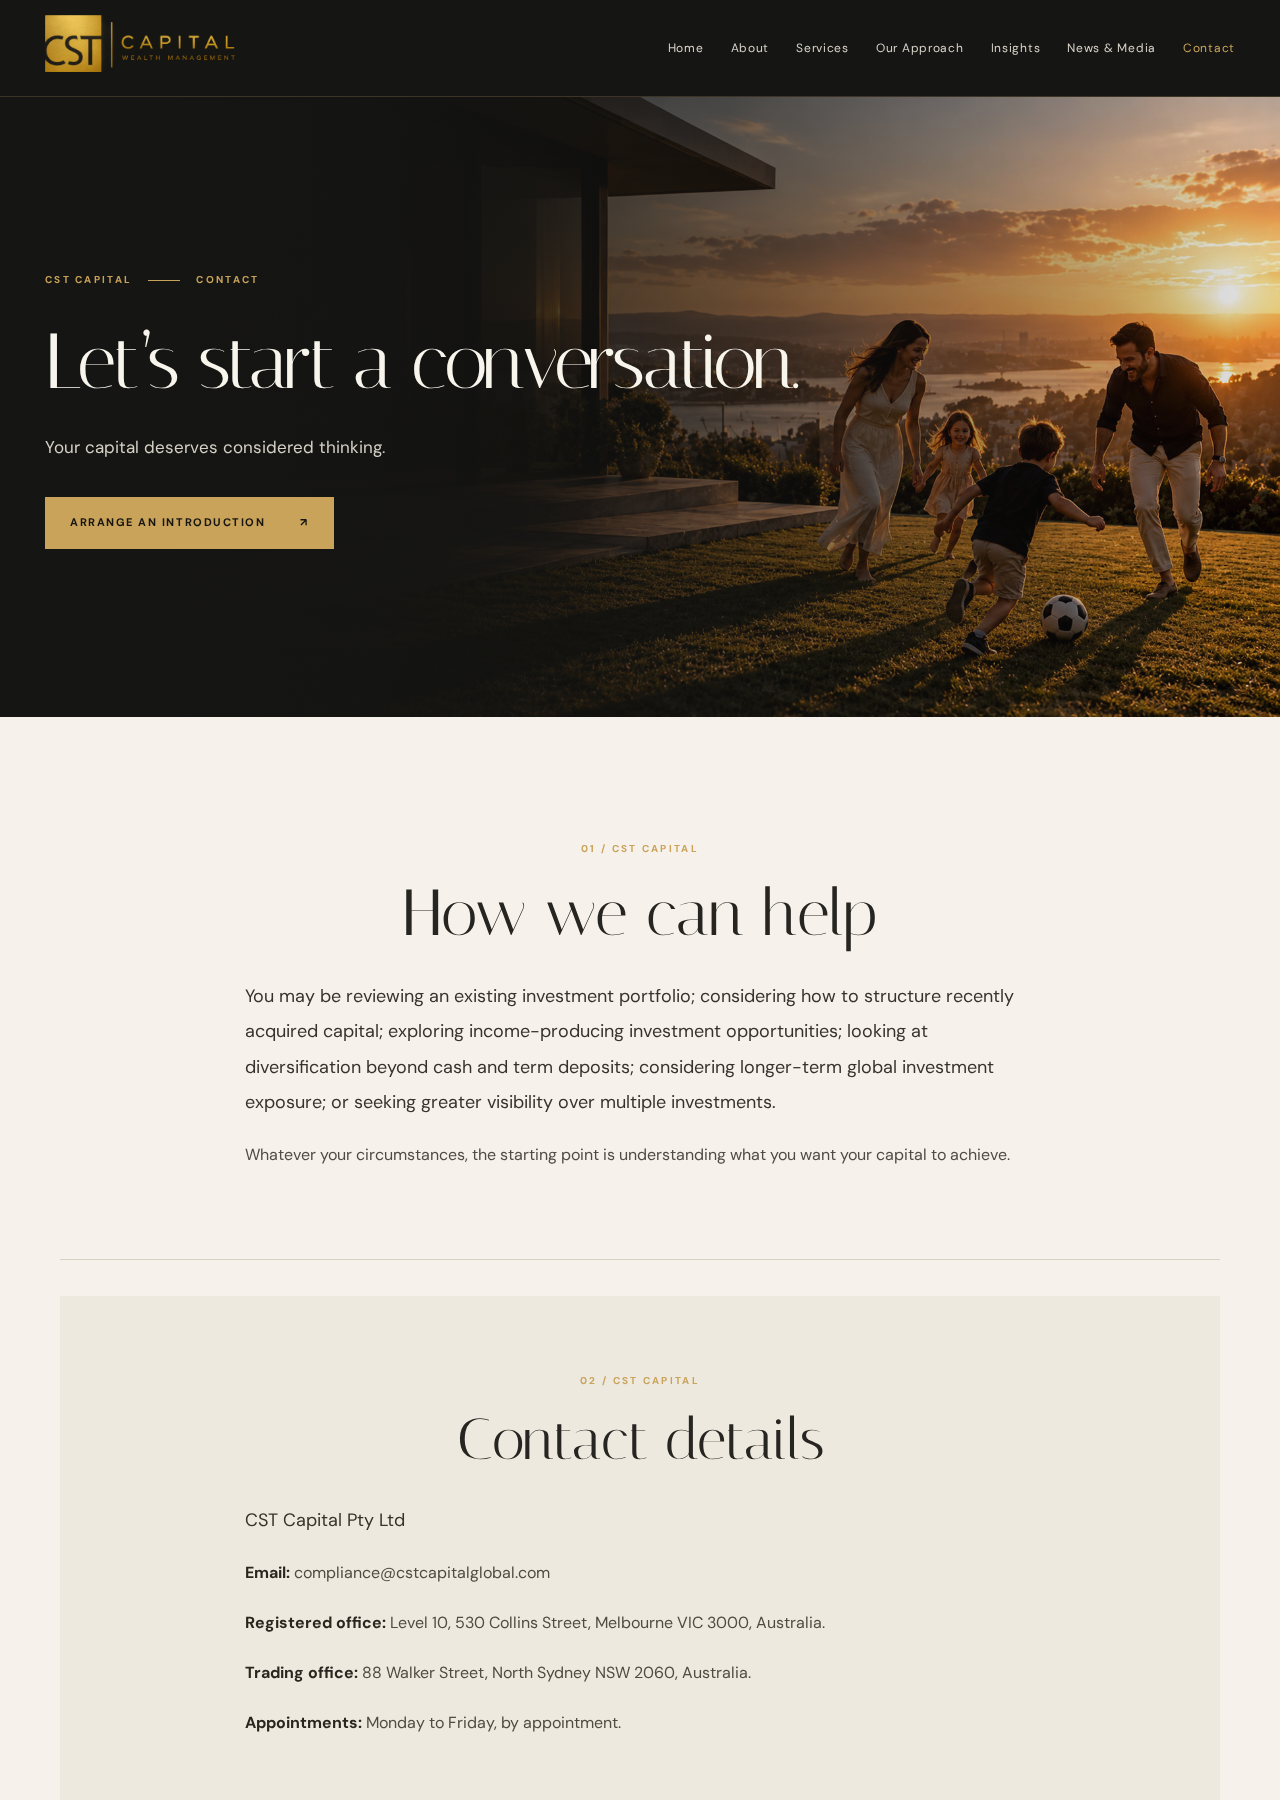
The contact page claims a registered office at Level 10, 530 Collins Street, Melbourne, and a trading office at 88 Walker Street, North Sydney.
It also displays an email address using cstcapitalglobal.com. These are contact claims from a website named in the warning, rather than independent verification routes.
A displayed street address does not demonstrate that the website operator occupies that office. Do not interpret it as proof that the bond or its salesperson is authorized.
The license holder and representative must be checked separately
The earlier website example prints AFS representative number 1277731 and AFS license number 314302. Another listed site previously claimed a relationship with L1 Capital.
L1 Capital’s own terms identify license 314302 with L1 Capital Pty Ltd. That separate company’s stated license does not authenticate these CST-branded websites.
The claimed representative relationship is not independently confirmed here. Check the exact entity, authorization, and contact details through ASIC and the independently located license holder.
The recipient of your payment needs a separate match
A familiar company name on a document does not identify the actual holder of the destination bank account. Read the payment instruction as a separate piece of evidence.
If an intermediary or payment provider is introduced, ask the purported issuer through an independent channel to confirm the arrangement. Do not accept the salesperson’s explanation alone.
For this warned-about offer, the practical decision remains to stop. Additional paperwork from the same contacts does not cancel Macquarie’s warning.
Why Detailed Bond Terms Can Be More Persuasive Than Hype
An investment pitch does not need unbelievable promises to be deceptive. A precise coupon, maturity date, and named institution can make it look restrained and routine.
ASIC’s Moneysmart bond-scam guidance explains that imposters can offer convincing, apparently low-risk investments. The advertised return may not appear obviously unrealistic.
The useful check is therefore not simply whether a rate sounds attractive. Confirm the product and seller through sources that the person requesting money does not control.
For example, receiving a second document with the same company number only repeats the same claim. It does not add an independent organization confirming the transaction.
Likewise, an email from a matching website domain proves little when the domain itself is part of the warning. Consistency inside the approach is not independent authentication.
What Independent Verification Should Establish
Moneysmart’s investment checks distinguish company registration from financial authorization and warn that scammers misuse genuine license details. A number printed online is the starting point, not the answer.
Verify the exact license holder and any representative against ASIC’s professional registers. Use independently found contact details to ask whether the person, domain, and specific offer are recognized.
When Macquarie’s name appears, reach Macquarie independently. Do not use a verification link or telephone number supplied by the person promoting the bond.
Keep a written record of what the independent organization confirms. A confirmation should address the actual offer and contact details, rather than merely acknowledging that a company exists.
This process is not an invitation to negotiate with the warned-about sites. It explains why the ordinary reassurance of a logo, company number, and document failed here.
What to Do if You Have Fallen Victim to This Scam
-
Stop further transfers and contact your bank. Explain that you may have paid an investment impersonation scam and ask whether a pending payment can be stopped.
Provide the amount, currency, date, recipient name, account details, and transaction reference. Identify each payment separately if several transfers were made.
Keep the currency exactly as shown on the transfer. An amount in A$ can differ from a converted total, so give your bank both records when available.
-
Keep the complete offer and communication trail. Save messages, email addresses, phone details, term sheets, website addresses, and receipts before removing or blocking contact.
Preserve original files privately, rather than relying only on cropped screenshots. Give the bank the instructions that actually accompanied the transfer.
-
Report the Macquarie impersonation through its official route. Use the bank’s own website to confirm its reporting address and forward suspicious correspondence as instructed.
Report the approach to Scamwatch through the route in Moneysmart’s scam-response guidance. Describe the exact website and payment request you encountered.
-
Address any identity information you supplied separately. Tell your financial institutions if you sent identity documents, account information, or other details that could support impersonation.
Use the exposure-specific guidance linked by Moneysmart, including IDCARE when appropriate. If a password was disclosed or reused, secure the affected legitimate accounts.
Tell the bank which documents were supplied and when. Sending a passport scan requires a different response from merely receiving an unsolicited brochure.
-
Discuss unresolved concerns through your bank’s complaint process. Ask for its written response and retain the case reference. Further complaint options depend on the circumstances.
Moneysmart explains the Australian internal complaint and AFCA pathway when you are unhappy with a financial institution’s response. That process does not guarantee reimbursement.
-
Reject requests for another payment to recover your money. A supposed tax, release fee, or replacement investment can expose you to another loss.
Continue through the bank or agency you contacted independently. A new caller knowing details of your original loss does not establish a genuine recovery service.
Frequently Asked Questions
Has Macquarie actually warned about the CST bond offer?
Yes, its November 2026 alert identifies fraudsters claiming to represent CST CAPITAL PTY LTD and offering fake fixed rate bonds, including Macquarie-branded investments.
Does the real company registration make the websites genuine?
No, a company record does not establish who controls a website or sent an offer. The impersonating contacts and the registered entity must be distinguished.
Are all six website addresses part of the bank’s warning?
Yes, the listed domains appear in Macquarie’s CST warning. Use them to recognize the approach, rather than visiting them to check whether an application works.
Does a security identifier prove that the investment is real?
No, financial details can be copied into misleading paperwork. Verify the actual offer, authorized seller, and payment destination independently instead of relying on one printed identifier.
Does a client portal prove that my money was invested?
No, a portal or displayed holding does not establish that the named bank received your money. Ask your bank about the actual transfer and preserve its records.
What should I do after sending money or identity documents?
Contact your financial institution immediately, stop further payments, and preserve the evidence. Address identity exposure separately and report through the bank’s official route and Scamwatch.
The Bottom Line
Do not invest through the CST Capital clone offer or the contacts named in Macquarie’s warning. The bank has identified the fixed rate bond approach as fraudulent.
A matching company record, polished website, or detailed term sheet does not override that warning. Verify any genuine Macquarie investment through independently obtained bank contact details.
If you already transferred money, contact your bank now and preserve the actual payment instructions. Do not wait for a promised interest payment before reporting the problem.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.