


A voicemail says there is a problem with the address on your FedEx package, and a website named in the message must be visited before a deadline of November 24.
We did not receive that call, but we checked the website behind a published sample and 21 look-alikes that share its fingerprints.
Overview
What the voicemail asks you to do
A published sample of the voicemail says there may be an issue with the delivery address and asks you to visit a named website before November 24.
It warns that the package will otherwise be returned to the sender.
The same write-up says callers may also claim to be a FedEx claims desk or driver, and may push victims toward remote-access software, ID photos or a small holding fee.
The sample names fedexyg.com, one of a family of domains that all follow the pattern FedEx plus two or three letters.
What we found when we looked at the domains
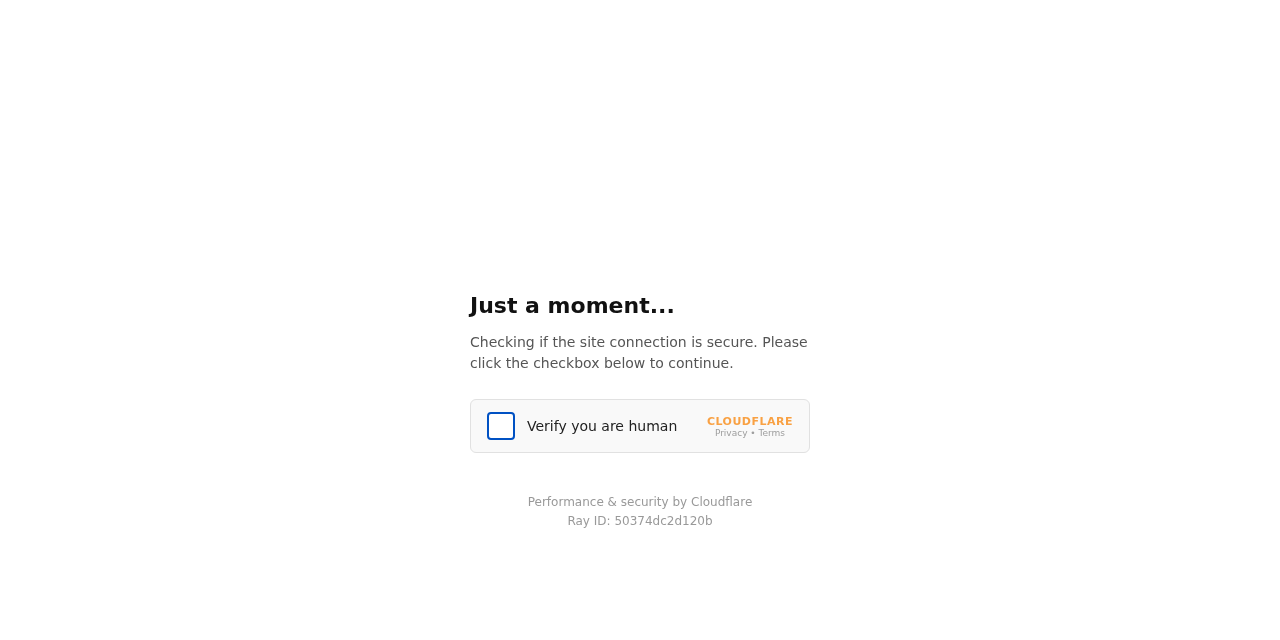
Ten of the 22 domains we checked currently resolve, and nine of those serve the same page: a fake Just a moment check with a Verify you are human checkbox.
The page borrows the Cloudflare name, but a uvicorn web server behind a Caddy proxy serves it, and its Ray ID is a random number made in your browser.
Clicking the checkbox sends a tracking beacon to the operator and, 200 milliseconds later, redirects the browser to a hidden address stored in the page code.
What we could and could not verify
We read the page code as text and did not click anything or follow the redirect, so we cannot say what the final page asks for.
- Verified by us: registration dates, registrars and name servers for 22 domains, the page behavior of 10 live domains and the hidden redirect targets.
- Reported by others: the voicemail wording, the November 24 deadline and the remote-access and holding-fee steps.
- Not verified: who operates the domains, what the final page shows and whether any victim lost money.
Our advice is simple: never use a website named in an unexpected delivery voicemail, and read the response section below if you already did.
The 22 Domains and Their Registration Pattern
We pulled the public registration record for each look-alike from the .com registry, and the pattern is much tighter than a coincidence of names.
Four older domains were registered between September 24 and October 1, 2026, at three different registrars: fedexql.com, fedexns.com, fedextm.com and fedexvq.com.
Three of those match earlier MalwareTips articles on FedExql, FedExNS and FedExvq, so the family has been active for weeks.
From October 5 onward, the registrar changes: 18 of the 22 domains sit at Dominet (HK) Limited, and 17 of those share ns7.alidns.com and ns8.alidns.com.
The batches are the telling part, because several domains were registered in the very same second:
- fedexra.com and fedexru.com, October 22 at 09:49:15 UTC.
- fedexts.com and fedexyr.com, October 27 at 09:33:59 UTC.
- fedexyc.com, fedexyg.com and fedexyj.com, November 4 at 01:18:56 UTC.
Registering three domains in one second points to a script or a bulk order, not to a person typing names one by one.
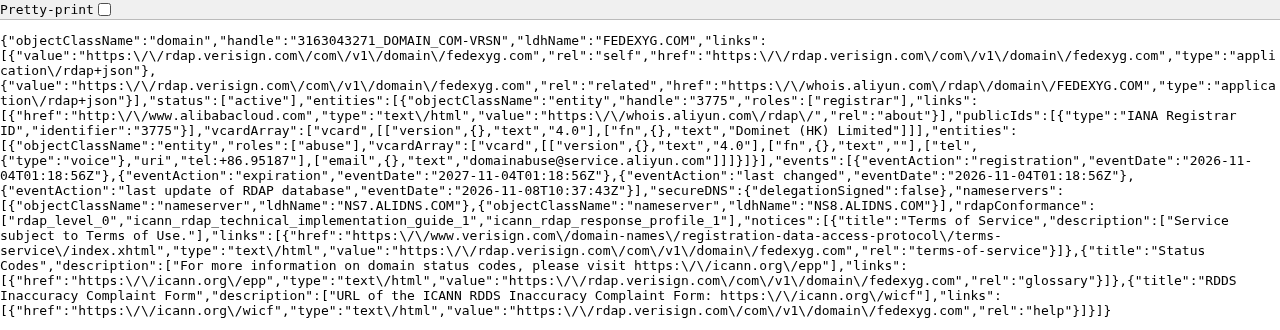
The registry record above is for fedexyg.com, the domain named in the voicemail sample, and it matches fedexyc.com and fedexyj.com to the second.
Eleven of the 22 domains now carry a client hold status, which suggests a registrar suspended them, while the other eleven remain active.
The newest, fedexlhp.com, was registered on November 7, 2026, a day before we looked, so the family is still growing.
How the FedEx Look-Alike Chain Works
Step 1: A voicemail names a domain and a deadline
The voicemail uses a delivery notification script, a vague address problem and a deadline, which matches our earlier FedEx voicemail article.
That article named fedexyd.com, a domain registered on October 5 that is now on hold.
A deadline works because it removes time to think, and a package problem works because nearly everyone is waiting for something.
Step 2: The domain looks like FedEx at a glance
Each domain starts with fedex, followed by two or three letters, which reads like a tracking or portal address on a phone screen.
FedEx’s own fraud page lists misspelled website addresses among the warning signs, and the real company’s pages live at fedex.com.
Step 3: A fake security check stands in the way
Instead of a FedEx page, the visitor sees Just a moment, Checking if the site connection is secure and a checkbox labeled Verify you are human.
The page script contains the text in nine languages, including Chinese, Japanese, Korean, Arabic and Russian, and picks one from your browser settings.
A real Cloudflare check is served from Cloudflare’s network, while these pages answer from a Python server behind Caddy.
The IP addresses we saw belong to address space registered to Aceville Pte. Ltd. in Singapore, which is a hosting provider, not Cloudflare.
Step 4: One click sends a signal and a redirect
The inline script reports the click to an address on the same domain, with a link ID and a target ID, and then redirects after 200 milliseconds.
The destination is stored as a base64 string, so a scanner that only reads the visible text sees a security check and nothing else.
Decoding the string shows four distinct targets on .top domains, and most are shared by several FedEx look-alikes.
- vicesdhsqqt.top receives fedexts.com, fedexyc.com and fedexyg.com.
- vicesdhsqqz.top receives fedexrz.com, fedexyr.com and fedexyj.com.
- qantemovixra.top receives fedexktm.com and fedexlhp.com.
- draxemulipqor.top receives fedextwm.com.
The targets were registered in pairs seconds apart, on November 4 at 00:43 UTC and November 6 at 23:44 UTC, with the same alidns name servers.
The first pair was registered about 35 minutes before the FedEx batch of that day, which fits a workflow of preparing the destination before the lure.
Step 5: The final page is hidden from us
We did not visit the .top addresses or click the checkbox, because following a scam redirect is not something a read-only check should do.
Published descriptions of the scam mention remote-access apps, ID uploads and a small holding fee, but we have not seen any of those pages.
One domain, fedextwq.com, redirected our request to an Apple page, a sign that these gates show different things to different visitors.
What the Page Code Does
The page loads nothing from outside, and its only script is inline, while a real Cloudflare check loads its code from Cloudflare’s own servers.
The script chooses one of nine languages by reading your browser’s language setting and falls back to English when none matches.
It then writes a random string of up to sixteen characters into the place where Cloudflare would show its Ray ID, so the number identifies no request at all.
On the click, it reports the event with the browser’s beacon call and falls back to a background POST request designed to survive a page change.
Next, it decodes the hidden address and replaces the current page in your history, so pressing Back does not return you to the gate.
The page contains no FedEx logo, no tracking number field and no parcel details, which means nothing on it relates to a shipment.
A Timeline of the Campaign
Putting the registry dates in order shows a campaign that started in late September and sped up in November:
- September 24: fedexql.com and fedexns.com are registered about an hour apart, at two different registrars.
- October 1: fedextm.com and fedexvq.com follow, at Gname and Realtime Register.
- October 5: fedexyd.com becomes the first domain at Dominet (HK) Limited, with different name servers.
- October 10 to 27: thirteen domains are registered at Dominet with the alidns name servers, including the same-second pairs.
- November 4: two .top targets are registered at 00:43 UTC, and three FedEx domains follow at 01:18 UTC.
- November 6 and 7: two more targets are registered, and fedexlhp.com appears the next afternoon.
The earliest scans in the public urlscan search for this address date from October 21, when fedexeq.com and fedexwv.com were checked within a minute of each other.
Twelve of the 13 scans returned the same Just a moment title and one ended on an Apple page, which is how a gate behaves when a scanner never clicks.
Why a Spoken Address Is Easy to Miss
A written link can be inspected before you click it, but a voicemail gives you a name to type, with no preview and no chance to hover.
Our earlier article noted that some phones turn a voicemail transcript into text, which can place the domain on your screen as if it were a normal notification.
Read aloud, fedexyg.com sounds like FedEx followed by a few letters, and a listener’s memory fills in the rest.
The gate then adds a second layer of false comfort, because a visitor who sees a security check may assume the site is protected, not impersonated.
Why the Fake Cloudflare Gate Matters
People have been taught to click through security checks without a second thought, and this page exploits that habit.
A genuine Cloudflare check appears on sites that sit behind Cloudflare, and these domains answered from other servers.
The gate also protects the operator: automated scanners and researchers see a harmless interstitial, while a human who clicks is passed on.
The tracking beacon reports a link ID and a target ID, which would let an operator compare which look-alike draws the most clicks.
Because the names are cheap and disposable, blocking one domain changes little, and eleven of the 22 are already on hold while newer ones appear.
What FedEx Says About These Scams
FedEx’s fraud page says the company does not request account credentials or identity information through unsolicited mail, email or text.
It lists misspelled website addresses, such as fedx.com or fed-ex.com, among the warning signs, along with urgent requests for money in return for delivery.
The page describes vishing as a message asking you to call a number to settle an account or fix an error, which is close to the voicemail pitch.
FedEx asks people to forward suspicious messages to abuse@fedex.com and to contact their bank immediately if they lost money.
It also points to the Internet Crime Complaint Center and state attorneys general, so those are the official places to report.
When we read the page, it did not describe fake security checks or domains made of fedex plus a few letters, so readers have no official guidance on this pattern.
Domains and Targets to Block
Defenders can use the list below, with the dots written in brackets so that nobody clicks by accident.
- Earlier batch: fedexql[.]com, fedexns[.]com, fedextm[.]com, fedexvq[.]com and fedexyd[.]com.
- Dominet batch, part one: fedexwt[.]com, fedexwv[.]com, fedexeq[.]com, fedexew[.]com, fedexkqt[.]com, fedexra[.]com, fedexru[.]com, fedexrz[.]com and fedextwq[.]com.
- Dominet batch, part two: fedexktm[.]com, fedexts[.]com, fedexyr[.]com, fedextwm[.]com, fedexyc[.]com, fedexyg[.]com, fedexyj[.]com and fedexlhp[.]com.
- Redirect targets: vicesdhsqqt[.]top, vicesdhsqqz[.]top, qantemovixra[.]top and draxemulipqor[.]top.
Three server addresses hosted the look-alikes, 43.166.214.47, 43.172.38.49 and 43.130.123.192, all inside space registered to Aceville Pte. Ltd. in Singapore.
New names will keep appearing, so a rule for fedex followed by two or three letters outside fedex.com will catch more than a fixed list.
What to Do If You Heard the Voicemail or Visited the Site
-
Do not call back or visit the site. Look up your shipment with a tracking number on fedex.com or the official app, as the FTC advises for unexpected delivery messages.
-
If you only listened, delete the message. FedEx says it does not request account credentials or identity information through unsolicited messages.
-
If you opened the site, close it and do not tick the box. Nothing we read proves harm from a visit, but the next page is unknown, so stop there.
-
If you entered a card or an ID, act at once. Call your card issuer to block the card, freeze your credit if an ID was shared and keep screenshots.
-
If you installed remote-access software, remove it. The FBI’s IC3 warns that scammers use such software to reach bank accounts, so uninstall it, change your passwords and call your bank.
-
Report it. Forward suspicious messages to abuse@fedex.com, file at ReportFraud.ftc.gov, and note the registrar abuse contact listed in the domain’s registry record.
Frequently Asked Questions
Is fedexyg.com a FedEx website?
No, FedEx’s own fraud guidance points to fedex.com, while fedexyg.com was registered on November 4, 2026 and shows a fake security check.
What is the fake Cloudflare check?
It is a page that copies Cloudflare’s look and wording, with a random Ray ID, to make a click-through feel routine before redirecting you.
Is it safe to visit one of these domains to look?
We read the code as text and did not click, so we cannot vouch for a visit, and we advise against going to the domains or the .top addresses.
What happens if I clicked the checkbox?
The page reports the click and redirects the browser to a hidden address we did not see, so enter nothing there and follow the steps above.
How can I check a real FedEx message?
Type the tracking number into fedex.com or the app yourself, and never use a link, number or website from the message.
Why do the domains keep changing?
The operator registers them in batches, eleven are already on hold, and new names appear, so blocking a single address does not stop the campaign.
The Bottom Line
Do not trust any website named in an unexpected FedEx voicemail: the fedexyg.com family hides behind a fake Cloudflare check and redirects clicks to hidden addresses.
We could not see the final page, so we cannot tell what it collects, but the registration pattern is consistent with a script-run operation rather than a delivery company.
If you already clicked or entered anything, protect your card and accounts first, then report the domain to FedEx, the FTC and the registrar.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.