


An email says there is a document to review and sign. The request feels ordinary, especially if your day is already full of contracts and forms.
The button promises a quick look at the file. What appears after that click is where this particular request becomes much less routine.
Overview
The document request
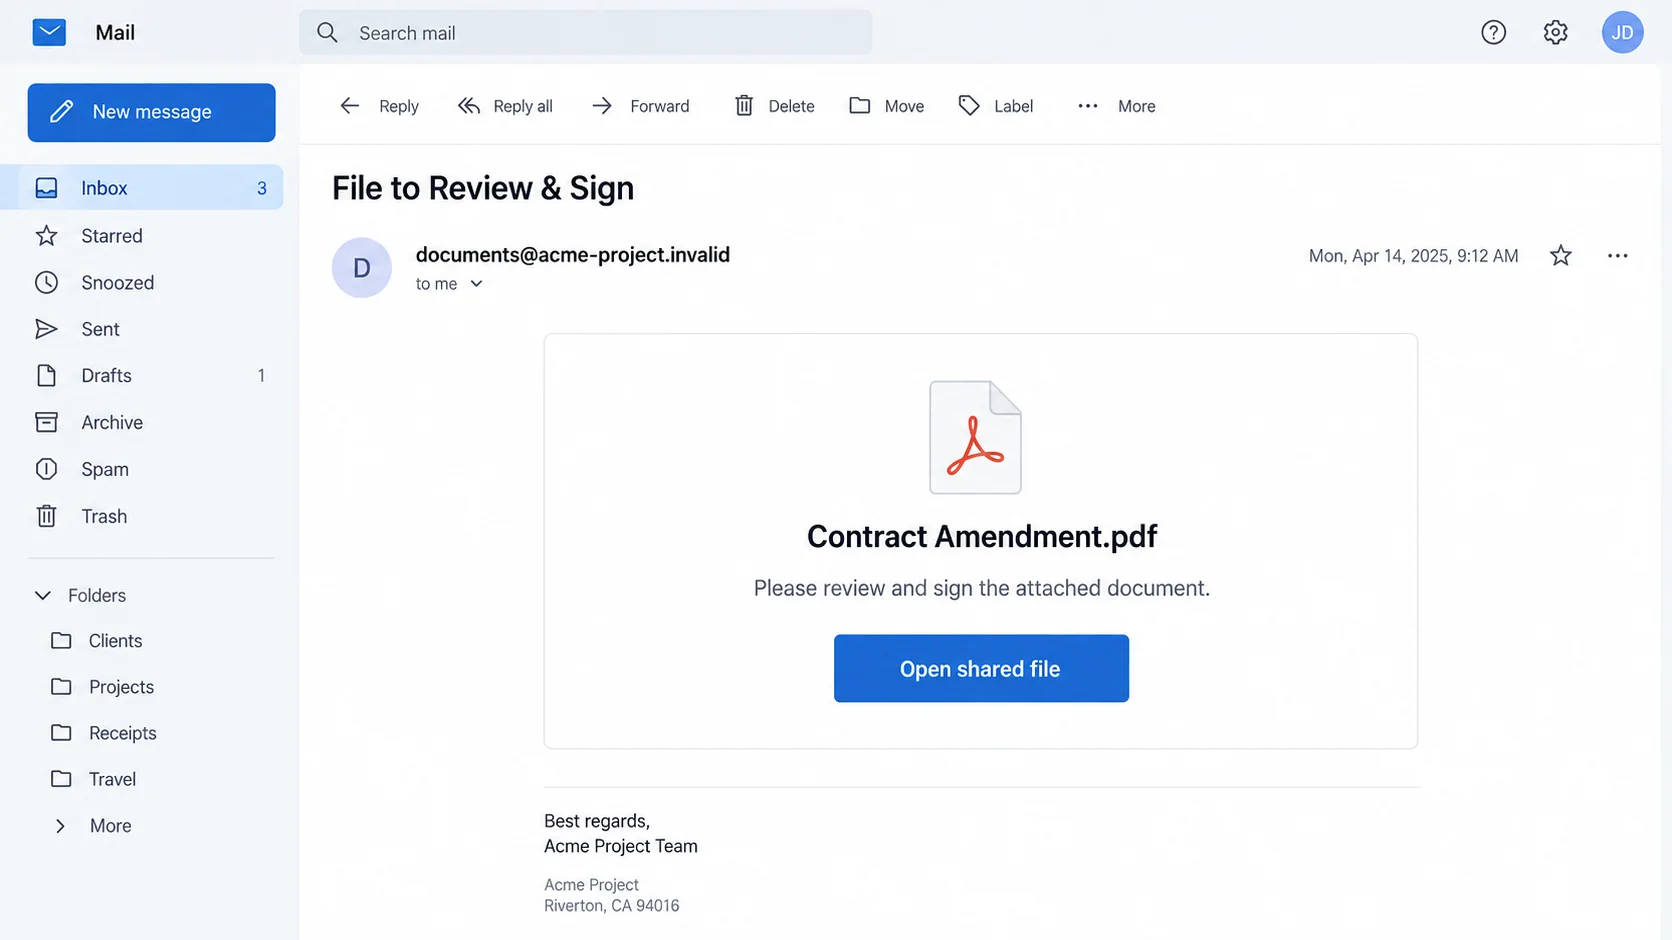
A reported email says a file is pending review and signature. It provides a “Review Document” action but little context about the agreement or sender.
After the click, the reader reportedly reaches a page styled as a shared-document portal. It lists files that sound legal or financial.
Attempting to open a file brings up an email confirmation prompt. The promise of a secure download makes the request seem procedural.
The image above is a fictional email illustration, not the original message. It shows the invitation that draws a reader toward an unverified file portal.
Where the information can go
The first requested detail is a valid email address. That can identify an active target and support a more tailored message later.
In some versions of document phishing, an address prompt leads to a password form styled after the recipient’s mail provider. That outcome is possible, not confirmed for every visitor.
Microsoft SharePoint is a legitimate service. Its name and visual language are being borrowed by the suspicious page, not evidence that Microsoft sent this email.
- The message creates an unexplained signing task.
- The click moves the reader to a document-sharing lookalike.
- A form asks for an email address before showing the files.
- Further credential requests should be treated as an immediate stop sign.
What readers should do
Do not use the emailed link to identify an unexpected contract. Ask the named sender through a separate channel and open known workspaces directly.
The reported website address is not needed to protect yourself and may change. This article does not direct readers to visit it.
The exact downstream behavior was not verified by submitting information. The documented redirection and unexpected form are enough to reject this invitation.
Why a Signing Request Can Feel Urgent Without Saying So
Some phishing messages shout about account closure. A document to sign can create its own deadline because business work often depends on signatures.
A supplier might be waiting, a manager might have sent paperwork, or a client might expect approval before the end of the day.
The email benefits from that background pressure. It does not have to know which agreement you are handling.
Its sparse wording can also help. The less it says, the more the reader fills in with a plausible project already on their mind.
An e-signature label suggests a normal, protected workflow. Plenty of legitimate platforms do send notifications, so the format is familiar.
That familiarity is why verification matters. The existence of real signing services does not authorize a link in an unsolicited message.
A confidential-information footer may reinforce the impression of a law or finance document. Such boilerplate can be copied without any legal relationship.
File names on the landing page play a similar role. “Agreement,” “statement,” and “review” are convincing labels but not proof of real contents.
A reader may hesitate to ignore the request because missing a genuine file could delay work. That is reasonable; the answer is independent confirmation.
You can verify the supposed document without feeding personal information into a page chosen by the sender.
Real SharePoint Sharing Versus a Lookalike Portal
SharePoint allows organizations to share files and folders with specific people or through controlled links. Notifications can be part of that normal workflow.
Microsoft’s sharing guidance describes how an owner chooses recipients and permissions. A notification should fit a document you can confirm with that owner.
The reported landing page was on an unrelated domain, despite its Microsoft-like presentation. A copied design does not move the page onto Microsoft’s infrastructure.
Check the browser’s full hostname before entering an email address or sign-in details. A lookalike may place trusted words before an unrelated domain.
Legitimate sharing settings vary. Some real links permit anonymous access, while others require a Microsoft account or an organization-issued identity.
That variation means no single prompt proves fraud. The suspicious combination is an unexpected email, unrelated site, vague files, and a form collecting details.
If your company uses SharePoint, open the file from its known tenant or ask the document owner to resend it through your normal workspace.
Do not try to resolve uncertainty by entering a work email “just to see what happens.” That can confirm the account for the operator.
Never enter a password or verification code into a page reached through an unverified signing email. Those credentials have value far beyond one document.
Microsoft itself lists fake hosted-document notices among common phishing examples in its Outlook phishing guidance.
How the File to Review and Sign Scam Works
Step 1: An unexplained document arrives as a task
The email claims a file is awaiting review and electronic signature. It may include a reference code that looks like a workflow ticket.
What it often lacks is a clear explanation of the agreement, the party requesting it, and why the recipient should be involved.
A broad campaign can still catch someone actively working on contracts. Timing can make a generic note feel personal.
Read the sender’s complete address and compare it with your project contacts before opening the request.
Step 2: The button redirects to a file-sharing facade
The button does not open an attached contract. It leads to a page that looks like a document portal.
That transition matters. The email supplies a task; the page supplies the visual “proof” that the task exists.
A list of files can make the environment feel populated, but labels and thumbnails are easy to fabricate.
The operator controls the page. No file should be considered authentic until its owner confirms it through a trusted service.
Step 3: A form asks for the visitor’s email address
When the reader tries to access a listed file, the page reportedly asks them to confirm an email address.
It says the address is needed for a secure download link. That explanation gives the request a privacy-friendly surface.
Submitting an address can tell the operator who reached the page. It may also allow a later email to use the exact address and document theme.
The fact that a form appears does not mean the service has verified an invitation. It means someone programmed a form.
Step 4: A later prompt can escalate to credentials
Document-phishing pages sometimes tailor the next screen to the address entered. A workplace domain may be followed by a matching login design.
That escalation was not tested by submitting an address in this case. Treat it as a possible continuation, not a guaranteed screen.
If a password or one-time code appears, close the page. Do not approve an unexpected authentication prompt on another device either.
A legitimate document owner can explain what was shared and how access should work without asking you to reveal your password.
Step 5: The collected details can support impersonation
A confirmed work address helps an attacker direct future messages to the right person or organization. Credentials create a much larger problem.
With mailbox access, they can read prior conversations and send a follow-up that seems to come from a colleague.
They can also search for invoices and reset links. Those are possibilities after account compromise, not outcomes proved by merely visiting the page.
That distinction determines the response: an address alone calls for vigilance; a password requires immediate account recovery.
How to Confirm a Document Without Using the Email Link
Look at the claimed sender. If it names a colleague, contact that person in your normal work chat or call them using an existing contact.
Ask for the document title and the project it belongs to. A genuine sender should be able to explain both without repeating the suspicious link.
If it names an outside firm, use a phone number from a prior contract or the firm’s independently verified website.
Do not reply to the suspicious message asking “Is this real?” A response may simply reach the same operator.
Open your organization’s known SharePoint or OneDrive portal from a bookmark. Look for the file there or ask the administrator to inspect sharing activity.
If the document is real but the email is fraudulent, the owner can send a new invitation through the usual service.
Pause before signing anything, even after confirming the portal. An authentic platform does not prove that a document’s terms are expected or correct.
Review the parties, requested signature, dates, and financial obligations. A real file can still be the wrong file.
For businesses, a shared reporting channel helps. One suspicious signing notice may have reached several employees with slight wording changes.
Forwarding the original as an attachment to your security team preserves headers. Do not forward it indiscriminately to coworkers as a warning.
Sender, Domain, and Sign-In Checks
The display name is not an identity check
“E-Sign,” “Contracts,” or “Accounts” can appear above any sender address. Expand the message details to see the domain.
Even a plausible address is only one clue. Attackers sometimes use compromised accounts or lookalike domains with one altered letter.
Check the underlying project and ask the supposed sender independently. Context is stronger than a logo.
A secure-looking page can still be unrelated
A browser lock icon tells you the connection is encrypted. It does not certify the site is Microsoft SharePoint or your company’s tenant.
Read the actual hostname. A name like “secure files” in the page heading is not part of the website’s identity.
If your organization has a managed portal, use it. Do not let a search result or email button choose a new login location for you.
Ask what information the document truly requires
A file owner might need your email address to share a document. They do not need your mailbox password, recovery code, or card number.
If a form asks for details beyond access, stop and ask the owner why. A legitimate person can clarify before you submit.
Do not use an address belonging to a colleague as an experiment. That can expose another person to follow-up phishing.
What to Do if You Have Fallen Victim to This Scam
If you only saw the email, report it. Use your mail provider’s phishing control or your employer’s established security channel.
Do not open the document button to prove it is suspicious. The administrator can inspect it safely.
If you visited the portal without typing, leave it. Inspect recent downloads and any permission the site requested from your browser.
A visit alone does not establish account takeover. Malwarebytes can help if a file downloaded or you ran software; AdGuard can reduce malicious ads.
If you entered only an email address, expect follow-up messages. Tell your security team which address you submitted and watch for tailored document requests.
Do not change a password solely because you typed an address, unless account activity or later steps justify it.
If you entered a password or code, secure the account immediately. Use the legitimate provider’s site from a clean device.
Change the password, end other sessions, enable multifactor authentication, and review recovery settings, forwarding rules, and connected apps.
If the account is used for work, notify IT promptly. They may need to inspect logins, revoke tokens, and warn contacts about messages sent from the account.
Preserve the suspicious email, page address, and approximate time. Those details help distinguish a false alarm from a wider incident.
If you signed or paid through the page, contact the right party. Tell the real document owner and your payment provider exactly what you submitted.
Keep a copy of the purported agreement and any receipt. Do not pay a “release” or “verification” fee to undo the event.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why a Real Microsoft Account Does Not Validate This Page
Some readers think a page must be genuine because it recognizes their Microsoft address. An attacker can know that address from the original email list.
A lookalike can also display a company logo after reading the domain you typed. That does not mean it can access your organization’s SharePoint tenant.
The safest test is independent navigation. Open the known Microsoft 365 app or your employer’s portal and look for the expected share.
If the document is absent, ask its owner. If the owner knows nothing about it, report the message without further interaction.
Do not rely on the page’s privacy policy or a “secure sharing” badge. The operator can write both.
Do not let fear of missing a deadline rush you into entering credentials. A legitimate business partner can resend an invitation.
If your team frequently signs documents, agree on a simple internal convention: who sends requests, which platform is used, and where to confirm them.
That habit removes much of the ambiguity this campaign needs to work.
Frequently Asked Questions
Is SharePoint itself a scam?
No. SharePoint is a legitimate Microsoft service. The concern is an unsolicited message and unrelated lookalike page using its familiar appearance.
Is giving only my email address dangerous?
It is less serious than giving a password, but it can confirm an active target for later phishing. Report the page and watch for follow-ups.
Does the shared-files list prove the documents are real?
No. File names and thumbnails can be placed on a page without any underlying contract. Confirm the share with the purported owner.
What if the sender is a colleague I know?
Contact them through your usual chat or phone. Their account may be impersonated or compromised, so do not verify by replying to the suspicious email.
Should I run a malware scan after clicking?
Check for downloads or executed files first. A simple page visit does not prove infection, while entered credentials require account recovery regardless of a scan.
What should I do after entering a Microsoft password?
Change it from the authentic Microsoft or company sign-in, revoke unknown sessions, review multifactor settings, and notify your administrator if it is a work account.
The Bottom Line
Do not enter details into a shared-files page reached through an unexpected “review and sign” email. Confirm the document with its owner and use your established workspace.
If you supplied a password, recover the account immediately and tell your administrator. A polished portal cannot substitute for a verified sender and destination.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.