


A nearly full mailbox sounds like a small problem with an easy fix. When work depends on email, even a routine storage warning can demand attention.
The message may contain familiar numbers and a helpful-looking button. Checking those details calmly can prevent a storage notice from becoming an account emergency.
Overview
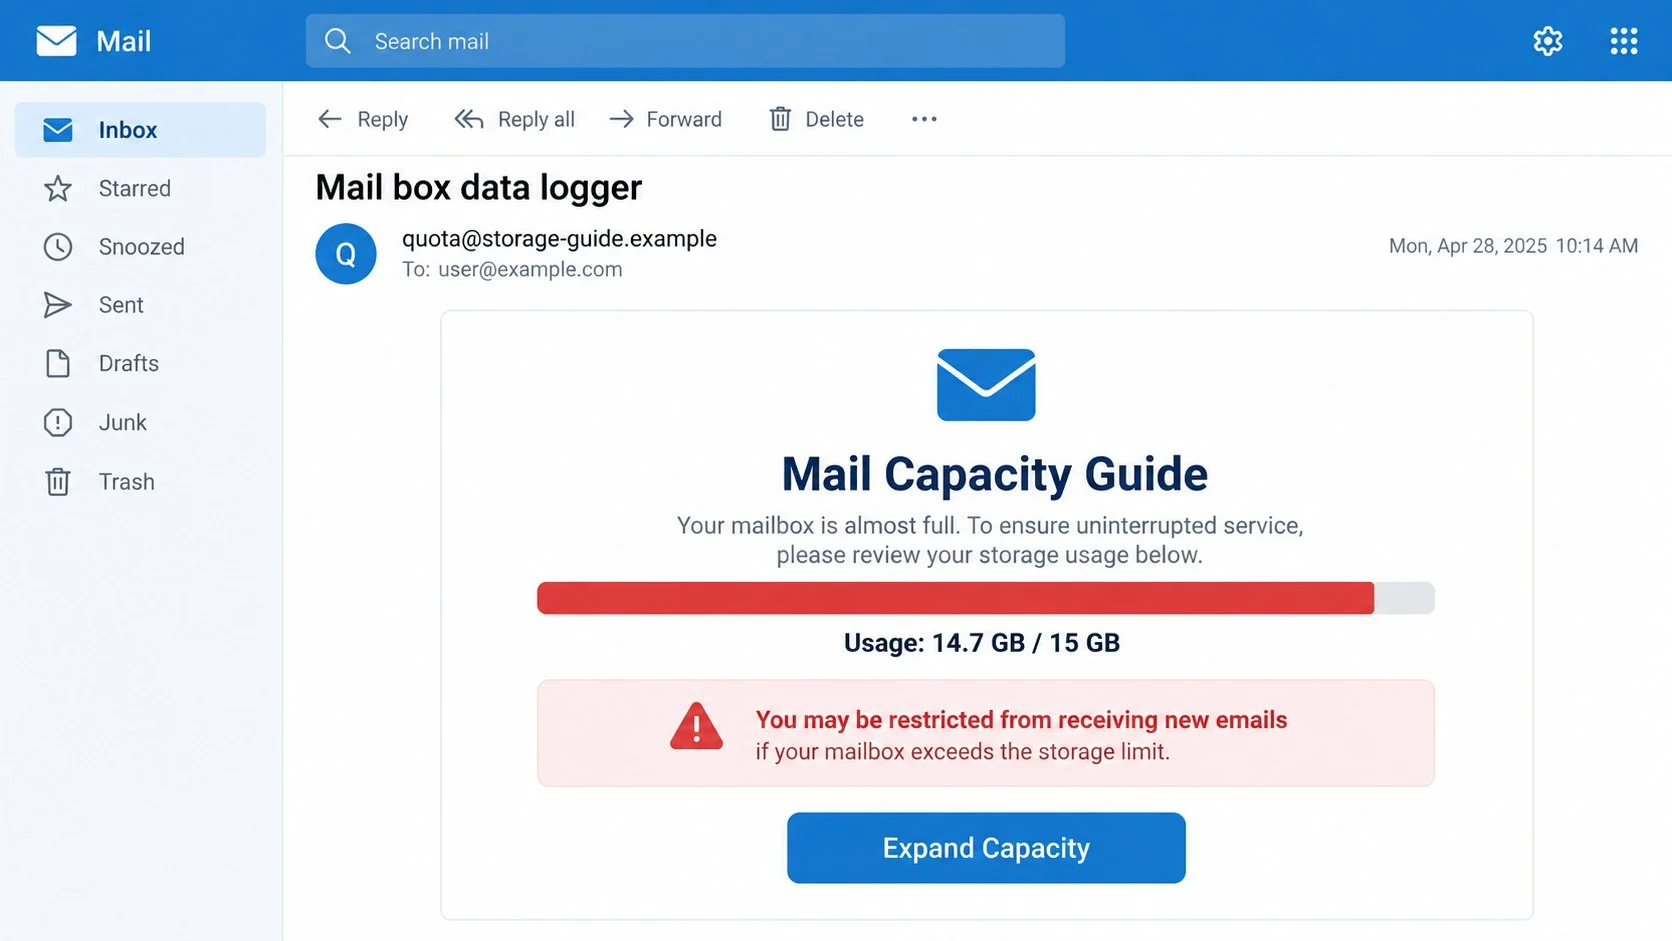
The warning claims only 0.3 GB remains
The message uses the subject “Mail box data logger” and presents a panel called “Mail Capacity Guide.” It says the mailbox is almost full.
A red meter reports 14.7 GB used from a 15 GB allowance, or 98% of the claimed capacity.
The recipient is warned that new messages may stop arriving. A button marked “Expanding capacity” or “Expand Capacity” promises a quick solution.
The numbers are invented for the email
The sender cannot determine mailbox usage merely by sending a message. The 14.7 GB figure is static content placed into the template.
Real storage information appears inside the signed-in account dashboard. It reflects the provider’s actual quota, folders, attachments, and subscription.
The mismatch becomes obvious when the recipient opens settings directly. Their account may have ample space or a completely different allowance.
The expansion button opens a password trap
The button leads through an unrelated or compromised website to a fake sign-in form. In observed versions, the route used a site with no connection to email hosting.
The form may resemble Gmail or another familiar provider. It asks for the recipient’s email address and password to complete the supposed upgrade.
Key warning signs include:
- A strange subject that does not match normal provider terminology.
- A precise 98% warning unsupported by the real account dashboard.
- Threats that incoming messages will be restricted immediately.
- A capacity button leading to a domain unrelated to the mail provider.
- A webpage requesting the existing mailbox password to add storage.
Why Mailbox Storage Warnings Feel Urgent
Email is an operational lifeline. Missing one customer request, password reset, delivery update, or appointment message can create genuine consequences.
The warning exploits that dependency without sounding dramatic. It frames the problem as ordinary maintenance that should take only a minute.
A nearly full progress bar is persuasive because people recognize it from phones, cloud drives, and real account settings.
The chosen numbers also feel measured. “14.7 GB of 15 GB” appears more credible than a vague statement that storage is low.
That apparent precision is not proof. A scam template can display any number, percentage, recipient address, or account label its operator chooses.
The phrase “new mail reception may be restricted” adds quiet pressure. Recipients may click before checking whether messages are actually bouncing.
Businesses face extra risk because shared mailboxes hold orders, support cases, and invoices. Staff want to protect workflow and may follow unfamiliar instructions quickly.
The safest response is wonderfully simple: ignore the email’s button and inspect storage through the provider’s official application or a saved bookmark.
How the Scam Works
Step 1: A generic quota warning reaches many inboxes
Attackers send the same storage template to addresses collected from breaches, mailing lists, public directories, and company contact pages.
The message does not need to know which provider hosts each mailbox. Generic blue styling and an envelope symbol can fit several services.
Some campaigns target corporate addresses because the domain itself reveals an organization with valuable correspondence and multiple potential victims.
Step 2: A fake usage meter manufactures a problem
The email displays a nearly complete red bar and claims 14.7 GB of 15 GB has been consumed.
These figures are embedded in the message. They are not obtained from the recipient’s account, computer, browser, or real storage service.
The design may still look personalized because the recipient’s address appears in the greeting. Mailing software can insert that value automatically.
Step 3: The threat of missed mail encourages haste
The notice says incoming messages may be placed on hold or blocked when the limit is reached.
That claim targets the fear of losing something important. A user awaiting a contract or security code may react especially quickly.
Real providers normally show storage alerts inside the account and explain which data consumes space. They do not hide every detail behind an unknown link.
Step 4: The button routes through unrelated infrastructure
Clicking the expansion button sends the browser to an address that does not belong to the recipient’s email provider.
The destination can be a compromised business website. Its legitimate owner may have no knowledge that a phishing page was planted there.
Attackers frequently move the form when hosting is suspended. The email design remains unchanged while the underlying addresses rotate.
Step 5: The landing page imitates a familiar login
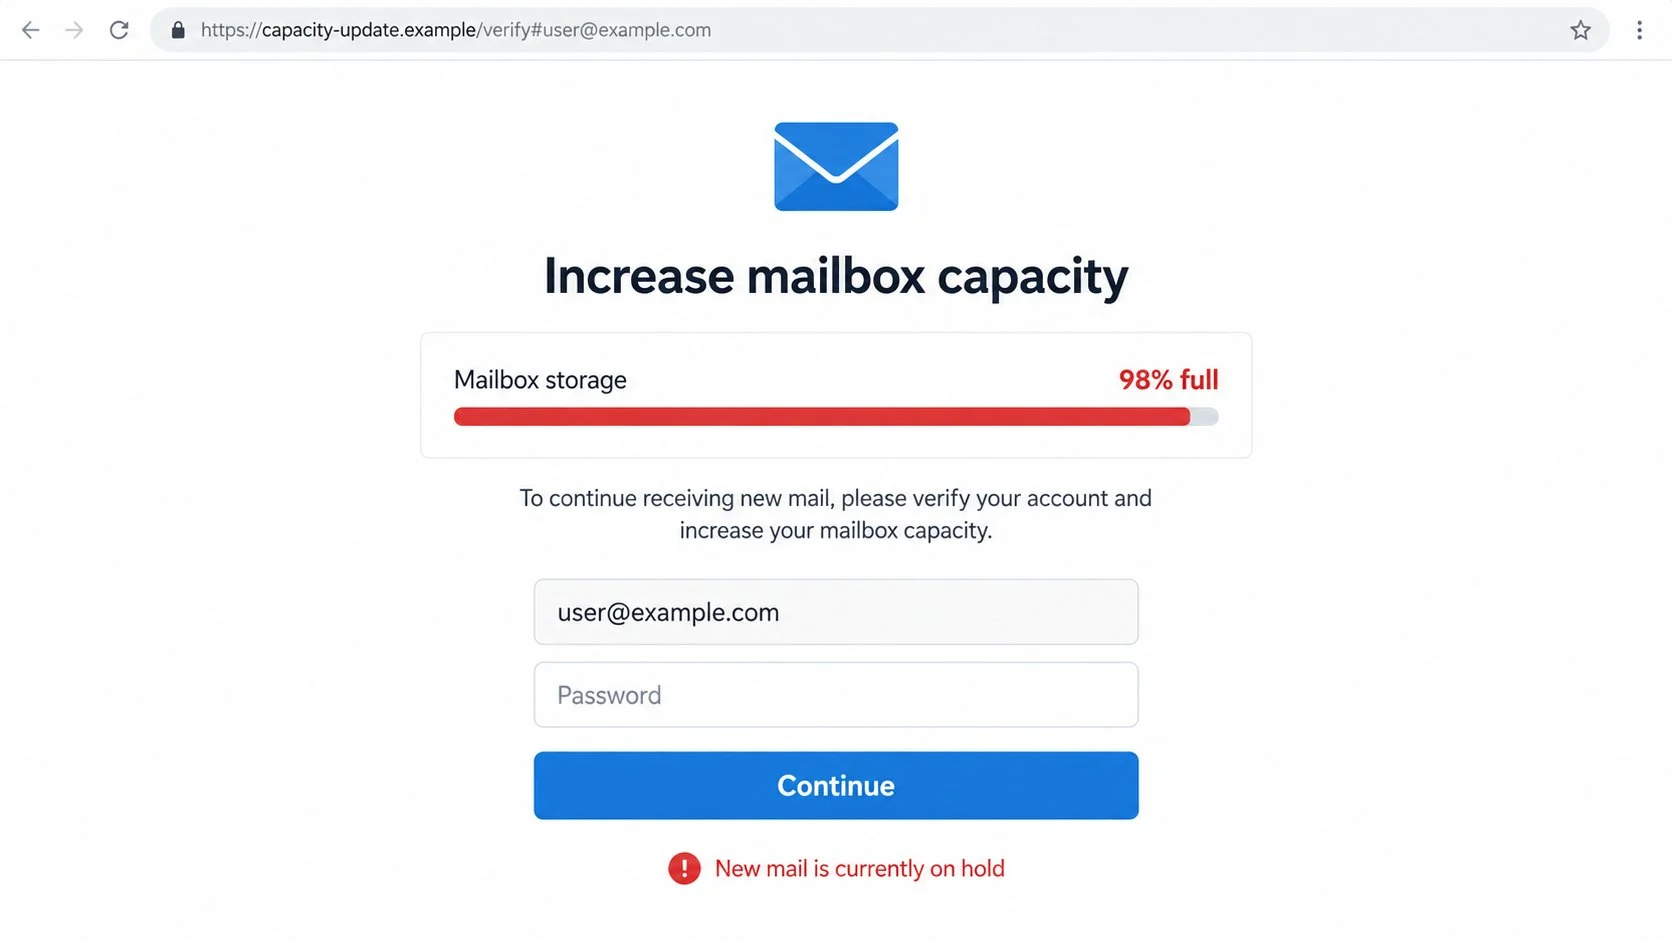
The page repeats the 98% figure and says verification is required before the mailbox can receive new messages.
A recognizable email layout lowers suspicion. Colors, logos, field labels, and spacing can be copied without any relationship to the real provider.
The address bar remains the decisive clue. Branding inside a page cannot transform an unrelated domain into an official service.
Step 6: A URL fragment may prefill the address
Some links place the target’s email address after a hash symbol. Browser code reads that fragment and inserts it into the username field.
Seeing a correct address can feel like account recognition. In reality, the scammer supplied the value inside the personalized link.
This trick reduces typing and makes the transition from email to webpage appear seamless. It does not authenticate the destination.
Step 7: The password is captured and tested
When the recipient presses Continue, the form transmits the entered credentials to the campaign operator.
The criminals may test them immediately. Automated tools can attempt a login before the victim realizes the storage warning was false.
A fake error sometimes asks for another attempt. That can collect corrected credentials or alternative passwords used on other services.
Step 8: The compromised mailbox becomes a new launch point
Successful access exposes contacts, attachments, password resets, billing records, and private conversations.
The attacker can create forwarding rules or send phishing from the real account. Messages from a familiar colleague carry much stronger credibility.
They may also search for banking instructions, payroll discussions, or active invoices. One stolen password can therefore lead to significant financial fraud.
What a Mailbox Intruder May Change
Many victims change the password and assume the incident is finished. That response is necessary, but it may leave hidden access behind.
A forwarding rule can copy incoming mail to an external address. Rules may use ordinary names and hide among legitimate filters.
Attackers sometimes create application passwords. Those codes can continue working independently after the primary password changes.
Recovery addresses and telephone numbers deserve attention. An unauthorized recovery method can help the criminal regain access later.
Connected applications may hold tokens that preserve sessions. Remove unfamiliar integrations and revoke access for services you no longer use.
Sent and deleted folders reveal whether the intruder contacted others. Search for quota warnings, invoices, payment changes, and password-reset messages.
Check the account’s recent sign-ins for unfamiliar locations, browsers, and timestamps. Remember that location estimates can be imprecise because of mobile networks or VPNs.
For workplace accounts, administrators can review deeper logs. Quick reporting helps them protect colleagues who received messages from the compromised address.
Real Storage Problems Behave Differently
Messages may bounce with a documented reason
When a quota is genuinely exhausted, senders can receive a delivery failure generated by the mail system. That notice contains technical identifiers.
The account owner may also see a persistent warning inside webmail. It remains visible after the suspicious email is deleted.
A single unsolicited message is therefore not the only evidence. Real capacity limits affect normal service and appear through authenticated controls.
The provider identifies what consumes space
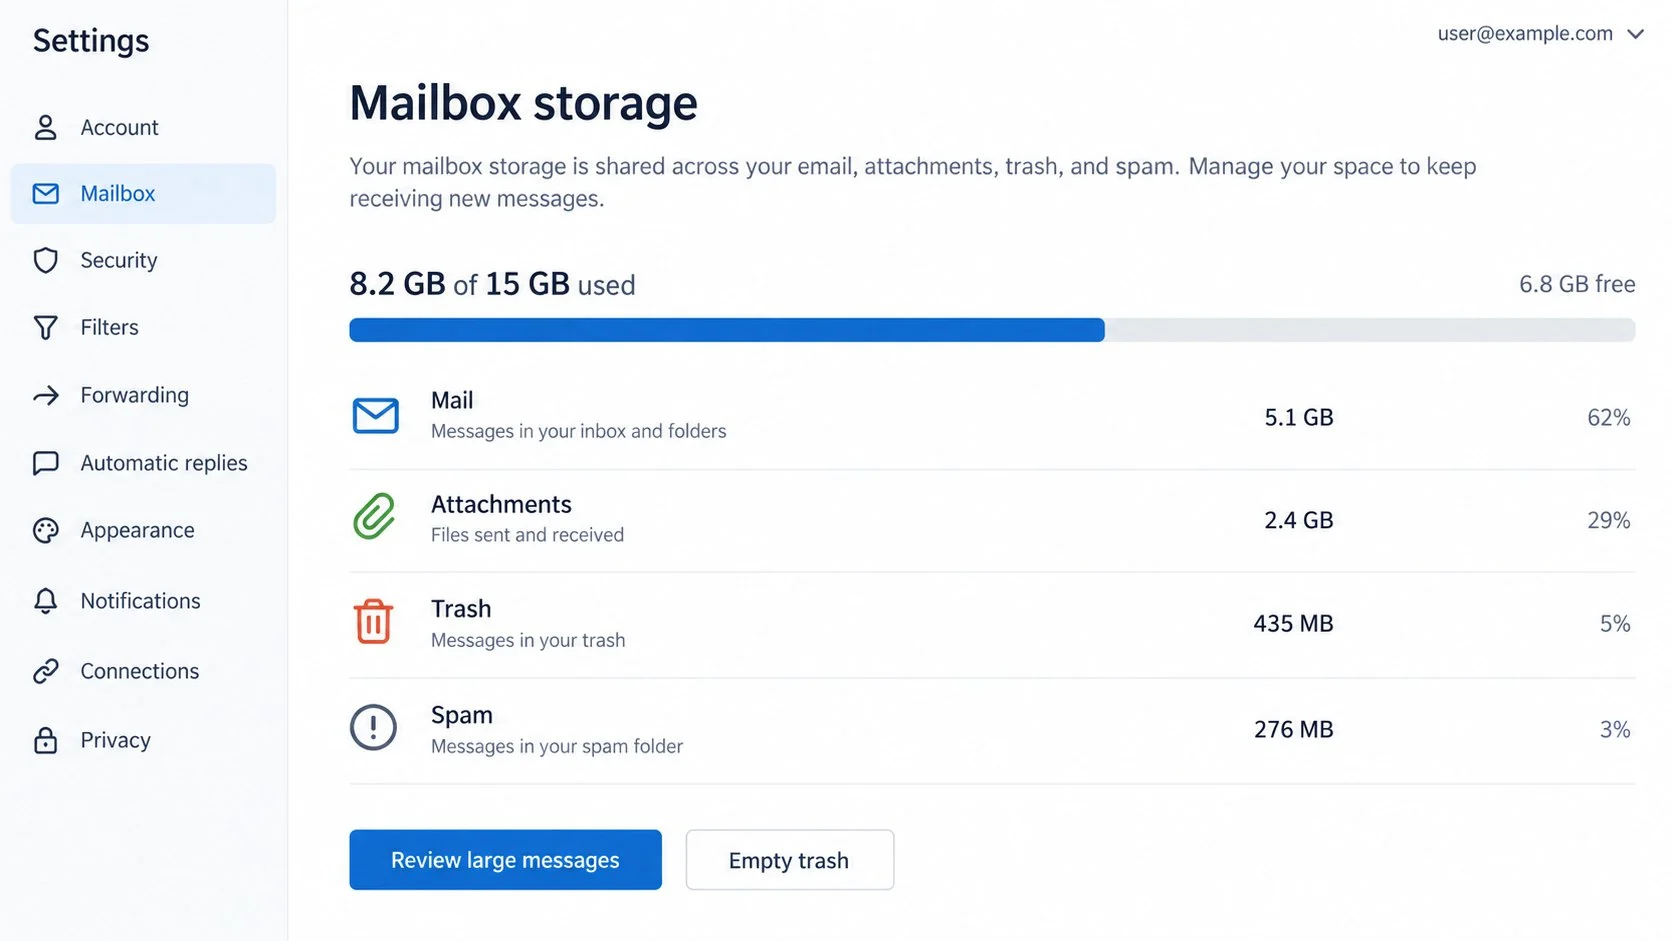
A genuine dashboard separates mail, attachments, cloud files, trash, or backups. Users can inspect large items and understand the reported total.
The phishing email offers no folder breakdown. Its red meter exists only to make an arbitrary number look measured.
Check whether deleted mail still counts toward storage. Emptying trash through official settings can sometimes resolve the issue without purchasing anything.
Upgrade options belong inside account billing
When additional capacity is available, the provider presents plan names, prices, renewal terms, and payment controls within the signed-in account.
The upgrade should not begin on a compromised third-party website. Billing pages should remain within domains clearly owned by the provider.
Workplace users may not control capacity at all. An administrator could manage quotas centrally, making a personal expansion button particularly suspicious.
Support can see the account without requesting its password
Legitimate support agents can examine plan and quota records through internal tools. They should never ask a customer to disclose the mailbox password.
If verification is needed, the provider may use a secure account prompt, support code, or established recovery process.
Contact support from the official help center. Do not reply to the quota message or use telephone details that it supplies.
Cleanup choices do not require an emailed link
Users can search for large attachments, remove duplicate files, empty spam, and export old messages directly through the mail service.
Organizations should follow retention rules before deleting business records. Administrators can expand archives or apply approved storage policies where necessary.
The important distinction is control. A real solution stays inside the known account, while the scam transports credentials to an unknown page.
Keep a screenshot of the genuine quota page when reporting the lure. It documents the contradiction without reopening the phishing destination.
Shared mailbox owners should coordinate cleanup so one employee does not delete records another department must retain.
How to Check a Mailbox Capacity Warning
Open the provider independently
Use the official application, type the known address yourself, or open a trusted bookmark. Do not use the warning’s expansion button.
Navigate to storage or account settings after signing in. The actual dashboard should show current usage and available management options.
Compare the quota and terminology
Check whether the account really has a 15 GB allowance and whether 14.7 GB is used. Many workplace plans use different limits.
Compare wording with earlier genuine notices. Awkward labels such as “Mail box data logger” can indicate an improvised template.
Examine the sender and destination
Expand the full sender address, then preview the button destination without opening it. Both should belong to the actual provider.
An unrelated national domain, compromised company site, shortened link, or random hostname has no authority to expand email storage.
Use safe storage controls
If the mailbox is genuinely full, delete large messages, empty trash, archive attachments, or purchase capacity inside the official billing area.
No legitimate storage upgrade requires entering your mailbox password into a page reached through an unsolicited warning.
What to Do If You Fell Victim to the Mail Capacity Guide Email Scam
- Change the email password immediately. Visit the provider through its official application or a manually entered address, not the suspicious page.
- Sign out every session. Revoke unfamiliar browsers, mobile devices, email clients, application passwords, and connected services.
- Enable strong multifactor authentication. A passkey, hardware key, or authenticator application offers better protection than password-only access.
- Check recovery settings. Remove telephone numbers and recovery addresses you do not recognize, then confirm your own information.
- Inspect rules and delegates. Delete unauthorized forwarding, filtering, automatic replies, shared access, and mailbox permissions.
- Review sent and deleted messages. Warn anyone who received a storage alert, invoice, or unusual request from your account.
- Reset reused passwords. Start with banking, shopping, cloud storage, social networks, and workplace systems using the same credential.
- Run a Malwarebytes scan. This campaign steals passwords through a form, but checking for unwanted software remains a sensible precaution.
- Install or configure AdGuard. Its filtering can reduce exposure to phishing redirects and malicious advertising, alongside careful account verification.
- Tell your workplace administrator. They can examine sign-in logs, revoke tokens, search for malicious rules, and protect other recipients.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the Mail Capacity Guide message legitimate?
No. The described campaign invents a storage problem and directs recipients to a fake login page intended to capture email credentials.
Is my mailbox really 98% full?
Only the official account dashboard can answer that. The 98% and 14.7 GB figures inside the email are prewritten bait.
Can a sender remotely measure my email storage?
No. An outside sender cannot obtain an accurate mailbox quota simply by emailing you. Providers calculate usage inside their own systems.
Why was my address already on the phishing page?
The scam link can carry your address as a parameter or fragment. The page reads it and fills the field automatically.
What if I clicked but entered nothing?
Close the page, remove any notification permission, and run a security scan. Your password is unlikely to be captured if never submitted.
Will deleting messages through the email’s link help?
No. Manage storage only inside the provider’s official settings. The phishing page cannot safely clean or expand your legitimate mailbox.
The Bottom Line
The Mail Capacity Guide email turns a believable maintenance issue into credential theft. Its exact-looking quota is simply part of the deception.
Check storage directly, distrust unrelated login domains, and secure the entire mailbox if a password was entered.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.