


A revised contract can arrive at exactly the moment a project feels close to completion. Redlined terms and a request for approval sound entirely routine.
This message uses that familiar final-stage pressure. Understanding the file sequence matters before anyone accepts the sender’s invitation to continue.
Overview
The sender poses as a purchasing and quality manager
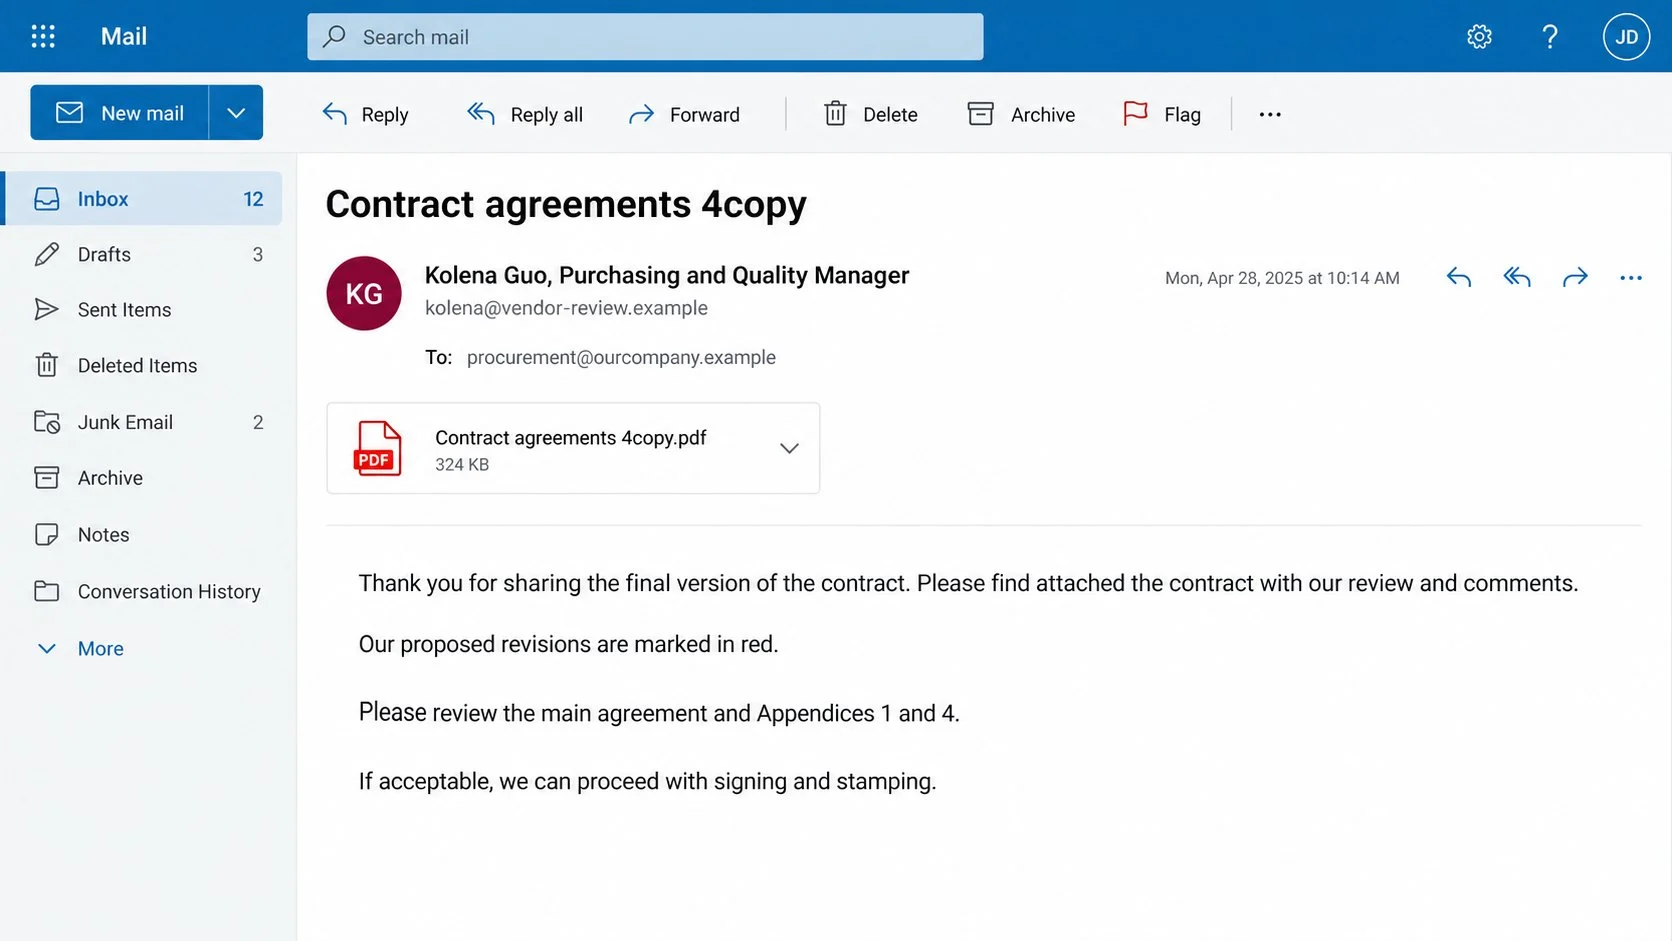
The email appears to come from “Kolena Guo” and describes the sender as a Purchasing and Quality Manager.
It thanks the recipient for sharing a final contract, then claims reviewed terms are attached. Proposed revisions are supposedly marked in red.
The message highlights the main agreement plus Appendices 1 and 4. If accepted, it says signing and stamping can proceed.
The first PDF manufactures a document problem
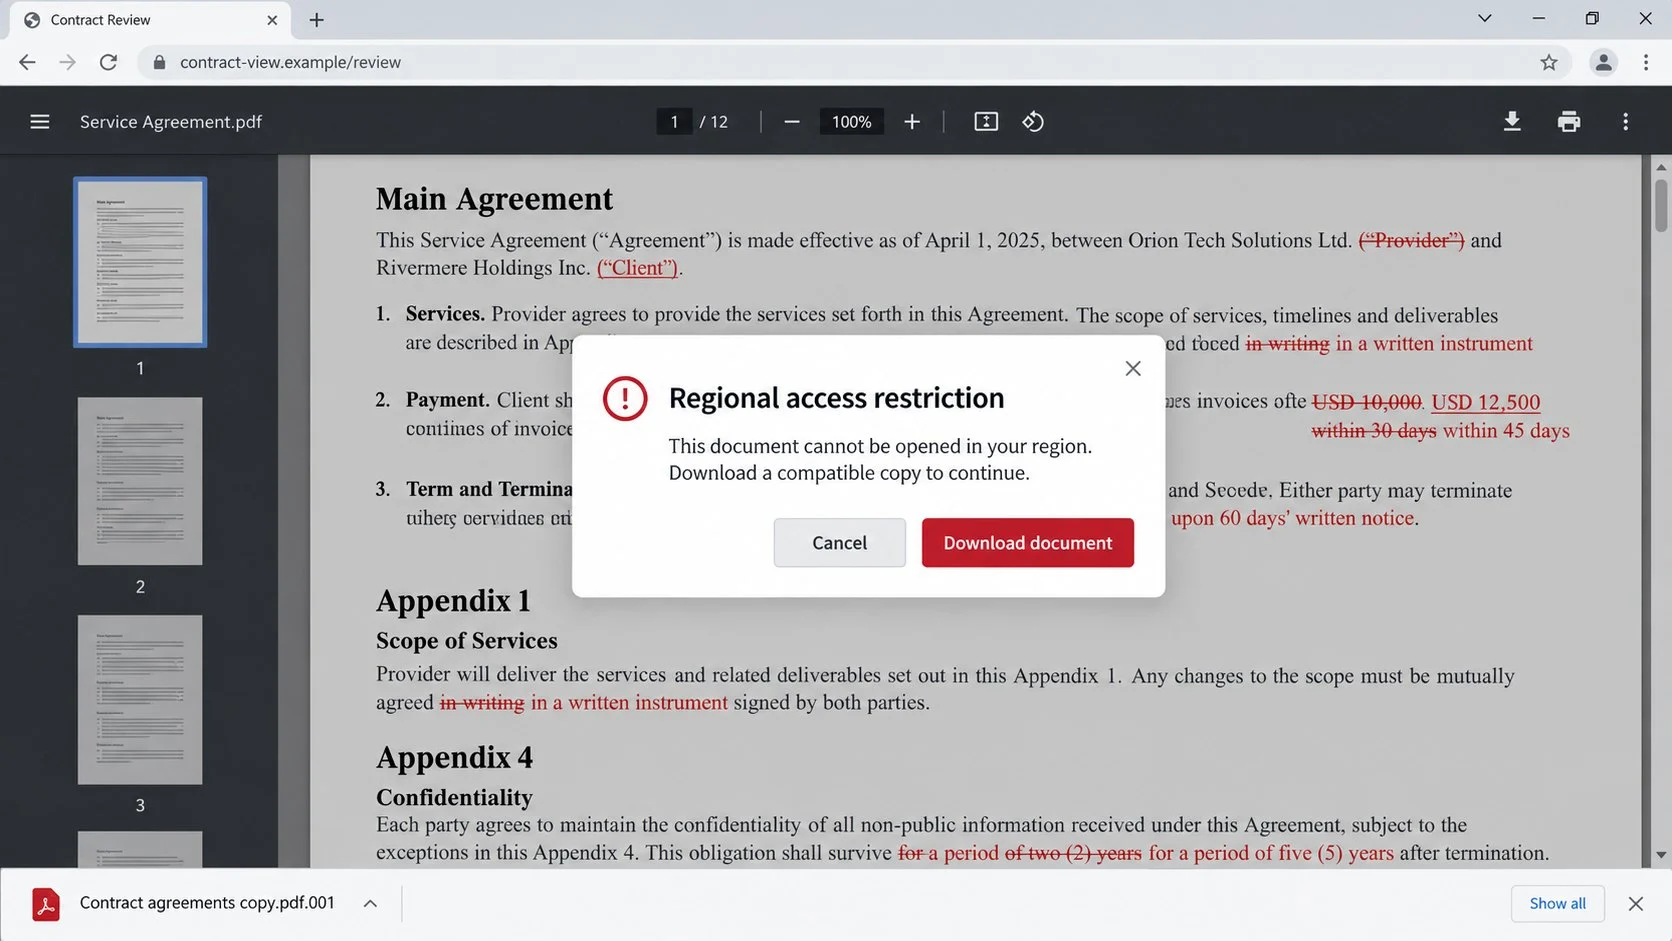
The attachment is named “Contract agreements 4copy.pdf.” Opening it displays contract-like pages and a regional-access error.
The pop-up says the file cannot open in the recipient’s region. A button offers to download a compatible copy.
A genuine contract does not need this strange handoff. The error exists to move the user into a second, riskier stage.
The download begins a multi-file malware chain
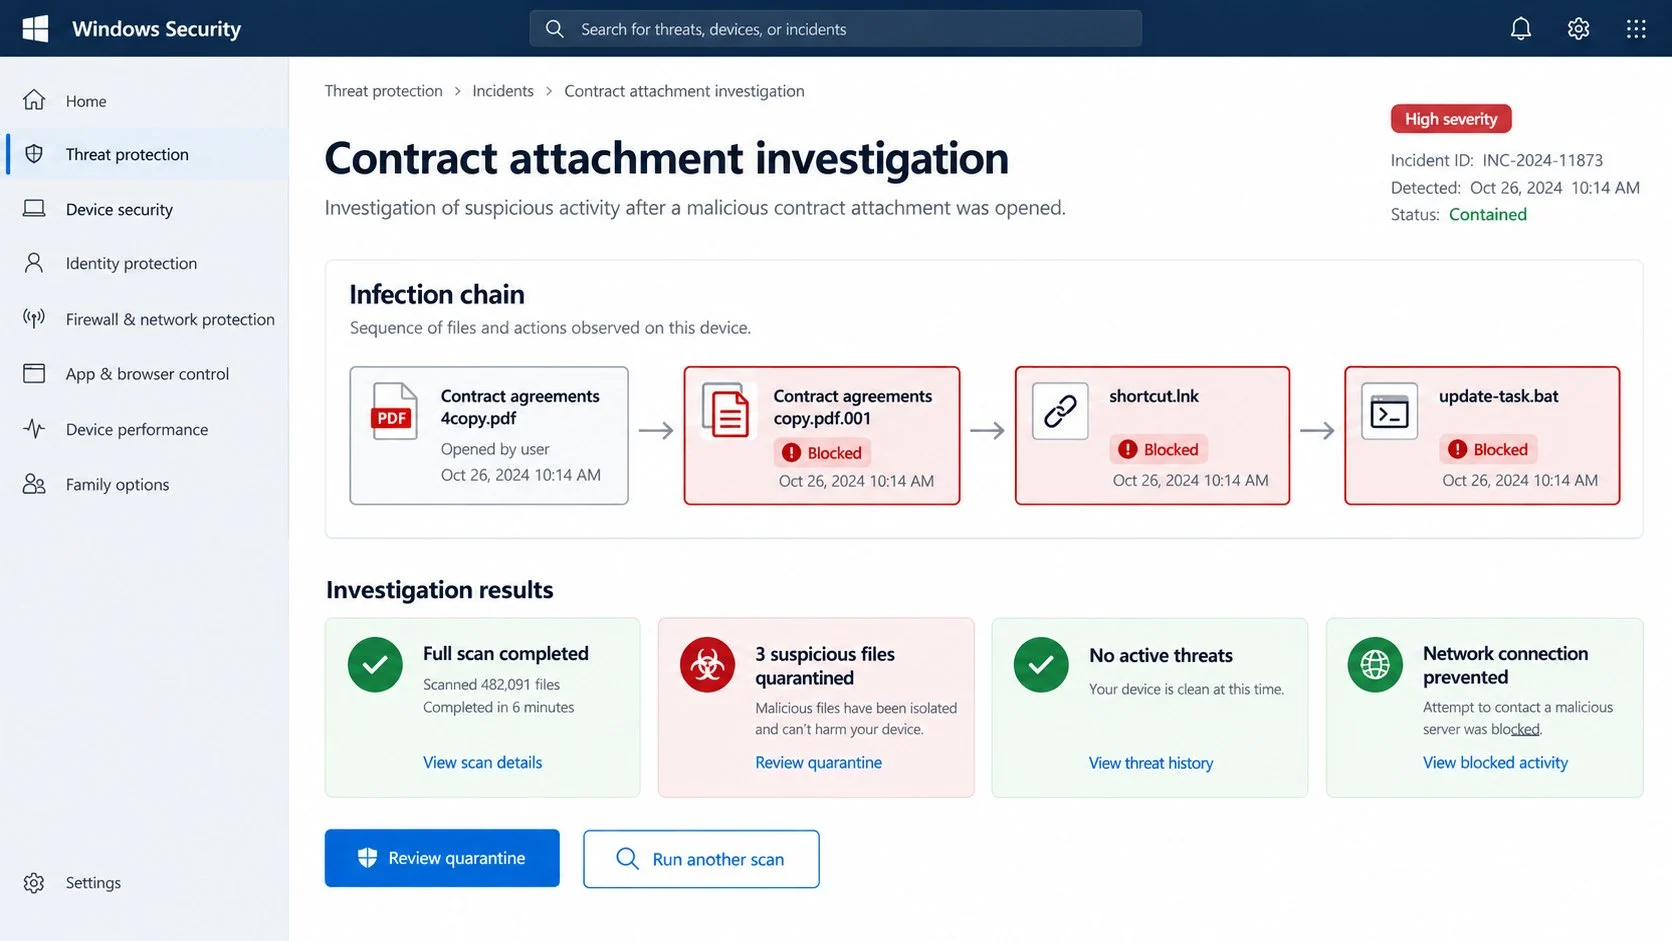
The downloaded file is called “Contract agreements copy.pdf.001.” Despite the PDF-like beginning, its final extension is 001.
The file behaves as an archive containing a Windows shortcut. Running that shortcut retrieves a batch script that issues commands on the computer.
The major warning signs are:
- A contract conversation the recipient cannot match to internal records.
- An attachment with “4copy” in its awkward filename.
- A PDF claiming an ordinary business document is region restricted.
- A second download ending in .001 rather than .pdf.
- An extracted Windows shortcut presented as contract content.
- A batch file fetched after the shortcut runs.
Why Contract Revisions Make Dangerous Email Bait
Contract negotiations naturally involve attachments, comments, redlines, and several versions. That complexity gives a suspicious filename plausible cover.
Recipients also expect late revisions. A document called “copy” or “final” may look untidy without seeming malicious.
The email places the transaction near completion. Signing and stamping imply that only a quick review stands between both parties and a finished agreement.
That timing discourages delay. Employees may worry that questioning the attachment will slow a project or appear unhelpful to a new partner.
Specific appendices add credibility. Mentioning sections 1 and 4 sounds like the sender actually read a document.
Yet the message provides no contract number, legal entity, project title, recipient name, prior thread, or verifiable history.
The identity in the signature can also be copied. A job title and professional closing are easy to reproduce without controlling the represented organization.
Business recipients should verify context, not polish. A real redline must connect to an agreement, counterparty, and colleague already involved in negotiations.
How the Scam Works
Step 1: The campaign targets contract-handling roles
Attackers send the lure to procurement, legal, sales, quality, administration, and management addresses found in public or leaked data.
These roles regularly receive files from outside organizations. An unfamiliar sender is therefore less unusual than it would be in a personal inbox.
Shared addresses create additional opportunity. One employee may assume another team member recognizes the supposed agreement.
Step 2: The email invents a completed negotiation
The sender thanks the recipient for a final contract even though no verified exchange occurred.
This wording transfers the burden of memory. The reader may search mentally for the missing conversation instead of requiring the sender to prove it.
References to red comments and appendices make the story detailed enough to feel individualized while remaining reusable across many targets.
Step 3: The attached PDF displays believable contract pages
The first file opens as a document and can show paragraphs, revision markings, page thumbnails, and formal headings.
Those visible pages serve as scenery. They encourage the user to believe meaningful revisions are present even though the content cannot be fully reviewed.
Simply seeing a normal document page does not establish safety. PDFs can contain links and actions that direct users toward external downloads.
Step 4: A false regional error prompts another download
A pop-up claims the current file is unavailable because of a geographic restriction or compatibility problem.
The proposed solution is a downloadable copy. The recipient is encouraged to treat this second file as the same contract in another format.
Regional restrictions are implausible for a normal agreement exchanged directly between businesses. The message offers no secure document portal or support contact.
Step 5: The downloaded name disguises an archive
The resulting filename includes “.pdf.001.” Users scanning from left to right may notice PDF and overlook the true ending.
Numbered extensions can belong to split archives, but they are not ordinary standalone contracts. Their contents require careful examination.
File icons are unreliable because Windows associations and embedded resources can make unfamiliar formats appear more recognizable.
Step 6: The archive reveals a Windows shortcut
Inside is an LNK file, which is a Windows shortcut capable of launching commands, programs, or scripts.
A legitimate contract archive should contain documents, not a shortcut. Running it executes its configured target rather than opening contractual text.
Attackers can give the shortcut a document-like name and icon. Visible appearance does not change its executable behavior.
Step 7: The shortcut retrieves and starts a batch script
The shortcut initiates a download for a BAT file. Batch scripts can run command-line instructions without providing a friendly application window.
Those instructions may contact remote servers, create files, change settings, or launch additional programs.
At this point, the interaction has moved far beyond viewing a contract. The computer is executing a chain selected by an unknown sender.
Step 8: An unknown payload may gain a foothold
The final malware family has not been reliably identified in the reviewed chain. It is important not to invent a specific diagnosis.
Possible payloads include information stealers, remote-access tools, loaders, ransomware, spyware, miners, or other malicious software.
Because behavior can change between downloads, every completed chain requires containment and investigation, even when the computer appears normal.
What Each Extension Tells You
The original .pdf file
PDF is commonly used for contracts and is not inherently dangerous. Risk depends on content, embedded actions, links, and the user’s decisions.
In this campaign, the first PDF acts as a lure. Its visible error pushes the recipient toward another download rather than delivering usable revisions.
The misleading .pdf.001 file
Windows normally treats the final suffix as the extension. A name ending in .001 is not converted into a PDF by containing “.pdf” earlier.
Some legitimate archiving tools create numbered pieces, but an unexpected email should not ask employees to reconstruct such content without verification.
The extracted .lnk shortcut
An LNK file tells Windows where to go or what to execute. It can contain command arguments that are not obvious from the icon.
Shortcuts belong in software and desktop workflows, not inside a supplier’s proposed contract. Their presence should stop the review immediately.
The downloaded .bat script
A BAT file contains a sequence of command-shell instructions. Double-clicking it can perform several actions rapidly under the current user’s permissions.
Security tools may block the network request, script, or later payload. No alert should be dismissed merely because the supposed contract looked professional.
Potential Consequences of Running the Full Chain
An information stealer can target saved browser passwords, session cookies, cryptocurrency wallets, application tokens, and documents.
A stolen session may let criminals enter an account without knowing its password. Changing credentials remains essential, but active sessions also need revocation.
Remote-access malware can give an operator continuing control. They may inspect files, capture keystrokes, download tools, or use the machine as an entry point.
A loader can install a different payload later. An apparently quiet computer may simply be waiting for further commands.
Ransomware could encrypt accessible files and network shares. Organizations should isolate the device before it communicates with additional systems.
Email and document access can expose real contracts, customer identities, pricing, intellectual property, and signatures.
That stolen material supports more convincing business impersonation. Criminals can continue a genuine negotiation using details taken from the infected computer.
The absence of obvious symptoms is not reassuring. Many modern threats avoid pop-ups and deliberately remain quiet while collecting valuable information.
Why the Unknown Payload Still Requires an Urgent Response
The download can change between recipients
A shortcut may contact a server that chooses files according to location, operating system, time, or campaign instructions.
Two recipients opening identical attachments might therefore receive different programs. One laboratory result cannot describe every later download.
Blocking or removing one hosted file may cause the operator to replace it. The surrounding email can remain useful after infrastructure changes.
Security controls may stop only one stage
An email gateway could permit the PDF while endpoint protection blocks the shortcut. Another product might prevent the script’s network connection.
Each alert describes a particular event, not necessarily the complete chain. Responders should correlate mail, endpoint, identity, and network evidence.
Do not restore a quarantined shortcut merely because the final payload was absent. Its intended behavior remains incompatible with a contract review.
Credentials may already have been exposed
Information stealers can collect browser data quickly. Disconnecting the device later does not retrieve passwords or session cookies already transmitted.
Reset important credentials from another trusted computer. Then revoke sessions so copied cookies cannot continue providing access.
Workplace administrators should consider secrets used on the endpoint, including VPN profiles, cloud tokens, saved remote sessions, and shared application accounts.
Clean-looking behavior may be temporary
A loader can wait before delivering its next component. Scheduled tasks, startup entries, or remote instructions may activate after the initial review.
Manual deletion of visible files does not prove the system is trustworthy. Hidden persistence and stolen access require broader investigation.
When business-sensitive data was accessible, rebuilding from a verified source may be safer than attempting to identify every modification individually.
How to Verify a Proposed Contract Changes Email
Find the negotiation in internal records
Search the contract register, customer system, project workspace, and existing email threads. Identify the colleague responsible for the alleged final version.
A real negotiation should have participants, dates, drafts, and approvals. No matching record means the attachment should remain closed.
Contact the counterparty through a trusted route
Call a known representative or use an address from the signed agreement, established account, or independently located corporate website.
Do not verify through reply details supplied by the suspicious sender. Ask whether Kolena Guo and the attachment name are recognized.
Display full filenames before opening anything
Enable file extensions in the operating system. Inspect the final suffix, not the icon or an earlier word inside the name.
Quarantine .001 archives, LNK shortcuts, and BAT scripts delivered as contract material. Submit them to the security team without executing them.
Use an isolated review process
Organizations can open uncertain documents in managed sandboxes or analysis environments with logging and restricted network access.
Ordinary employees should not improvise this step. Forward the original message as an attachment to trained responders so headers and files remain intact.
What to Do If You Fell Victim to the Proposed Contract Changes Email Scam
- Disconnect the computer from networks. Disable Wi-Fi and unplug Ethernet to limit communication and possible spread.
- Do not delete the downloaded files. Leave evidence untouched for trained responders unless your security team instructs otherwise.
- Notify workplace security immediately. Describe every action, including opening the first PDF, downloading .001, extracting LNK, or running the shortcut.
- Run a full Malwarebytes scan. Update it first from a trusted connection when safe, then quarantine confirmed threats and retain the report.
- Use AdGuard after containment. It can block known malicious advertising and destinations, but it cannot reverse commands already executed.
- Change passwords from a clean device. Prioritize email, business systems, banking, cloud storage, and credentials saved in the affected browser.
- Revoke sessions and tokens. Sign out all devices, remove unknown applications, and replace exposed API keys or application passwords.
- Check neighboring systems. Administrators should inspect authentication, endpoint, firewall, proxy, and DNS logs for related activity.
- Prepare for restoration if required. Use verified backups and rebuild the machine when responders cannot establish trustworthy cleanup.
- Warn relevant business contacts. Explain that contract-themed messages may have been sent using stolen information or compromised accounts.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Contract agreements 4copy.pdf a real contract?
In this campaign, the file is a lure that introduces a second download. Verify similarly named attachments independently before opening them.
Does opening the first PDF guarantee infection?
No. The documented chain requires additional interaction, including downloading and running later content. Opening it still warrants caution and reporting.
What is a .pdf.001 file?
Its final extension is .001, not .pdf. Here it is used as an archive that contains a dangerous Windows shortcut.
Why is an LNK file dangerous in a contract archive?
A shortcut can execute commands or scripts. It is not a contract document and has no legitimate reason to appear in this workflow.
Which malware does the campaign install?
The final family is currently unknown and may change. Treat a completed chain as a serious compromise requiring professional investigation.
Can I keep working if the computer looks normal?
No. Disconnect it and contact security. Stealers and remote-access threats can remain silent while transmitting information or awaiting instructions.
The Bottom Line
The Proposed Contract Changes email turns a believable redline review into a layered download chain involving an archive, shortcut, batch script, and unknown malware.
Confirm contract history first, display complete extensions, and isolate the device immediately if any executable stage was reached.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.