


A message from someone you know offers a document or installer. Later, a banking screen behaves strangely and refuses to get out of the way.
TCLBanker can connect those events by abusing Windows and its signed-in accounts. Getting back to banking safely also means cutting off the messaging access it used.
Overview
TCLBanker targets banking activity on Windows
TCLBanker is banking malware targeting Brazilian users. This is a Windows infection, not an Android cleanup problem involving TCL-branded phones.
It watches browser navigation and can place deceptive full-screen interfaces over a banking session. These screens can request information or keep the user waiting.
A disguised package and trusted accounts spread it
The analyzed attack used a malicious MSI inside a ZIP, with a genuine Logitech application loading an attacker-supplied DLL. Logitech’s official installer is not the malicious package.
Separate modules abused authenticated WhatsApp and Outlook accounts to send messages onward. An unexpected installer can arrive from a contact you already recognize.
Handle the urgent banking and account risks first
- Disconnect the PC and stop entering banking credentials, codes, or transfer approvals.
- If banking was affected, call the institution from a trusted phone using a known number.
- Use a trusted phone to log out affected WhatsApp linked devices.
- Work computer: contact security before scanners or restarts. Let the administrator handle work-account sessions.
Save the incoming message, filename, approximate execution time, and any transaction reference. Do not forward the installer to warn other people.
How to Remove TCLBanker From Windows
For a personal Windows PC, follow the removal procedure below. Keep banking and messaging recovery on trusted devices while the computer is cleaned.
For a work or school computer, contact its IT or security team before installing tools or restarting. Its investigation may need evidence from the running system.
If remote access is suspected, disconnect Wi-Fi or Ethernet and stop using this PC for sensitive accounts. Arrange trusted downloads and updates before proceeding with cleanup.
Start with Malwarebytes. HitmanPro and ESET are optional second opinions for unresolved findings or continuing symptoms. Run one scanner at a time.
- STEP 1: Use RKill only if malware blocks your scanner
- STEP 2: Scan and quarantine threats with Malwarebytes
- STEP 3: Optional: Check unresolved threats with HitmanPro
- STEP 4: Optional: Run a second-opinion scan with ESET
Step 1: Use RKill only if malware blocks your scanner
RKill attempts to stop known malware processes so your security software can run. It does not remove the infection.
Use it only on a personal Windows PC when malware is blocking your scanner. Otherwise, skip directly to Malwarebytes.
-
Download Rkill.
Download RKill using the button below. On the download page, choose the iExplore.exe version.
This is a renamed copy of RKill, provided for infections that block security tools by filename.
RKillStops malware processes so other tools can runDownload RKillOpens the BleepingComputer download page in a new tab.
-
Run RKill.
Open your Downloads folder and double-click iExplore.exe. Allow the program time to finish checking for processes that interfere with cleanup.
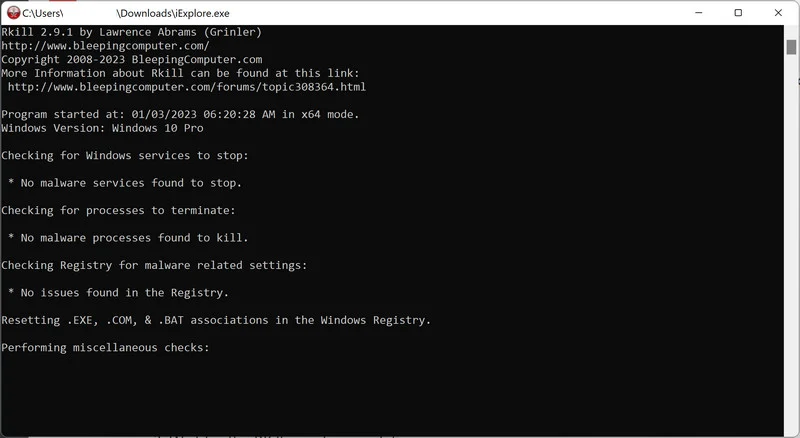
When the black window closes, a log opens. Keep the log, do not restart yet, and continue directly to Malwarebytes.
Step 2: Scan and quarantine threats with Malwarebytes
Malwarebytes for Windows can scan for malware and quarantine detected threats. Use the free Custom Scan below; a paid plan is not required for this cleanup.
-
Download Malwarebytes
Click the button below to download Malwarebytes for Windows. Paid real-time protection is optional.
Malwarebytes Free for WindowsScans and removes malware at no costDownload MalwarebytesMalwarebytes free scanner informationOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium
-
Install Malwarebytes
When the download finishes, open Downloads and double-click MBSetup. If Windows asks for permission, check that the prompt identifies Malwarebytes, then click Yes.

-
Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
Installer screens and optional offers vary. Skip unwanted Browser Guard, trial, or paid-plan offers. The free Custom Scan remains available; Threat Scan may require a paid plan.
-
Choose Personal for your own computer, then click Next. For a work-managed device, use your organization’s approved response instead.

-
Wait for installation to finish.

-
If the Welcome to Malwarebytes screen appears, click Get started and follow the remaining prompts.

-
On the final screen, click Open Malwarebytes to launch the program.

-
-
Choose the scan type and optional rootkit check
On the Scanner tile, click the three dots, choose Advanced Scan, then Custom Scan.
Expand the folder selector and select the C:\ system drive. Include any other drive where the suspicious files were stored.
If Scan for rootkits is available, you can enable it. This setting is unavailable on Windows ARM devices; leave Windows security protections enabled.
Review how potentially unwanted programs and modifications will be handled. Keep detection enabled rather than automatically ignoring these items.
-
Start the Scan
Click Start Custom Scan. Allow Malwarebytes to update its detection information if prompted.
-
Wait for the Scan to Finish
Wait for the Custom Scan to finish. The time required depends on the selected locations and the amount of data.
-
Quarantine the Detected Threats
When the scan finishes, review the detections and keep the threats you want removed selected. Click Quarantine.
If a detection is unclear, save the report and ask for help before excluding or restoring it.

Wait while Malwarebytes quarantines the selected items. Do not restore a file merely because an unfamiliar name appears in the results.

-
Restart Your Computer
If Malwarebytes asks for a restart, save your work and click Yes. After signing back in, reopen Malwarebytes and check the report for unresolved detections.

Step 3: Optional: Check unresolved threats with HitmanPro
HitmanPro is a second-opinion scanner for Windows. It examines suspicious files using cloud analysis, including SophosLabs. An internet connection is needed for that check.
Scanning is free. Removing detections requires an eligible one-time 30-day trial or a paid license.
A computer that already used its trial may not qualify again. You do not have to buy HitmanPro to follow the Malwarebytes cleanup above.
-
Download HitmanPro
Click the button below to download HitmanPro if you want a second opinion on unresolved symptoms or detections.
HitmanProSecond-opinion malware scanner from SophosDownload HitmanProFree scan. Removal requires an eligible 30-day trial or a paid license. Opens the official HitmanPro page in a new tab.
-
Install HitmanPro
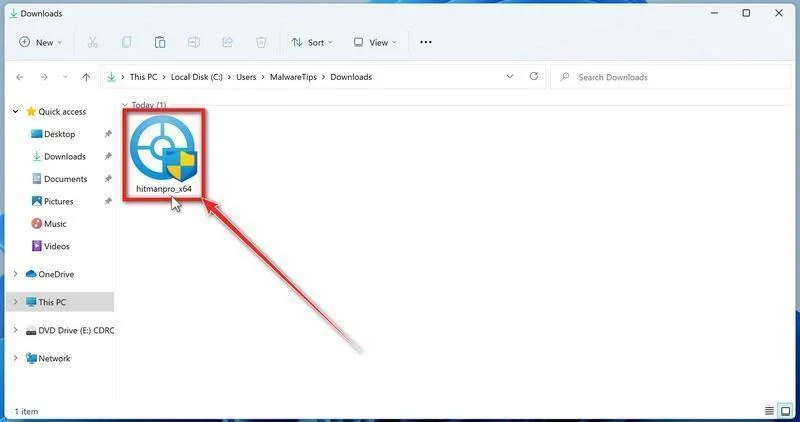
When the download finishes, open your Downloads folder and double-click the file: “hitmanpro.exe” on 32-bit Windows, or “hitmanpro_x64.exe” on 64-bit Windows.
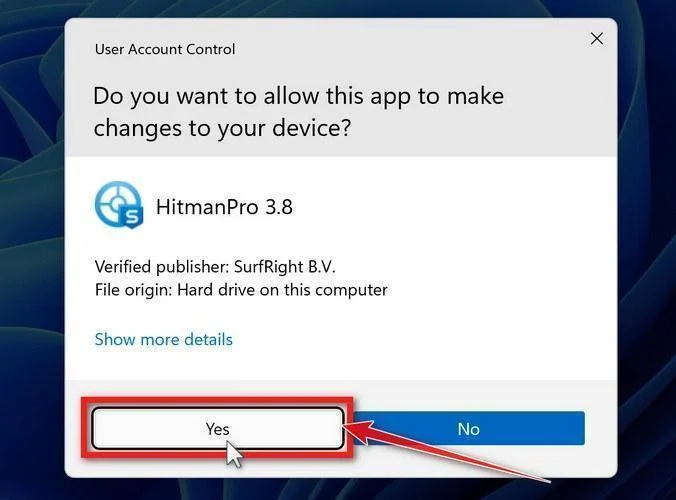
If a User Account Control pop-up asks whether HitmanPro can make changes to your device, click “Yes” to continue.
-
Follow the On-Screen Prompts
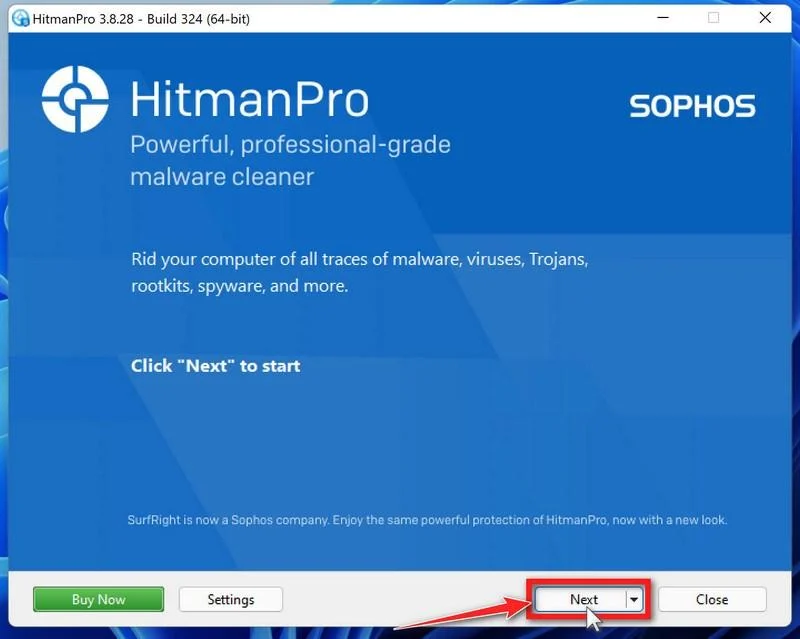
On the HitmanPro start screen, click Next. Read and accept the terms if you agree, then continue.
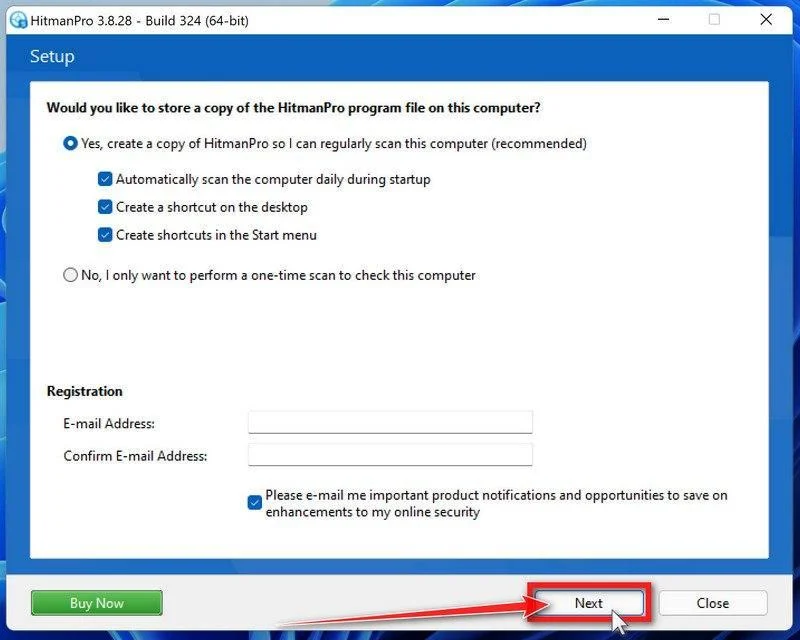
Choose whether to keep a copy for later use or run a one-time scan. Review optional startup and email preferences, then click Next.
-
Wait for the Scan to Finish
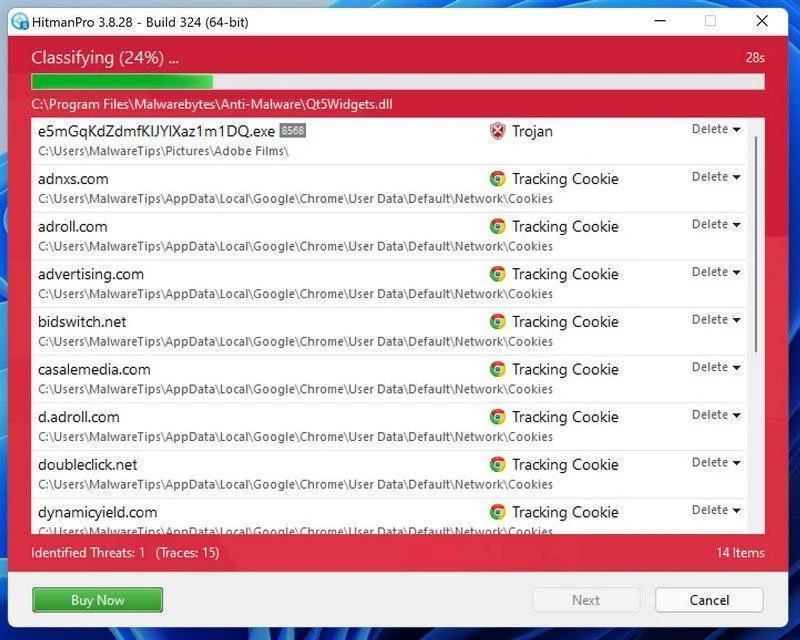
Let HitmanPro finish scanning. Review its findings once the scan has completed.
-
Review the Results and Click “Next”
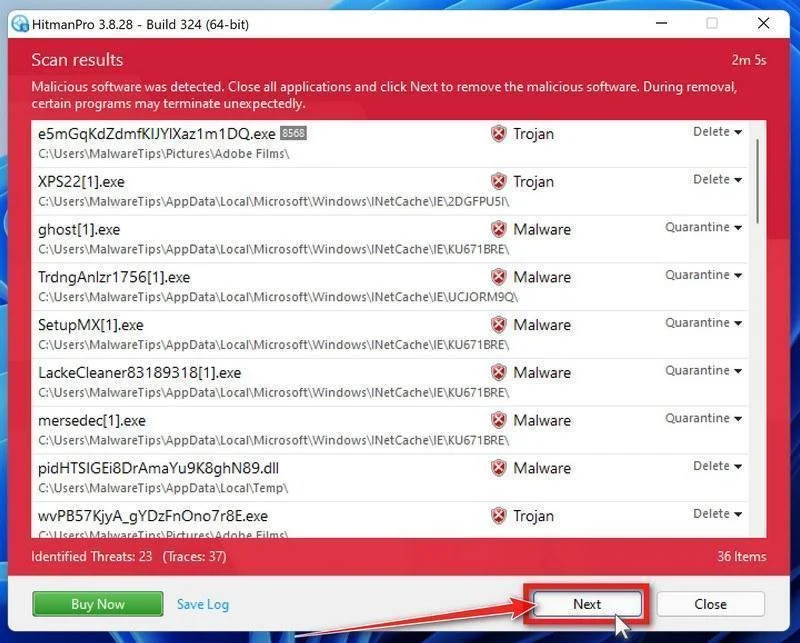
Review the detected items and their proposed actions. Save the log if you need help with an unfamiliar detection, then click Next to proceed.
-
Click “Activate Free License”
If this computer qualifies, click Activate free license and follow the activation prompts.
If no trial is available, use an existing license or save the report for assistance. Do not assume a purchase is necessary to continue cleanup.
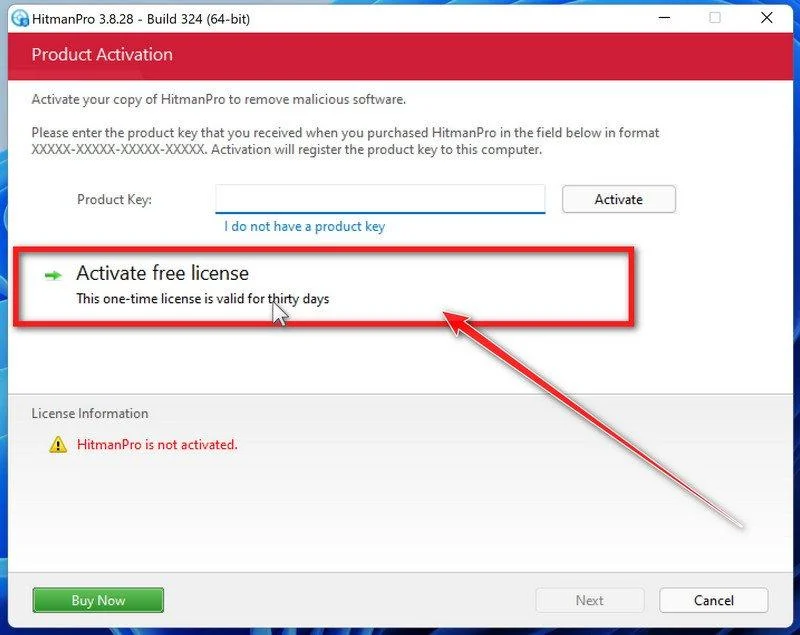
After removal, review the summary and click Next. Choose Reboot if requested, or Close if no restart is needed.
If detections return or the original symptoms persist, keep the reports and ask for help. A clean scan cannot rule out every threat.
Step 4: Optional: Run a second-opinion scan with ESET
ESET Online Scanner is a free second-opinion scanner for Windows. Use it if you need another check after cleanup, rather than running several scanners together.
-
Download ESET Online Scanner
Click the button below to download ESET Online Scanner.
ESET Online ScannerFree one-time malware scan from ESETDownload ESET Online ScannerOpens the official download page in a new tab.
-
Run the Installer
When the download finishes, open Downloads and double-click esetonlinescanner.exe. Approve the Windows permission prompt after checking that it identifies ESET.
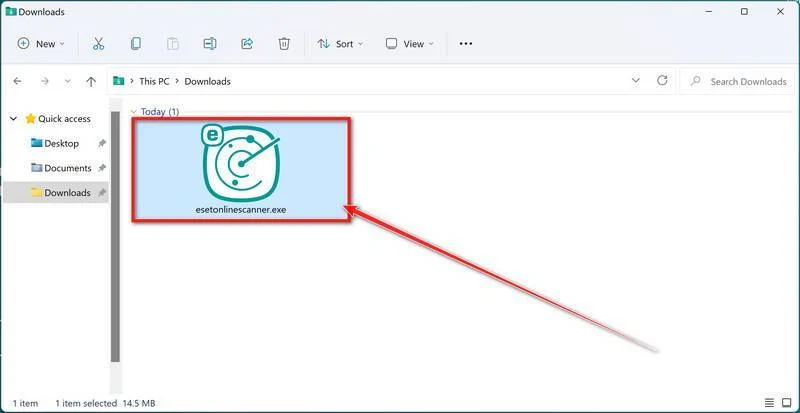
-
Install ESET Online Scanner
On the start screen, select your language from the drop-down menu and click Get started.
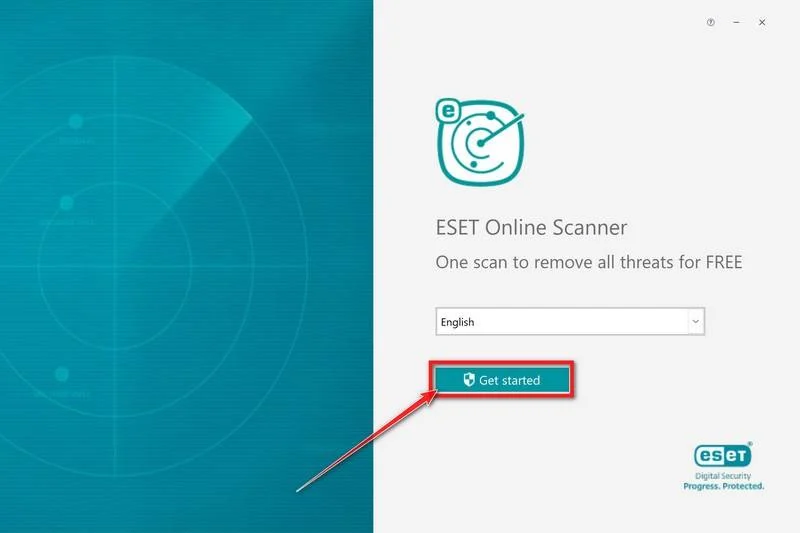
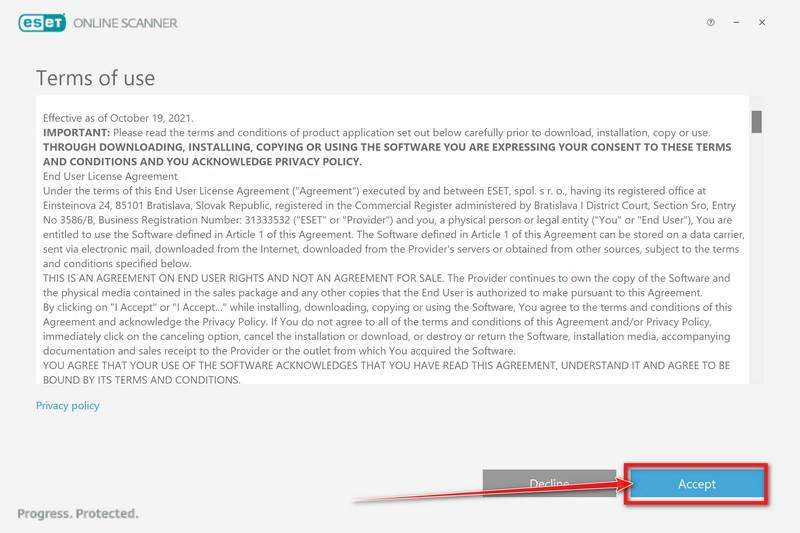
Read the Terms of use. Click Accept if you agree, then Get started if that screen appears again.
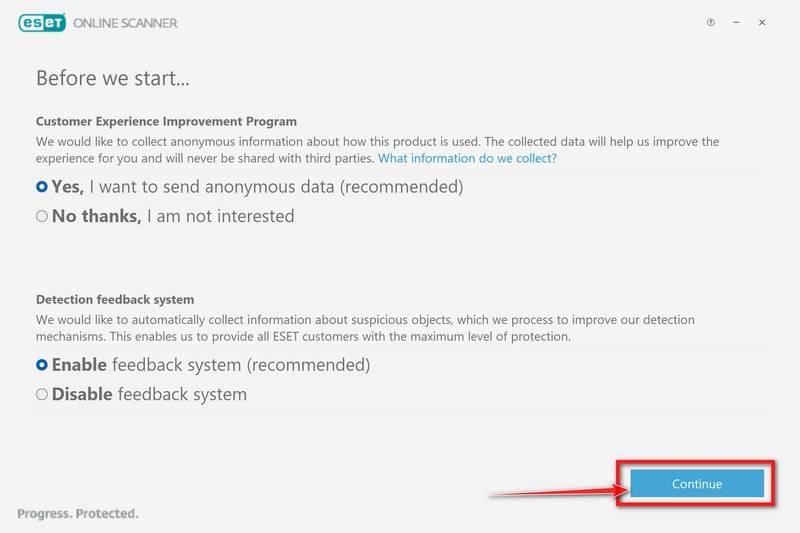
Choose your preferences for the Customer Experience Improvement Program and the Detection feedback system (either choice is fine), then click Continue.
-
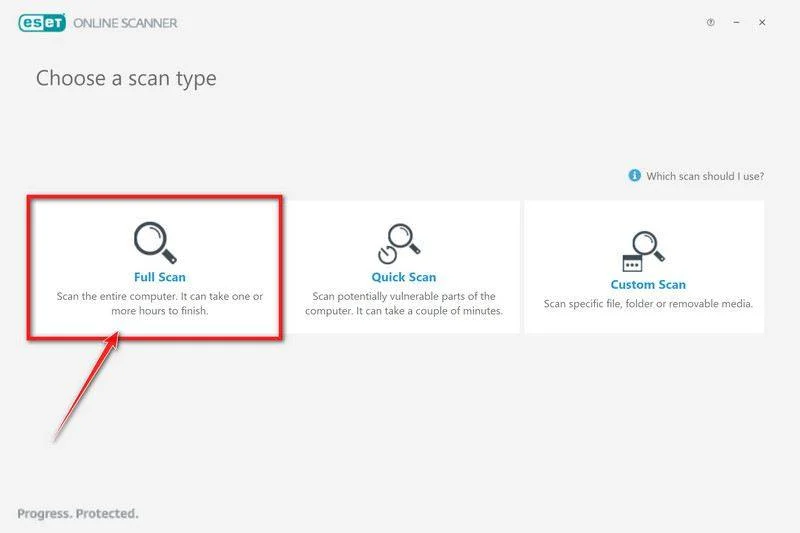
Start a Full Scan
Click Full Scan for a broader check than the quick-scan option.
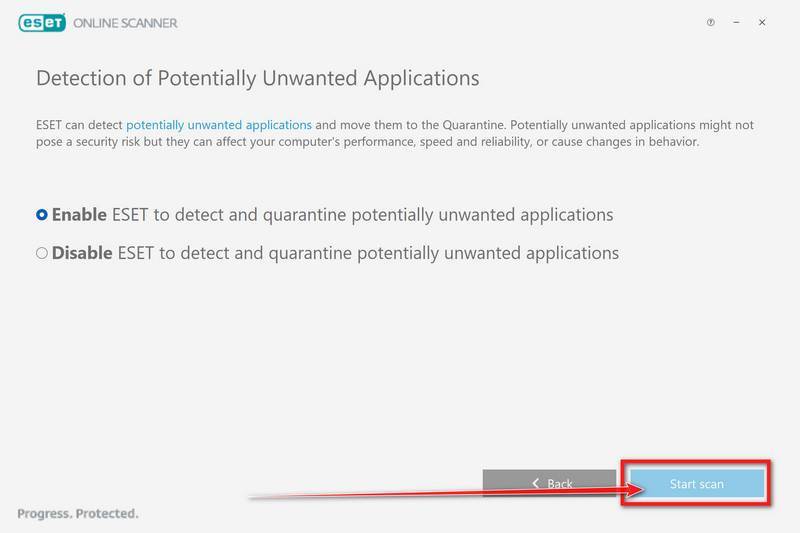
Select Enable for Detection of Potentially Unwanted Applications. Then click Start scan.
-
Wait for the Scan to Finish
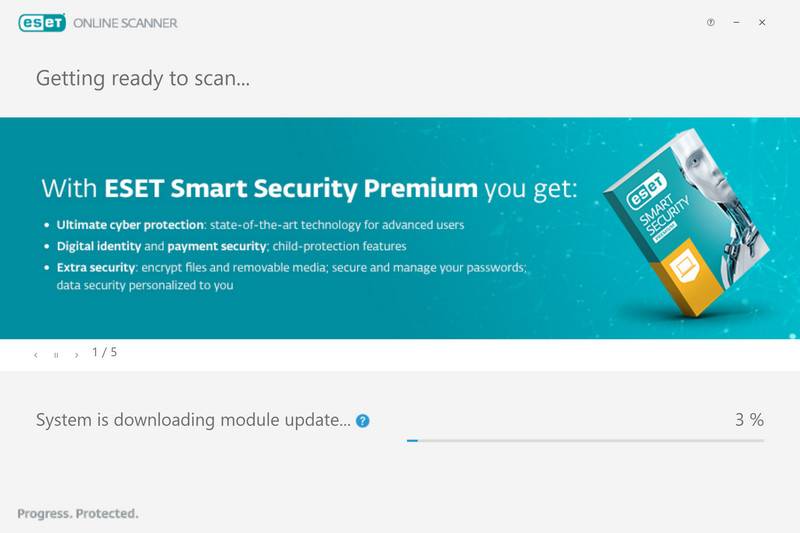
Allow the detection modules to download and update. The file scan begins afterward.
Leave the scan running until it finishes. A full scan can take an hour or longer, depending on your computer and the data being checked.
-
Review the Results
When the scan finishes, open View detailed results and check the action recorded for each detection.
ESET attempts to clean and quarantine detected threats. If an item remains unresolved, keep its details for assistance.
Click Save scan log to keep the results. Then click Continue.
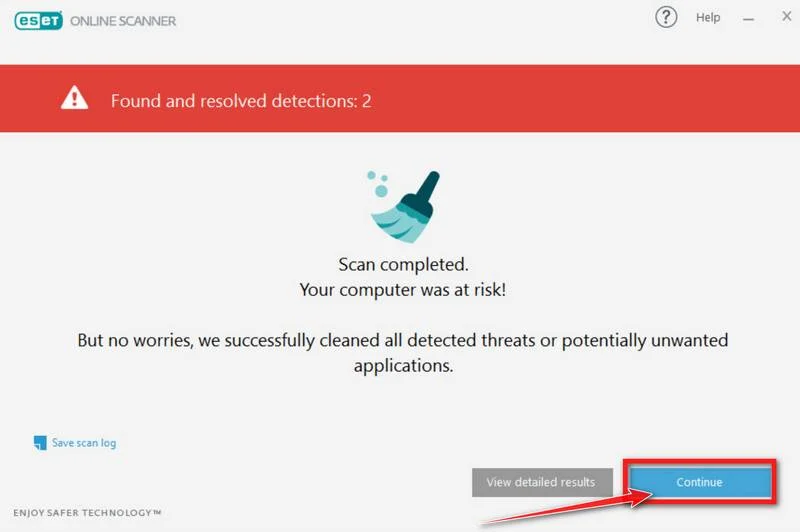
Restart if ESET requests it. Afterward, check whether detections or the original symptoms return.
If problems continue, keep the scan reports and ask for help in the MalwareTips removal forum. Do not repeatedly restore quarantined files.
What to Do After Removing TCLBanker
-
On your trusted phone, open WhatsApp’s Linked devices screen. On Android, use the three-dot menu; on iPhone, open Settings.
-
Select the affected or unrecognized linked device and choose Log out. Do not relink the Windows PC until its remediation is complete.
-
Review sent messages and warn contacts who received an unexpected package. Use WhatsApp’s linked-device instructions if you cannot find the session.
-
For Outlook and Microsoft accounts, review sign-in activity, sent mail, forwarding rules, recovery information, multifactor methods, and unfamiliar connected applications from a trusted device.
-
On a personal Microsoft account, change exposed credentials and use Sign out everywhere when needed. Allow up to 24 hours; this action excludes Xbox consoles.
-
For Microsoft 365 work accounts, give your administrator the incident time and Microsoft’s compromised-mailbox response steps.
-
Keep the affected PC offline during session recovery. Warn contacts without sending the executable or exposing private account details.
Give the Bank the Details It Needs
Tell the bank which screen appeared, what information or codes you entered, and whether a transfer was approved. Include the transaction reference and time.
Use the number on your card, trusted bank app, or statement. Do not call a number displayed by the suspicious overlay.
Ask the bank to secure access and investigate unauthorized activity. Keep its response with your incident records while Windows cleanup continues.
Warn recipients without spreading the installer
Make a list of unauthorized WhatsApp and Outlook messages, including the recipient, time, and attachment name. Keep it with the Windows incident record.
Warn affected recipients through a trusted channel. Identify the message they should avoid, but do not forward the ZIP or installer to demonstrate the problem.
If business email was involved, give the list to your administrator. Let the organization coordinate message tracing and any wider notification.
Keep the bank’s case reference and follow-up instructions separately from public removal-help posts. Share transaction records only through the bank’s verified reporting process.
TCLBanker Persistence and Family Names
Elastic Security Labs assessed TCLBanker as a major update to MAVERICK/SORVEPOTEL and tracked the campaign as REF3076.
The analyzed build used a LogiAI directory and a scheduled task named RuntimeOptimizeService. Give the complete path and alert to your responder.
Have that specific entry checked rather than deleting unrelated scheduled tasks or application folders. Retain the scan report if the same component returns.
Frequently Asked Questions
Can a familiar WhatsApp contact send the malicious package?
Yes. The propagation modules abused signed-in accounts. Confirm unexpected installers through a separate trusted channel before opening them.
What if the bank address still looks correct?
Stop entering information if a strange overlay blocks normal controls or requests more codes. Call the bank independently from another device.
Does removing the file log out linked accounts?
Use WhatsApp and Microsoft session controls separately. Keep the PC offline until both device cleanup and account recovery are complete.
Should I tell everyone in my contacts?
Warn people who received unauthorized messages from your account. Identify the suspicious message without forwarding its executable attachment.
What should I keep for removal help?
Keep the original message, download source, filename, execution time, and detection report. Give banking records only to the bank or an appropriate responder.
What comes first if a transfer looks wrong?
Contact the bank from a trusted device immediately. Do not wait for the scans or enter another code supplied by the suspicious screen.
The Bottom Line
Do not trust an unexpected installer simply because a familiar account sent it. Confirm the request through another channel.
If execution or banking interference occurred, isolate Windows, contact the bank when relevant, complete removal, and secure the linked messaging sessions.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.