Advice Request Driver from Lenovo identified as virus. False positive?

Share practical recommendations that address the author's needs.
The "Sabsik.FL.A!ml" detection's on Microsoft Defender is a detection by AI Machine Learning.
Even if the recognized AVs (Kaspersky, GDATA, Bitdefender, F-Secure etc.) do not detect it, I can't say that it is 100% clean... (given the detection Sophos / Malwarebytes)
But on the other hand, Symantec/Norton has removed the detection....

The most likely hypothesis is that Lenovo uses a confuser (to protect source codes) that has potentially been used by a malware, hence the "PowerShell" detections...

If someone has a download link to run it on a virtual machine, I take :)
Thanks for reply.
Because I don't know if I can post link here, I DM you the driver's information page, whink includes a download link.
Thanks for your kindly help again!
 
Microsoft is fast at fixing false positive when reported to them. Though in this case of this driver, Lenovo themselves should contact Microsoft and sort it out quickly and should even pause the delivery of the driver for now. But TBH, Lenovo should have checked this beforehand. Even our resident developer on this forum Andy Ful submits his apps to security vendors prior to releasing a new version to make sure popular AV products don't detect his tools after releasing.
 
Microsoft is fast at fixing false positive when reported to them. Though in this case of this driver, Lenovo themselves should contact Microsoft and sort it out quickly and should even pause the delivery of the driver for now. But TBH, Lenovo should have checked this beforehand. Even our resident developer on this forum Andy Ful submits his apps to security vendors prior to releasing a new version to make sure popular AV products don't detect his tools after releasing.
I want to report to Microsoft at first, but they force me to uploaded file.
BTW, I report to Lenovo psirt this week, they said they have a team on this issue, but don't have results to share yet.
 
Last edited:
Hello guys!

After testing, I can give you a verdict.
He sent me the link, I was able to download it and test it.

Result : It's a 100% false positive :)

Already, the file is about 780Mb (I downloaded it very quickly, I have fiber optics).
Then, it is signed, but that means nothing, you can also sign a malware you will say...

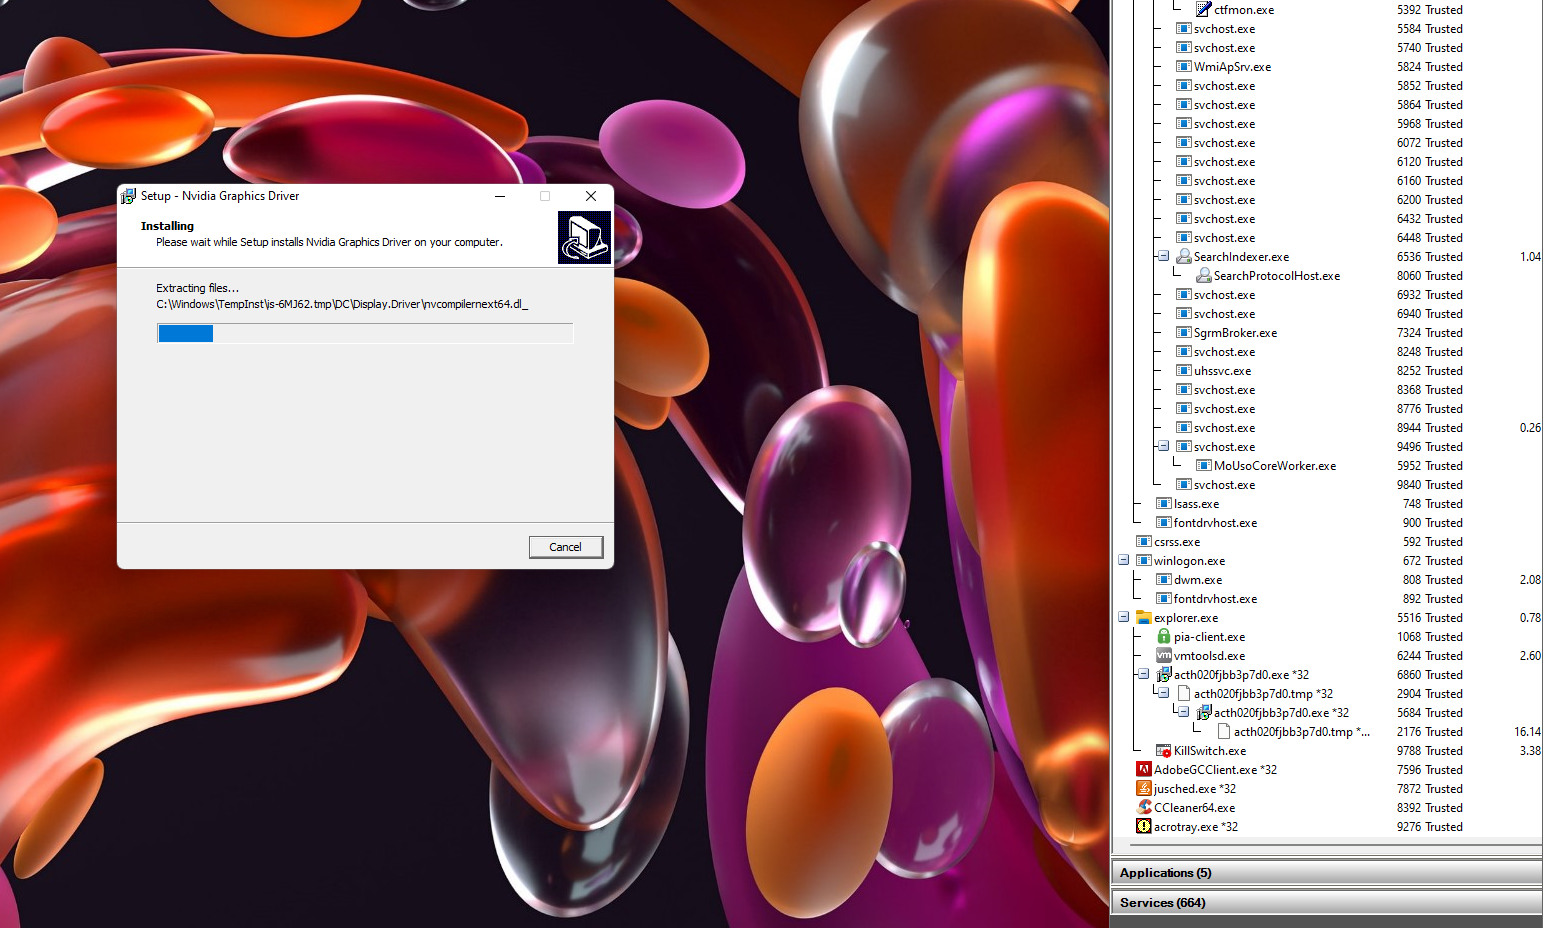
Well, nothing happened. The installation went smoothly :)

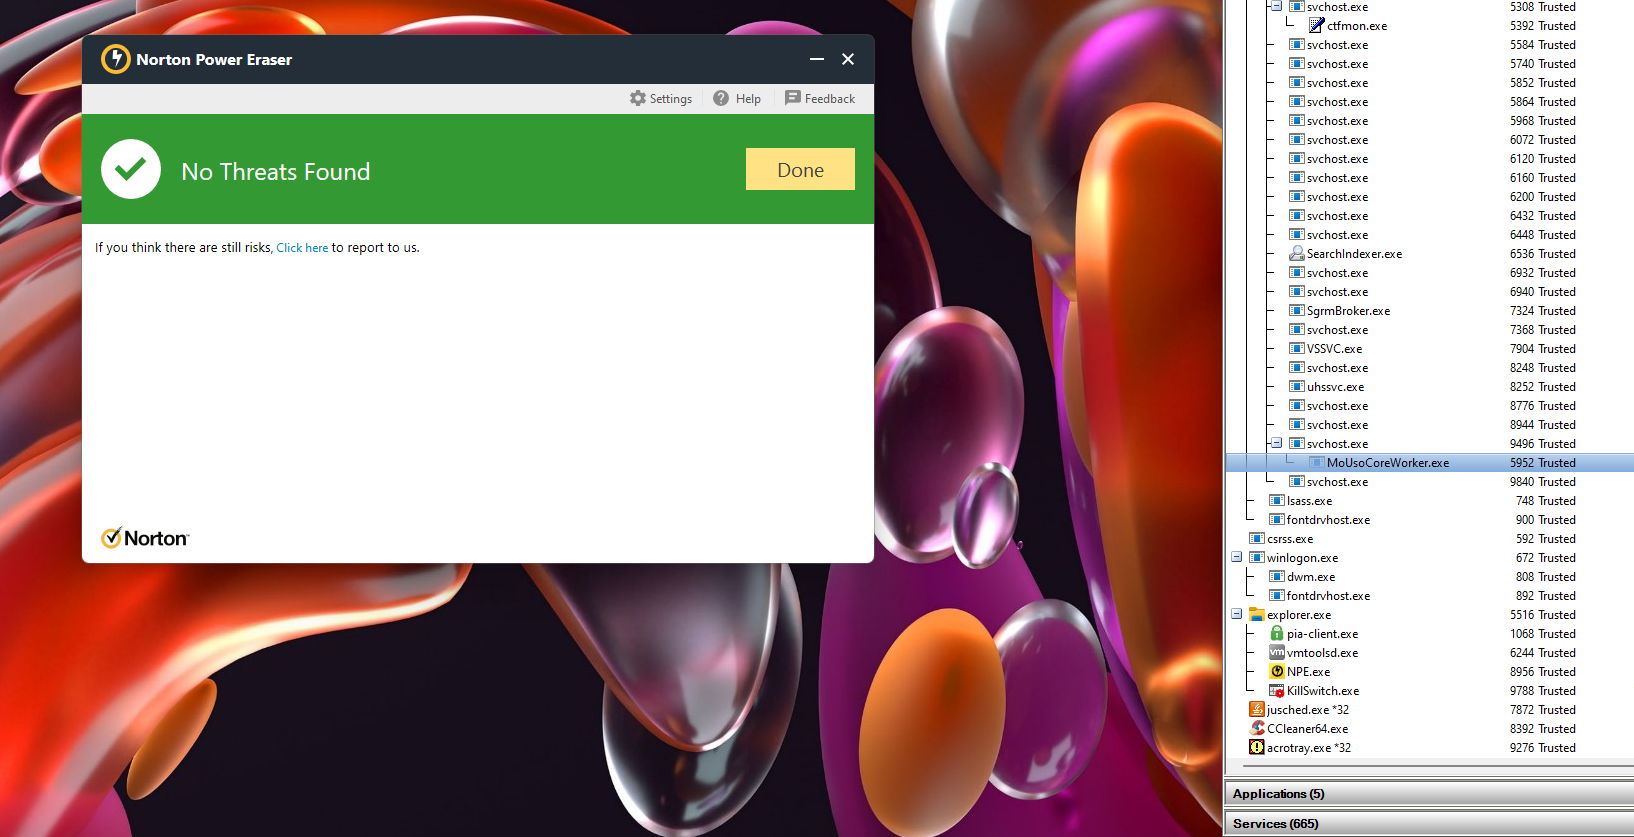
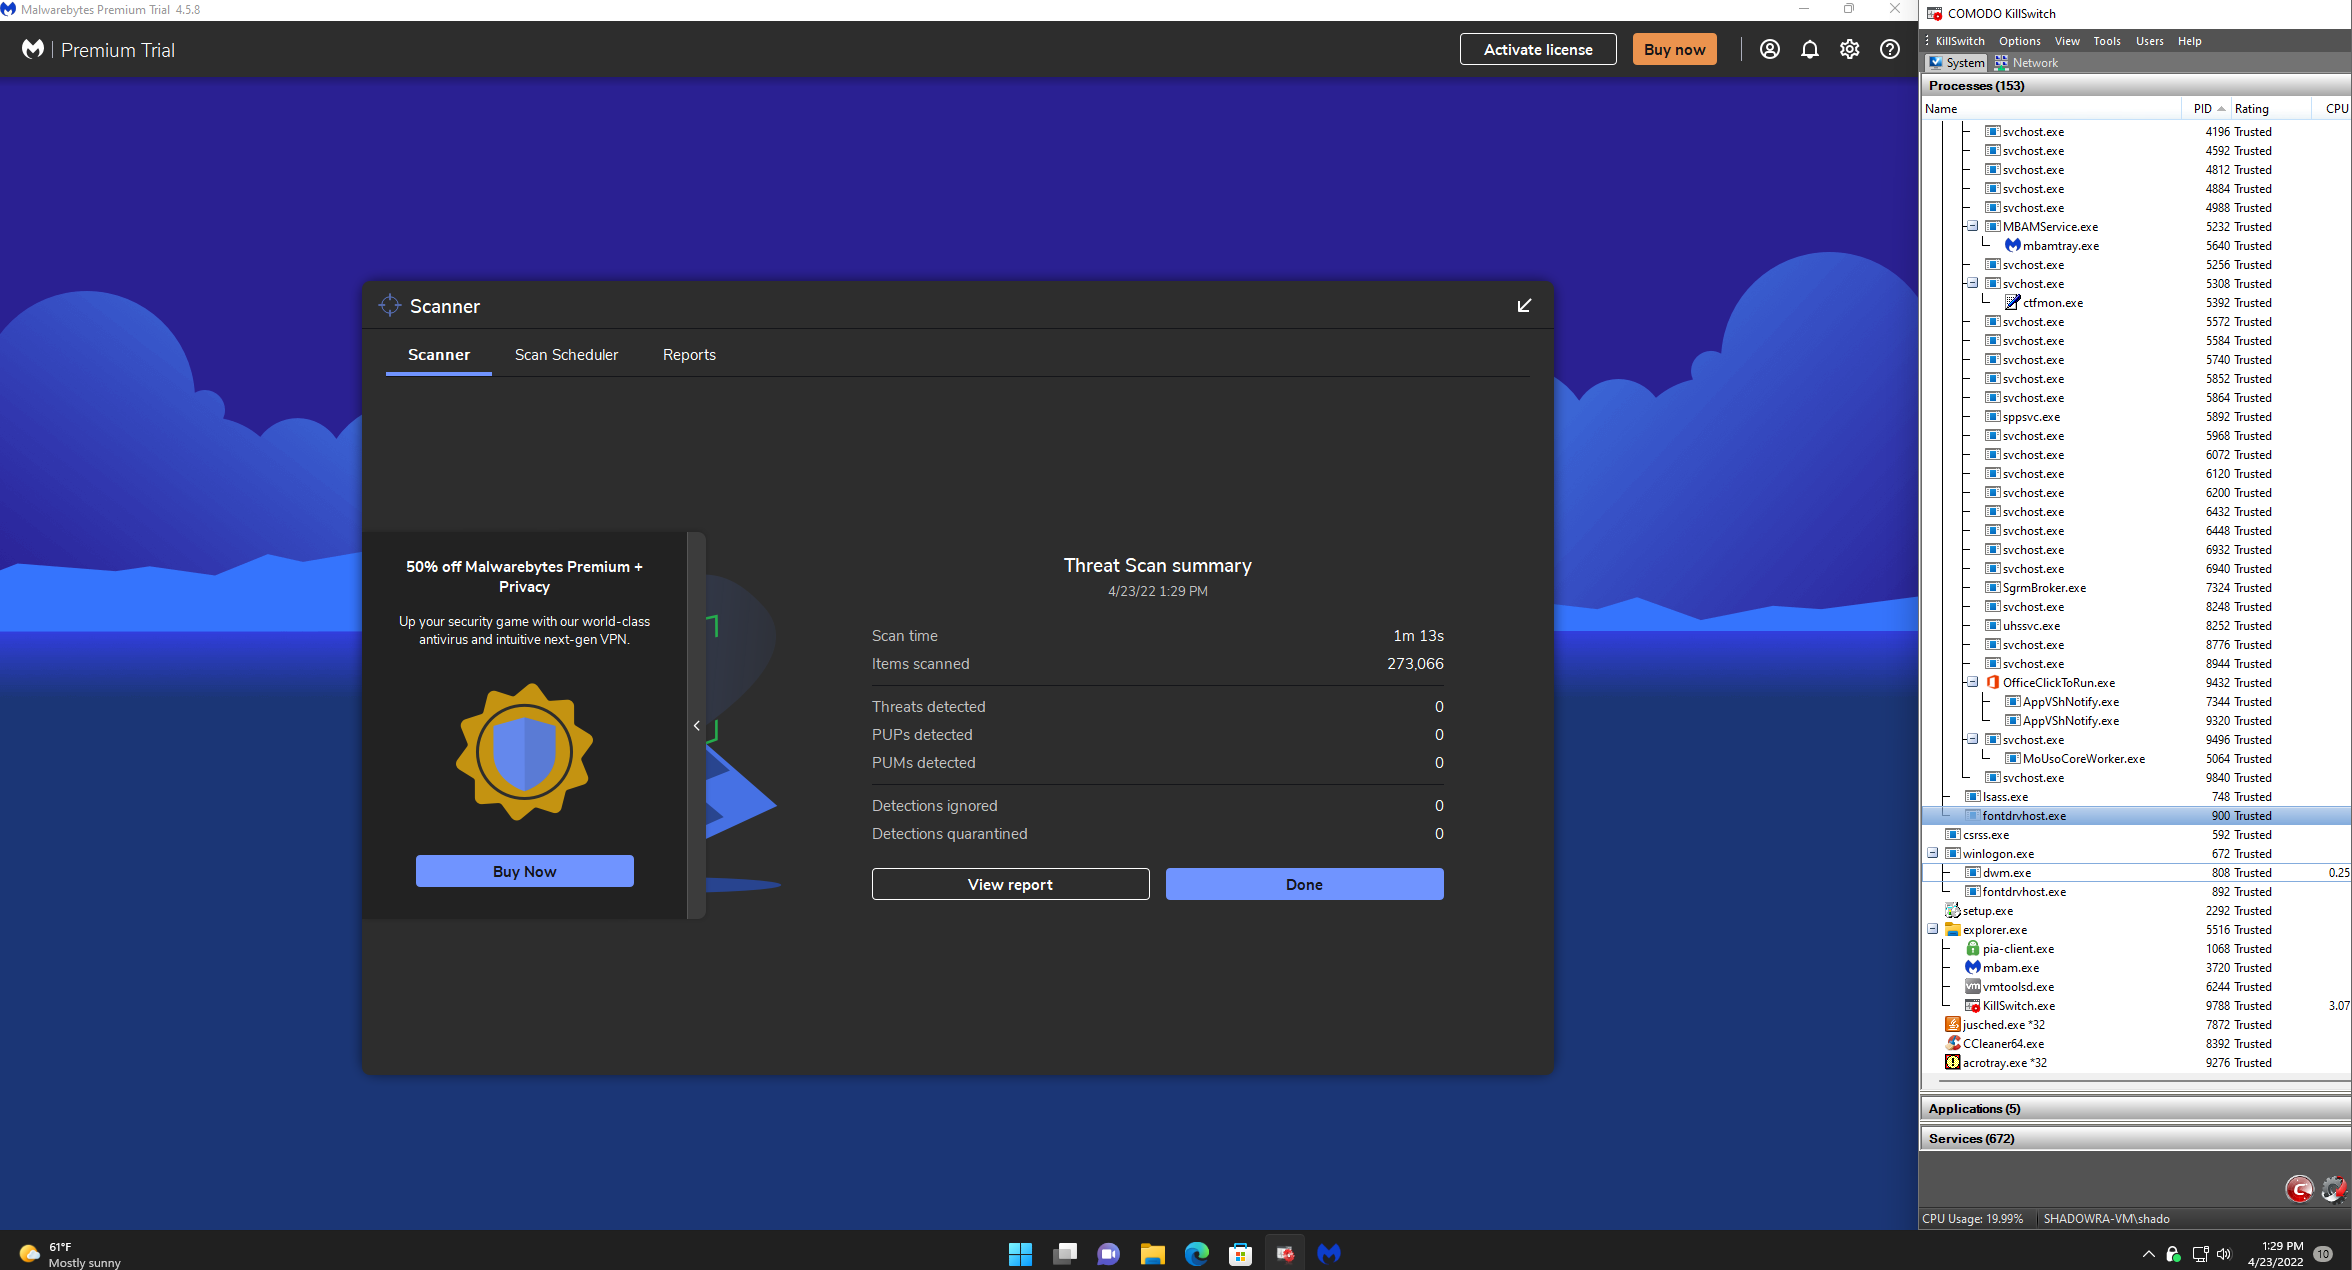
Here are the screenshots.

He used PowerShell once, probably to replace a driver.

1eGxWvwj.png

qASRQTpi.png

mnwP6BbO.png

Nothing has been detected and the virtual amchine is doing very well.
It is a false positive of the antivirus :cool: ;)
Actually, I downloaded MB at first, and MB detect 11F3.exe as trojan Powershell.

Maybe the new database fixed it?
 
It should be unrelated, as a video driver in unrelated to a BIOS update.
If you say so but I was just assuming the driver included WITH the NIOS update was why MB was flagging it. Please read again.

CVE-2021-3971: A potential vulnerability by a driver used during older manufacturing processes on some consumer Lenovo Notebook devices that was mistakenly included in the BIOS image could allow an attacker with elevated privileges to modify firmware protection region by modifying an NVRAM variable.
 
If you say so but I was just assuming the driver included WITH the NIOS update was why MB was flagging it. Please read again.
The detection "Trojan.PowerShell" is in no way related to a BIOS vulnerability. It seems that the download is just for the video driver anyway.
 
Ok was posted, then removed. Backdoor

Lenovo issues fixes for laptop backdoors | Malwarebytes Labs​

Apr 21, 2022 · Lenovo issues fixes for laptop backdoors UEFI. UEFI is a specification that defines

But yes you are correct, the OP downloaded the driver and it was not because his computer was shipped with the backdoor .

 
Last edited by a moderator:
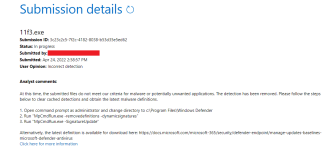
I submitted it to Microsoft today, and now they have removed the detection. So the false positive is gone.
But it also shows how incompetent or careless the people at Lenovo are. They couldn't even submit a false positive report.
View attachment 266103
Thank you for your help ☺️
I contact to Lenovo Twitter, Lenovo website support, and ask them if they can report to Microsoft.
Seem they did't do this.🤔
 

Recently browsing

Members who viewed this thread in the last 5 minutes

Back
Top