Advanced Plus Security LinuxFan58's PC Security Config

Original forum configuration · expand details
Last updated
Sep 14, 2026
Main use of this computer
For work or educational use
Operating system
Linux
OS version and support details
Linux Mint 22.3 Zena Cinnamon Wayland
On-device encryption
Other full-disk drive encryption software
Device sign-in security
    • Windows Hello PIN or biometric sign-in (face / fingerprint / Touch ID)
Security updates
Allow security updates and latest features
Update channels
Allow stable updates only
User Account Control (UAC)
Not applicable - not running Windows
Smart App Control
Not applicable / not available on this device
Network firewall
Enabled
Router and network details
TP-Link triband with IPv6 disabled, We use the three WIFI-networks seperately. The 2.4 Ghz is used for IoT-devices and guest (SPI-, NAT, ARP-filtering and intrusion detection enabled). The two 5 Ghz networks are for my wife and I (each uses his/her own) with additionally IP-MAC binding and MAC filtering enabled. I have set the e-mail log message level to critical events (acting as a rudimentary NIDS). The 5Ghz network has eternal lease time while 2.4 Ghz has short lease time (8 hours) and network partitioning enabled.
Real-time protection
Non root user using build-in Linux sandboxing (AppArmor, Firejail, Flatpak) as extra protection layer.
Device firewall
Built-in Firewall for Mac/Linux
Custom security settings
  • Using only official package sources from verified publishers and de-installed all unused accessoires and applications.
  • Installed FAPOLICYD denying normal users to execute something which does not come from above repositories
  • Mildly hardened Linux by disabling P2P, remote access, old TLS versions and enabling ASLR system wide.
  • Created additional Firejail profiles with firecfg and reduced Flatpak permissions with flatseal.
  • Added OpenSnitch outbound application firewall to compliment inbound GuFW.
  • Installed logcheck with e-mail warning for security alerts & events
  • Using Wayland (experimental) on Cinnamon desktop.
Periodic malware scanners
When I receive files from others I scan them with Virus Total. My half yearly data backups to external USB are scanned with Microsoft Defender :cool:
Malware sample testing
I do not participate in malware testing
Environment for malware testing
None
Browsers and extensions
Brave-Origin policies and site-pernissions with Brave adShield disabled
Secure DNS
  1. NextDNS in the Router with OISD and telemetry blocklists enabled (for IOT devices), allowing only common TopLevelDomains to connect.
  2. We use Quad9 as default DNS (at OS-level and DoH) for our Laptops and smartphones
  3. Cloudflare Zero Trust Free with account as DOH in the browser.
Desktop VPN
Proton VPN free for Linux on-demand (out of home). At home I have little use for VPN because our IP and IP location are changed regularly :-).
Password and passkey manager
Build-in (OS and Browser)
Maintenance tools
None
File and photo backups
  • FreeFileSync quick on-demand backups to a partition on my internal SSD to which sandboxed utilities, desktop accessoires and applications have no access to.
  • The half yearly full backup saves to an external USB-SSD which is checked (afterwards) by Microsoft Defender on my wife's laptop (which has triple USB protection).
Subscriptions
    • None
System recovery
TimeShift (to another partition on 1 TB SSD)
Usage and exposure
    • Visiting familiar websites
    • Working from home
    • Making audio/video calls
    • Opening email attachments
    • Online shopping and card payments
    • Logging into my bank account
    • Streaming audio/video content from trusted sites or paid subscriptions
    • Coding and development
Computer specs
AMD Ryzen 7 (5700U) laptop with 1 TB SSD and 16GB RAM
Notable changes
To many :)

After jumping back and forth, I finally decided for:
  • Changed from ControlD free to Cloudflare free ZT
  • Replaced 7-zip (unsandboxed) with PeaZip in Flatpak
  • Moved from LibreOffice in Flatpak to LibreOffice in Firejail
  • Moved from Thunderbird to Evolution (both in Flatpak sandbox)
  • Moved from Xfce desktop with X11 to Cinnamon desktop with Wayland
  • Installed fapolicyd (simular to WDAC on Windows) application control (see post)
Feedback preference

Detailed suggestions and alternatives welcome

Sampai-san I listened to your advice :-) but this is part of Safe Browsing, so I stick to double download protection ;)

1789283498885.png
 
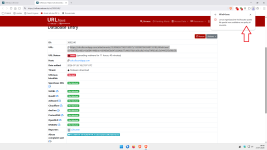
But considering that the default policy value is 0 (No special restrictions) and that probably only 1–5% of users enable it, only those users (me + you + @7Oz-64 ) can rely on this type of protection against malicious downloads, as shown in the image below:

2a.png

Look at the red arrow at the top.;)

Translation:

"Your organization has blocked this file because it did not comply with a security policy"
 
@Sampei.Nihira
Thanks for remember me(y);),
Yes download restriction set to 4 here and M Kees @LinuxFan58 i saw your policies and you should add more brave specific policies like these (i know you've already had some of them but not all :
Code:
  "TorDisabled": 1,
  "BraveRewardsDisabled": 1,
  "BraveWalletDisabled": 1,
  "BraveVPNDisabled": 1,
  "BraveAIChatEnabled": 0,
  "BraveNewsDisabled": 1,
  "BraveSpeedreaderEnabled": 0,
  "BraveWaybackMachineEnabled": 0,
  "BraveStatsPingEnabled": false,
  "BraveWebDiscoveryEnabled": 0,
  "BravePlaylistEnabled": 0,
  "BraveLocalAIEnabled": false,
  "BraveP3AEnabled": false,
  "BraveTalkDisabled": true

I'm back with brave-origin (External Ublock Origin (gorhill one) as UG-C is too slow for updating.
@Sampei.Nihira
MBG does a really good job to catch some fresh url haus bad url's, but it's slowdown browsing during my test.
And for Brave-Origin (still free on linux), i've disabled brave ad shields (just fingerprinting keeped).
@LinuxFan58
am still testing your extension package (uboS, matrix, ds, adshield), don't worry i think in near future i'm going to pass them in my production machine, DS is really a unique one, catch alls bad download 100%, for the others i think these needs more time to be completly mature(y).
And as you use Mint, you should try self hosted searxng + nginx + ca-https, no others search engine can protect you like this, if you're intersted i've a strong maintenance scripts pakaging (install, update, check, clean, renew cert, uninstall and hardened settings.yml, nginx.conf, searxng.service and limiter.toml)
 
Last edited:
@7Oz-64

For my Security setup,though I believe other Security setups could also do without this extension,a web filter extension is useless.
I already have NextDNS, Google Safe Browsing, excellent dynamic filtering, at least four consecutive layers of protection against malicious downloads, the most vulnerable software listed in the anti-exploit database with at least 13 or 14 overrides, and a hardened Brave sandbox that isn’t set to default......;)

P.S.

Why don't you start a thread with your own Security configuration?:)
 
@Sampei.Nihira

When you first told me about the new RUST features in flags (a few weeks ago), I typed in rust to see what is else available (Rust has memory integrity protection and C/C++ not).

I noticed RUST decoding was enabled for BMP but disabled for JPG and ICO (which are more complex than BMP), so assumed a phased migration and left it at the defaults (also my image/photo viewe/editor run sandboxed in Linux, and the old JPG meta data exploit was directed ar Windows and it was long ago, so I thought it was not a big deal).
 
am still testing your extension package (uboS, matrix, ds, adshield), don't worry i think in near future i'm going to pass them in my production machine, DS is really a unique one, catch alls bad download 100%, for the others i think these needs more time to be completly mature(y).
Thanks for the heads up 3P-Matrix-lite is complete matured.

AdShleld and uBS are nearing completion (added last useability features like saving/restoring settings and don´t know to optmize further in the code, from 9.5.1 for uBS and 1.3.1 for AdShield it will be bug fixing). There is not much use using uBS and AdShield side by side. Would be helpful when you focus on AdShield in combination with your favourite adblocker.

Thanks for the poliicy setting (maybe I had forgotten to tell you) I already added a few which you posted earlier (and not set myself)

Selfhosting search engines is a bit over the top for me, I pass on that :-)
 

Recently browsing

Members who viewed this thread in the last 5 minutes

You may also like...

Continue exploring the conversation.

Back
Top