Is Kaspersky able to detect?


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.

Still amazed virus scope catched it
Not at first site but by manuallyIs Kaspersky able to detect?
Kaspersky?

VirusScope is amazing at analyzing unknown apps in sandbox it uses Static Analysis and Dynamic Analysis to do thatStill amazed virus scope catched it
Got it enabled only in the container on my system but maybe if it gets better I could enable it globally
Please check KasperskyMS Defender configured
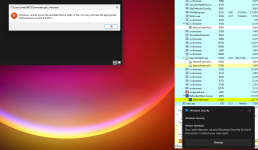
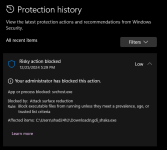
View attachment 286859View attachment 286860
But once I reset it to default in DefenderUI, it passes without reaction (which was to be expected).
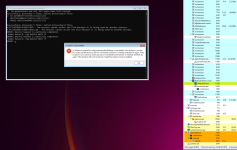
View attachment 286861

Sorry I missed. @harlan4096 could you please reply again??@harlan4096 has already done so and mentioned

VirusTotal What about Zillya?Interesting, hadn't heard previously that Rising uses the cloud from Kaspersky.
View attachment 286845


Shaka when walls fellLest Eset's dynamic analysis isn't sad alone, Sophos also totally lost this battle. While its screens show significant damage to the system.
View attachment 286842
View attachment 286843
The emulation from the extension failed but pretty sure if you actually executed the sample the behavior components would have stopped it and probably the same with ksn , liveguard both failed but if you actually executed the sample it just might have stopped the infection using some behavior componentsZone alarm?
Above harlan showed that actually execution ofthe sample would cause behavior components to defend at least some damage and the same will happen with some other avsI see You got no bootable systems, but in the case of Kaspersky, system was not destroyed up to that point, in fact I could reboot without issues, but all my custom settings in my local account were changed to default or removed, for example the taskbar icons pinned, the order of the icons in the desktop, the color theme of the session, things like that, but system was completely usable.
I don't think it was in the first execution in the opentip sandbox but changing the hash is probably enough to find outHum actually the sample did not trigger any behavior component (although KOTIP service tagged it as malware in 1st execution), but probably Intrusion Prevention, putting it in Low Restricted group, minimized in part, the malicious activities, and avoided to completely destroy the system.
It's easy to evade sophos anyway as they literally load services of sophos software into the sandbox of intelixLest Eset's dynamic analysis isn't sad alone, Sophos also totally lost this battle. While its screens show significant damage to the system.
View attachment 286842
View attachment 286843
Not just that new gaming engine languages and even rust to some extent
Members who viewed this thread in the last 5 minutes