Hot Take uBlock Stripped - Dynamic Filtering is available on the webstore

Thread details
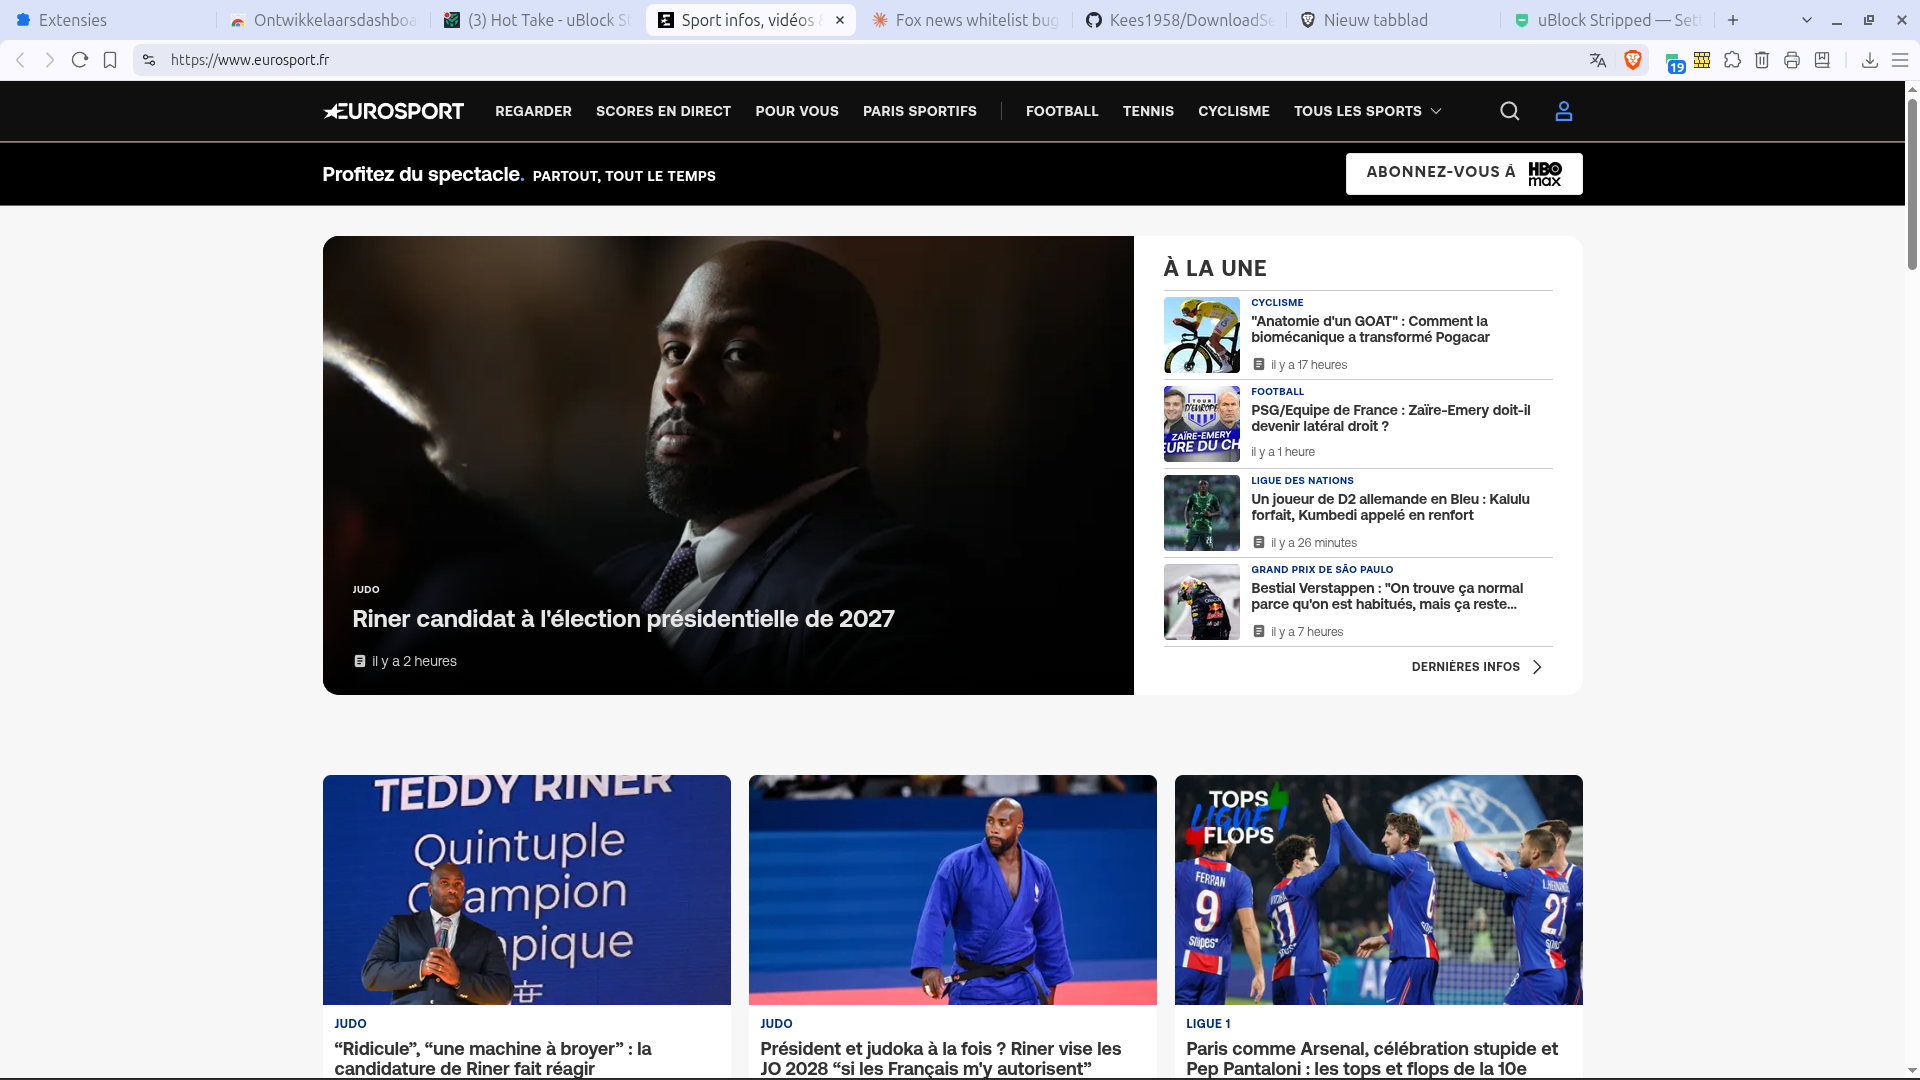
First website use Cosmetic element picker (and only select bannertop)
Click more in left bottom corner when you don´t see. You can select and unselect identifiers by clicking on them (turns them blue when selected)
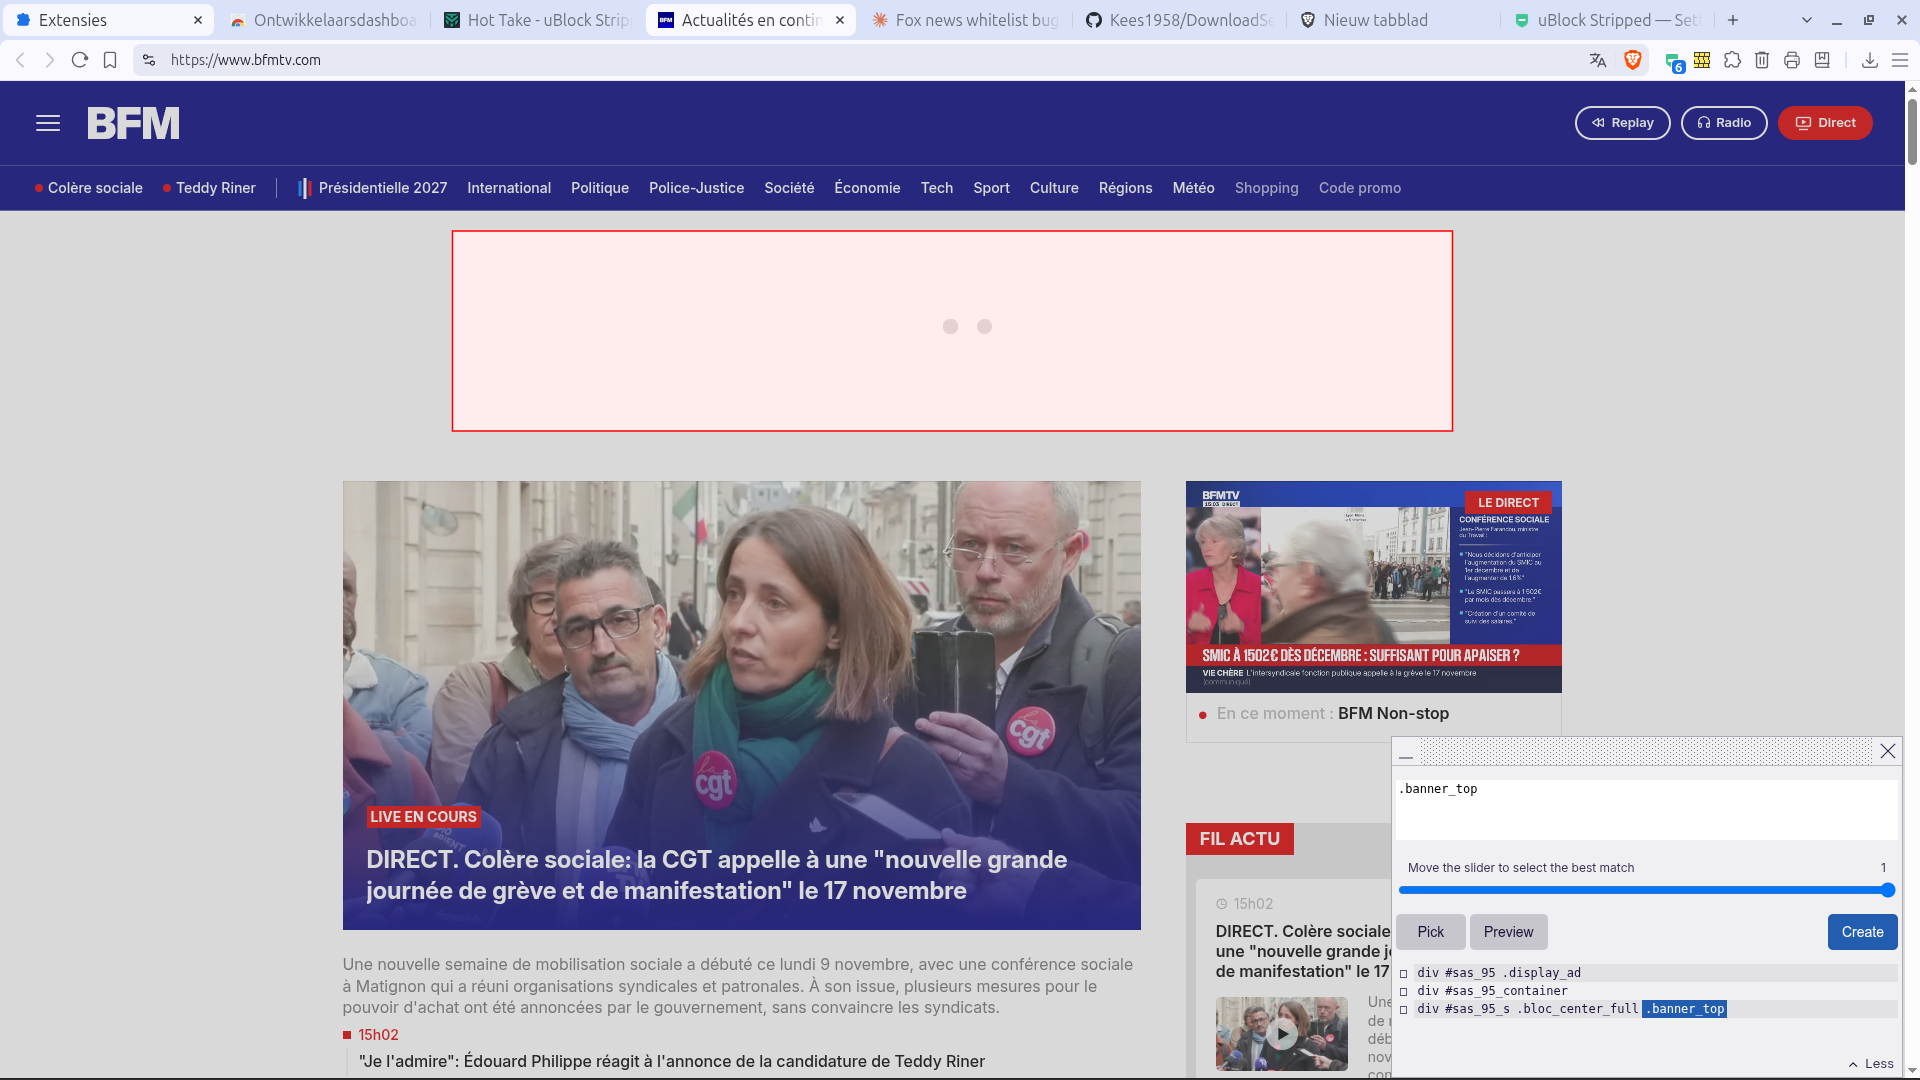
1794233125692.png


Second one needed two cosmetic element pickter hides
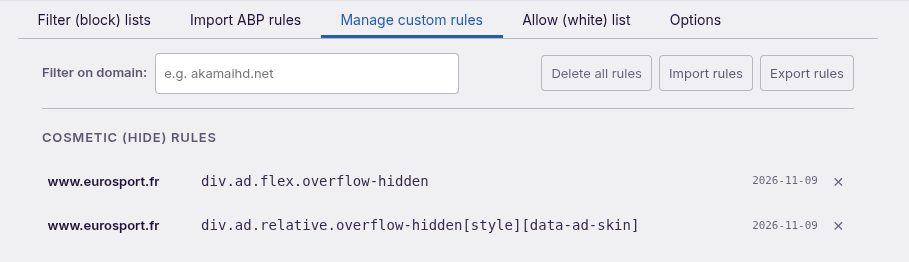
1794234254229.png

1794234150015.png


Do you have French language filter enabled?
 
Last edited:
@LinuxFan58
Yes i already do that but upon reload page it reappeared and cosmetics element picker rules have no effect, give it a try, it's easily reproducible
Second website ok sorted out, thanks

Capture d’écran du 2026-11-09 15-15-48.pngfr.png
 
Last edited:
@LinuxFan58 - why have you removed the "No pings" feature? Or has it moved, or been hard coded?
Ping is hardly used anymore for tracking puposes. When you want to apply it system wide enter ||*$ping in import ABP Rules.
Pings are mostly used to pre-load stuff nowadays (when you watch a movie, pinging fragments are used by the CDN or Gstatic to prefetch them).

10.7 has more fingerprint signals (now also include the whole bunch Tracking Pings, 1x1 and 3x3 tracking pixels and 1x1 frames plus Tracking Beacons
Advantage of tracking pixels, frames and beacons for advertising servers over pings is you are more easily tagged.
 
Last edited:
Pings is hardly used anymore, for tracking puposes. When you want to apply it system wide enter ||*$ping in import ABP Rules.
Pings are used to pre-load stuff nowadays (when you watch a movie, pinging fragments are used by the CDN or Gstatic to prefetch them).

10.7 has more fingerprint signals (now also include the whole bunch Tracking Pings, 1x1 and 3x3 tracking pixels and 1x1 frames plus Tracking Beacons
Advantage of tracking pixels, frames and beacons for advertising servers over pings is you are more easily tagged.

View attachment 301281

Yes, 1p-frames can often cause privacy issues as well.
Here's another reason why I use,you know,to get rid of them.;)
 
Forgot to mention, besides the additional tracking signals in Fingerprint protection, I rationalized the filtering system

As you know in most generic filters I cut off websites not in the Top 1 million most visited websites and websited outside the TLD scope (filtering out countries where eBD is not distributed). AG Base (which is based on EasyList English) contains
1. English language websites outside the top 1 Million
2. Rules for countries which did not had their own language filter

Additional language filters are automatically enabled based on your browser's language settings.
Because I don't apply the "must be in top 1 mio" for language filters I added an English language filter (split off from AG Base) and moved the language rules of other languages out of AG (e.g. the Albanian language filter). This is why you see a lot more language filters in uBD than in AG or uBOL.

1794289036350.png


Fingerprint protection with (existing) Tracking Beacons and new Tracking pings, 1x1 frames and 1x1 and 3x3 images (tracking pixels)
As you can see these are together with canvas drawing a popular tracking mechanism :-)

1794289614666.png
 
Last edited:
V 10.7.2 => V 10.7.4 (an optimization introduced a bug, corrected)

Completely removed Disconnect (I should have listened to @oldschool, @Morro and @Jan Willy). I found out that in the fingerprinting categorie ordinary trackers (80% of the top 25 tracking networks) were also listed.

I found out because I encountered a rare loss of functionality occasionally. So i decided to run Claude's AI extension to find out what caused it (yes I know Claude knows all my surfing habits now o_O) to find out that Disconnect was the cause. :-(


I also noted that I was not using the timing function and privacy exposure of allowing cookies is minimal when you clear the history at start and block 3P-cookies.
1794379270339.png


I also noted that since enabling Worry-free surfing (which is renamed to seamless surfing) at start is the default, I never used the time options of old Worry-free.
Because privacy impact of allowing (1P) cookies is minimal when you clear them at browser start I offer a choice now when enabling seamless surfing
1794379453304.png


When you accept cookies with seamless surfing, website breakage risk is zero. When you automate the missed cookie prompts with Cookie consent clicker, surfing becomes seamless again, hence the rename of worry-free surfing to seamless surfing.

By selectively combining several filters in a smart way (for instance specific annoyances blocking of both AG and EL or Anti-admiral from several sources) the number of rules stay low while effectiveness is high.
 
Last edited:
Pushed Versison 10.7.5 with popup and popunder options only done differently :-) through scriptlets


When popups are blocked in AG_Base, you get a warning like this
1794574751105.png


uBD automatically creates a dynamic (session rule) to hide this silently for that (target - tries to open) URL, so it won´t be shown again

In ABP-Import is explained how you can write those rules for yourself: the first two are for popups, the third for popunders.

1794574906694.png
 
Last edited:
This shows it is a real cross-over (according to my not so objective opinion, the best of both worlds).


1794727511471.png


All code is adopted using these programming priniciples: uBol-stripped/Engineering_Manual_v13.pdf at main · Kees1958/uBol-stripped
These are @oldschool practices applied to a modern Chrome extension platform (forgive me the tongue-in-cheek use of your nickname).

The two large (over 1000 lines of code) uBO modules with around 70 percent of the uBO-code, have been restructured in logical functions and improved security wise with state & lifecycle monitors and error handling added, but they are kept as a monolith (in my coding time considered bad programming practice) and one monolith with just under 50% of the original code is broken down in separate function calls also.

So the 53 JS-modules are three large ones and around 50 scriptlets. The 6 handported scriptlets are UNSAFE scriptlets, made SAFE (no raw JS or large parameters accepted)
1794726997871.png
 
10.7.12 Completed refactor also did a filter update.

I know it is the second or third completed refactoring🫣 , but new insights and other changes allowed for further improvements like verbatim changes using other coding mechanism, moving code around and grouping it in functions, use bit-for-bit comparison of output when slicing the change in smaller steps (hence the jump from 10.7.7 to 10.7.12)

This thread shows I put much effort on bringing professional coding practices (70% of AG team, 30% my own oldschool): the point is made in these 3 posts
a. Trying to apply (corporate standards) to uBOL: Best practices for Chrome extension development | MalwareTips
b. Using old school ¨forbidden to use" practices: Best practices for Chrome extension development | MalwareTips
c. Benefits of my own best practices additions: Best practices for Chrome extension development | MalwareTips

That said I have to say that uBO/uBOL code is battle tested and prestine (although things can be done better, AI found only a dozen problems of which 4 were serious). I noticed (reading the release info of uBOL) that this got the attention and I can see some weaknesses being structurally improved in uBOL (also the IMO dangereous json-edit family of scriptlets is being hardened).
 
Last edited:
10.7.14 pushed to webstore because of @lokamoka820 great find (y)

Although uBD is immune to this attack
see (Universal XSS in uBlock Origin from website-driven element picker | MalwareTips

I had not thought about this angle of attack, therefore I added the same checks and balances to settings import/restore. Again @lokamoka820 thanks for thinking about using an extensions features as an entry point.

I asumed settings were save by the user and all settings (and rules) are checked and i wrongly assumed that when a user restores these settings/rules the rules are always limited by the restrictions uBD applies to rules. Due to Sandbox protections in Chrome it is much harder for an attacker to access your data on disk, it is still a possible entry point. Therefore all checks and balances are now also applied to imports and restores of settings/rules.

Also tightened the Content Security Policies of the screens used by the power tools
see Universal XSS in uBlock Origin from website-driven element picker | MalwareTips

Plus filter lists update
 
Last edited:

MalwareTips community

Join the discussion

Create a free account to reply to this thread, ask your own questions and get help from the community.

  • Reply and ask questions
  • Get alerts when someone answers
  • Free malware removal help

Join 75,691 members who help each other for free, since 2010.

Create free account
or continue with

Recently browsing

Members and guests who viewed this thread in the last 5 minutes

Back
Top