

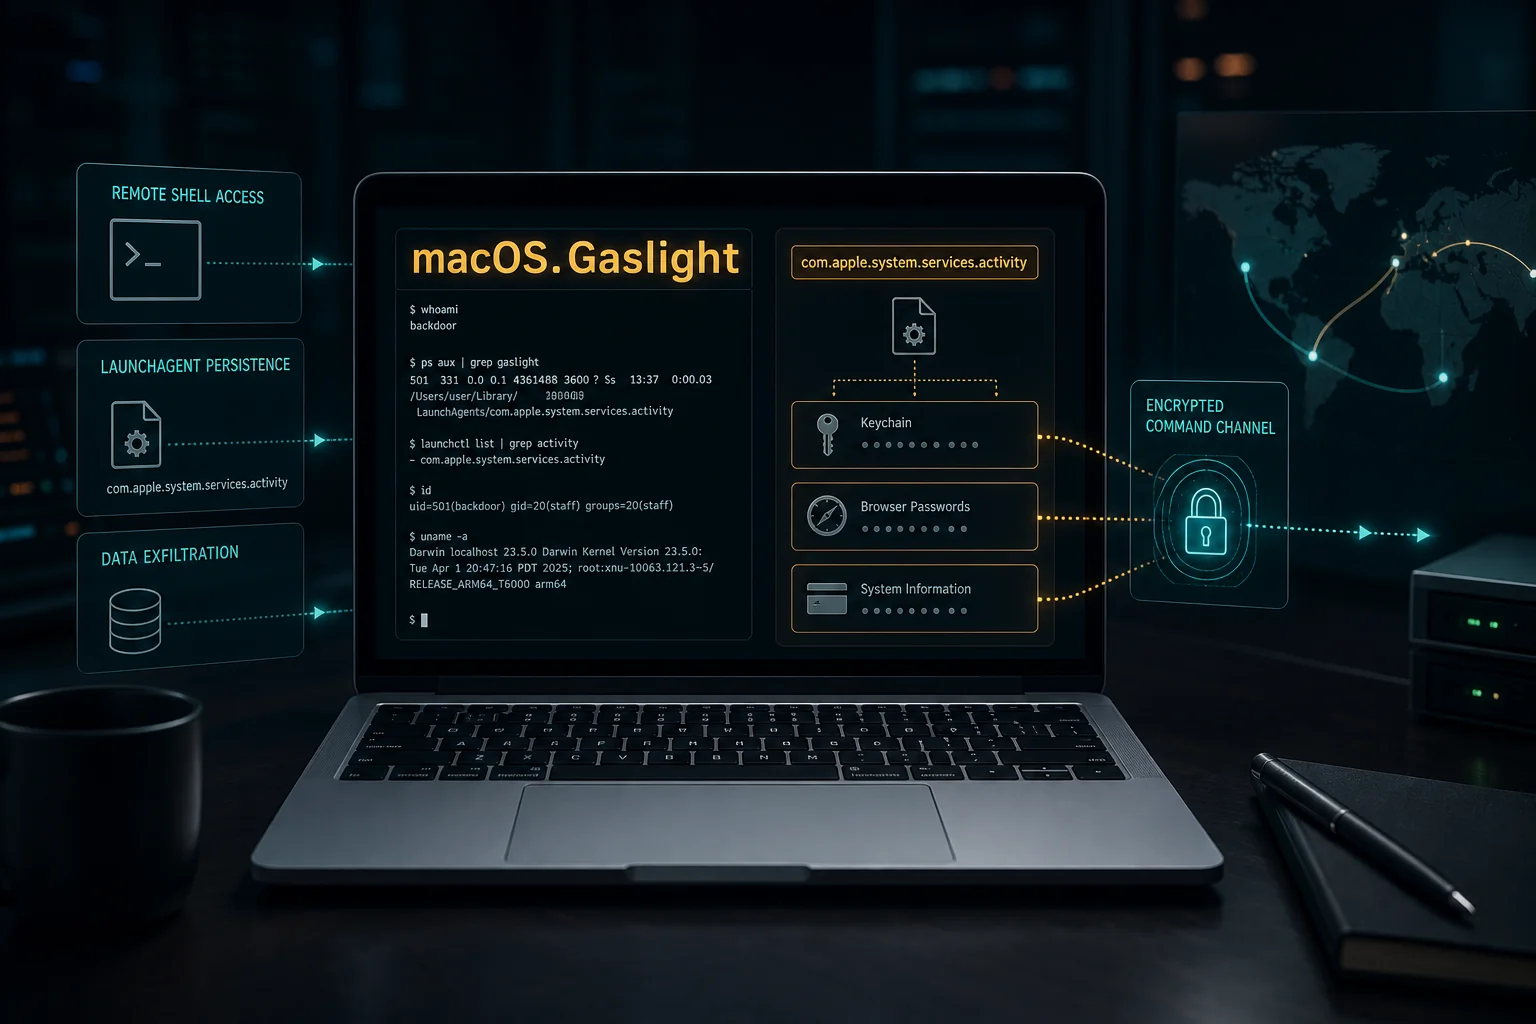
macOS.Gaslight Backdoor: How This Mac Malware Steals Passwords and Takes Control
macOS.Gaslight is a stealthy Rust backdoor that steals browser passwords and Keychain data while giving attackers remote control of a Mac.
Author · 46,781 articles · page 128
Thomas Orsolya investigates casino, shopping and other online scams as an editor at MalwareTips. Before joining MalwareTips, Thomas worked in public institutions on combating misleading advertising and on consumer protection.
macOS.Gaslight is a stealthy Rust backdoor that steals browser passwords and Keychain data while giving attackers remote control of a Mac.
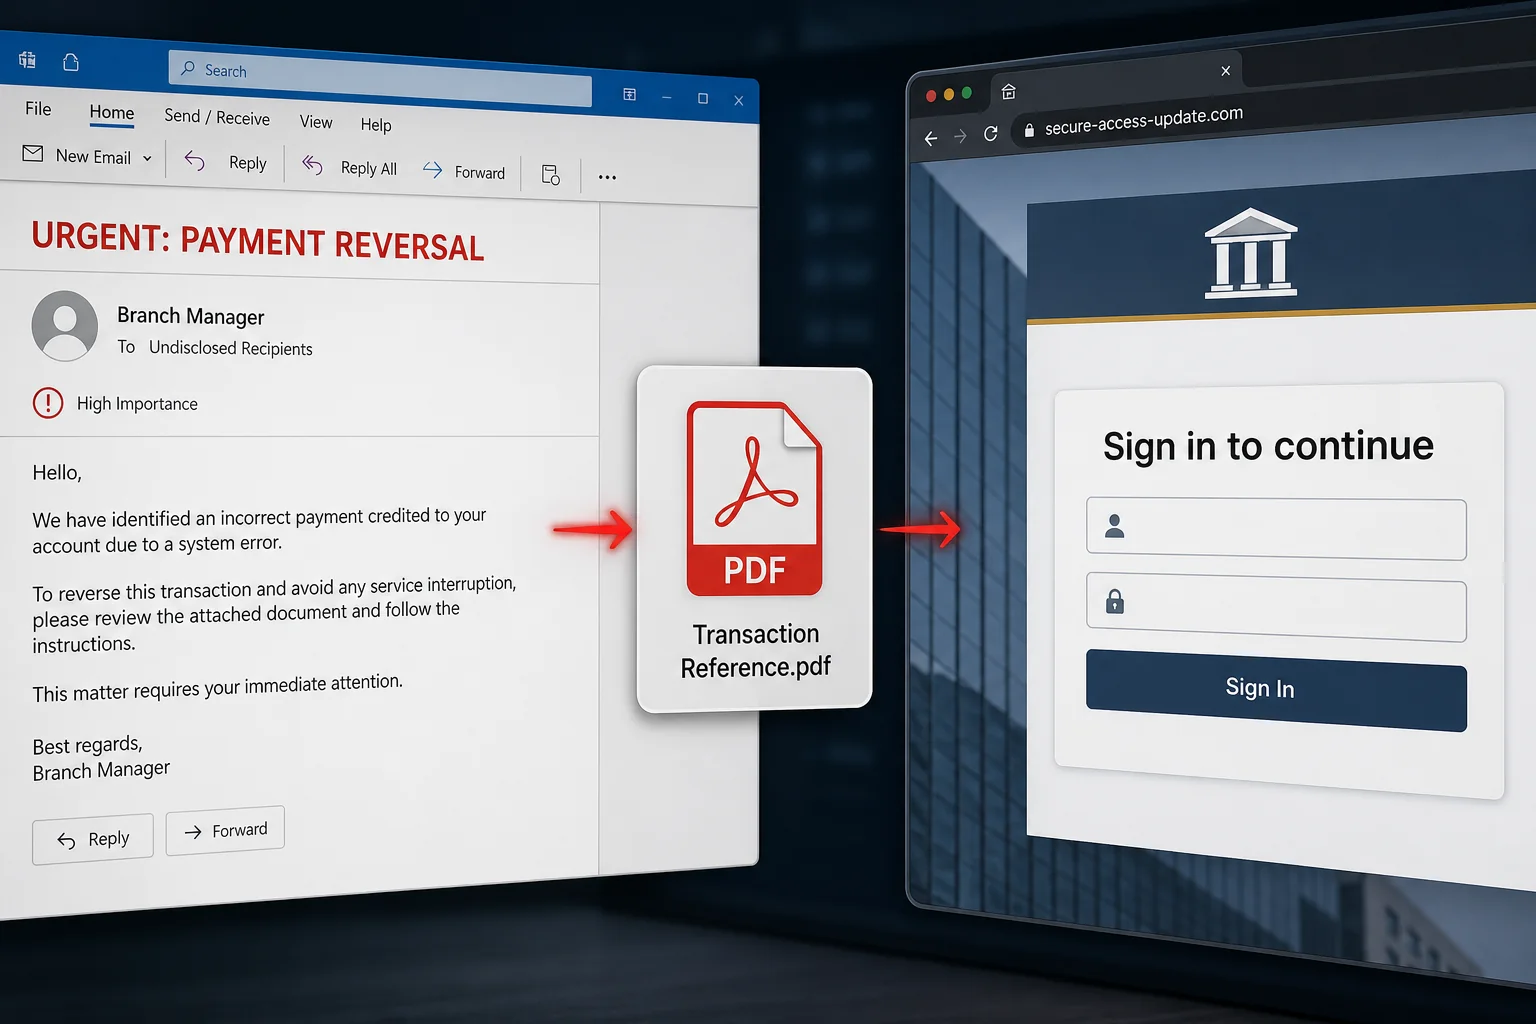
The Misdirected Payment email scam impersonates a bank manager and uses an urgent PDF to send victims to a fake login page. Learn the warning signs.
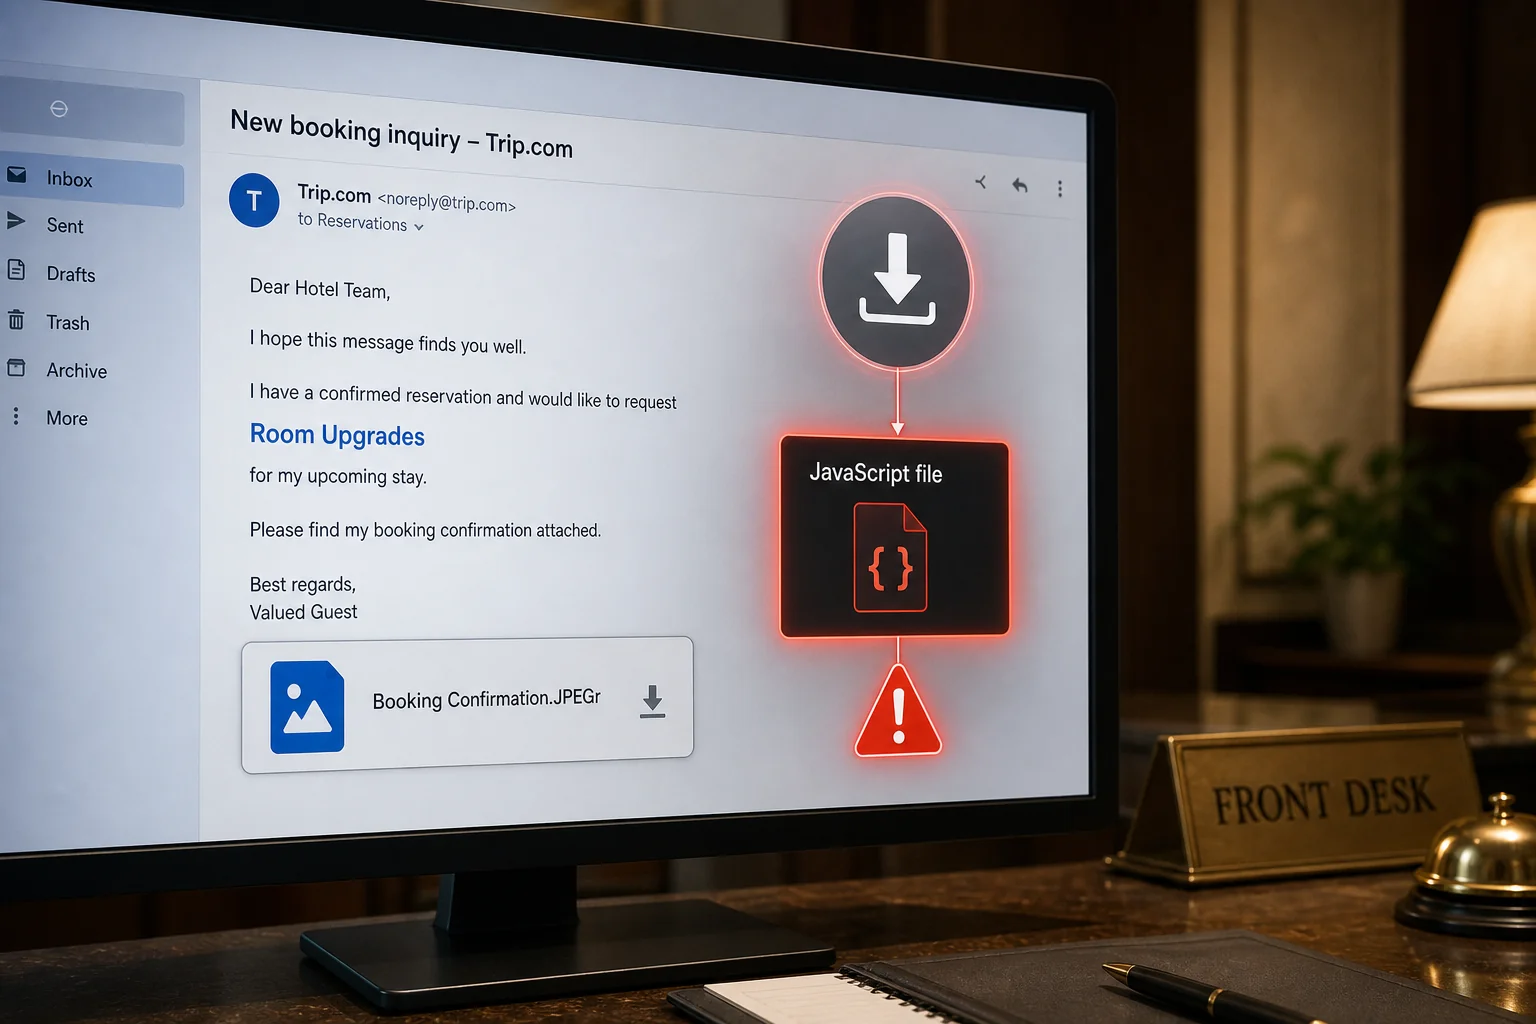
A fake Trip.com guest inquiry targets hotels with a Booking Confirmation.JPEGr link that downloads malicious JavaScript. Learn how the attack works.
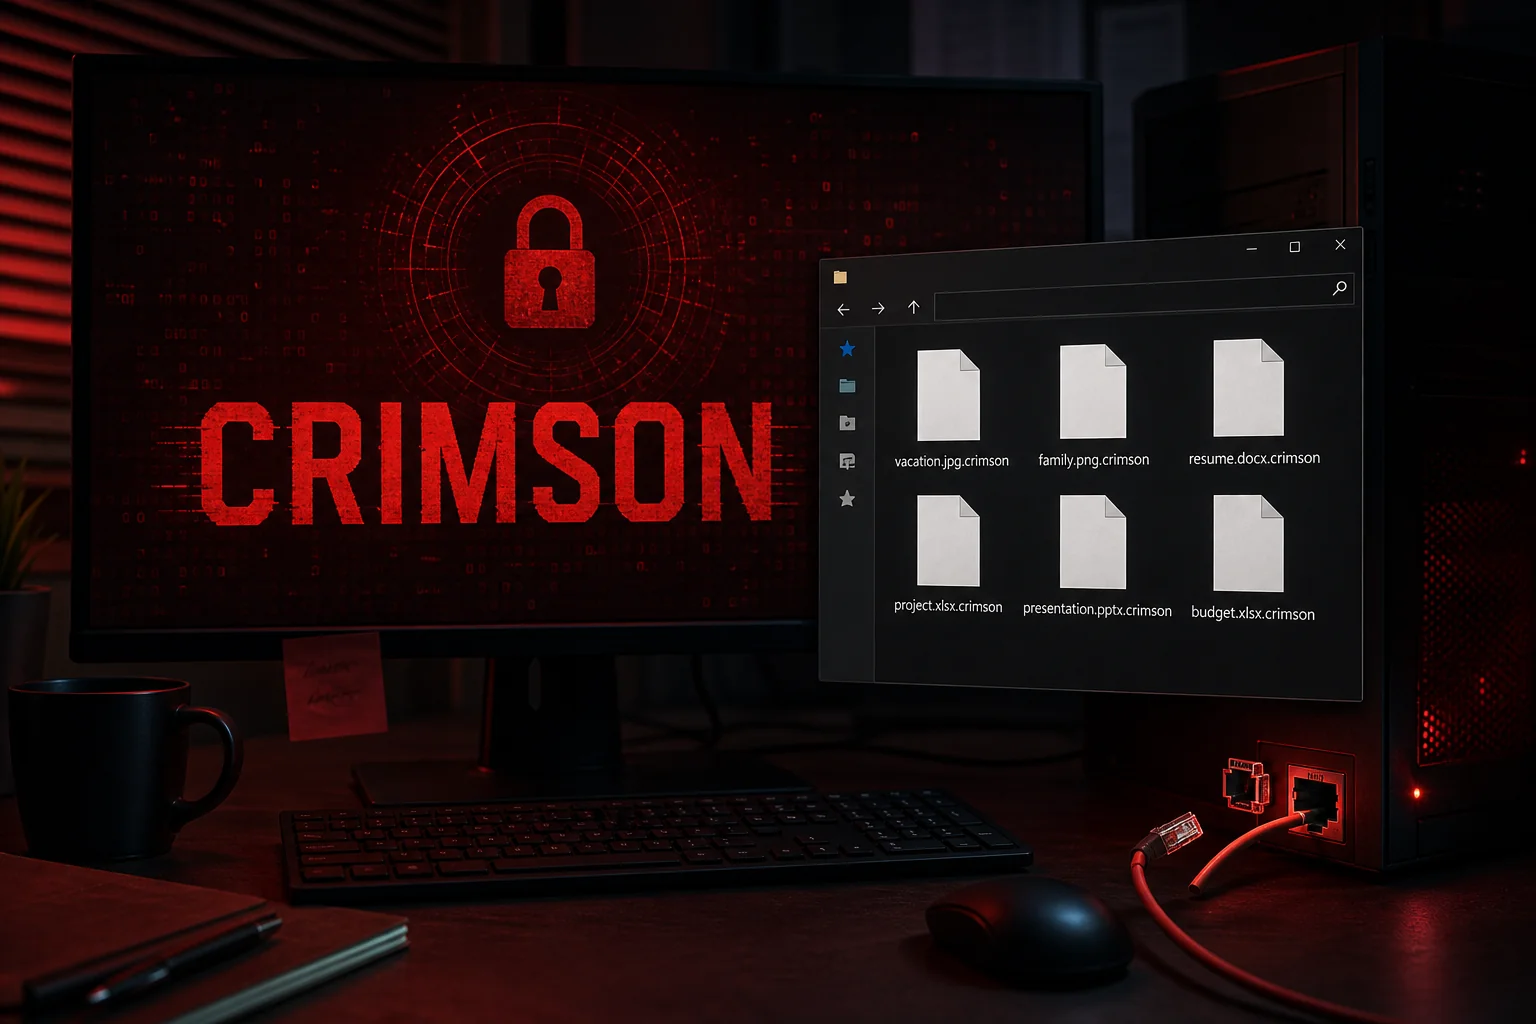
CRIMSON ransomware encrypts Windows files, adds the .crimson extension and displays a full-screen ransom demand. Learn how to contain and remove it safely.
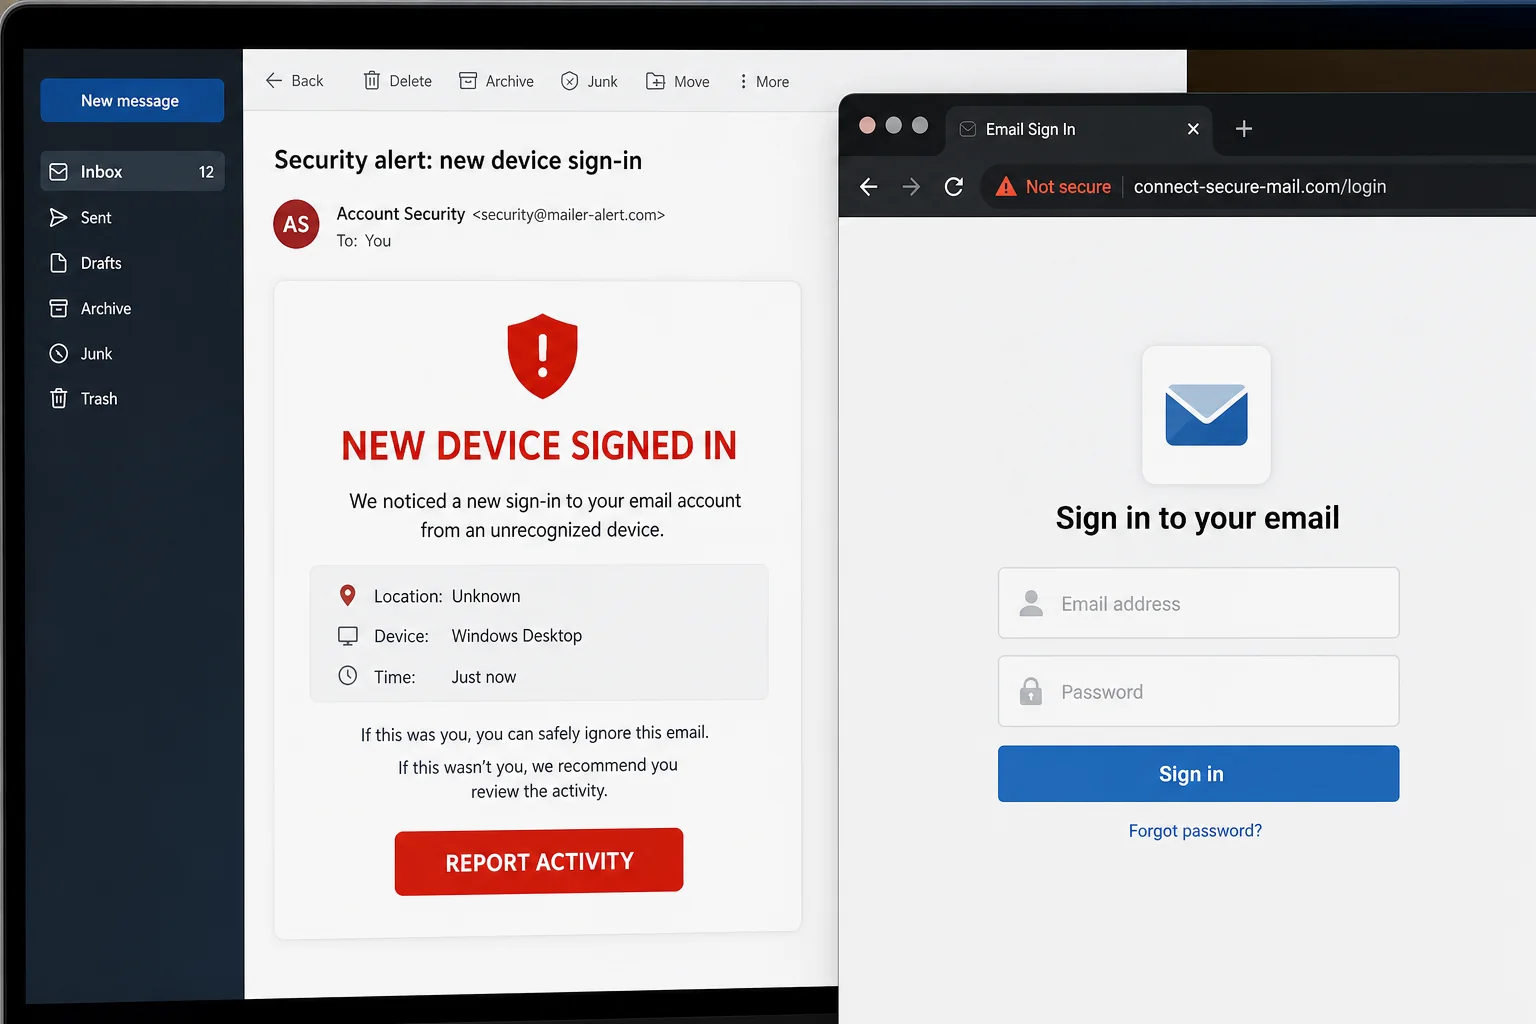
A fake New Device Signed In email sends recipients to a counterfeit login page hosted on cloud storage. Learn how the phishing alert works and what to do.
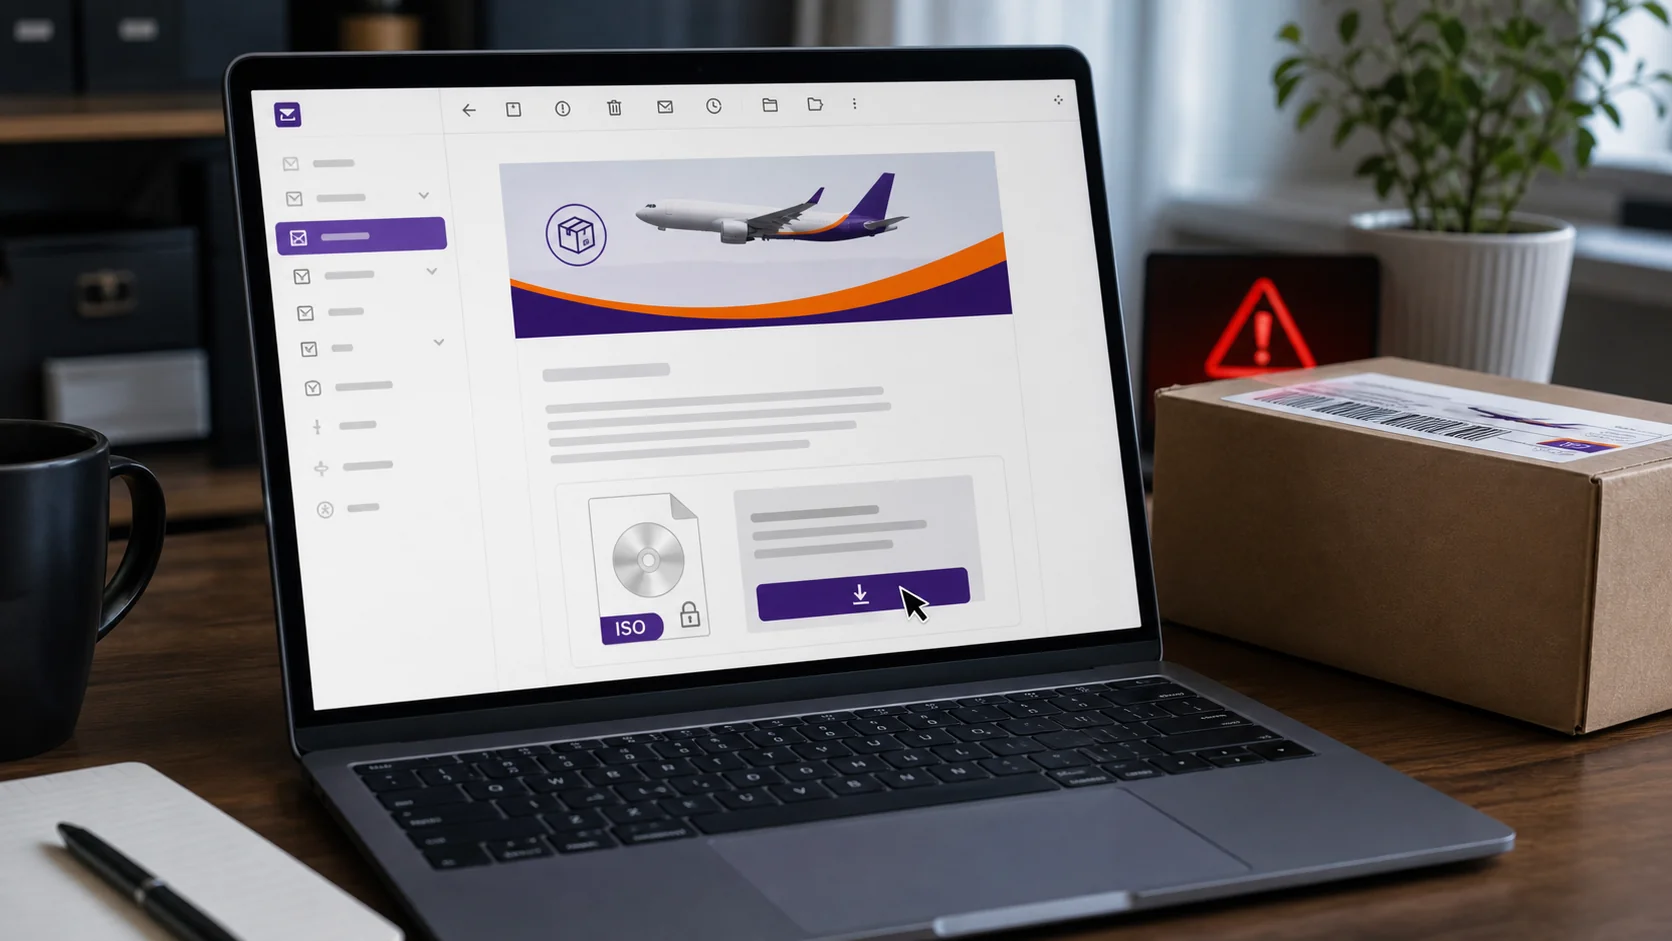
A fake FedEx customs email uses a tracking number, password and ISO download to infect Windows PCs. Learn the warning signs and what to do.
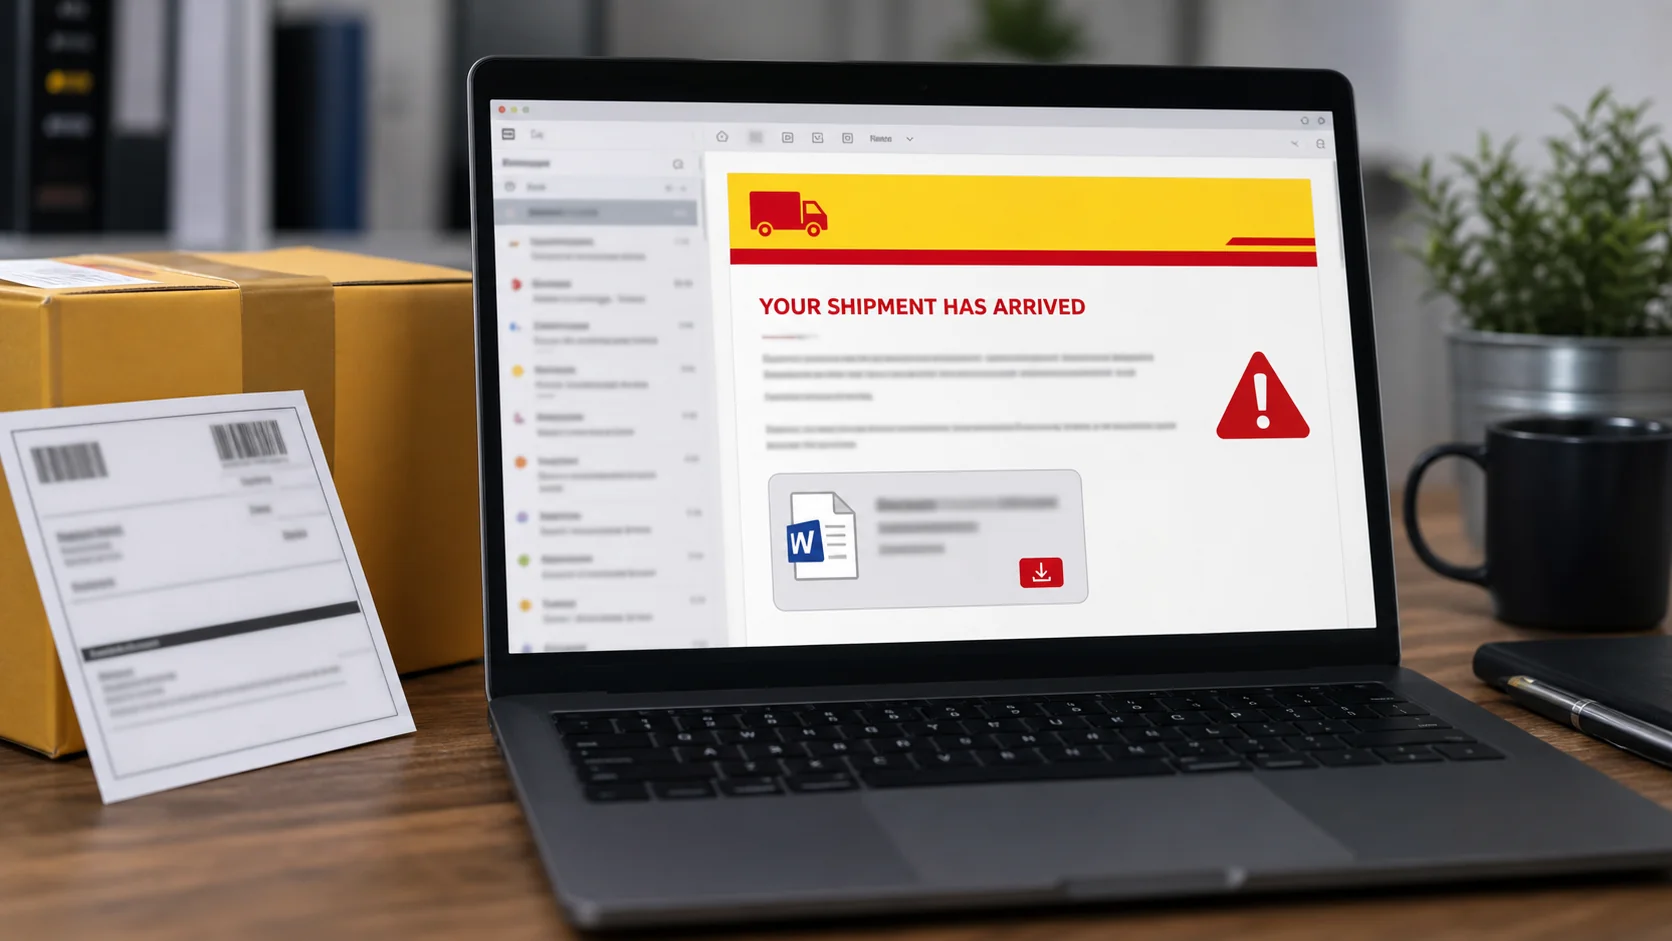
A fake DHL shipment notice uses a waybill number and malicious attachment to infect Windows PCs. See the red flags and cleanup steps.
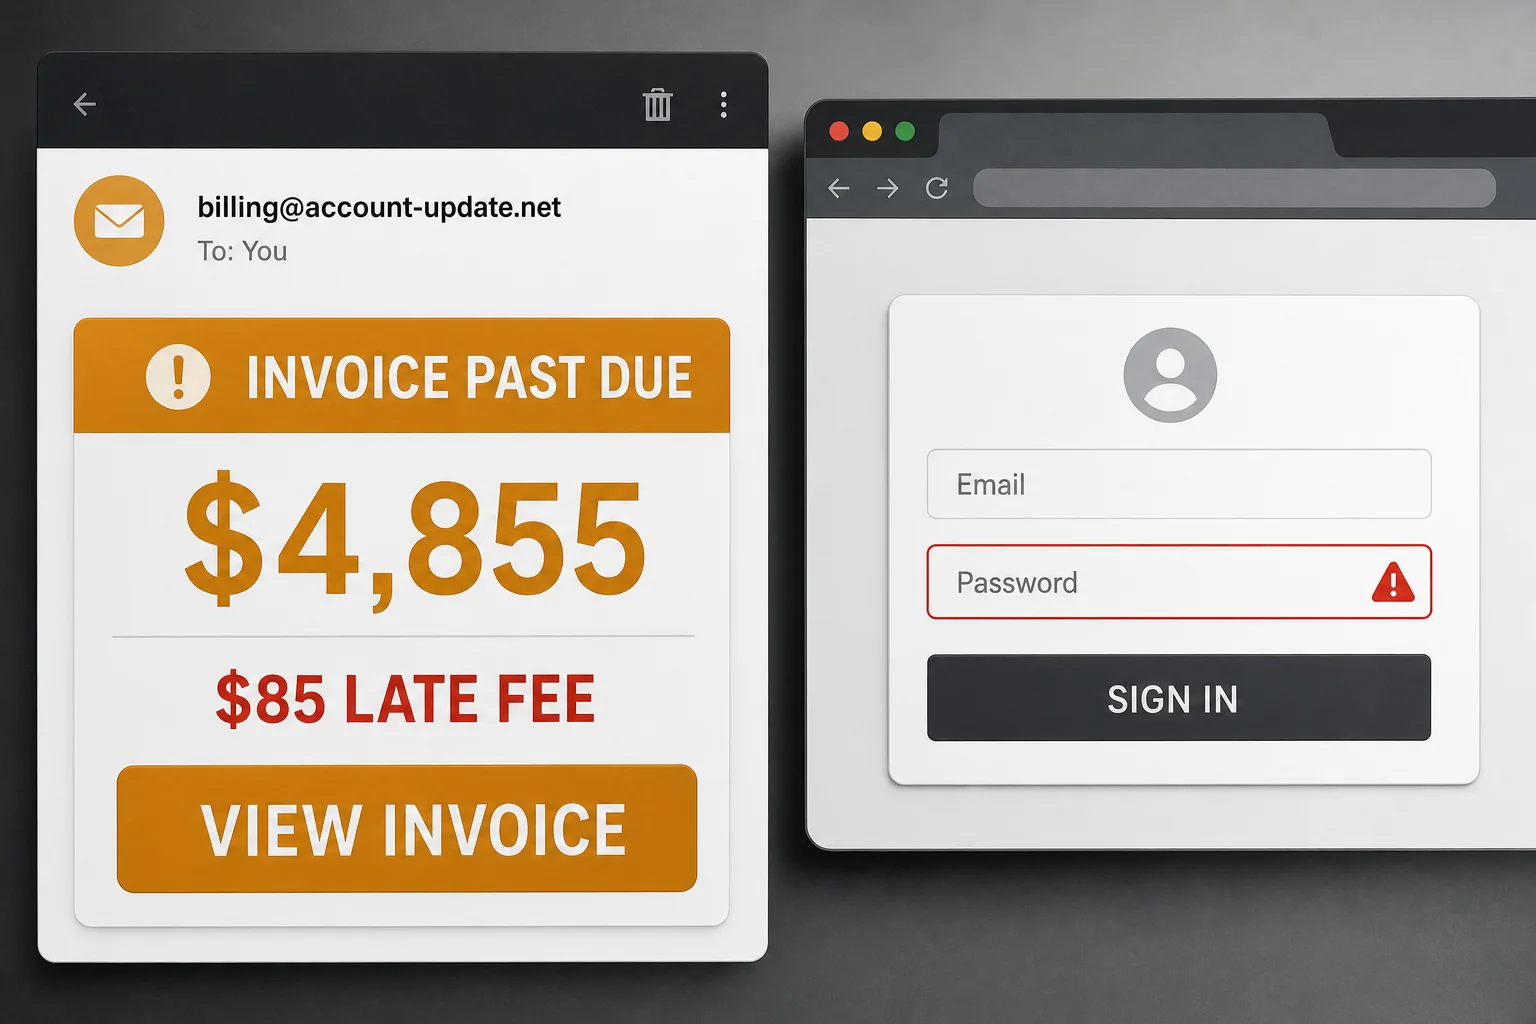
The Invoice Is Past Due scam demands $4,855, threatens an $85 fee and sends victims to a fake email login. Learn how to spot it.
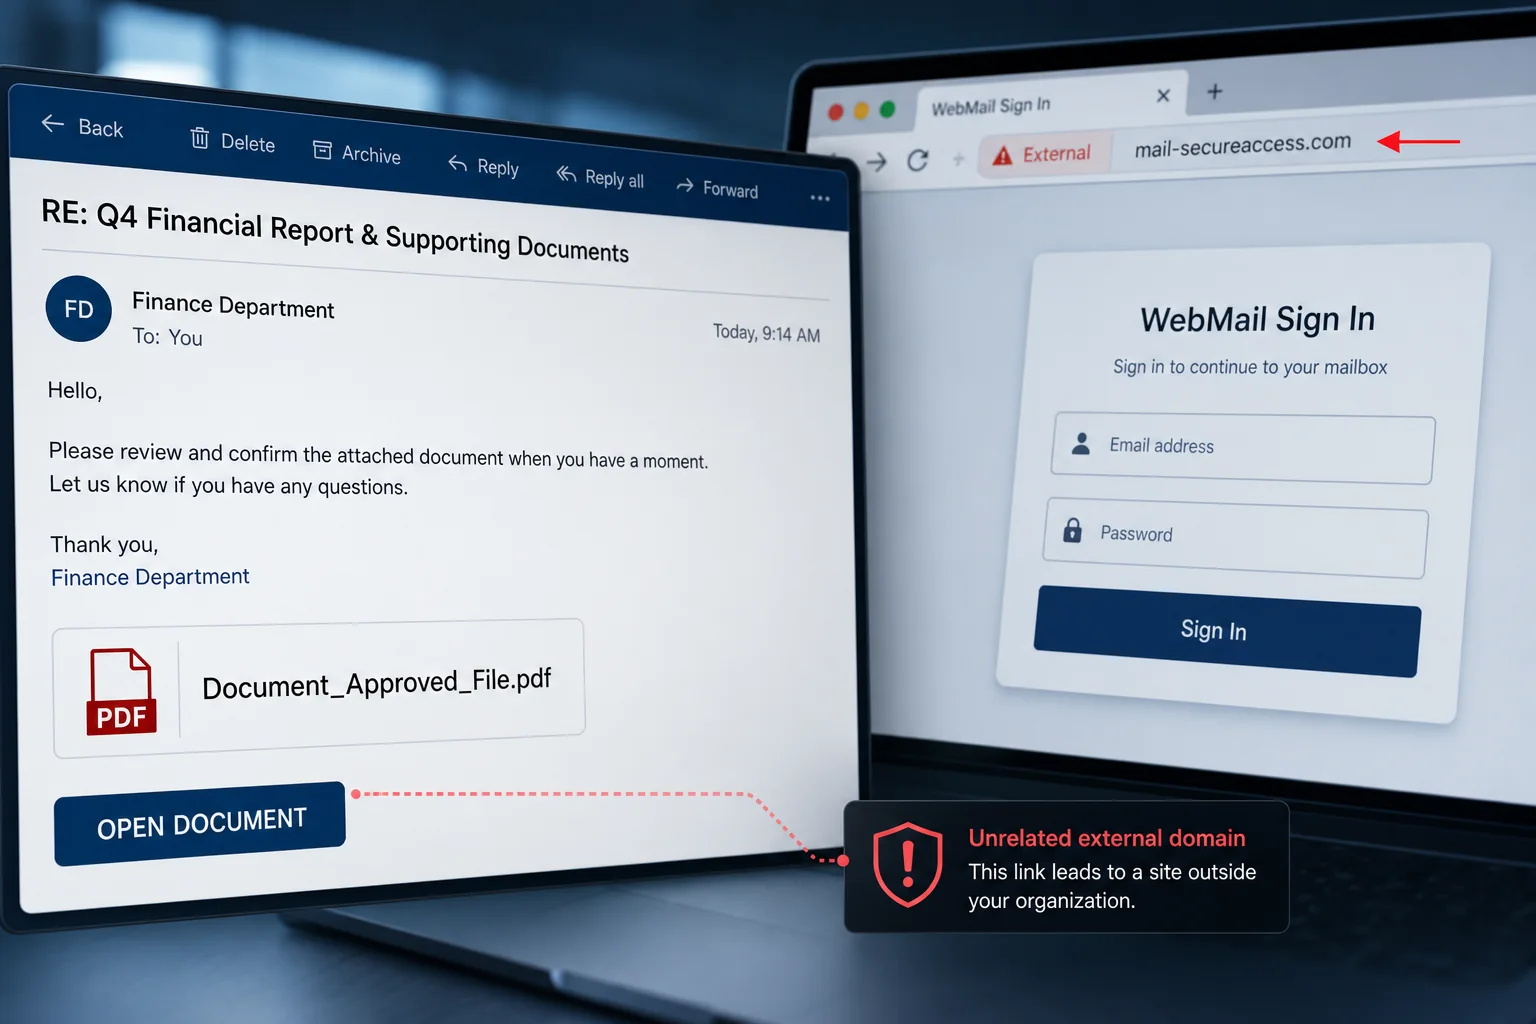
A fake Finance Department file-share email uses Document_Approved_File.pdf to send employees to a counterfeit webmail login.
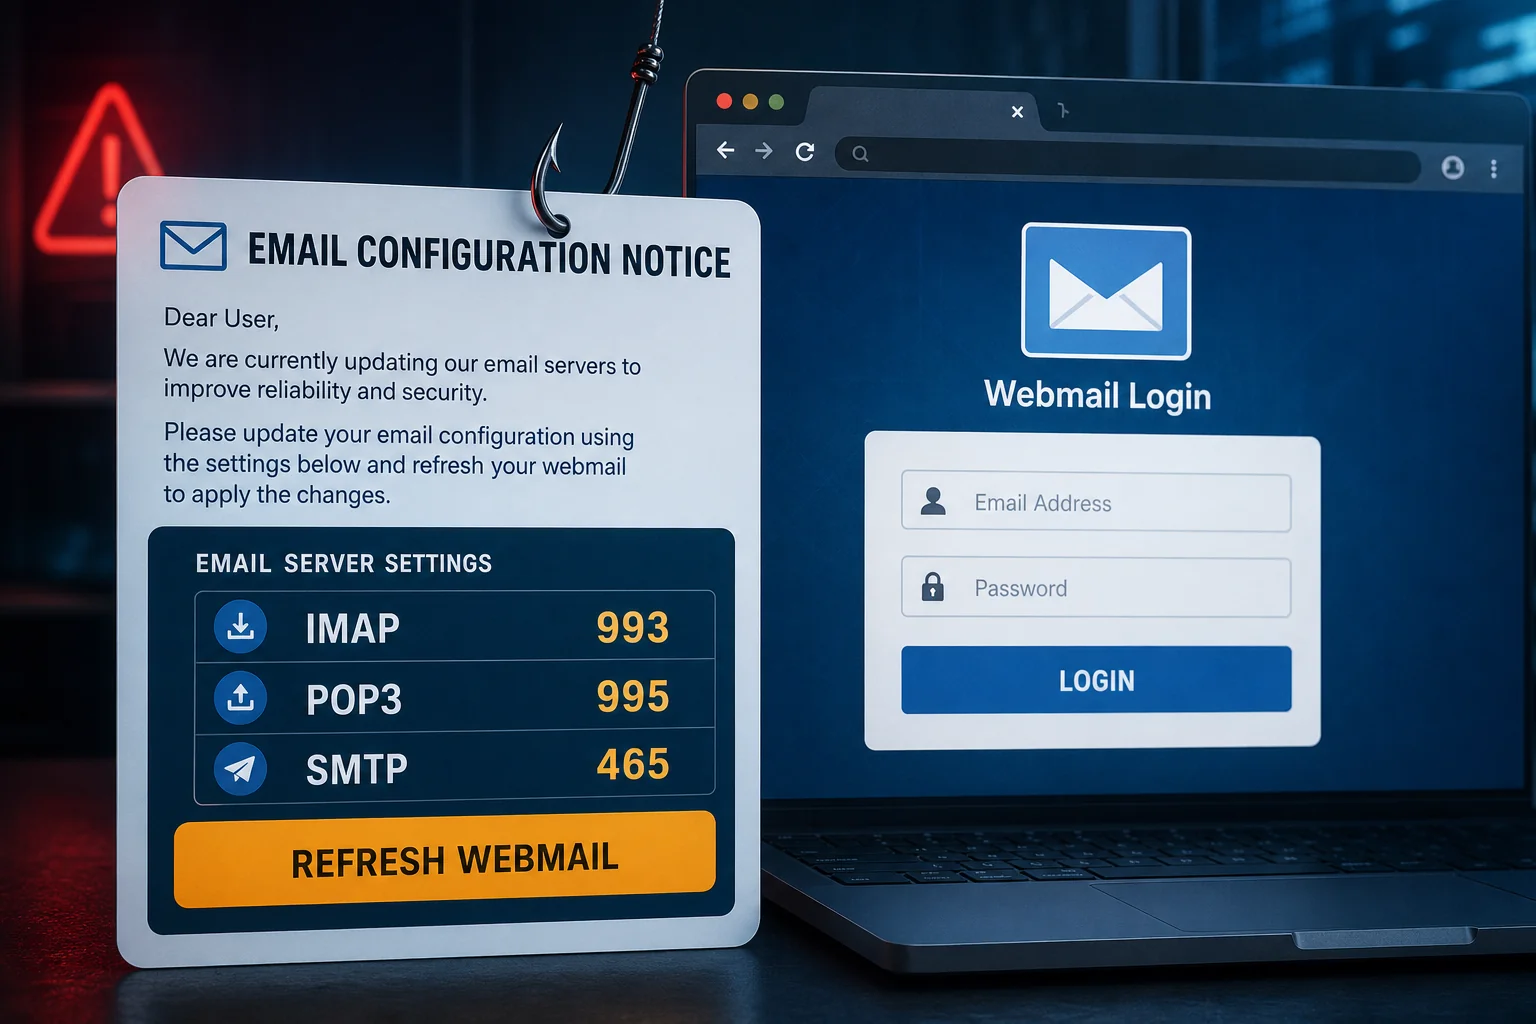
The Email Configuration Notice scam lists real IMAP, POP3 and SMTP ports, then uses a fake webmail page to steal your password.
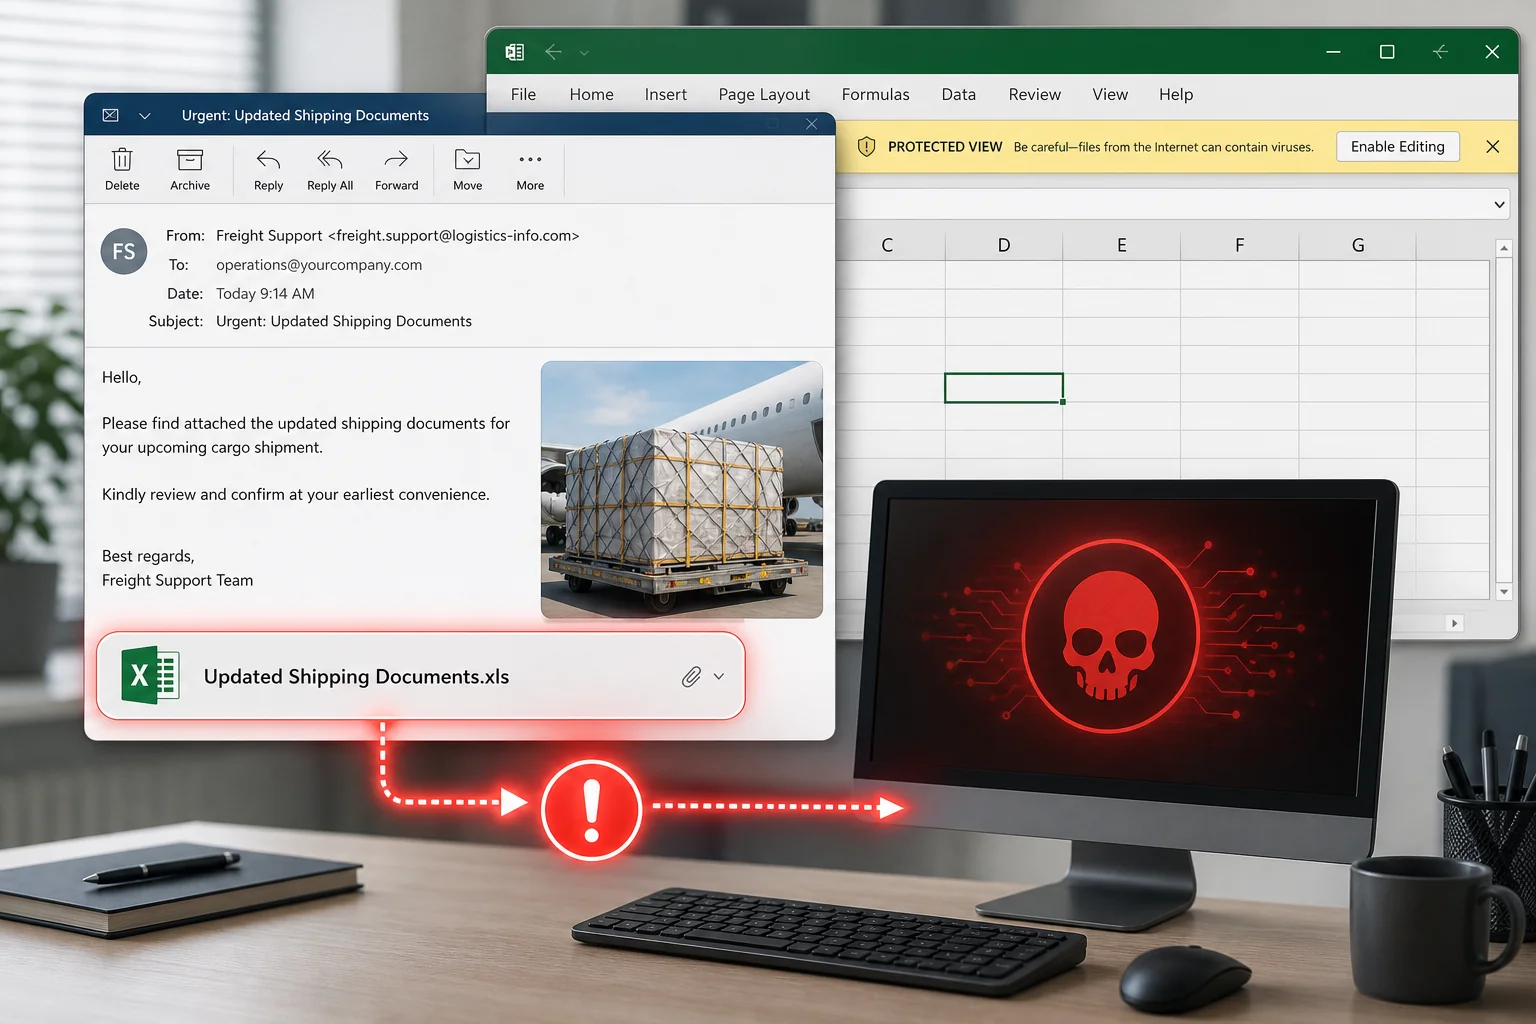
A fake Insoorya cargo email delivers Updated Shipping Documents.xls and uses Excel’s Enable Editing button to run malware. Learn what to do.
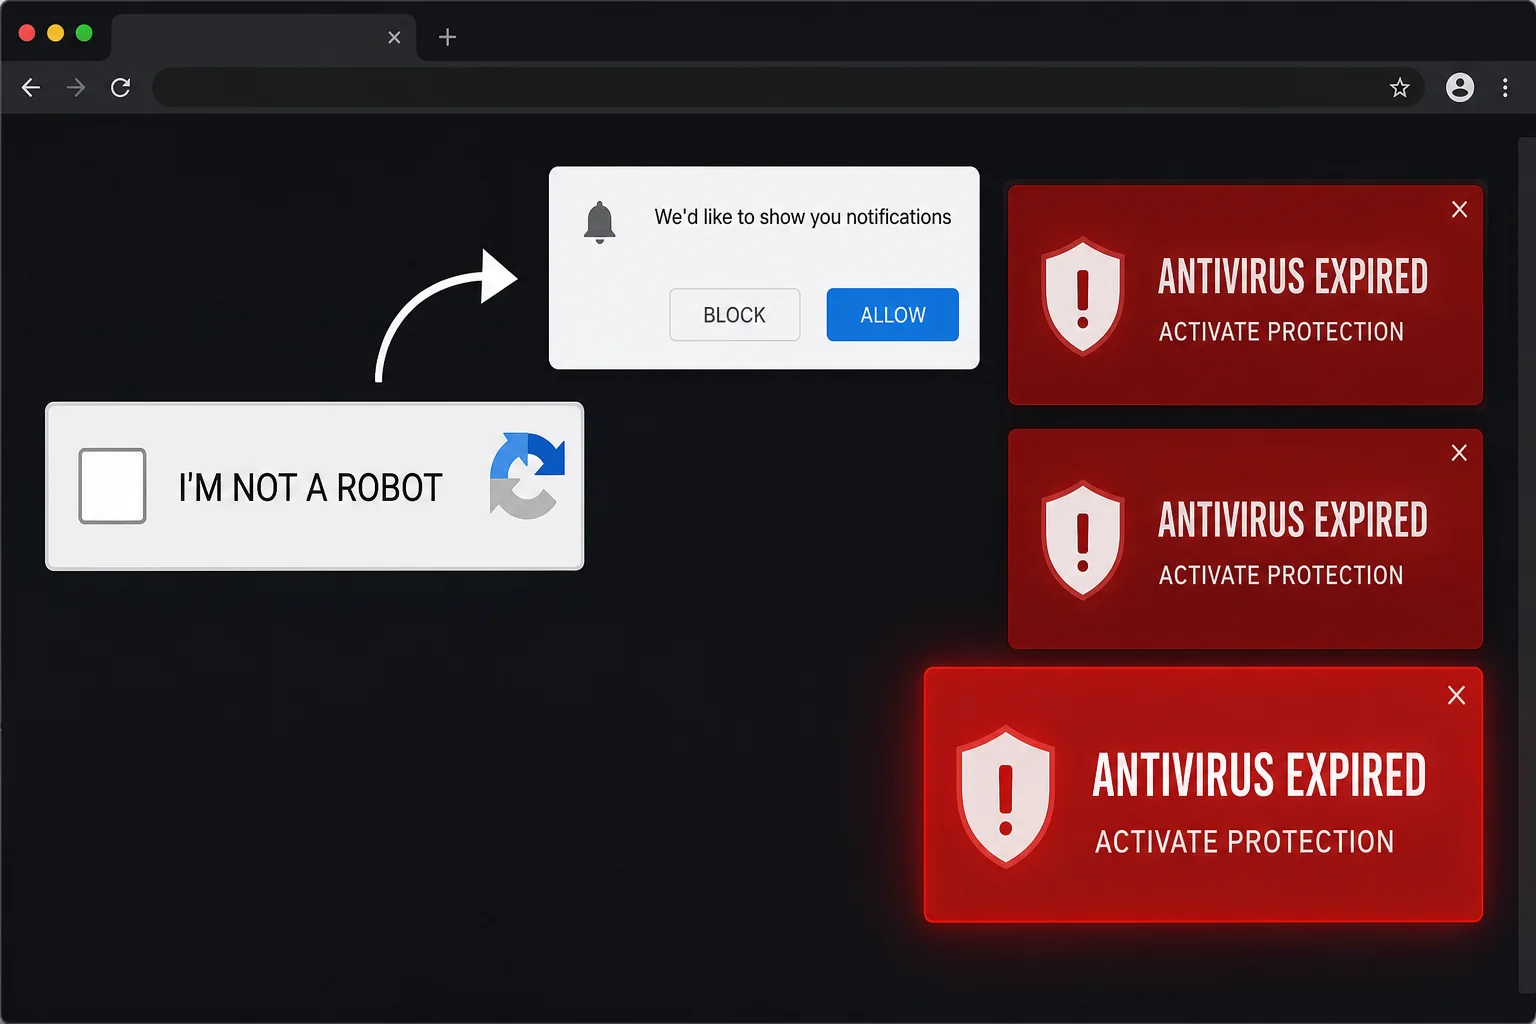
Protectsignalarc.co.in uses a fake CAPTCHA to gain notification permission and flood browsers with deceptive antivirus alerts.
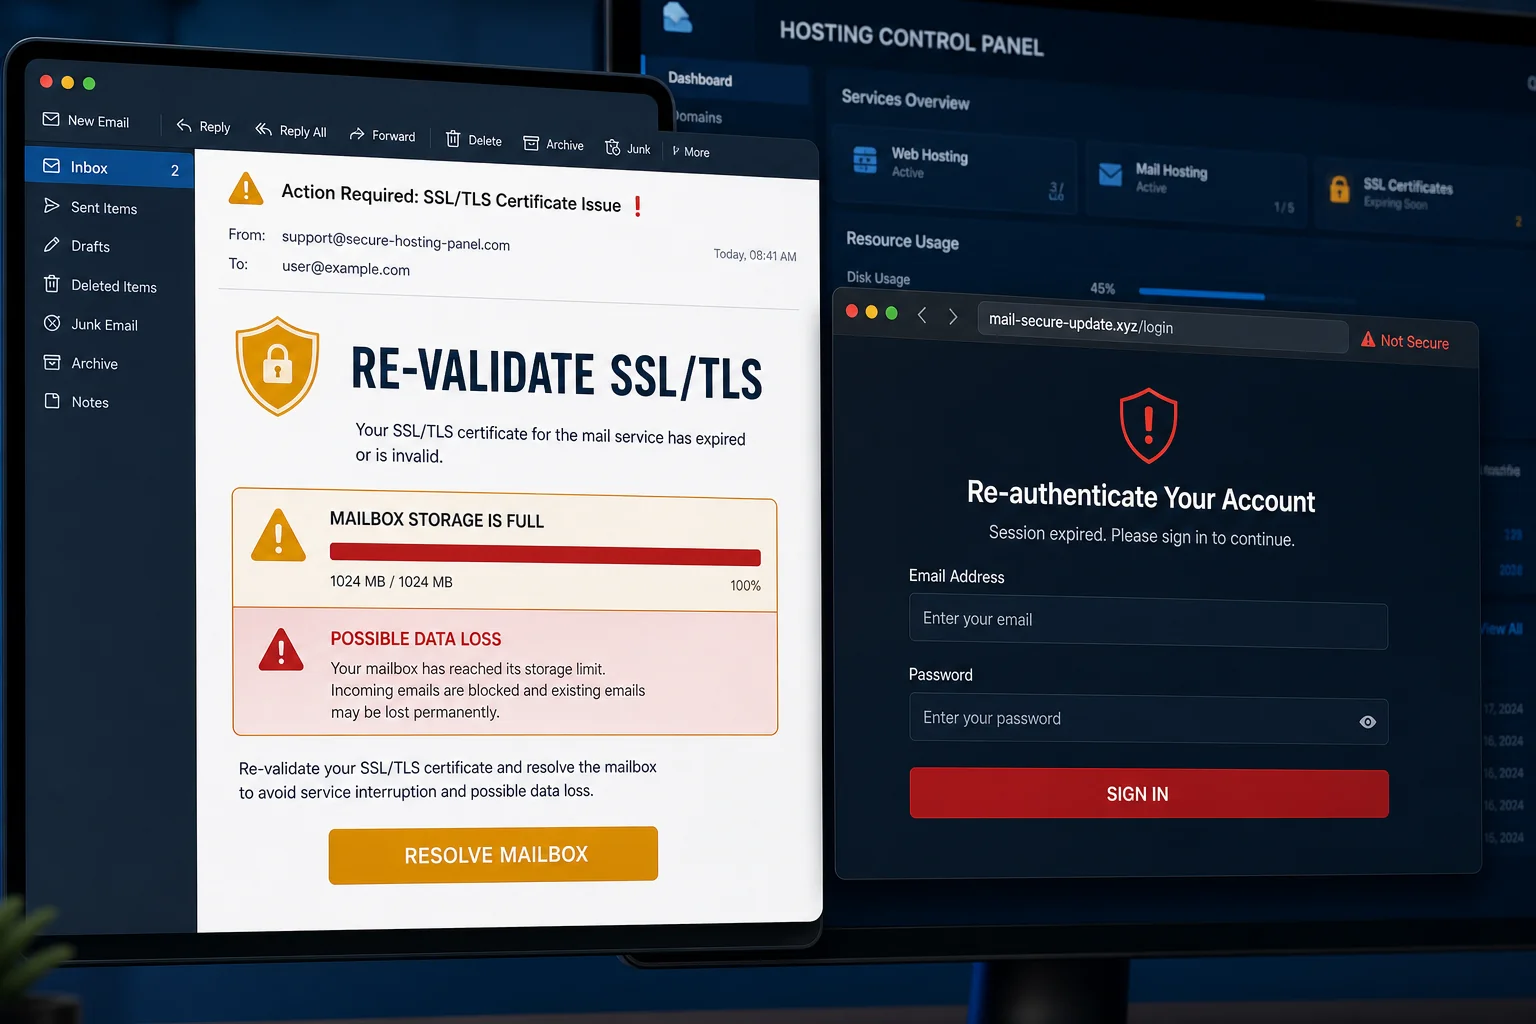
The cPanel Re-validate SSL/TLS email combines a fake full-mailbox warning with a counterfeit login page designed to steal your password.
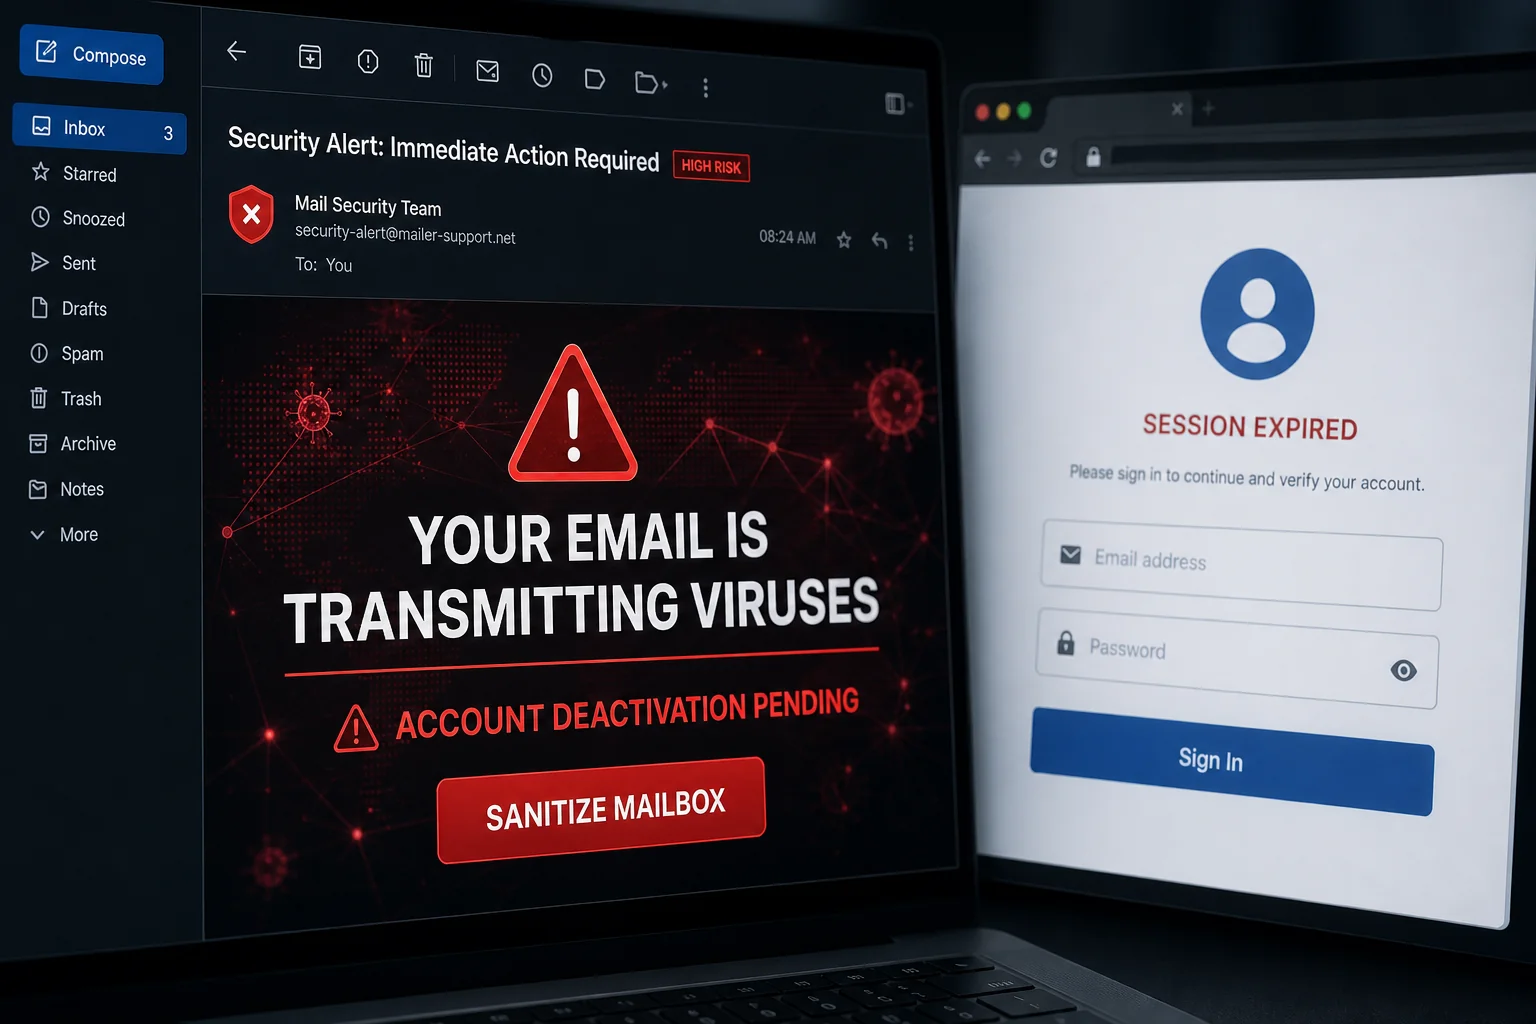
The Email Account Is Transmitting Viruses scam threatens deactivation, then uses a fake mailbox-cleaning page to steal your password.
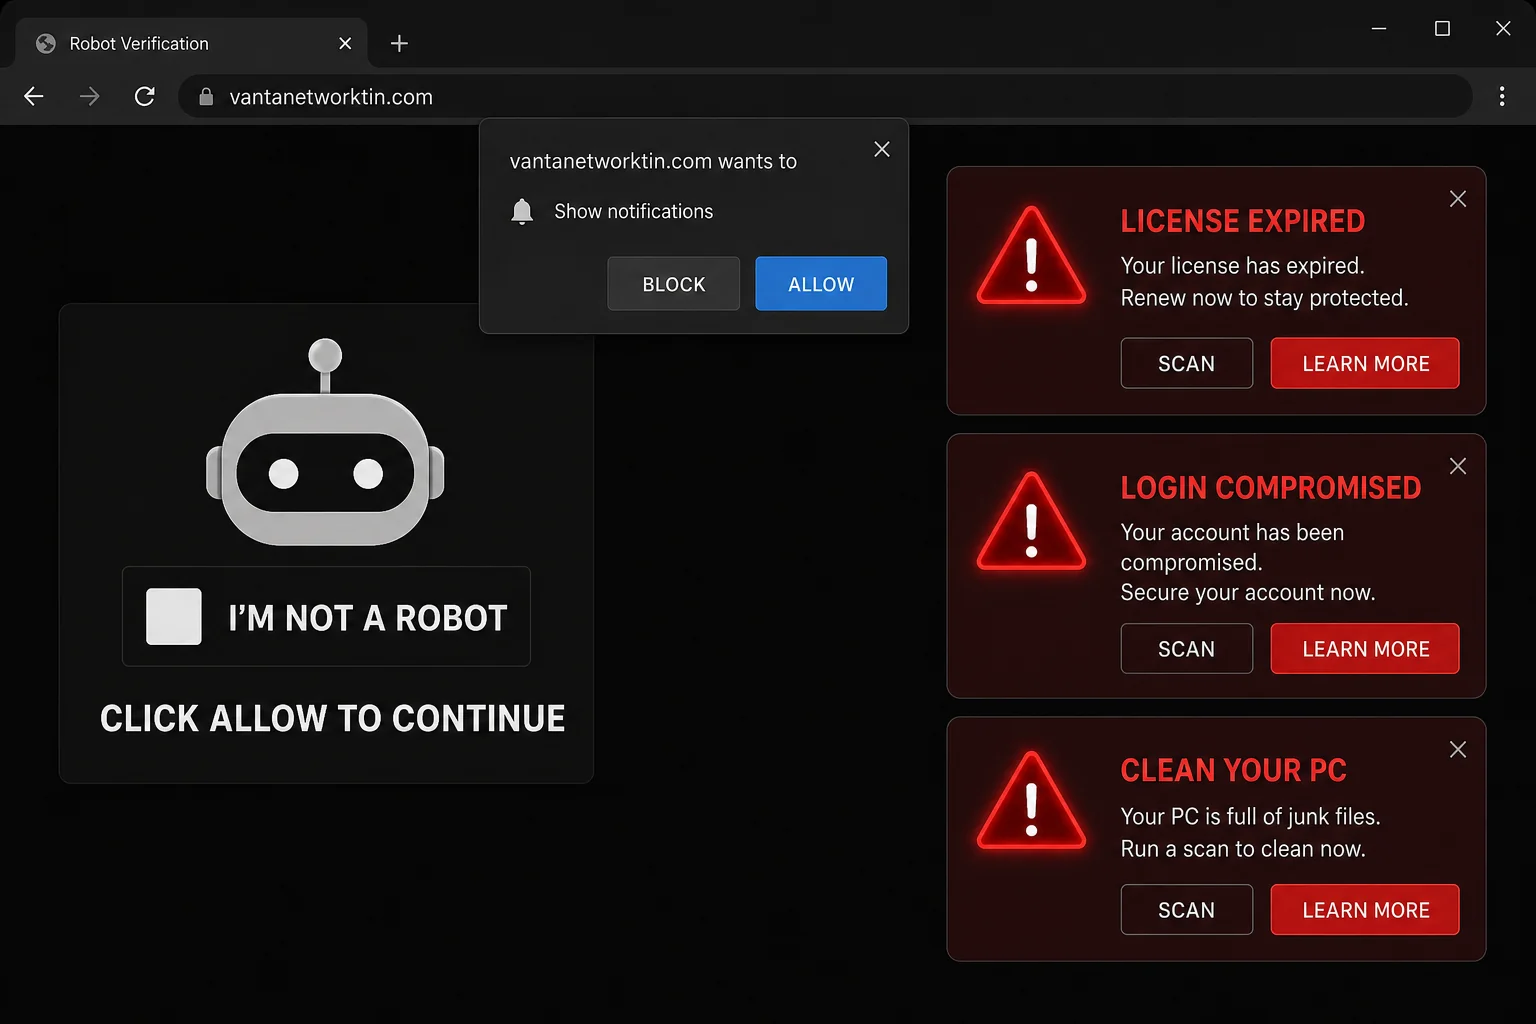
Vantanetworktin.com uses a fake robot check to gain notification permission, then sends fabricated license and account-security alerts.
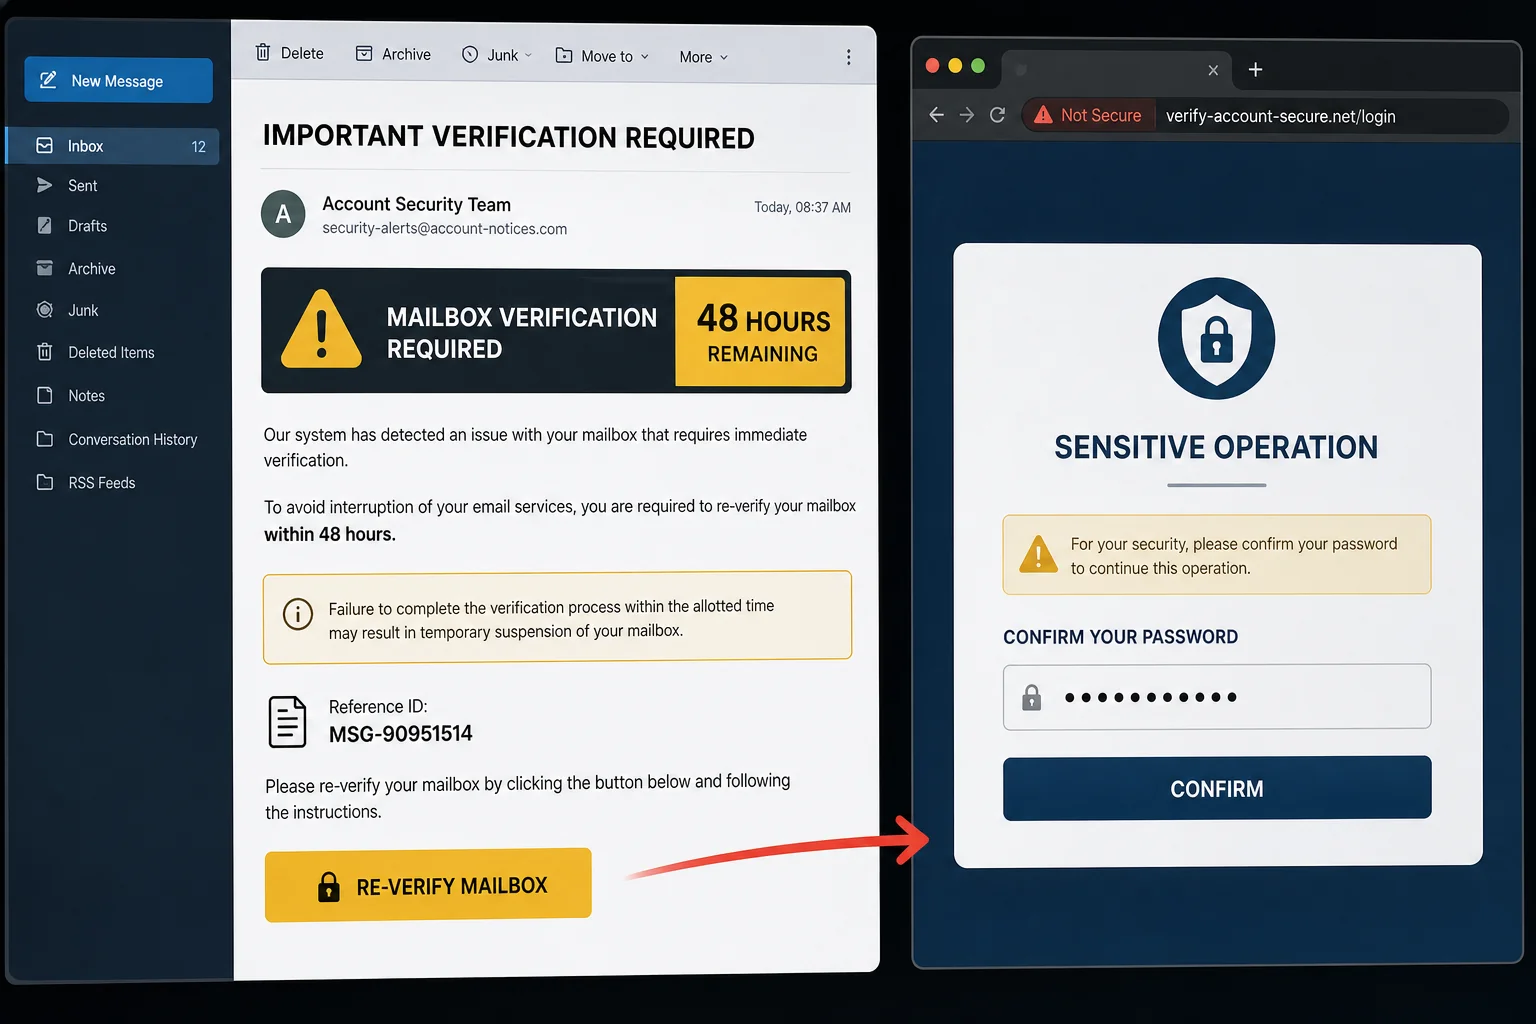
The Email Account Requires Re-Verification scam threatens suspension within 48 hours and directs users to a provider-themed fake login page.
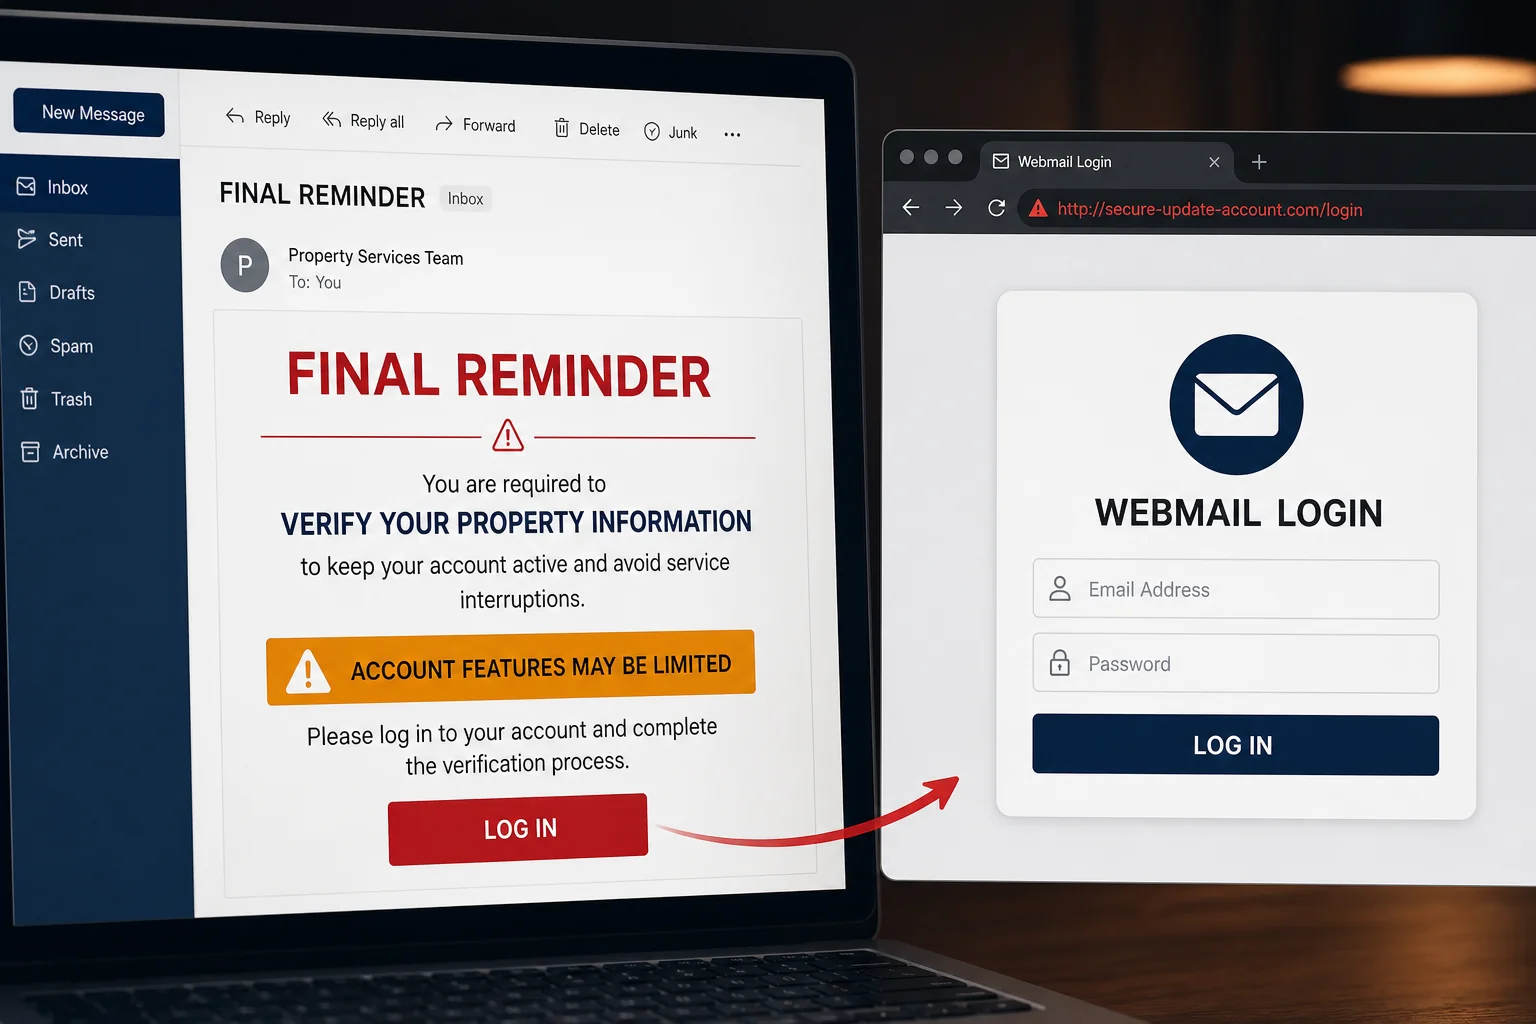
The Verify Your Email Property Information scam uses an odd final reminder and a fake webmail login to steal account credentials.
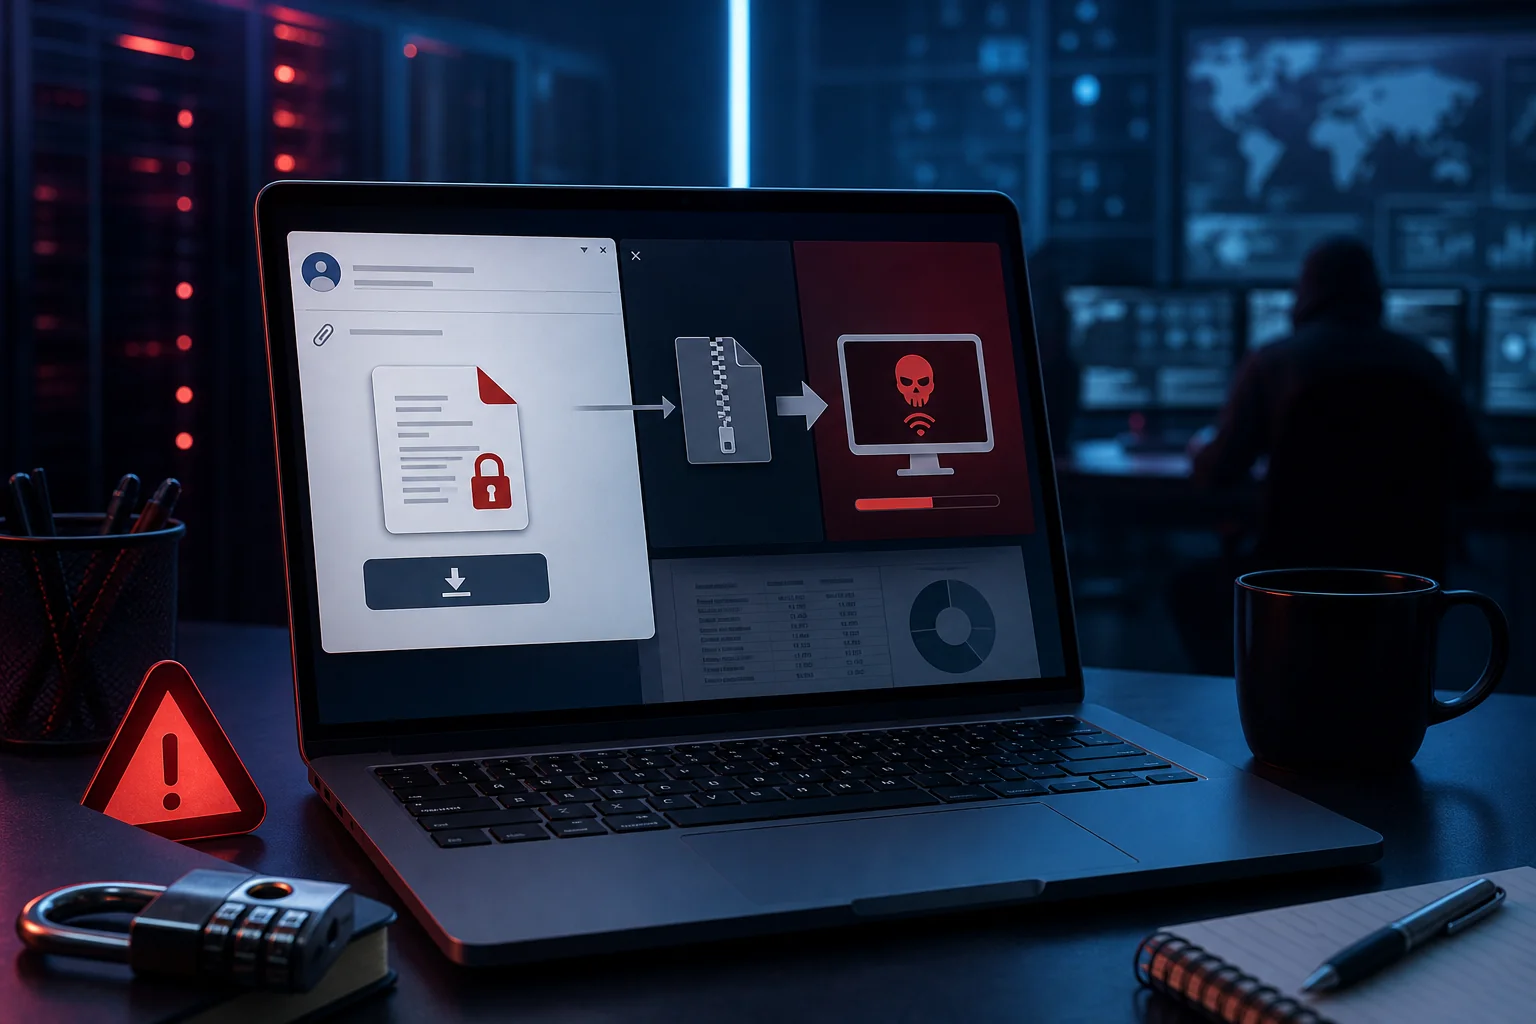
The Finance Department Secure Document email uses a fake PDF portal and reader update to install a remote access trojan on Windows computers.
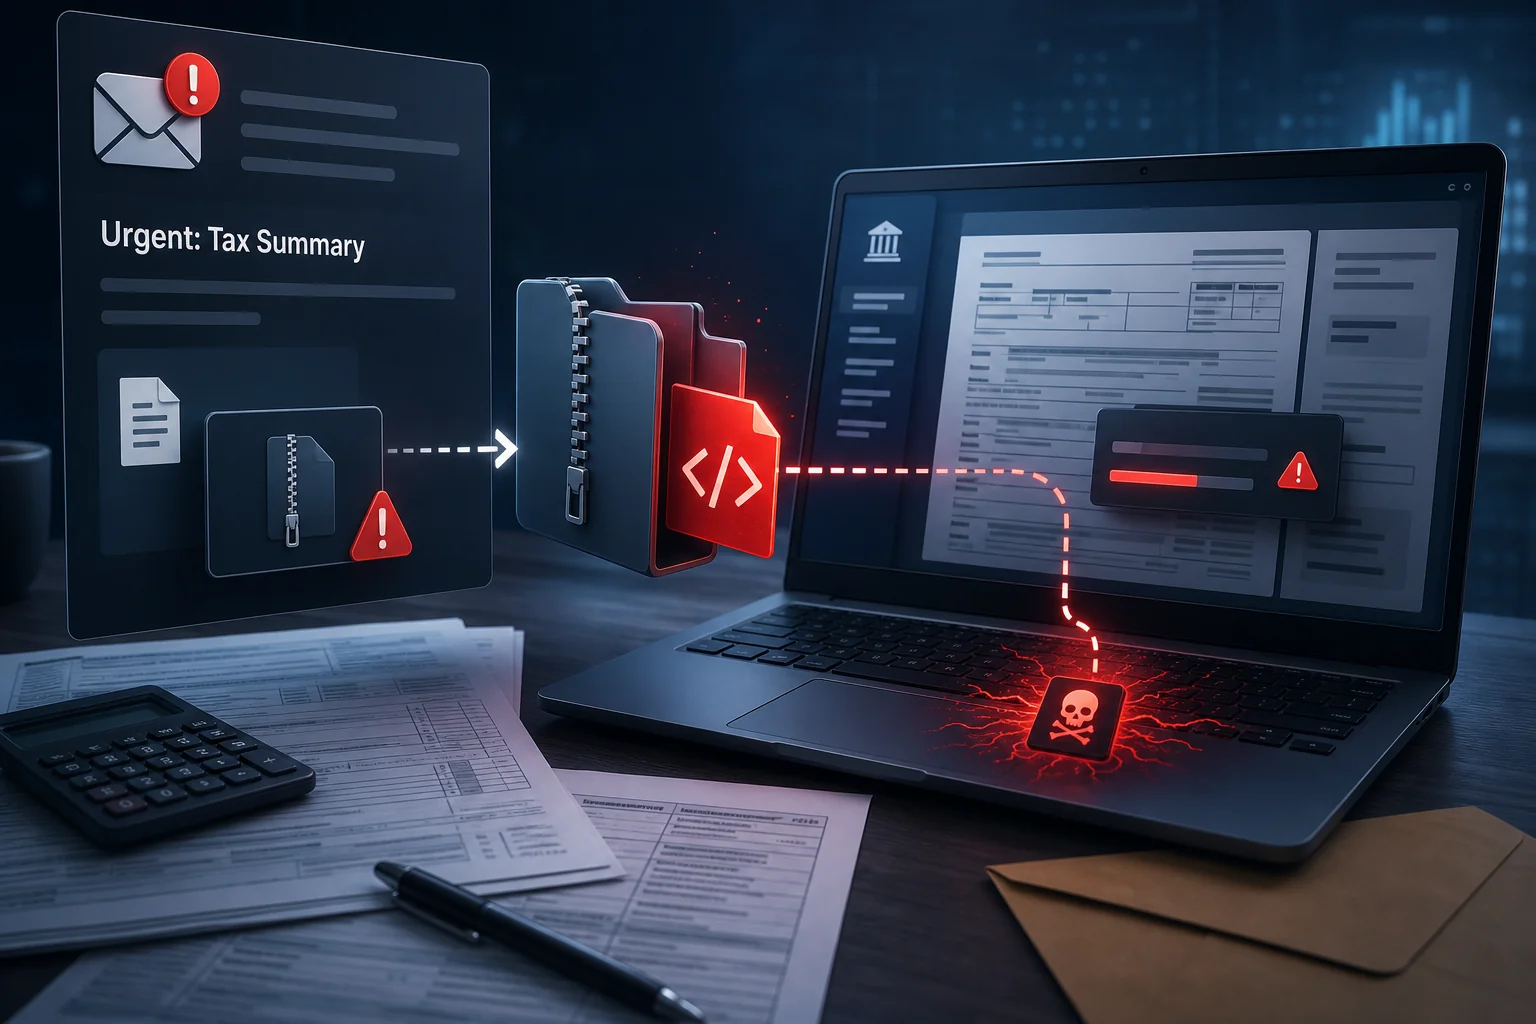
The Tax Summary email impersonates a tax service, opens a fake download page and installs malware through a ZIP archive containing a VBScript file.
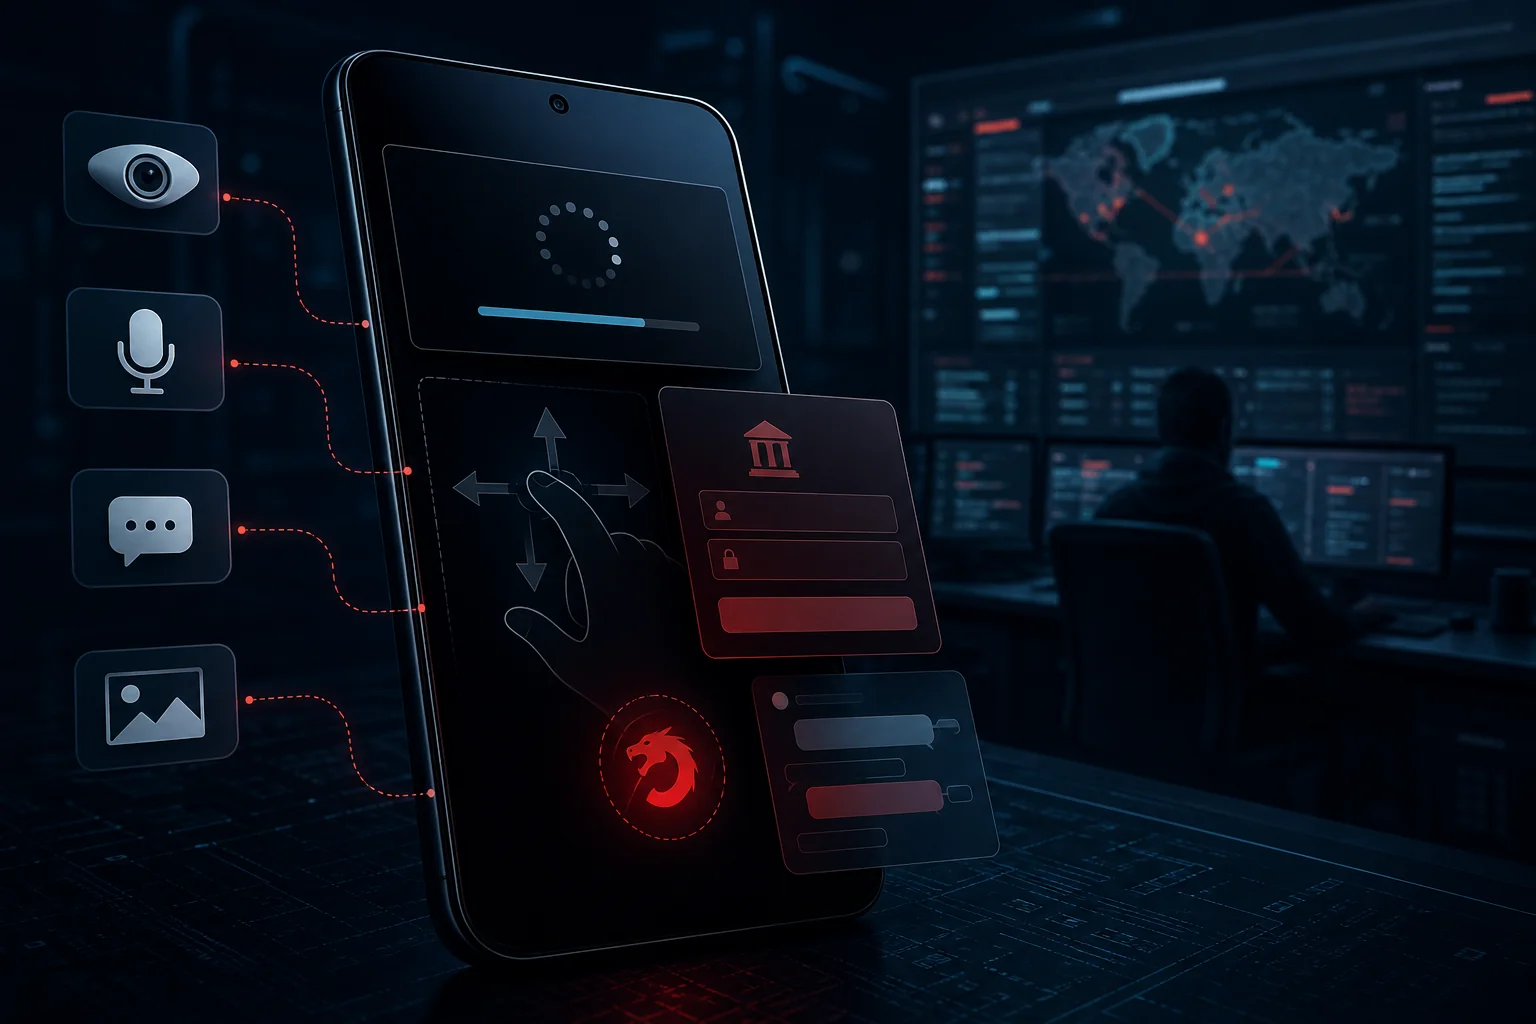
Night Dragon is an Android remote access trojan that can hide its icon, record the screen, steal financial passwords and secretly control an infected phone.
Flying Eagle is an Android remote access trojan sold as a customizable toolkit for recording screens, stealing passwords and controlling infected phones.
TONResolver is a Windows remote access trojan that uses a TON smart contract to locate changing command servers and launch password-stealing malware.
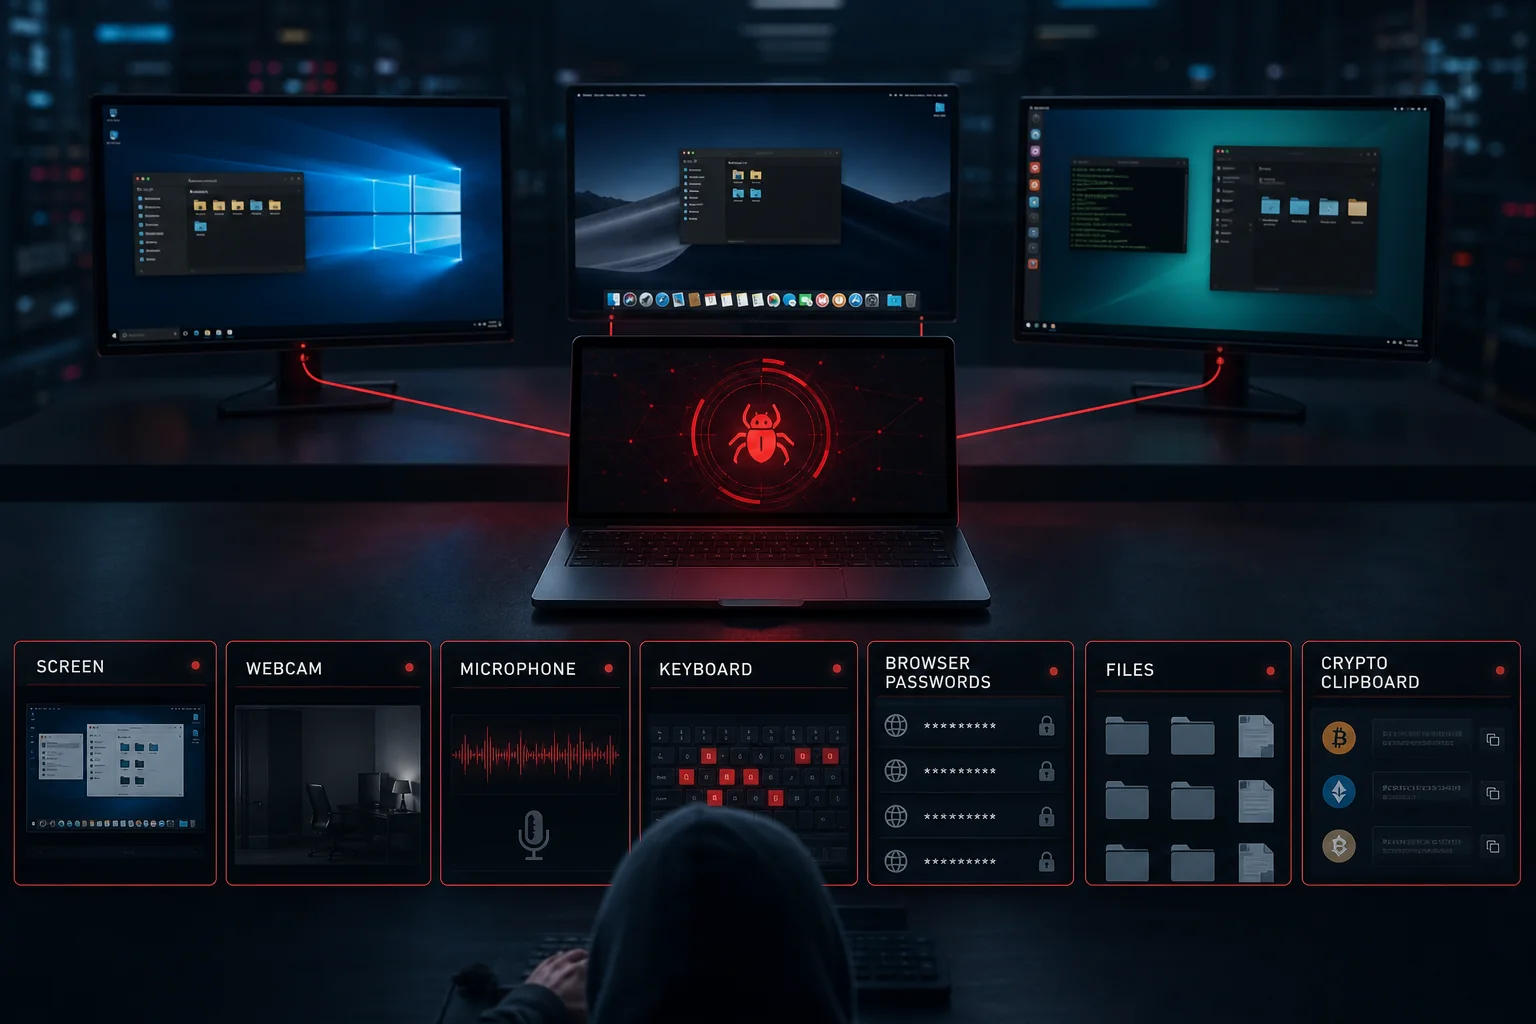
QuimaRAT is a cross-platform remote access trojan that can steal passwords, record activity and give attackers control of Windows, macOS and Linux devices.
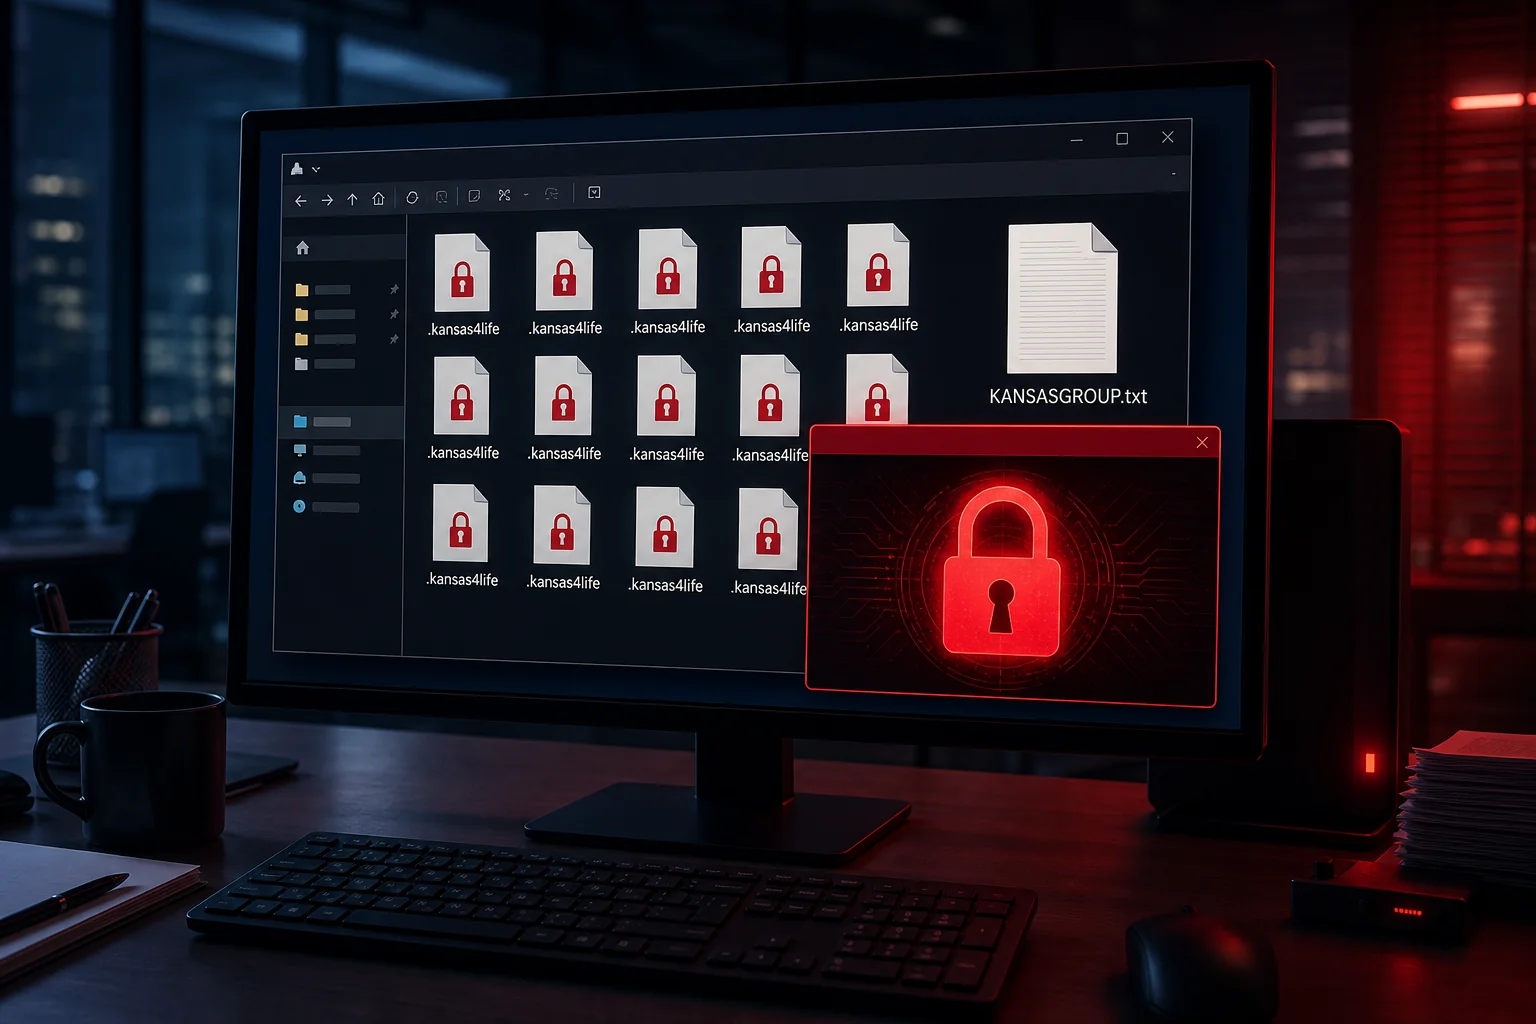
KansasGroup ransomware encrypts files, adds the .kansas4life extension and leaves a KANSASGROUP.txt ransom note. Learn what to do without making the damage worse.
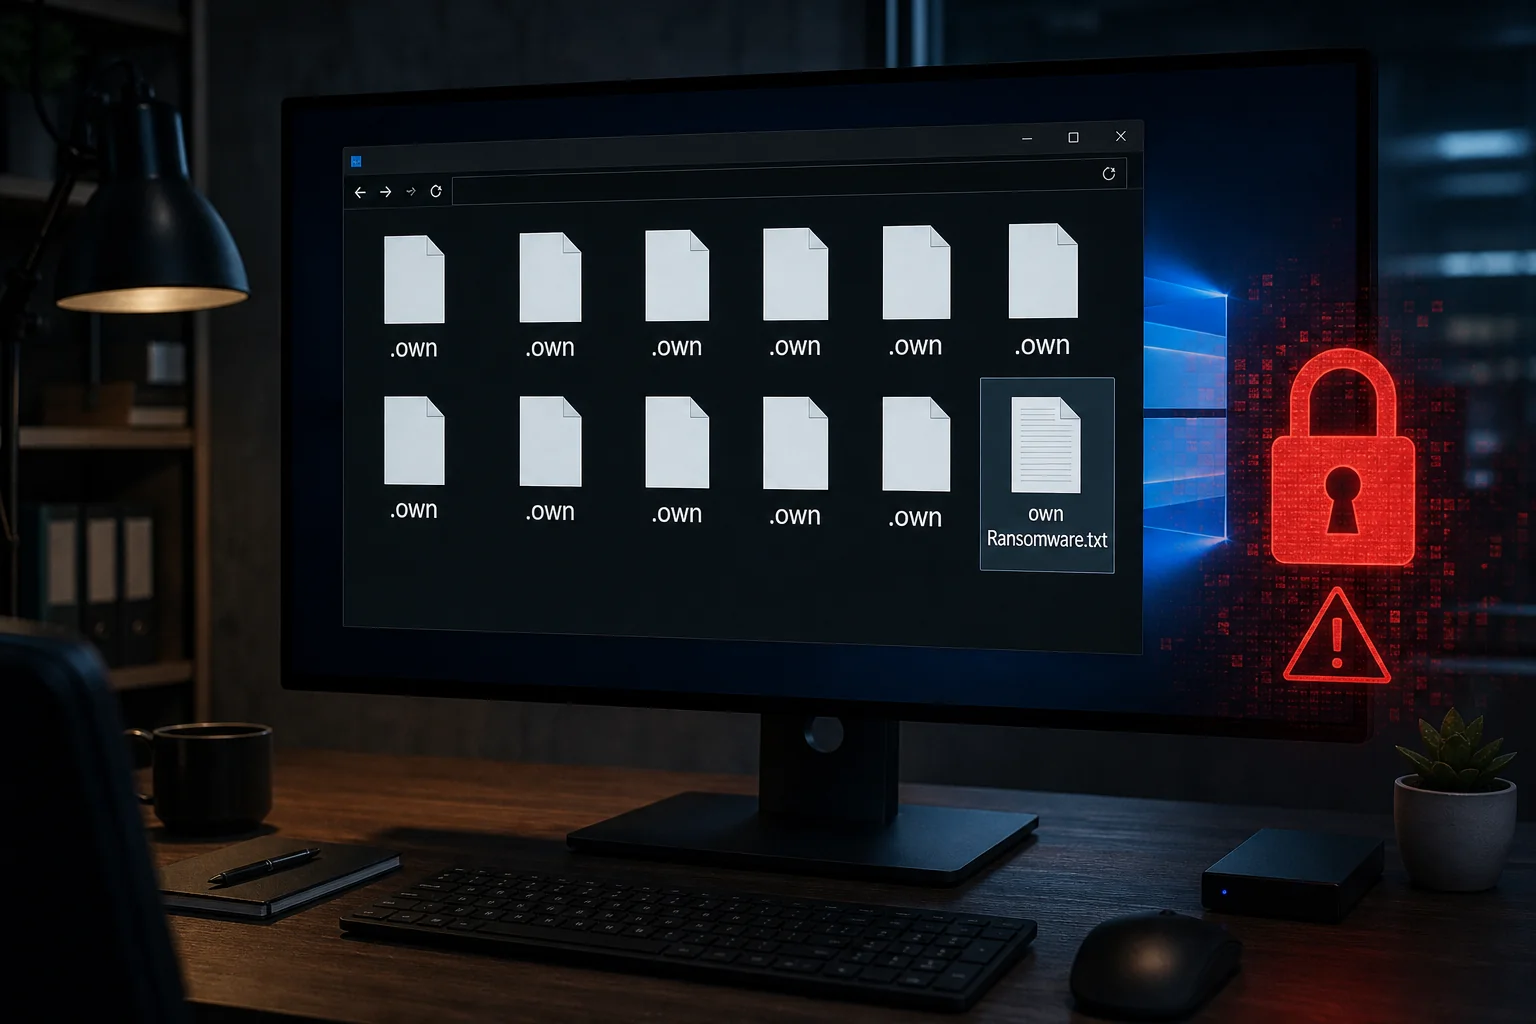
Own ransomware encrypts files, embeds attacker contact details in their names and adds the .own extension. Learn how to contain the attack and assess recovery options.
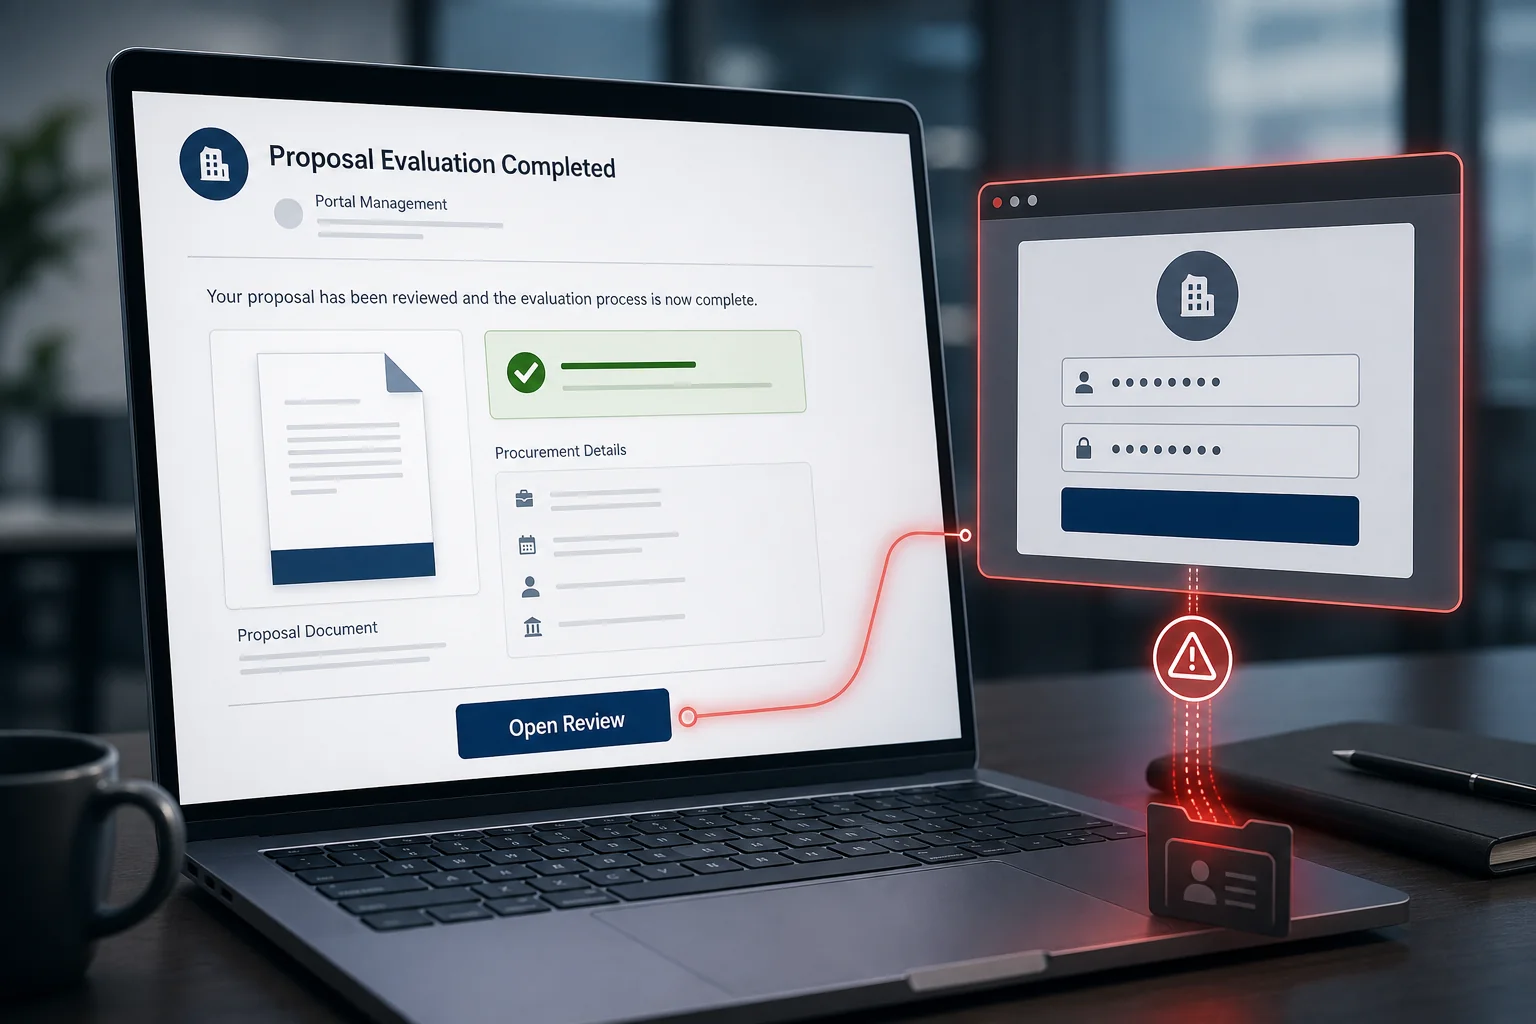
The Proposal Evaluation Completed email is a phishing scam that sends recipients to a fake sign-in page. Learn how the message works and what to do after clicking.
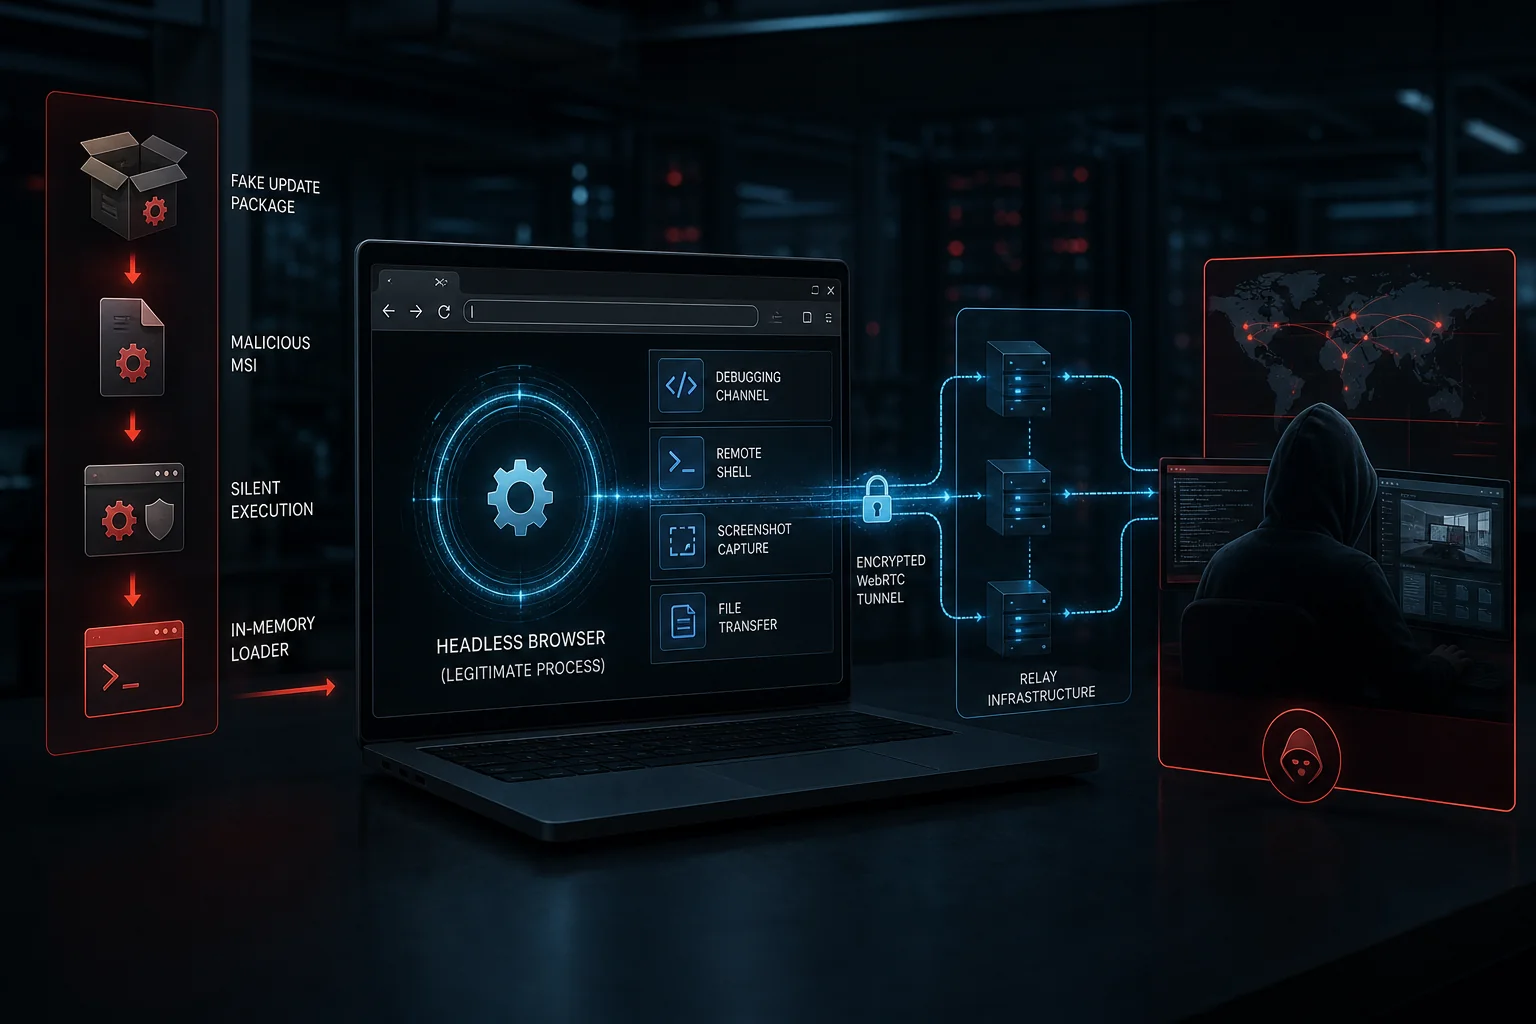
msaRAT is a Rust-based remote access trojan linked to the Chaos ransomware group. It controls Chrome or Edge to hide command traffic inside a browser connection.
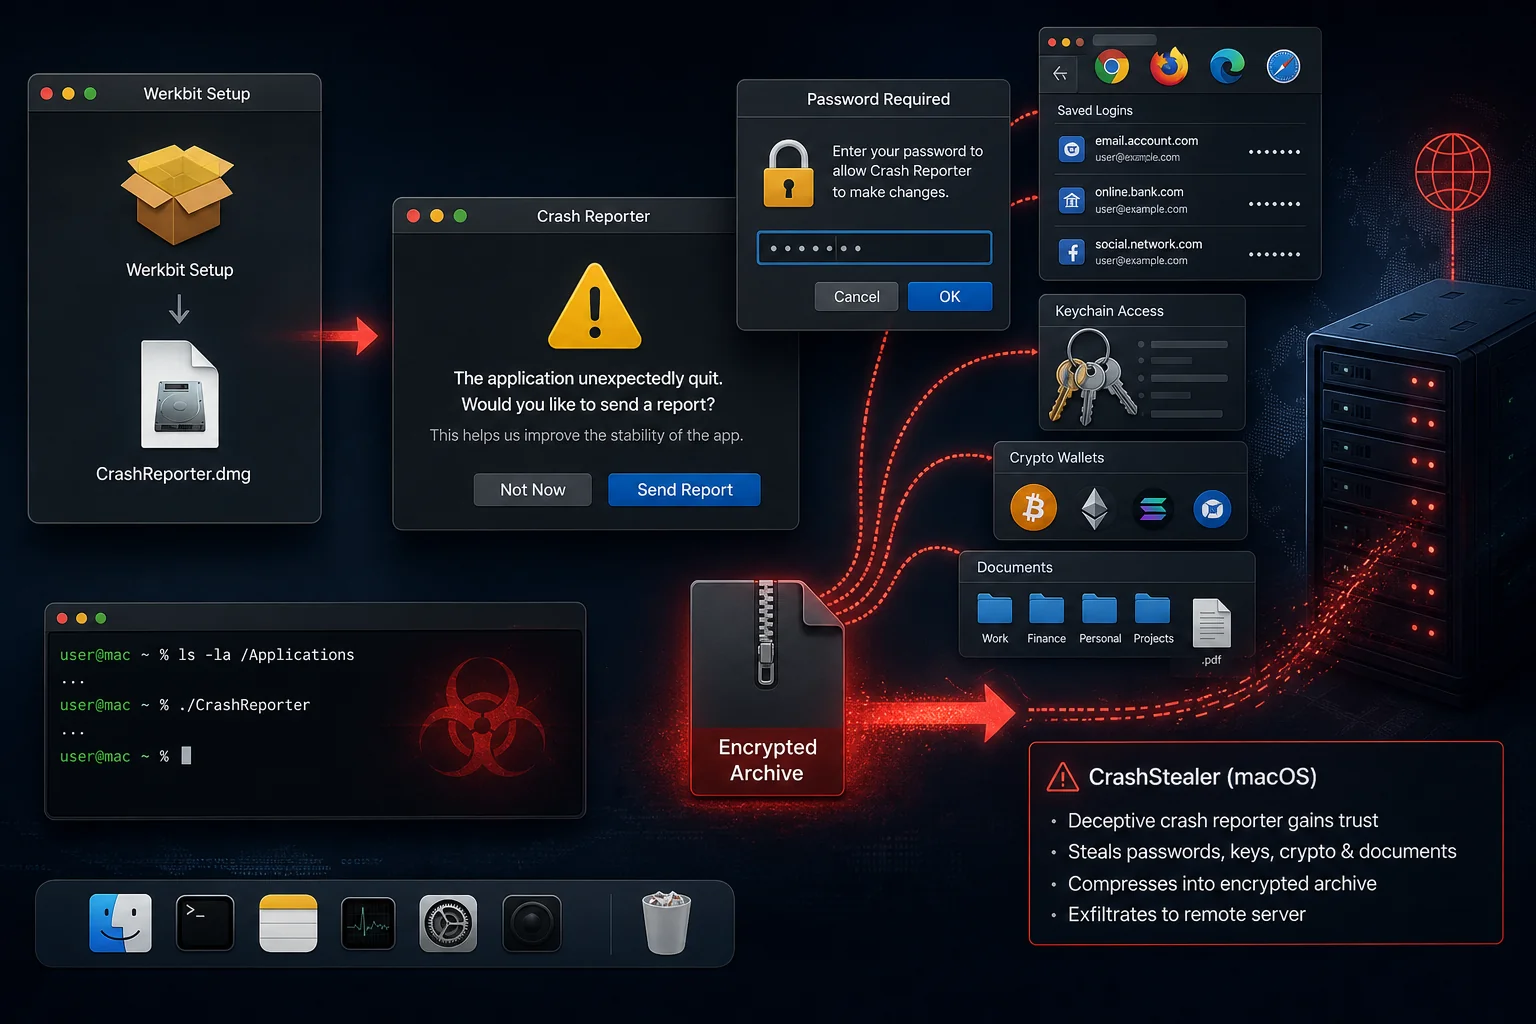
CrashStealer is a macOS information stealer disguised as an Apple crash-reporting process. It targets Keychain passwords, browsers, wallets, password managers and personal files.
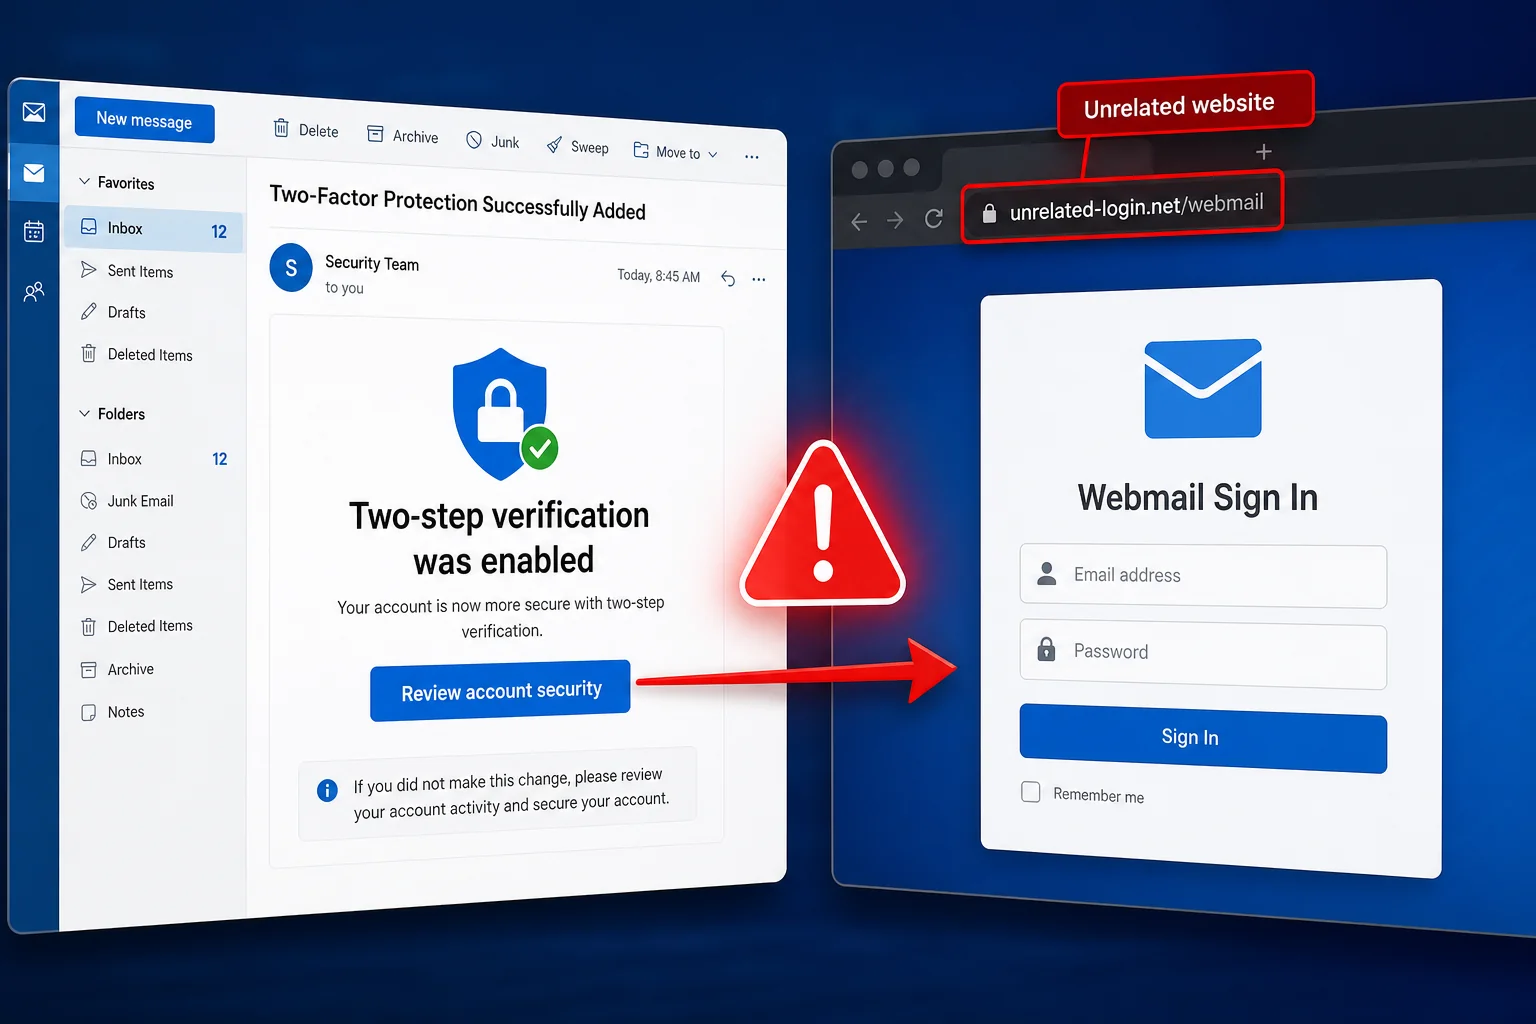
The Two-Step Verification Was Enabled email is a phishing scam that leads to a counterfeit webmail login. Learn how to recognize it and secure an exposed account.
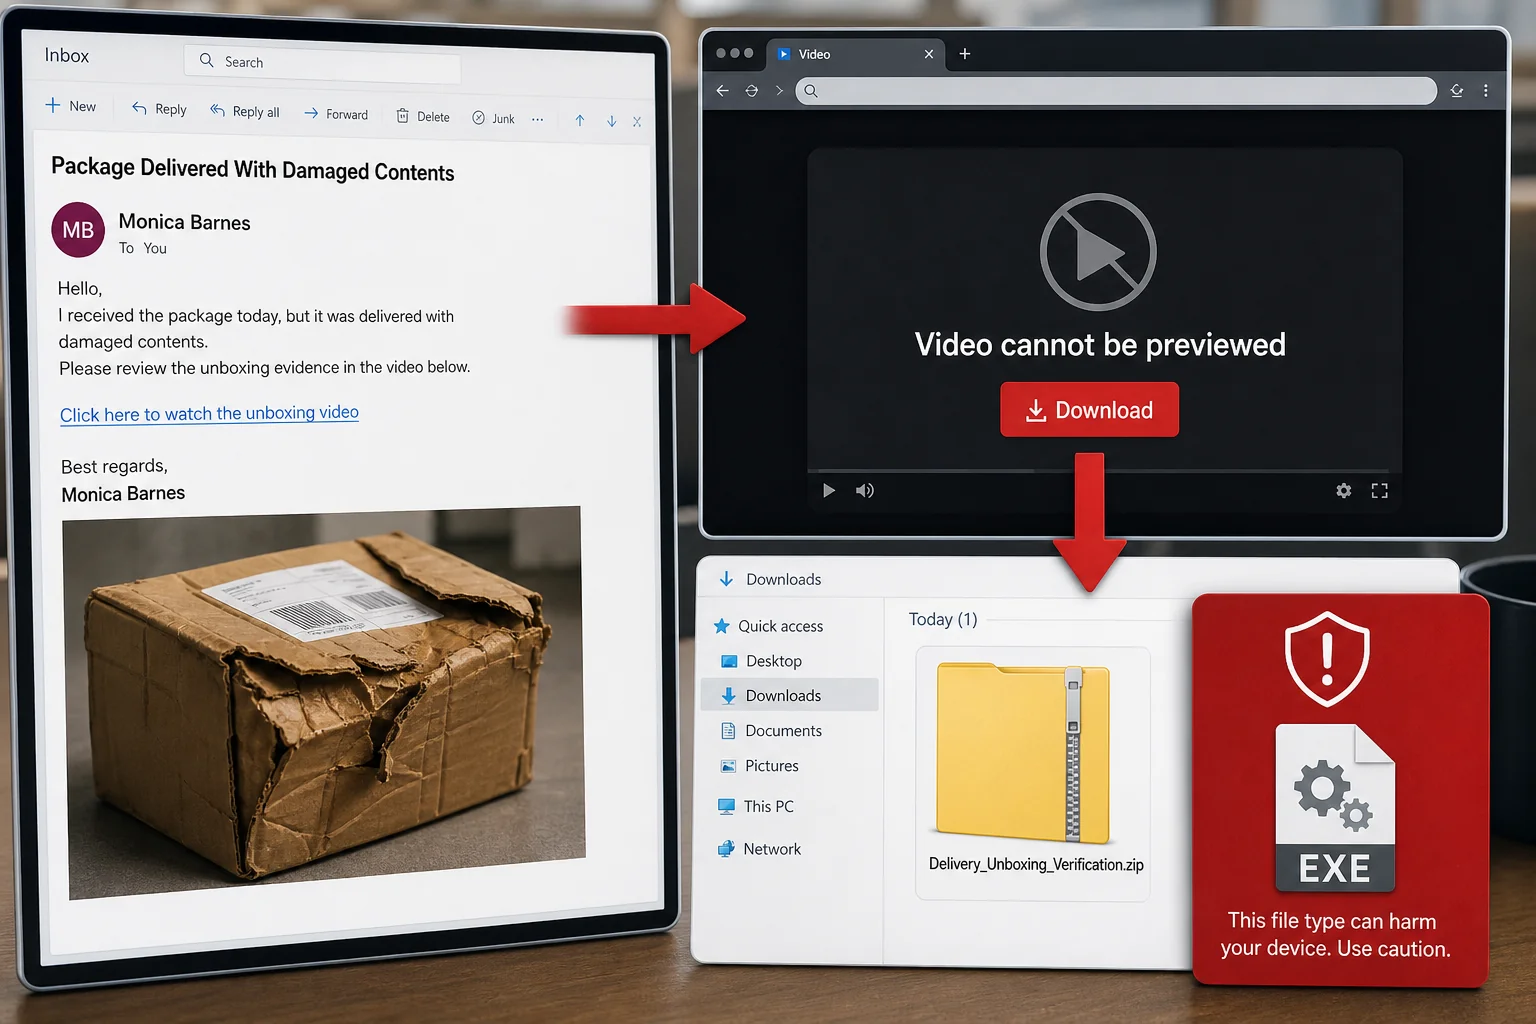
The Damaged Package email disguises malware as unboxing evidence from a dissatisfied customer. Its link downloads a ZIP archive containing a dangerous Windows executable.
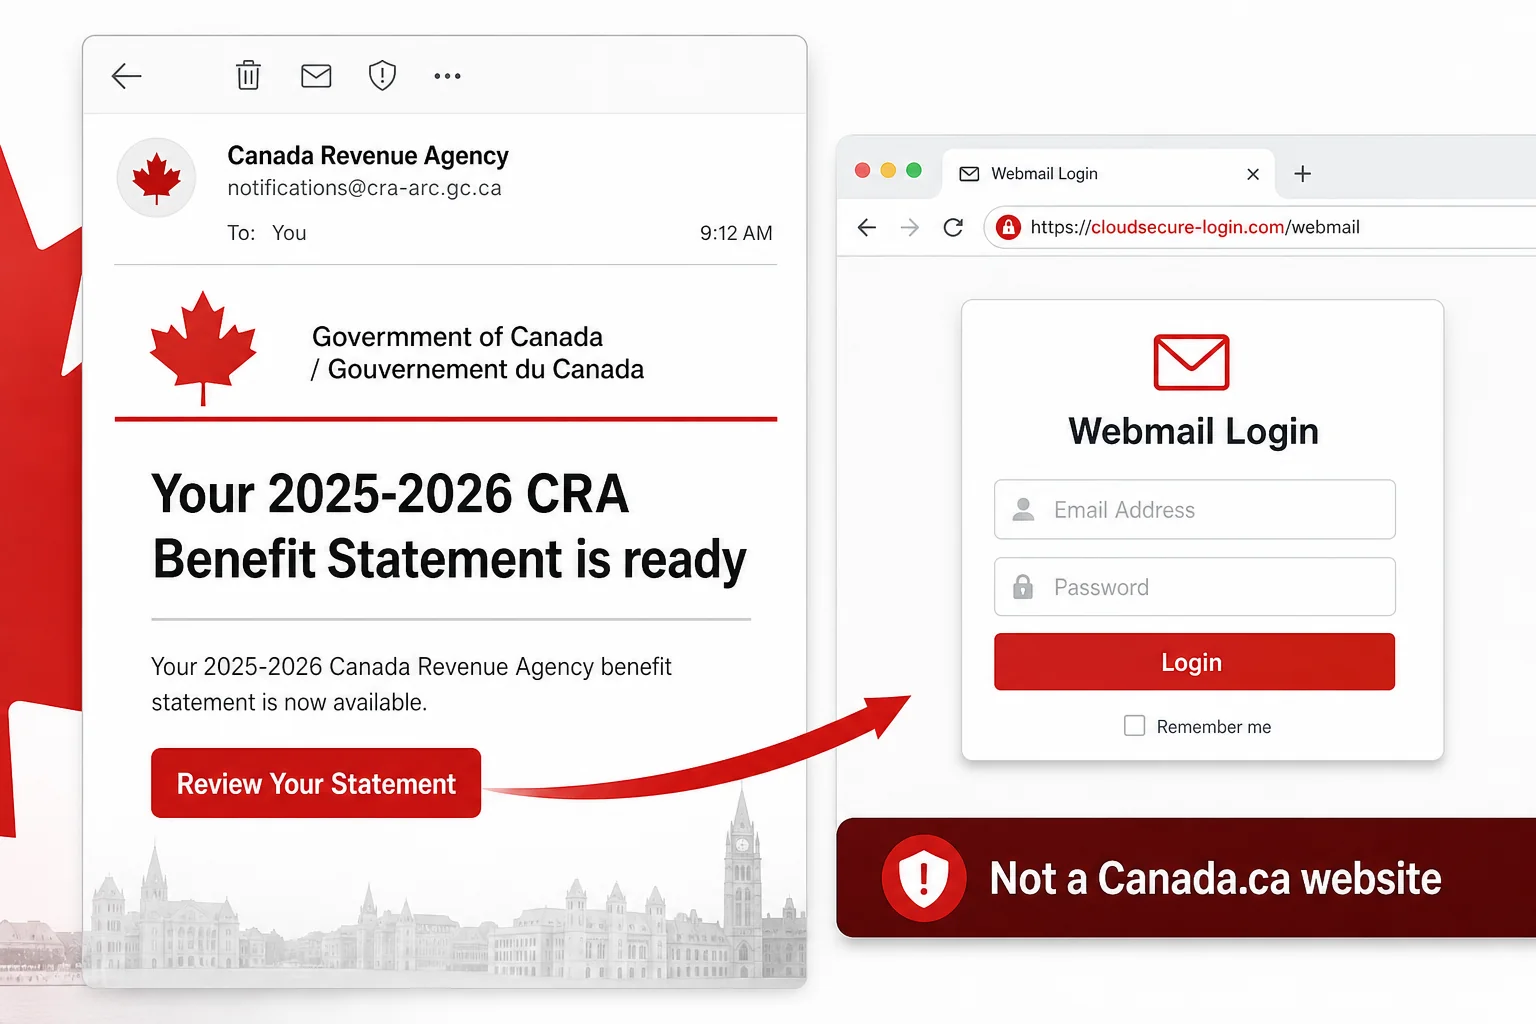
The CRA Benefit Statement email impersonates the Canada Revenue Agency and sends recipients to a fake webmail login. Learn how the phishing message works.
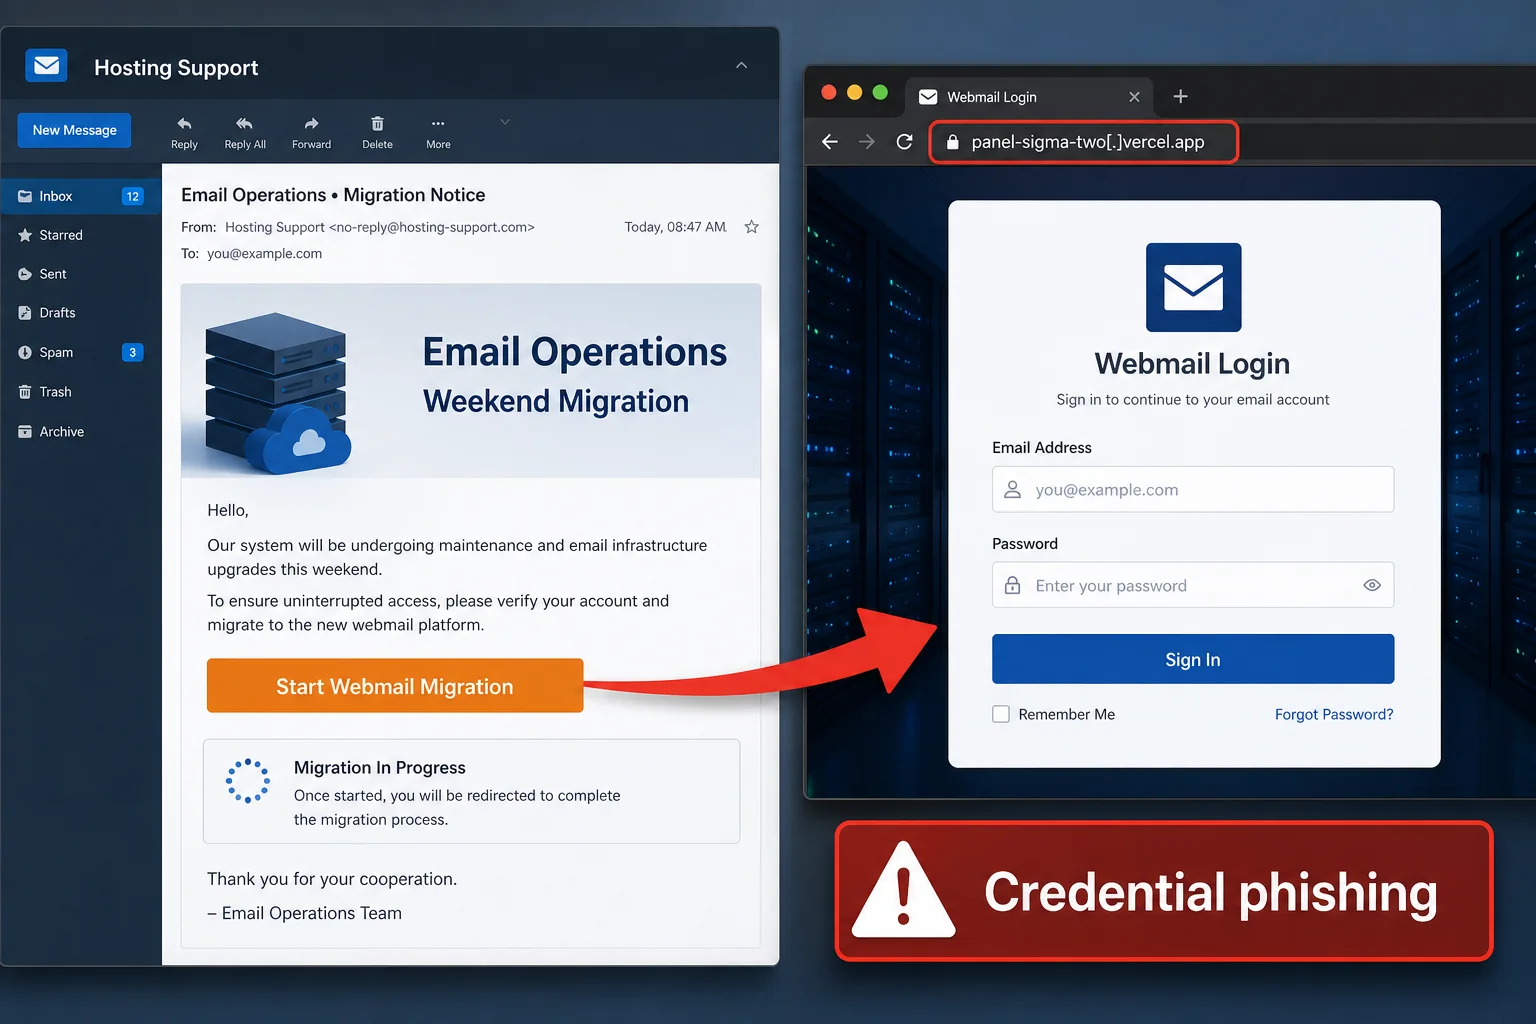
The Email Migration Notice is a phishing scam that sends recipients to a counterfeit Webmail login. Learn how the fake weekend upgrade captures email passwords.
Soft Serve Clothing is a real long-running store, but an F BBB rating, hundreds of unanswered complaints and years of missing-order reports make it unsafe to recommend. Read this before ordering.
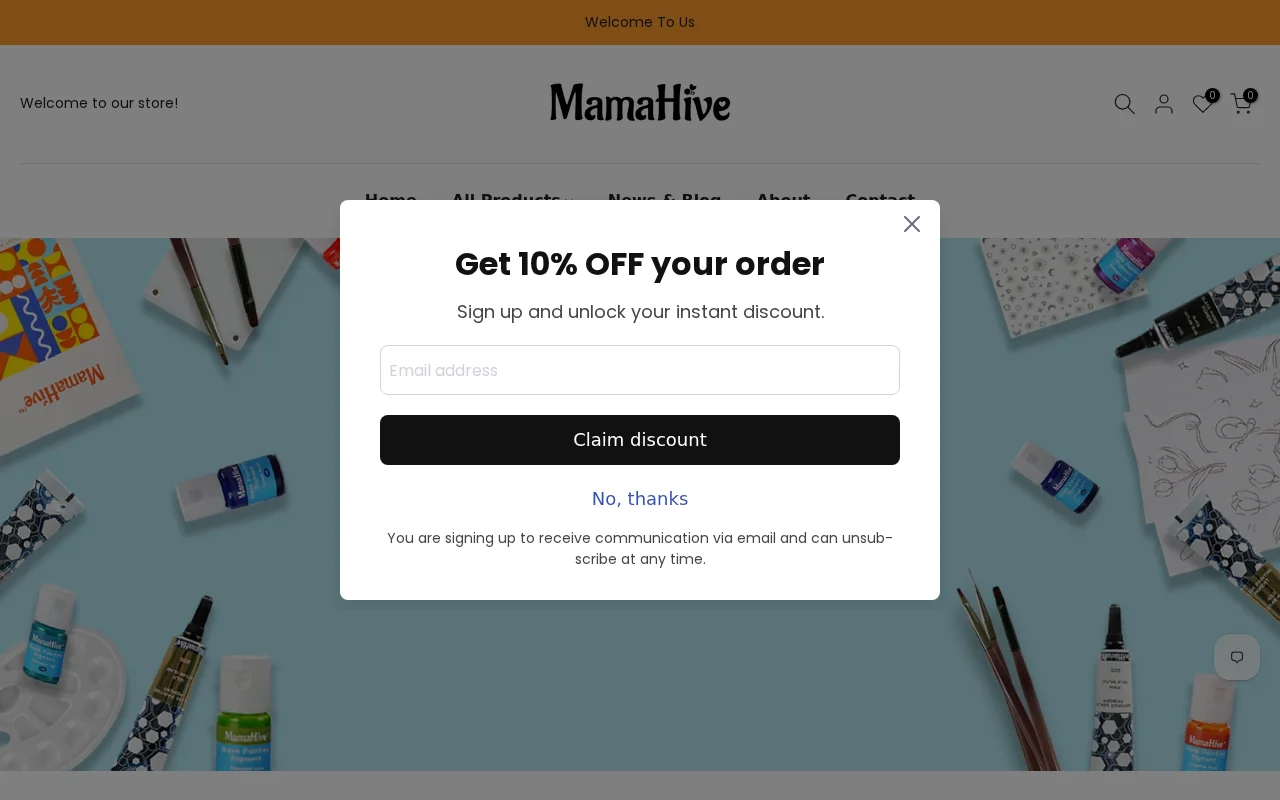
We investigated Mamahivestudio.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
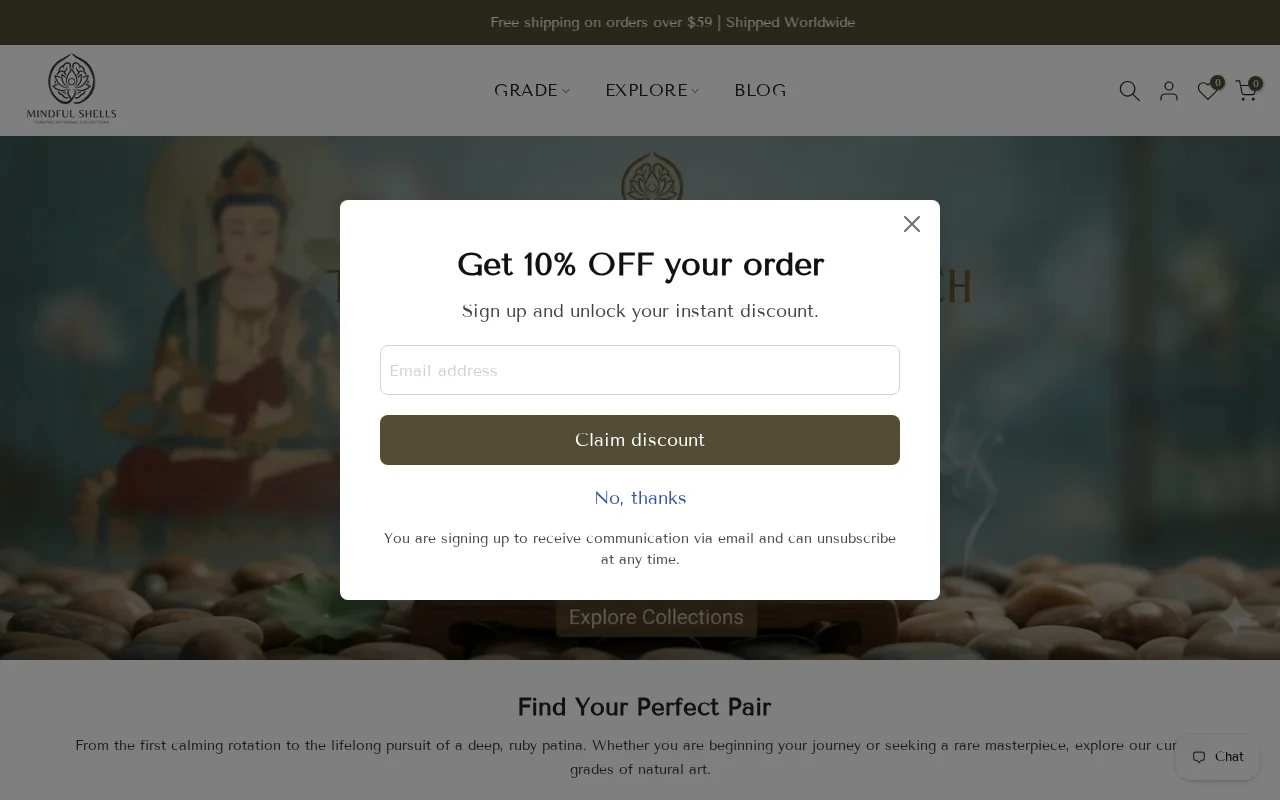
We investigated Mindfulshells.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
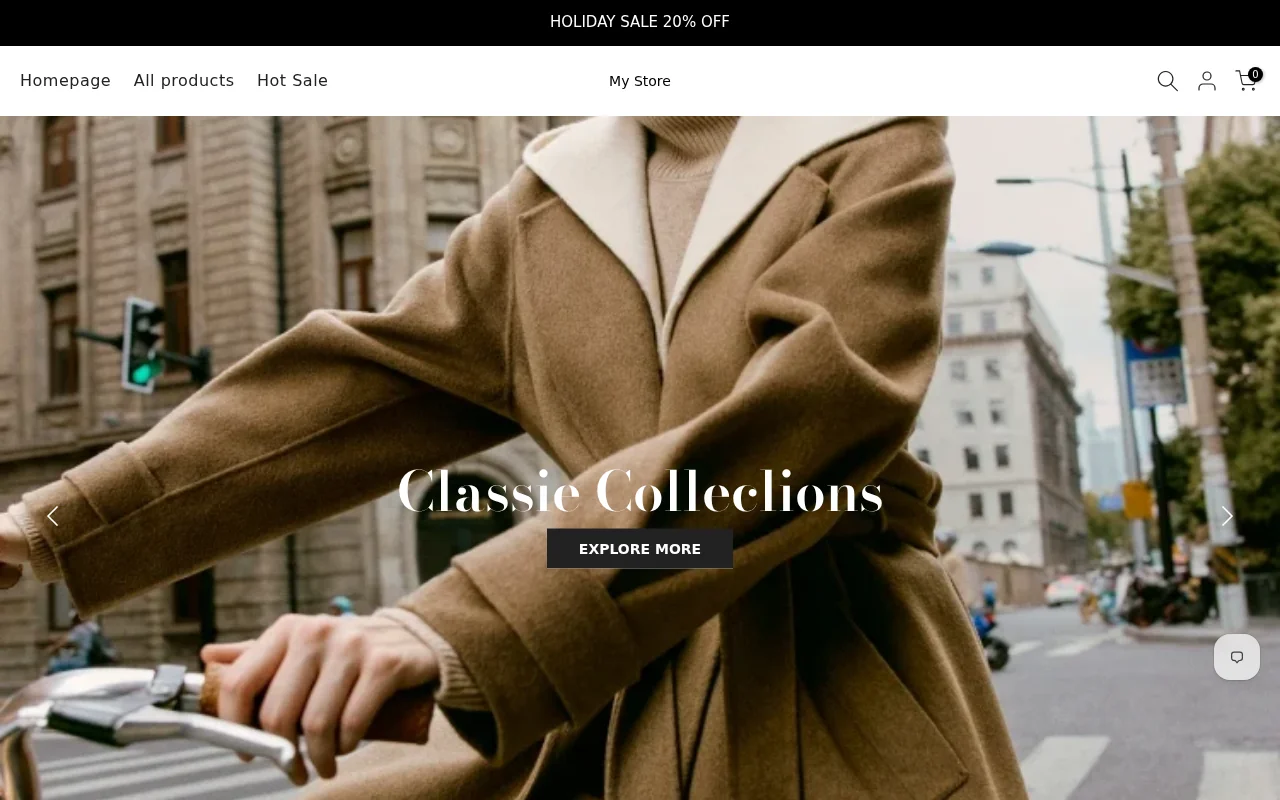
We investigated Mondaysmile-ny.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
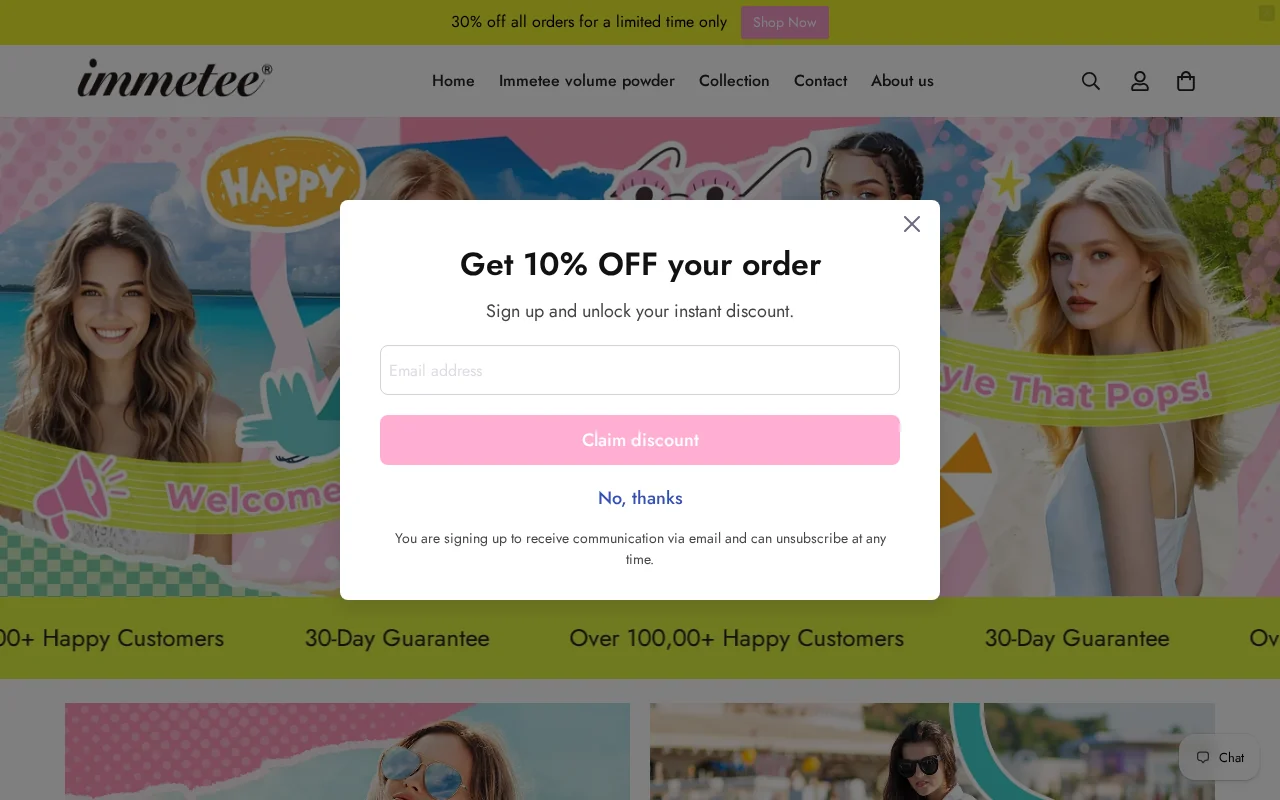
We investigated Immetee.net shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
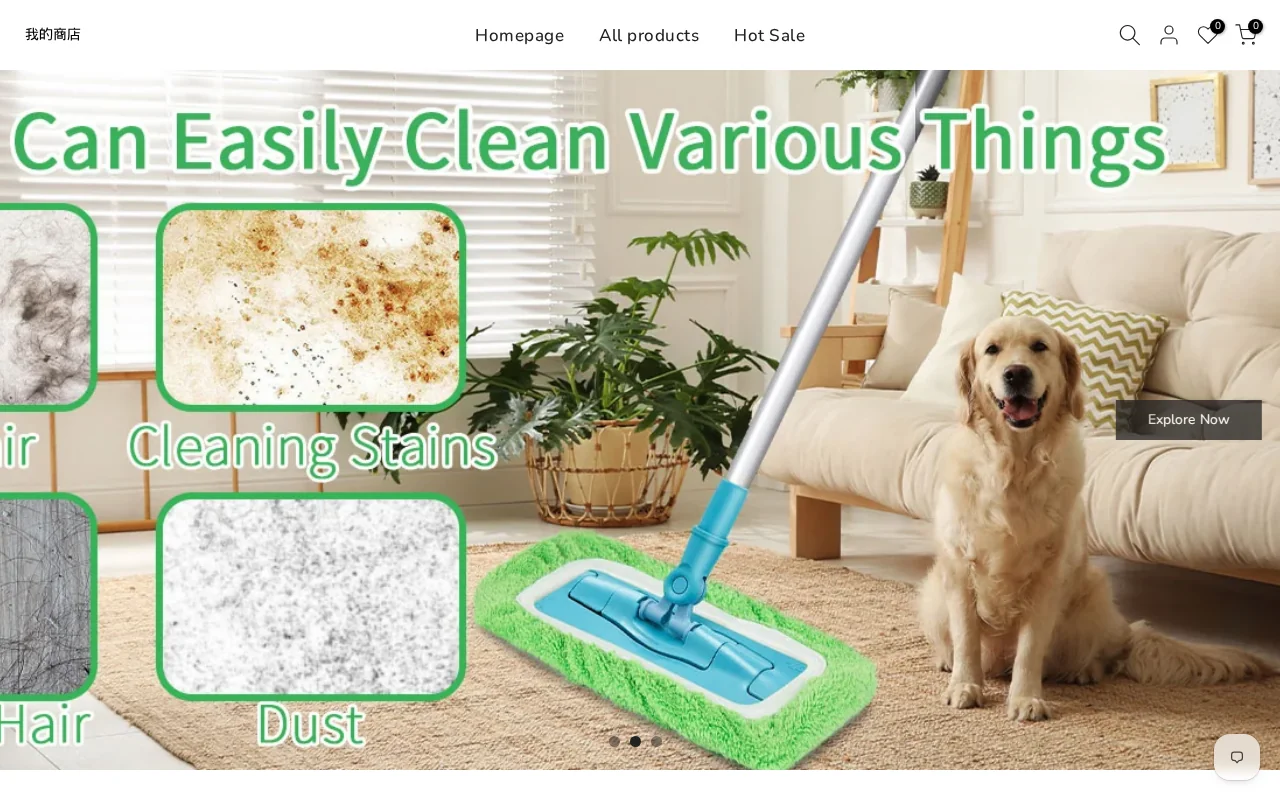
We investigated Unoutur.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
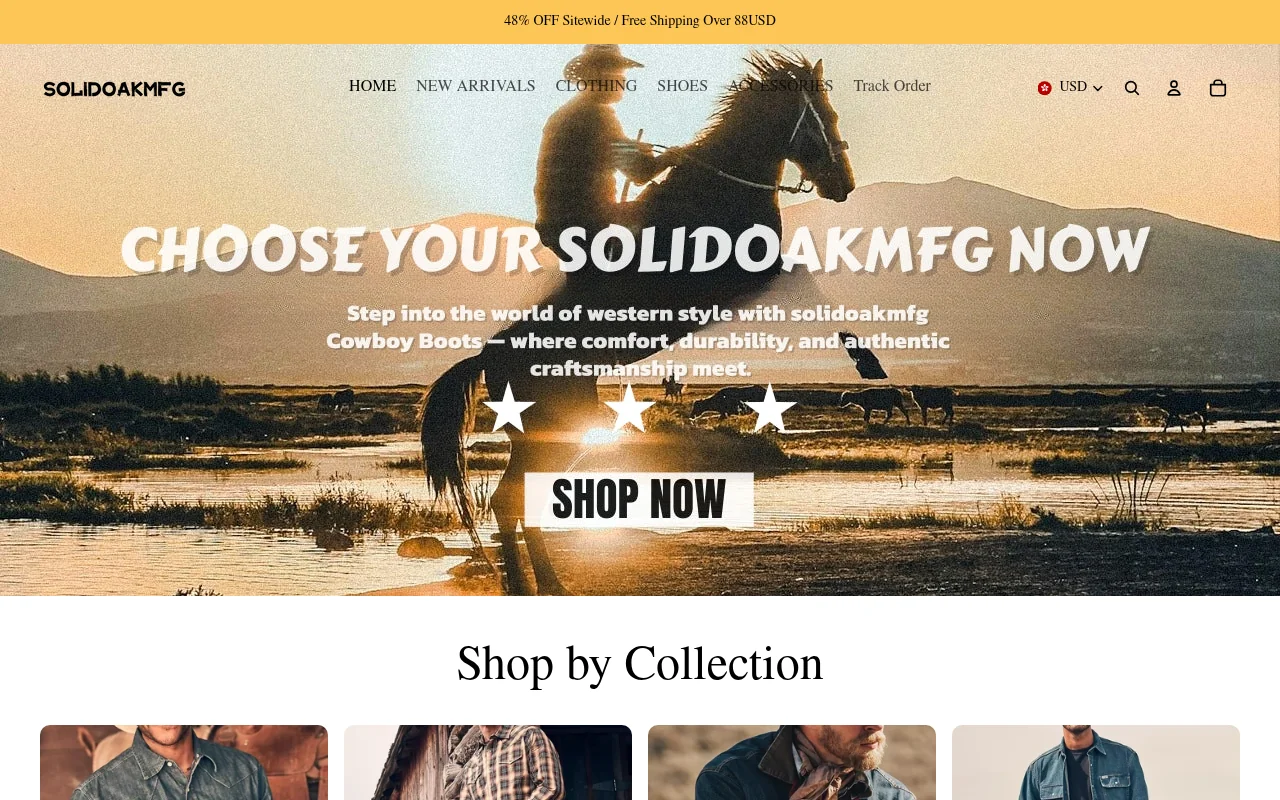
We investigated Solidoakmfg.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
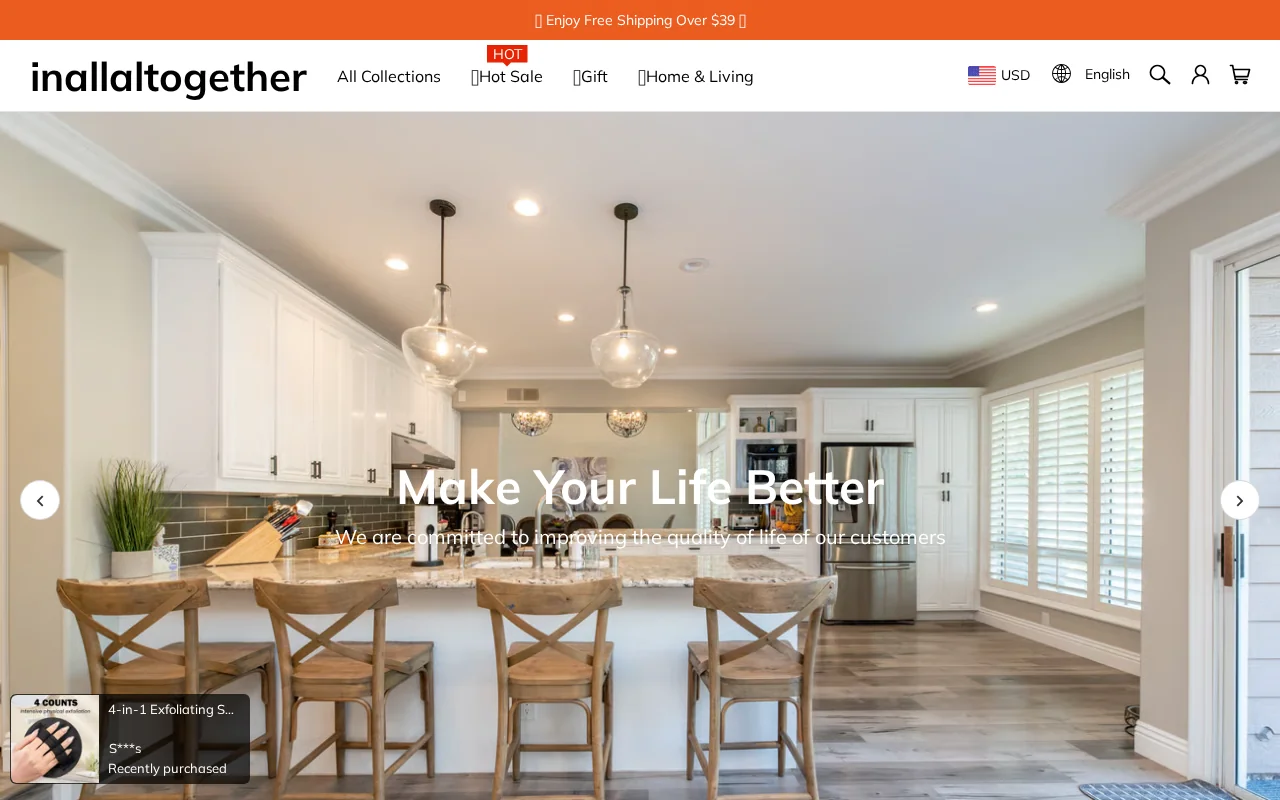
We investigated Inallaltogether.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Webilliards.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Kunluntooth.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Flavoryfood.ca shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Tenkints.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Deechysilverjewelry.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Hoppenly.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
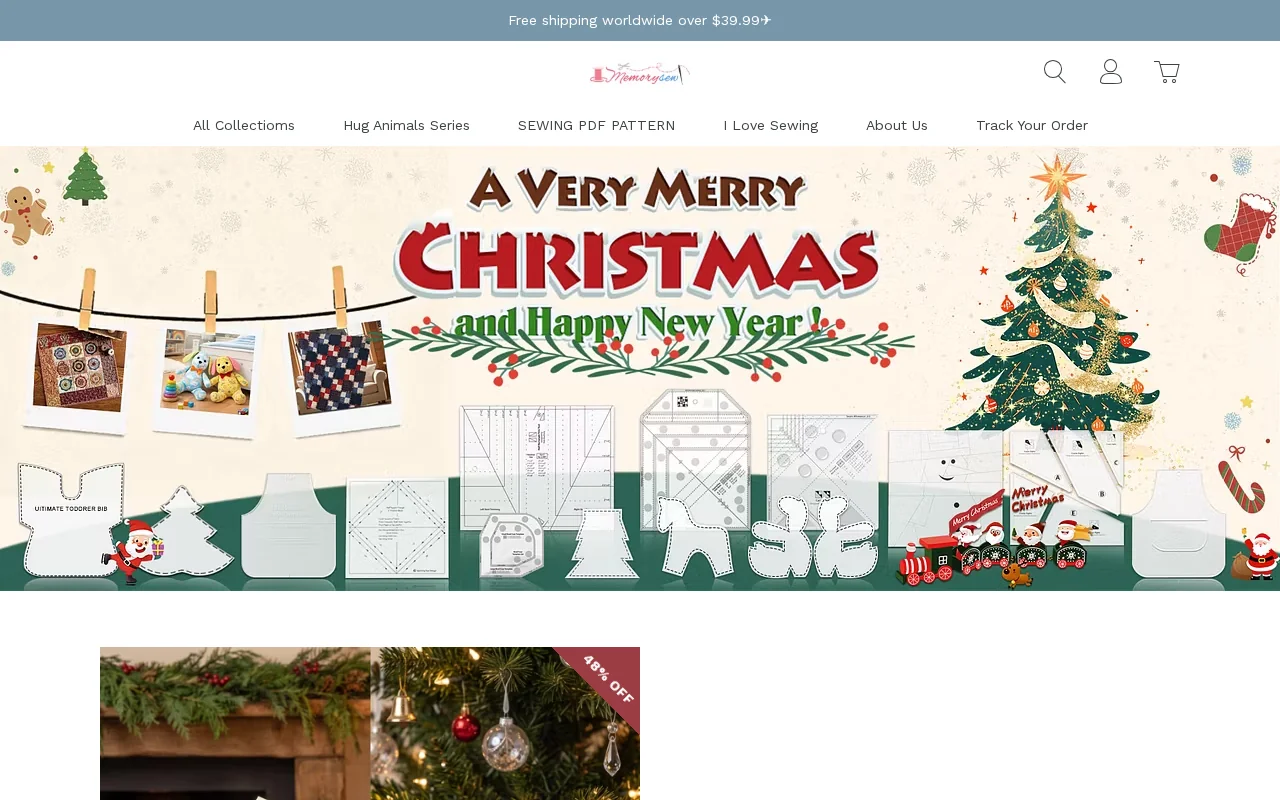
We investigated Serendipitydiy.com shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
We investigated Mysports.stores shopping site – legit store or a scam? Read this before you shop to see what we uncovered.
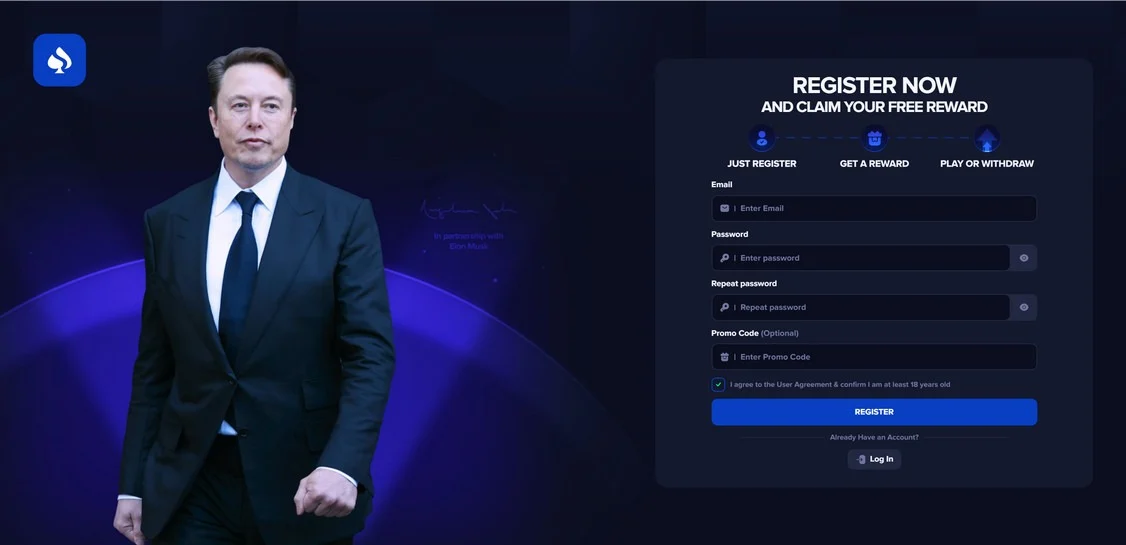
Read our Go.rasowin.com investigation covering crypto casino red flags, bonus claims, withdrawal risks and what users should know before depositing.
Read our App.meopex.com investigation covering crypto casino red flags, bonus claims, withdrawal risks and what users should know before depositing.