

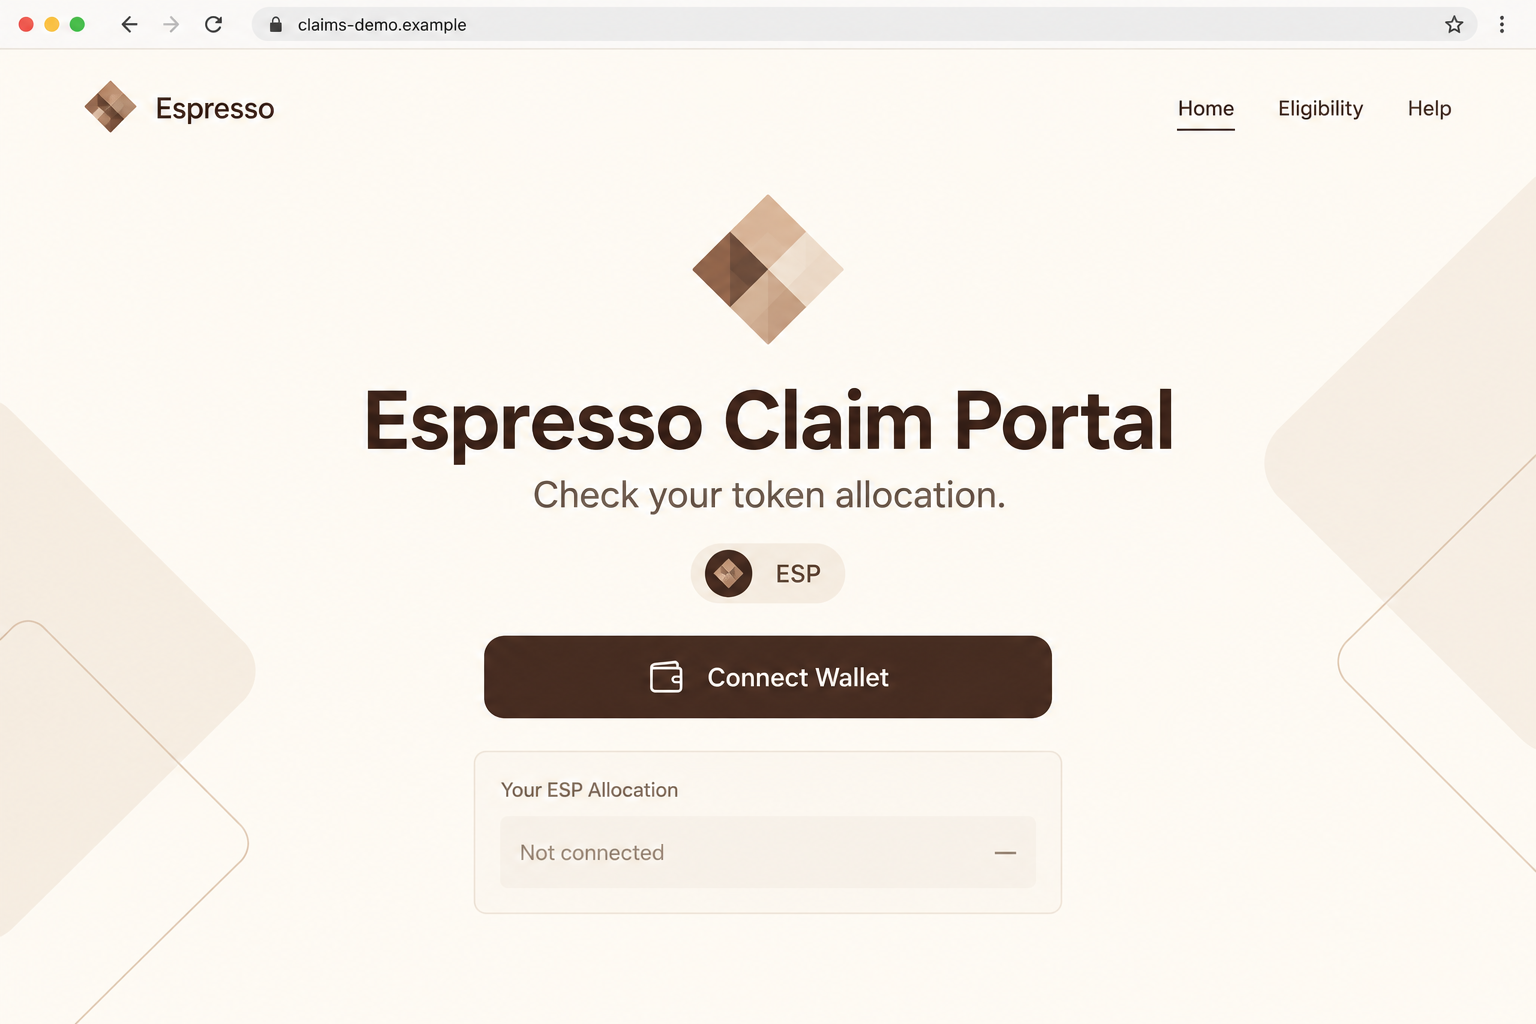
A page offers to check your Espresso token allocation. The design is tidy, the project name is recognizable, and a wallet button sits in the middle.
If you have been following crypto announcements, the invitation may not seem unusual. Take a moment to work out where that invitation came from.
Overview
The claim portal borrows a genuine project’s identity
The Claim Espresso ESP scam presents an unofficial token-collection page as though it belongs to the real Espresso project.
Reported imitation addresses include claim-espresso[.]app, claim-espressofoundation[.]org, and register-espresso[.]com. Their familiar wording is part of the invitation, not proof of an official relationship.
Espresso itself is a genuine blockchain project. This warning concerns websites impersonating it, not a claim that every ESP token or legitimate reward program is fraudulent.
A promised allocation brings a funded wallet into reach
The reported portals solicit wallet activity and have been associated with a cryptocurrency drainer. The purpose is to obtain access that benefits the attacker.
Simply connecting an address does not necessarily transfer assets. The danger depends on the later signature, spending permission, transaction, or disclosure requested.
No wallet interaction was performed here. The precise contract and network were not reproduced, and the lead image is a fictional interface rather than the original portal.
What deserves attention before checking eligibility
- Where did the claim link originate, and can an independently verified project source confirm it?
- Does the destination have an established connection to the project, rather than merely containing its name?
- What does the wallet actually ask you to authorize?
- Could the request affect assets you already own, not just the promised reward?
- Is the page asking you to ignore a warning or reveal recovery information?
The apparent value of an allocation should not decide these questions. A reward displayed by an unknown website is still only a statement made by that website.
A Real Project Does Not Authenticate Every Claim Using Its Name
Crypto projects can publish genuine launches, staking information, and reward instructions. That gives an impersonator a believable setting for a false portal.
The visitor may already know the project exists and stop checking too early. Recognition answers one question, but not the important one: who operates this particular page?
A copied logo, project description, or link to genuine documentation can make a clone feel connected to the real ecosystem.
Those elements are public. A scammer does not need to compromise the project to reproduce them or place them beside a malicious button.
Start from Espresso’s official website and independently verified announcements when checking a program. Do not treat the imitation’s own links as independent confirmation.
The direction of the check matters. An official resource can establish an application route; an unknown portal linking back to the project cannot establish itself.
Even then, verifying identity is not an investment recommendation. You still need to understand the activity, its requirements, and the risks of using your assets.
How the Claim Espresso ESP Scam Works
Step 1: A token invitation supplies a reason to visit
The offer centers on claiming an allocation rather than buying something. That can lower resistance because the visitor believes the action will add value to their wallet.
A link might circulate through an advertisement, message, post, or compromised account. The exact route should be recorded from your experience rather than guessed afterward.
A familiar account sharing the link is not enough. Accounts can be imitated, compromised, or simply mistaken about what they are recommending.
Likewise, a discussion full of enthusiastic replies is not a substitute for an official announcement. Comments can be manufactured or copied.
Before opening the claim flow, locate the relevant announcement independently. Check that it identifies the destination and explains who is eligible.
If the only explanation comes from the page offering the reward, you have not completed an independent check.
There is no need to connect a funded account just to discover whether the invitation was genuine. That question should be settled before wallet permissions enter the picture.
Step 2: The portal turns curiosity into a connection request
A claim page can ask visitors to connect before showing an allocation. The request feels consistent with checking an address against eligibility rules.
That familiar pattern is useful to an impersonator. It gives the site a reason to involve the wallet while the visitor still thinks they are only looking.
The wallet may correctly identify the account and show a genuine connection window. A real wallet interface does not authenticate the website requesting access.
Read the application identity and permissions carefully. Confirm which account is selected, especially if the wallet contains several profiles.
Connecting is not the same as entering your recovery phrase. If a website asks for those words, stop rather than treating it as another connection method.
A claim portal should not receive the secret used to recreate your wallet. The words remain sensitive regardless of the reward being offered.
If you only connected and declined everything afterward, keep that distinction in your incident record. It matters when deciding what needs attention.
Step 3: A follow-up request can reach beyond the advertised reward
Once an address is connected, the application can present more requests. The page may describe them as checking eligibility, registering participation, or preparing a claim.
Those descriptions are not the authority you grant. The genuine wallet’s request is what needs to be understood.
A transaction could move an asset. A token approval could authorize another account or contract to spend. Some signatures can carry consequences without resembling an ordinary payment.
Do not approve because the page says the action is free. A missing price label is not proof that your existing holdings are unaffected.
Compare the requested action with your intention. You arrived to receive a token, not to surrender control over unrelated assets.
Unexpected spending scope, an unfamiliar recipient, or a warning you cannot explain is a reason to stop and obtain trustworthy help.
Do not test a suspicious request with another funded wallet. That would expand the exposure without resolving who controls the page.
Step 4: An unsuccessful claim encourages retries or a supposed repair
If the promised tokens fail to appear, a visitor may assume the process was incomplete. They might retry the button or accept another prompt.
A scammer benefits from that uncertainty. A technical-sounding explanation can keep the person inside the same unverified workflow.
Do not pay a separate release charge, deposit more crypto, or use a repair portal supplied by an unsolicited helper.
These are precautions against possible follow-up demands, not additional stages confirmed on every reported Espresso imitation.
Leave the page and look at actual wallet activity. A failure message on the website cannot tell you whether a request was signed or a transaction completed.
Equally, a displayed success message cannot prove you received a legitimate allocation. Check real records before accepting the portal’s account of what happened.
Connection, Approval, and Recovery Words Need Different Responses
A connection exposes less than a transfer, but still needs review
A basic connection generally makes the selected address available to the application and allows it to request further interaction.
That is not a reason to panic about an automatic loss. It is a reason to disconnect the imitation and establish what followed.
Check the correct wallet account. Looking at an unused account’s clean history would not explain activity involving a different one.
An approval can remain after you close the page
Some permissions continue until changed through the relevant network process. Closing a tab is not a reliable way to remove them.
MetaMask’s permissions guidance specifically distinguishes disconnecting an application from revoking token approvals.
Use instructions suited to the wallet and chain involved. Avoid a random revocation tool introduced in the same comment thread that promoted the claim.
Revoking unwanted authority can limit future exposure. It does not roll back a finalized transfer or guarantee that every asset is safe.
A leaked backup is a broader compromise
If you typed recovery words into a website, someone else may be able to recreate access without keeping that site connected.
Changing the wallet application’s password does not change those underlying recovery words. Reinstalling the same wallet can recreate the same compromised accounts.
Seek verified assistance with protecting remaining assets using securely generated replacement credentials. Do not feed a compromised wallet more funds without understanding the risk.
Fees and Balances Can Make the Wrong Request Look Normal
Legitimate blockchain transactions can involve network fees. A fee shown by a real wallet therefore does not, on its own, tell you whether an application is genuine.
The amount also says little about the scope of an authorization. A low fee can accompany a consequential permission.
Read what the action does, not only what it costs. An unfamiliar transfer destination is not made safe because the network charge is small.
A separate demand to send money to a helper for activation or release deserves a different response: stop the exchange and verify independently.
Do not treat a displayed allocation as money you already own. The website can choose the number it shows without creating a genuine claim.
Once you start thinking of the reward as yours, paying to clear a small obstacle can feel like protecting money you already own.
Step back from that framing. Until a legitimate program and entitlement are established, there is no verified payout for a stranger to unlock.
Build an Incident Record That Can Actually Help
If you interacted, write down the account used, the network, the time, and the requests you remember. Keep uncertainties clearly marked.
For example, approving a connection and signing a message are different events. Saying only that you clicked claim can hide the information needed to assess exposure.
Save transaction identifiers and public addresses where available. These can support investigation without revealing the secret material that controls your account.
Do not post recovery words in a public forum to prove ownership. A genuine helper can discuss public transaction data without taking possession of your backup.
If funds reached an identifiable exchange, contact its official reporting team promptly. Provide the actual transaction record rather than the allocation the portal promised.
Blockchain tracing may show where funds moved without making them recoverable. Treat guaranteed-return services with particular suspicion after a crypto loss.
Keep the real project’s identity separate from the imitation address in your report. That helps investigators understand which website you actually used.
What to Do if You Have Fallen Victim to This Scam
Abandon the claim session. Reject any remaining prompts and close the page. Do not reconnect to see whether the reward has appeared.
Preserve the hostname and how you reached it. Avoid sharing the link as an invitation for someone else to test.
Check the account that interacted. Open your genuine wallet separately and review its recent activity, including pending, failed, and completed requests.
Record any transaction you did not intend. An error on the claim website does not establish that the wallet rejected everything.
Remove the imitation’s access and inspect approvals. Follow official wallet instructions for connections, then separately examine spending authority where relevant.
Verify the network and asset before changing permissions. Never transfer money to a stranger as a supposed method of revocation.
Act on exposed secrets. Recovery words or private keys require a response beyond disconnecting an application.
Arrange a securely created replacement wallet through trusted guidance and assess remaining assets. Keep its backup private and separate from the compromised material.
Check any software you installed for the claim. An unfamiliar extension or downloaded helper introduces a device issue as well as a wallet issue.
Consider Malwarebytes for that possible infection exposure. AdGuard can reduce some deceptive advertising; neither tool cancels token approvals or returns a completed cryptocurrency transfer.
Report with precise evidence. Contact genuine project support, relevant platforms, and appropriate fraud authorities through independently located channels.
Include public addresses and transaction references where useful. Do not disclose private keys to someone claiming that a recovery investigation requires them.
Ignore unsolicited rescue messages. A person offering guaranteed recovery may use another portal to obtain more signatures or another payment.
Pause before accepting help advertised beneath a scam warning. Being the first person to respond does not make someone qualified or trustworthy.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Espresso itself being called a scam?
No. The warning applies to reported imitation claim portals. It is not an accusation against the genuine project or a recommendation to invest in its token.
Does an Espresso-branded domain prove a claim is official?
No. A project name inside a hostname can be chosen by an impersonator. Confirm the destination through independently reached official resources.
Did my wallet lose funds just because I connected?
Not necessarily. Review subsequent requests and actual activity. A connection, a spending approval, and a completed transfer must be assessed separately.
Can a zero-price claim still create risk?
Yes. An authorization can matter even without a conventional purchase price. Read its scope rather than relying on the page’s description of a free reward.
Why is disconnecting not always enough?
Separate token approvals may remain, and exposed recovery material can recreate wallet control. Your response should match the authority or secret actually disclosed.
Should I use another wallet to test the portal?
No. Do not introduce more assets or permissions into a suspected imitation. Verify the claim elsewhere instead of completing its workflow.
The Bottom Line
Avoid the reported fake Espresso claim portals. A recognizable crypto identity does not authenticate a website or justify authority over your existing assets.
If you already interacted, inspect the actual wallet requests, contain remaining access, and protect exposed secrets. Do not send another payment to make the promised allocation appear.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.