


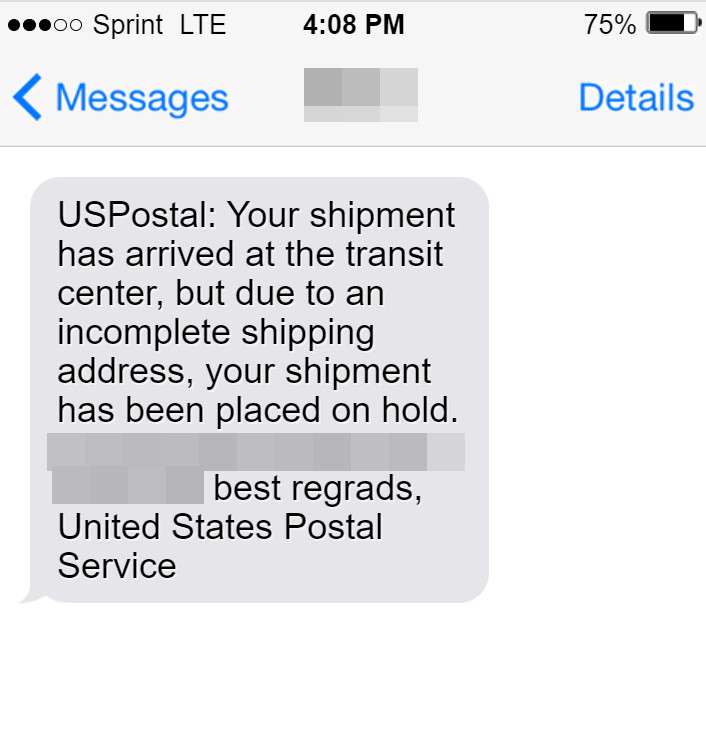
The USPS “Package Has Arrived At The Transit Center” smishing scam involves consumers receiving fraudulent text messages stating that a package addressed to them has reached a USPS transit facility but cannot be delivered due to an incomplete shipping address. The messages provide a link to supposedly update your address so USPS can dispatch your stuck package. However, the links actually connect to phishing websites designed to steal personal and financial information from victims who fall for this ruse.
Scam Overview
The USPS “Package Has Arrived At The Transit Center” scam starts with smartphone users receiving SMS messages stating that USPS received a package intended for delivery to them, but it is currently held up at a postal transit hub due to missing or inaccurate shipping address information.
The messages pretend to come from USPS service teams and are made to produce urgency about fixing the address issue quickly so the pending package can be released and shipped. The texts include a link where recipients can supposedly enter their updated address details for USPS to dispatch the stuck parcel.
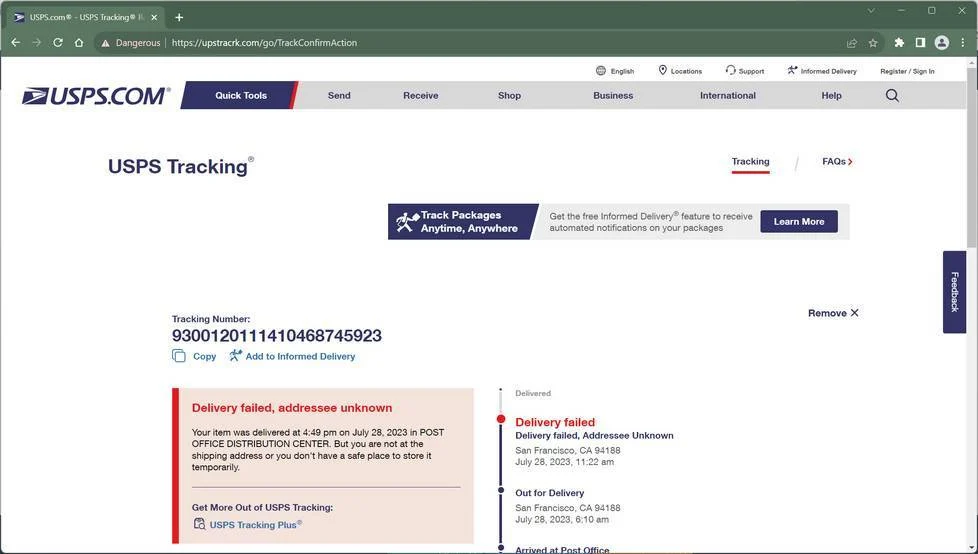
However, the link directs to convincing imposter websites that spoof official USPS domains. If users visit these fraudulent sites and enter any personal details into the forms, all that information gets harvested by scammers for identity theft, financial fraud, and sold online. No real undelivered package exists.
These fake USPS texts are blasted to random phone numbers across the U.S. hoping recipients will be duped into believing they have a pending postal item. By claiming sought-after packages are stuck, scammers prey on consumer worries over missing mail and online orders. The messages pressure urgency to provide the requested info quickly without scrutinizing the scam. Avoid getting hooked by learning to recognize these USPS smishing frauds.
How the Scam Works
The USPS “Package Has Arrived At The Transit Center” smishing scam unfolds in several key phases:
1. Receiving the Fraudulent Text
The first step involves a consumer receiving an unsolicited SMS message stating that USPS received a package for delivery to them but it’s currently held at a postal transit facility and unable to be shipped due to missing or inaccurate address details.
The message stresses urgency to update their address immediately so USPS can release and deliver the stuck package before it gets returned. A link is provided where the recipient can supposedly enter their correct address.
For example:
“USPS: Our records indicate we have a package for you that arrived at our facility but cannot be delivered due to an incomplete address label. Please tap here [malicious link] to update your address ASAP so we can dispatch your package! Thanks, USPS Shipping”
2. Clicking the Malicious Link
If the recipient clicks the link, instead of being directed to USPS.com as stated, they are taken to an elaborate fake website that mimics the real USPS site. The fraudulent site appears convincing at first glance with USPS branding, colors, graphics and navigation links.
However, the URL will be slightly altered like usps-packageassist211.com instead of an official domain. These scam sites are intentionally designed to deceive victims.
3. Submitting Personal Information
The phishing site will have forms prompting visitors to enter details like their full name, physical address, phone number, email address, package tracking numbers, and sometimes financial data or account logins.
The forms state this info is needed to validate, correct, or complete the shipping address attached to the package waiting at the transit facility. Users who provide details will have that sensitive data sent straight to scammers.
4. Malware Downloads
Some fake USPS smishing sites may also get visitors to download malware using tactics like:
- Fake pop-up windows prompting users to download files or enable permissions
- Push notifications to update security settings or enable “location-based” features
- Apps that must be installed to “track” the held package
Any downloads from the phishing site could infect devices with data-stealing malware.
How Stolen Information Gets Misused
Once scammers obtain victims’ details, they leverage it to conduct identity theft, financial fraud, and account compromise such as:
- Accessing financial accounts using phished login credentials
- Making unauthorized transactions using stolen banking info
- Opening fraudulent new lines of credit using the victim’s name and SSN
- Impersonating the victim to gather more sensitive info for identity theft
- Selling the data on dark web sites that traffic in stolen identities
- Monitoring infected devices via malware to silently gather more personal data
Just a single exposed detail can have cascading consequences enabling a wave of related fraud and damages.
What to Do if You Are Scammed
If you engaged with one of these fraudulent USPS texts and entered any personal information into the linked phishing site, take these steps immediately to limit the damages:
- Cease all activity and communication with the scam website. Do not provide any additional personal or financial details no matter what urgent pleas they make, as this will only expand access and damage.
- Contact your bank and financial services providers if you submitted any account usernames, passwords, credit card details, or other financial information. Request that they closely monitor your accounts for suspicious activity and enact heightened security protections like forced password resets and two-factor authentication. Ask about cancelling compromised cards and being issued new ones.
- If you entered a Social Security Number, request an initial fraud alert be placed on your credit reports with the three major credit bureaus. This flags your accounts for monitoring and requires verifying identity for new lines of credit. Consider a credit freeze instead which entirely blocks new credit in your name unless lifted. Check your credit reports for any signs of current identity theft.
- Report the phishing scam text sender phone number, website URLs, and any other details to the appropriate cybersecurity authorities. Key contacts include the USPS Postal Inspectors, FBI IC3, FTC, and Anti-Phishing Working Group (see below for reporting resources). Supplying information helps their investigations in tracking the scammers behind the smishing campaign and taking down the fraudulent sites.
- Run complete anti-malware scans on all your devices if you clicked any links, downloaded files, enabled permissions, or installed anything that the phishing site prompted you to. The site may have stealthily installed info-stealing malware without your knowledge. Thorough scans can uncover and remove malicious apps and files. Enable ongoing real-time protection.
- Change the passwords on any accounts for which you provided login credentials to the fake USPS site. Apply unique complex passwords and enable two-factor authentication everywhere possible. This blocks scammers from directly accessing compromised accounts.
- Place an extended fraud alert on your credit files if substantial amounts of personal information were potentially exposed, lasting one year. This makes it much harder for identity thieves to open new accounts in your name.
- For phished email addresses, update your account security settings to be as strict as possible, and mark unsolicited emails as spam to train filters. Disable account features that allow password resets via email confirmations, and enable alerts for login attempts.
- Carefully monitor bank and credit card statements, credit reports, account activity, and medical records for any signs of fraudulent access or activity. Remain vigilant for anything indicating misuse of your stolen information. Review your credit reports from Equifax, Experian, and TransUnion every few months.
- If tax-related information was exposed, inform the IRS. If medical or insurance information was stolen, notify your healthcare providers and insurance company.
- Update account information and points of contact with any services that may retain phished details on file such as phone number, home address, or email address. Create new contact points not known by scammers.
- If identity compromise is severe enough, consider an identity theft recovery service to help manage the restoration process and ensure maximum protections.
The quicker fraudulent activity can be identified following a phishing scam, the faster steps can be taken to freeze damages and regain control.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
What is the USPS “Package Has Arrived At The Transit Center” scam?
This is a smishing (SMS phishing) scam where victims receive a text message claiming to be from USPS stating that they have a package that arrived at a transit center but can’t be delivered due to an incorrect shipping address. The message contains a malicious link to a fake USPS site designed to steal personal information.
How does the scam work?
You receive a text purportedly from USPS saying your package arrived at their facility but can’t be shipped due to address issues. It instructs you to click a link and enter your info so they can deliver your package. But the link goes to a phishing site that steals your information.
What information are scammers trying to get?
Scammers want your full name, physical address, phone number, email address, passwords, financial information, and any other personal details they can phish by fooling you into entering it on their fake site.
What do scammers do with my information?
Scammers use your details for identity theft, accessing accounts, and financial fraud. They may sell it online or use it themselves to impersonate you and commit crimes in your name. Your data is now in the hands of criminals.
Why does USPS need me to update address details online?
USPS does not contact customers via unsolicited texts with links to non-USPS websites. They communicate postal issues through official channels only after you initiate contact. Any SMS messages about an address update needed to deliver a package are scams.
How can I tell if a USPS notification is legitimate?
Real USPS texts will come from a verified USPS number only. They will never contain links outside of USPS.com or request personal details to correct address problems. Contact USPS directly if you have delivery concerns.
I entered my details, what now?
If you shared any personal or financial information, immediately contact those providers to lock down accounts. Watch for fraudulent activity in your name. Enable credit freezes and fraud alerts. Scan devices for malware and reset all account passwords as a precaution.
Can USPS help me if I was scammed?
Unfortunately USPS has limited ability to aid scam victims since the fake texts/sites are not within their systems. They may try taking down fraudulent domains impersonating them but cannot restore compromised data. Managing fallout is up to you.
How can I avoid future scams?
Be wary of texts claiming to be from USPS, UPS, FedEx or others with links requiring you to enter any personal data. Verify the sender’s number first. Never click links or provide information without confirming validity on official sites. Use unique passwords and enable two-factor authentication where possible.
Conclusion
The USPS “Package Has Arrived At The Transit Center” smishing scam aims to trick anxious consumers into providing personal data under the guise of a postal service notification. Scrutinize unsolicited texts claiming you must enter details on linked sites to receive pending packages carefully before responding. Never click links or provide information without explicitly verifying the sender and domain are legitimate. We can disrupt these smishing scammers by being alert to signs of phishing and refusing to supply the personal details they seek to steal. Don’t let your data get caught up in transit to fraudsters.
Reporting Contacts
- USPS Postal Inspectors: uspis.gov
- FBI IC3: ic3.gov
- Federal Trade Commission: reportfraud.ftc.gov
- Anti-Phishing Working Group: apwg.org
- SMS Short Code 7726 (Spell SPAM)

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.