App Review Avast Free (Hardened Mode) vs Ransominator

It is advised to take all reviews with a grain of salt. In extreme cases some reviews use dramatization for entertainment purposes.
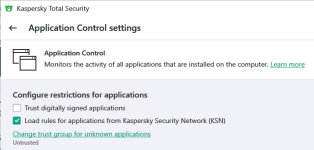
And it can be mimicked with the existing Application Control by setting unknown applications to 'Untrusted'

There is anyway to create a rule for that or do i need to set unknown applications as 'Untrusted' individually. I couldn't find any way to create a rule that could set all unknow apps as untrusted by default
 
There is anyway to create a rule for that or do i need to set unknown applications as 'Untrusted' individually. I couldn't find any way to create a rule that could set all unknow apps as untrusted by default
Open "Protection" components of Kaspersky. Click on Application Control. There in this page this option is available.
 
i tested this sample with Comodo internet security latest version with two different settings. the first one: i changed the auto containment to block unknown files and with this settings Comodo blocked it immediately. the second one: i kept the default settings (Run virtually Partially limited) and the sample contained in the sandbox and the text file appeared but the files didn`t encrypted and when i closed the text file, it disappeared from the sand box.
 
There is anyway to create a rule for that or do i need to set unknown applications as 'Untrusted' individually. I couldn't find any way to create a rule that could set all unknow apps as untrusted by default

1587970810955.png
 
Avast has security flaws, I don't expect it to stop a ramsonware that even kaspersky couldn't, lol kkk, it's a very weak antivirus.

Its always been decent, they have large userbase, they have the cashflow for everything with all that bloat/ paid services

Its top product, its far from weak,,,,some people just dont like that they datamine so much , but that doesnt mean their antivirus is lacking against others
 
Did someone submit it or was this automatic?

Kaspersky was also super aggressive in my testing at the cloud having a reaction. I had to recompile my sample with a bit more obfuscation midway through testing because it started getting blocked statically on other VMs after I clicked the button saying to undo.

No other AV I tested did this -- I suspect they required more than one or two hosts detecting a binary.
Not in the endpoint version you can be patient zero with never seen malware on just one endpoint and get a detection super fast .
The speed of the Russians is incredible!
Good to hear the speed of the non endpoint protection is fast as well !
 
Did someone submit it or was this automatic?

Kaspersky was also super aggressive in my testing at the cloud having a reaction. I had to recompile my sample with a bit more obfuscation midway through testing because it started getting blocked statically on other VMs after I clicked the button saying to undo.

No other AV I tested did this -- I suspect they required more than one or two hosts detecting a binary.
Maybe both automatic and manual submission! I'm not sure because I found it here last night and I didn't submit it: https://opentip.kaspersky.com/C92E226D39B612785F8CE5074DA03DEEC6618E5C9AAEB4046AD153133B027805/
Now you would see in that report that in the extracted files category Kaspersky found one Adware but that wasn't there for some reason when I checked the first time. It appeared there later. You're maybe right about it requiring more than one host to detect a binary. I think most of the initial UDS based detection are hash based. KSN blacklists this suspicious items with hash as a first line of defense to protect other users. The detection here was "UDS:Hoax.Win64.FakeRansom.a" Here "a" surely refers to variants so if the sample is slightly modified then Kaspersky might not detect it at first launch on a new PC but later would create another UDS signature and maybe this time the variants would be different so something like "b" instead of "a". It may continue to be like this till a malware analyst personally analyze and create a proper signature. I've seen similar behavior for Microsoft for some other samples.
Interestingly Bitdefender and ESET has now created signature for this sample: VirusTotal
Even Microsoft but I ran it in sanboxie with Windows Defender installed and WD didn't stop the sample from executing instead waited for me to open Windows Security and then I had to manually chose options but by that time the sample already did its job. This is detected by their cloud as some not so dangerous PUP it seems.
Edit: WD now detects it with a different signature: "Trojan:Win32/Wacatac.C!ml"
 
Last edited:
i tested this sample with Comodo internet security latest version with two different settings. the first one: i changed the auto containment to block unknown files and with this settings Comodo blocked it immediately. the second one: i kept the default settings (Run virtually Partially limited) and the sample contained in the sandbox and the text file appeared but the files didn`t encrypted and when i closed the text file, it disappeared from the sand box.
Thanks for test Comodo.

So even in the default settings Comodo protected the system. As i suspected
 
Last edited:
Has Avast already created 'don't sell my personal information' mode? LOL
Do you have state secrets? They all get your info/data, don't be naive… The difference is either you're aware or not, if they tell you about it or not and if someone found out or not. Windows does it, Facebook does it, Google... If you start caring for that you won't be able to get online.
 
  • +Reputation
Reactions: stefanos
Looks like I maybe using Avast as my next AV after my subscription for F-Secure runs out. Is Avast light on a system at all? Haven't used it in ages. If one could provide an SS regarding the CPU & disk usage that would be great.

~LDogg
 
Looks like I maybe using Avast as my next AV after my subscription for F-Secure runs out. Is Avast light on a system at all? Haven't used it in ages. If one could provide an SS regarding the CPU & disk usage that would be great.

~LDogg
I remember Avast Free 2019 when installed with minimal components being really light not as ESET but lighter than anything else, what concerns me is their data oriented business model.