

Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Installation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Advanced Plus Security wat0114 security config 2021
- Thread starter wat0114
- Start date
CSC Archive
107 Replies
29,001 Views
- Last updated
- Jun 12, 2021
- Main use of this computer
- For home and private use
- Operating system
- macOS 15 Sequoia
- OS version and support details
- MX-21
- On-device encryption
- Device sign-in security
- Windows Hello PIN or biometric sign-in (face / fingerprint / Touch ID)
- Security updates
- Check for updates and Notify
- User Account Control (UAC)
- Always notify
- Smart App Control
- Network firewall
- Real-time protection
- Windows Defender, OSArmor
- Device firewall
- Microsoft Defender Firewall
- Custom security settings
Malwarebytes Firewall Interface for Windows Defender Firewall, Added all but Adobe Reader Firewall Hardening measures in Hard_Configurartor, several Group Policy settings enabled.
SRP - Default-deny
-Hard_Configurator_6_latest: High setting
-Full BitLocker encrypted system partition.
-BIOS: passworded, Memory Protection, Intel Virtualization & Intel VT-d- enabled
-Hyper-V enabled
- Periodic malware scanners
- VirusTotal
- Malware sample testing
- I do not participate in malware testing
- Browsers and extensions
- Firefox latest (primary), MS Edge
-uBlockO
-CSS Exfil
-LocalCDN
- Secure DNS
Cloudflare
Quad9
- Desktop VPN
- None
- Password and passkey manager
Lastpass and Browser's built-in
Keepass free
- Maintenance tools
- Occasional system images using IFW (Image for Windows) and Disk cleanup using built-in Disk cleaner
- File and photo backups
- -Separate, encrypted partition
-USB Drive
- System recovery
- IFW (Image for Windows)
- Usage and exposure
- Visiting familiar websites
- Visiting unknown or untrusted websites
- Opening email attachments
- Streaming audio/video content from trusted sites or paid subscriptions
- Streaming from untrusted sites
- Computer specs
- Device name Lenovo-E580
Processor Intel(R) Core(TM) i5-7200U CPU @ 2.50GHz 2.70 GHz
Installed RAM 8.00 GB (7.86 GB usable)
System type 64-bit operating system, x64-based processor
- Feedback preference
Detailed suggestions and alternatives welcome

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran

Oops, sorry, I mean Configure Defender Protection level within H_C to High. I forgot CF is built into H_C.????
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Oops, sorry, I mean Configure Defender Protection level within H_C to High.
Which H_C's setting profile do you use for now?
Which H_C's setting profile do you use for now?
Do you mean from the main interface?
EDIT
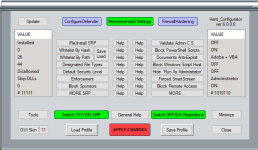
I chose Recommended Settings if that's what you mean.
EDIT 2
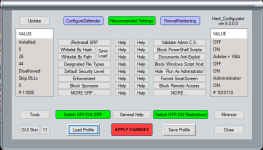
So Andy, you have helped me discover predefined profiles. I went to the Manual and found out about them. I just applied: Windows_10_Strict_Recommended_Settings.hdc. I had always thought the Load Profile button was to load profiles saved only by the user - not to also load predefined profiles included with the utility. I had simply hit the Recommended Settings button before.
Thanks!
Last edited:
I forgot to mention, I also added many Firefox about:config settings from Yet Another Firefox Hardening Guide
Thanks again to @oldschool for your recent post on this.
Thanks again to @oldschool for your recent post on this.

With Microsoft Defender and Hard_Configurator at your settings you could easily go without OSA. You might want to check out the impressive results in these links:
Malware Hub Report - Hard Configurator - march 2019 report
Malware Hub Report - Hard Configurator - april 2019 report
Malware Hub Report - Hard Configurator - may 2019 report
https://malwaretips.com/search/276925/
Malware Hub Report - Hard Configurator - march 2019 report
Malware Hub Report - Hard Configurator - april 2019 report
Malware Hub Report - Hard Configurator - may 2019 report
https://malwaretips.com/search/276925/
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Do you mean from the main interface?
EDIT
I chose Recommended Settings if that's what you mean.
View attachment 261613
EDIT 2
So Andy, you have helped me discover predefined profiles. I went to the Manual and found out about them. I just applied: Windows_10_Strict_Recommended_Settings.hdc. I had always thought the Load Profile button was to load profiles saved only by the user - not to also load predefined profiles included with the utility. I had simply hit the Recommended Settings button before.
View attachment 261614
Thanks!
With these settings you have to remember that:
- Many application auto-updates will be blocked. You have to update these applications manually after switching off the SRP temporarily (<Switch ON/OFF SRP> green button). The details are described in the H_C FAQ.
- In these settings "Install By Smartscreen" works with high privileges, so it should not be used on SUA. When using these settings on SUA the application installations should be done like in point 1. If not then some applications will install files on administrator account instead of the standard user account.
There is no problem when using only one account (default Administrator account).
Last edited:
With Microsoft Defender and Hard_Configurator at your settings you could easily go without OSA. You might want to check out the impressive results in these links:
Malware Hub Report - Hard Configurator - march 2019 report
Malware Hub Report - Hard Configurator - april 2019 report
Malware Hub Report - Hard Configurator - may 2019 report
https://malwaretips.com/search/276925/
Those are indeed impressive results. Thanks for sharing. I'll keep OSA installed at least until my license expires in three months, then I'll decide whether to remove it.
With these settings you have to remember that:
- Many application auto-updates will be blocked. You have to update these applications manually after switching off the SRP temporarily (<Switch ON/OFF SRP> green button). The details are described in the H_C FAQ.
- In these settings "Install By Smartscreen" works with high privileges, so it should not be used on SUA. When using these settings on SUA the application installations should be done like in point 1. If not then some applications will install files on administrator account instead of the standard user account.
There is no problem when using only one account (default Administrator account).
This not only works for me, but I like the restrictions better than the Recommended settings

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Oldschool is right that OSA is not necessary in those settings. Such a setup would be overkill for most home users. Anyway, If you do not encounter any problems and do not feel the setup inconvenient, then there is no reason to change it.
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
... I like the restrictions better than the Recommended settings
The Recommended Settings are in fact better for most home users. Anyway, I can understand that you can feel that more restrictive settings can be 'better' for you.
The Recommended Settings are in fact better for most home users. Anyway, I can understand that you can feel that more restrictive settings can be 'better' for you.
There seems to be no limit to the ingenious level of attack methods malware authors create. I guess my overkill setup is to potentially prevent a future attack that might bypass a setup that is currently adequate for home users. I could be out to lunch on this theory, but I guess I like the additional insurance policy, even though it may never be needed.
Haha, I was asked this same question back in post #28 of this thread. A long discussion ensued. Basically I can't remember specifically why I enabled it, it was so long ago.
F
ForgottenSeer 92963
Are you using Application Guard for Edge? (you have a Windows Pro, so it comes with the OS).
Are you using Application Guard for Edge? (you have a Windows Pro, so it comes with the OS).
No I just use Firefox with hardened about:config settings, some Privacy settings enabled, with UBO and LocalCDN extensions.
Also several Exploit protection settings enabled in Defender for Firefox.
Last edited:
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
There seems to be no limit to the ingenious level of attack methods malware authors create. I guess my overkill setup is to potentially prevent a future attack that might bypass a setup that is currently adequate for home users. I could be out to lunch on this theory, but I guess I like the additional insurance policy, even though it may never be needed.
Yes, that is true. I think that in your case this setup is simply fun or kind of a hobby. It is safe and it is OK if you like it.
Be safe.
Last edited:
Well, LOL, I reverted to Recommended settings due to being unable to launch OneDrive, and for a lesser reason, the %TEMP% directory is restricted by the SRP rules.
Besides, the latter is nicely under surveillance from OSA
EDIT
and yes I realize scripting is likely going to trigger first in this type of exploit, which H_C will stop.
Besides, the latter is nicely under surveillance from OSA
EDIT
and yes I realize scripting is likely going to trigger first in this type of exploit, which H_C will stop.
Last edited:
Recently browsing
Members who viewed this thread in the last 5 minutes
You may also like...
Continue exploring the conversation.
-
 8
- Chatbots and AI
- Started by annaegorov
-
 7Serious Discussion Data Collection Core Principles (Security Software)
- Privacy and encryption
- Started by Trident
-
7Serious Discussion Deep Research: Trend Micro VSAPI and ATSE Release History and Modus Operandi
- Trend Micro
- Started by Trident
-
413Software Review McAfee Protection (Plus Plans, Total Protection, LiveSafe)
- Written Reviews - Security and Privacy
- Started by Trident
-
 39
- Guides - Privacy & Security Tips
- Started by Andy Ful