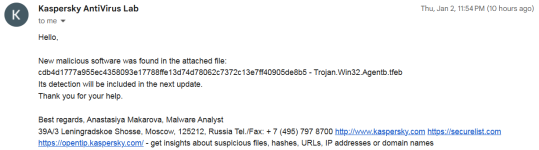
well Kaspersky's own analyst doesn't take VHO detections seriously. That VHO detection has been updated.Hum VHO: Very Harmful Object


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
well Kaspersky's own analyst doesn't take VHO detections seriously. That VHO detection has been updated.Hum VHO: Very Harmful Object

Maybewell Kaspersky's own analyst doesn't take VHO detections seriously. That VHO detection has been updated.


Welcome to MT. Please remember to stay safe, not paranoid!I came to this forum looking for Antivirus recommendations, and I had never decided to create an account until today, to thank Shadowra and everyone else for their reviews, comments on AVs


If he/she became paranoid what to do?Welcome to MT. Please remember to stay safe, not paranoid!


Of course, but not for that reason, I think it is because it belongs to the Early Detection System, populated via the cloud as soon as possible, but They finally end creating an specific fixed signature.well Kaspersky's own analyst doesn't take VHO detections seriously. That VHO detection has been updated.

In this video, we compare 8 paid antivirus programs.
The aim is to see how effective they are, and rank them from worst to best.
Please note:
- the antiviruses are already ranked in the video, I've taken into account Web blocking, the reaction to an attack, my malware pack and how the antivirus will defend itself.
- Please be courteous and respect my ranking. Filming took over 9 hours and 2 hours of preparation.
- the winning antivirus goes straight to the final, episode 4.
- A 3rd part has been added with enterprise antivirus, delaying the video schedule.
- all antivirus are default, I've only activated IF NECESSARY some options that the editor hasn't activated (heuristics, PUP detection etc.)
- the protocol is the same.
K7 Ultimate is an Indian antivirus that is beginning to make a name for itself.
The interface has evolved and welcomes us with a beautiful blue, which I like, the interface looks new while the old one was starting to date ...
Web: 10/10 , K7 blocks all malicious links.
Crack: 1/1 , blocked by K7
Pack : 33 out of 215 . K7 has improved a lot on behavioral blocking (the MAT effect?) but still lags behind on more direct attacks like scripts or other injectors...
In the end, an infection drops random files into Document. K7 deletes them, but this creates a loop.
Too bad, it's in 8th place.
Trend Micro is a well-known Japanese antivirus, especially in the corporate and school sectors.
For a long time now, Trend has been providing a fully automatic, 100% Cloud solution.
It's suitable for novices because... you can't configure anything! (but I've customized its interface, Japan obliges
Web: 10/10 , Trend blocks all links!
Crack: Trend says it doesn't know the file and recommends deleting it, which I do. 1/1
Pack: Remains 18 out of 215 . Trend continues its efforts to detect malware, but still relies too much on its reputation system. It's good because it prevents executions, but it doesn't give any information other than to delete.
In the end, 2 scripts pass without reaction.
It ranks 7th. Despite good performance, relying too much on reputation and providing no information can annoy people.
ZoneAlarm is an Israeli company formerly known for its famous firewall.
Previously using Kaspersky, it now uses Sophos in addition to its own Cloud engine.
It's also the longest, taking around 40 minutes to install! (because ZA wanted to install 6 Microsoft programs.... )
Web: ZoneAlarm's Web protection is very poor. It's called Anti-Bot and only reacted twice.
But it intercepted all downloads! (9/9)
On the other hand, it analyzes by emulating the file, which is relatively time-consuming...
Crack: ZoneAlarm blocks installation. 1/1
Pack: Remains 17 out of 215. Zone is quick to scan, but takes a very long time to clean up, taking exactly 1 hour!
Because ZoneAlarm bombards with alerts, doing 1 after the other...
At launch, ZoneAlarm reacts rather late, but ends up destroying the installation attempts. In the end, only one script remains active.
It's in 6th place, so a little reactivity would be in order!
Emsisoft is undoubtedly one of the best-known anti-malware products.
Formerly a-Squared and running under IKARUS, Emsisoft adopted the Bitdefender engine several years ago.
However, the installation system has been modified. You need to create a comtpe and then download the software. The license will be added to an online account. A bit like Sophos or Bitdefender…
Web : 9/9 . Emsisoft blocks all links, one link is dead.
Crack: 1/1 . Blocked by the Emsisoft Cloud.
Pack: 15 left out of 215.
At first, I was very scared... not seeing Emsisoft react.
Then, the antivirus started to react and sweep away the attacks one after the other. A lack of reactivity is noted.
The machine is back to normal, but Emsisoft still needs to work on its reactivity.
Kaspersky is a Russian antivirus company widely known and respected in the security world.
In this version, I opt for the Plus version, which includes everything you need to be protected.
I've had to create exceptions for ProcessHacker, which doesn't like it...
Web : 9/9 . Kaspersky blocked everything, one link died.
Crack: Kaspersky detects malicious behavior and deletes the file. 1/1
Pack: Remains 9 out of 215. Excellent responsiveness from Kaspersky, even blocking files I launch!
But LummaStealer gets the better of Kaspersky and doesn't react.
It's a shame.
Formerly a hated antivirus like Norton, McAfee made a big comeback last year by completely redeveloping their application.
Gone is the heavy McAfee, and in comes the new McAfee, lightweight and entirely cloud-based!
And it's paying off! It's much lighter.
I've agreed to install McAfee WebAdvisor.
Web: 9/9, McAfee blocks all links. Only one is dead.
Crack: McAfee blocks installation. 1/1
Pack: Remains 8 out of 215.
McAfee surprised me a lot, because it has really improved its engine and finally knows how to defend itself properly!
It's not always reactive to scripts, which takes it out of 2nd place, but it does block payload downloads.
A little effort on scripts, but it's heading in the right direction!
Bitdefender, often Kaspersky's competitor, is a well-known Romanian antivirus.
The software retains its reputation, while boasting a polished interface.
I've activated Ransomware remediation and protection against crypto-jacking.
Web: 9/9, Bitdefender blocks all links. A slight slowdown was noted.
Crack: 1/1, Bitdefender blocks the dropper.
Pack: Remains 10 out of 215. Bitdefender shines and starts blocking the malware I'm running. It almost fell for Tank's fake game because PowerShell commands were in progress, but Bitdefender didn't let itself be fooled!
Only 1 piece of malware remains at the end, but Bitdefender cuts off its connection to the server.
ESET is a Slovakian antivirus, much appreciated by gamers for its lightness.
It's also a highly configurable antivirus!
Personally, I leave it at default.
Web: 10/10, ESET has blocked all links at source.
Crack: 1/1, ESET has blocked all installations.
Pack: 12 out of 215.
During runtime, Eset noticed a LummaStealer attack, impressive because the malware was unknown! In fact, it detected the pattern during launch.
On another piece of malware attempting to install itself, here ESET uses LiveGird to block the installation and remove the threat.
Congratulations, Eset is finally improving its Cloud network!
The machine is now infection-free, and deserves its 1st place.
Winner : Eset

 www.av-comparatives.org
As I wrote earlier, it turned out to be a good test. However, that's no reason for anyone to discontinue their favourite product. User awareness is more important. For me, Kaspersky is still my favourite product. That's one thing I would like to see them do, make their product lighter and smoother. Eset is also a very good product, but it bleeds under really heavy load. Just because of what the forum mates have already described.
IMO Ver. 9 of ESET was by far the best.Agreed. There's so much 'crud' in there on the standard version that I don't want.
Disk cleanup, app management, email address checker, speed up your pc, software update checker etc.
I'd love them to go back to the old school IS days. AV and firewall only. Less to go wrong!
I was talking about KasperskyIMO Ver. 9 of ESET was by far the best.

Exactly why I retired from testing and commenting, people are to aggressive and pushing, I noticed I sometimes got dragged along with it and I am fed up with all the aggressive nonsense those so called experts here mention, with this I do not mean the good old testers like @Shadowra , @harlan4096 , @Trident and many more but the new ones with the stupid questions and the big mouths.Surprised me that the topic isn't Comodo even this time as here we see another forum thread where someone is unable for self-control what shouldn't said nor written.
For better understanding, just quoted a part of the Forum Rules:
Forum Rules
The following guidelines outline the rules for participating in our community forums.malwaretips.com
My mistake...I was talking about Kaspersky
 Sorry

Hello,@Trident you're an expert on checkpoint
It is already kinda aggressive through behavioural guard and it gets more and more aggressive every day. There is still more to be desired (there always is).I was wondering why can't they make script detection more aggressive for consumers as they usually dont make much use of scripts and does zone alarm send local scripts to emulation ?
At Check Point, all system objects have reputation. Object can be file, folder, registry key (service which as well is in the registry), shortcut, memory object (such as named pipe) and URL/IP address.How does it decide what local files to send to emulation ?
Welcome back mate. Happy New Year !Hello,
I am not very active on here nowadays but let me reply to these questions.
It is already kinda aggressive through behavioural guard and it gets more and more aggressive every day. There is still more to be desired (there always is).
Local scripts that you create yourself are generally not emulated.
Local scripts that are dropped by applications with unfavourable reputation are emulated, which leads to the next point.
At Check Point, all system objects have reputation. Object can be file, folder, registry key (service which as well is in the registry), shortcut, memory object (such as named pipe) and URL/IP address.
Possible reputations are safe, malicious, suspicious, unknown.
So, files such as downloads will always be emulated, as long as the format is supported.
The file level emulation decides based on the reputation of the object — objects proven as safe are not emulated, objects proven malicious are removed/blocked. It is only suspicious and unknown objects that need more digging around.
Now to the fake stores, Zero Phishing is not yet equipped with any models that can detect fake stores. It does block everything that involves brand impersonation, but when the brand itself is scam… can’t do anything.
In this relation, adding additional extensions might help, but unfortunately none of them offer perfect protection against scam websites and stores. They can sometimes be difficult even for the most senior content analyst, let alone an extension or an AI model.
Fake stores seems like an impossible thing to fully combat but actually I have seen checkpoint zero pishing a few times able to detect even some random fake pets shops and all kinds of fake stores wich did surprise me as it's not trained on much fake storesHello,
I am not very active on here nowadays but let me reply to these questions.
It is already kinda aggressive through behavioural guard and it gets more and more aggressive every day. There is still more to be desired (there always is).
Local scripts that you create yourself are generally not emulated.
Local scripts that are dropped by applications with unfavourable reputation are emulated, which leads to the next point.
At Check Point, all system objects have reputation. Object can be file, folder, registry key (service which as well is in the registry), shortcut, memory object (such as named pipe) and URL/IP address.
Possible reputations are safe, malicious, suspicious, unknown.
So, files such as downloads will always be emulated, as long as the format is supported.
The file level emulation decides based on the reputation of the object — objects proven as safe are not emulated, objects proven malicious are removed/blocked. It is only suspicious and unknown objects that need more digging around.
Now to the fake stores, Zero Phishing is not yet equipped with any models that can detect fake stores. It does block everything that involves brand impersonation, but when the brand itself is scam… can’t do anything.
In this relation, adding additional extensions might help, but unfortunately none of them offer perfect protection against scam websites and stores. They can sometimes be difficult even for the most senior content analyst, let alone an extension or an AI model.
Generally to identify scam stores, people would have to look for reviews. Many of these reviews could be fake, so 5-star reviews from people who registered solely to leave them are very suspicious. The truth will be in the 1 and 2 star reviews always.Fake stores seems like an impossible thing to fully combat but actually I have seen checkpoint zero pishing a few times able to detect even some random fake pets shops and all kinds of fake stores wich did surprise me as it's not trained on much fake stores
Symantec uses reputation only on certain files and calculates it differently. For Symantec, you as a user make a difference, so if you come across a lot of malware, all files on your system, even if safe, have less of a “weight” to the calculation algorithm, compared to a user that only downloads safe files. Next, it looks at factors such as prevalence.Interesting how they use reputation well and actually although Symantec endpoint protection uses reputation etc as well but unfortunately unlike checkpoint it has higher false positives ratio from my experience
That’s how the Zero Phishing is designed, the analysis is rather complicated so it starts when you interact with a form. If you don’t interact with the site, then it can’t steal your credentials and cloud resources can be saved.they should automatically scan web forms like .css rather then only scanning when interacting with the web form like
It is possible to bypass pretty much all ransomware protections out there. The full product with all capabilities is difficult to bypass.cruel sister showed it's possible to bypass the ransomware protection in zone alarm so that has to be improved
I had investigated how different extensions deal with scanning web forms only checkpoint looks for interaction of the actual .css wich is although superior method to detect pishing with much less noise sent to checkpoint as telemetry as wellGenerally to identify scam stores, people would have to look for reviews. Many of these reviews could be fake, so 5-star reviews from people who registered solely to leave them are very suspicious. The truth will be in the 1 and 2 star reviews always.
Symantec uses reputation only on certain files and calculates it differently. For Symantec, you as a user make a difference, so if you come across a lot of malware, all files on your system, even if safe, have less of a “weight” compared to a user that only downloads safe files. Next, it looks at factors such as prevalence.
Check Point reputation comes from internal and external feeds and to a huge extent, from the emulation.
Symantec does not monitor reputation of other system objects, apart from files and connections.
That’s how the Zero Phishing is designed, the analysis is rather complicated so it starts when you interact with a form. If you don’t interact with the site, then it can’t steal your credentials and cloud resources can be saved.
It is possible to bypass pretty much all ransomware protections out there. The full product with all capabilities is difficult to bypass.
She used a targeted ransomware and zone alarm wich is made specifically for low false positivesGenerally to identify scam stores, people would have to look for reviews. Many of these reviews could be fake, so 5-star reviews from people who registered solely to leave them are very suspicious. The truth will be in the 1 and 2 star reviews always.
Always use trusted websites and stores that have built a reputation over the years.
Symantec uses reputation only on certain files and calculates it differently. For Symantec, you as a user make a difference, so if you come across a lot of malware, all files on your system, even if safe, have less of a “weight” to the calculation algorithm, compared to a user that only downloads safe files. Next, it looks at factors such as prevalence.
Check Point reputation comes from internal and external feeds and to a huge extent, from the emulation.
Symantec does not monitor reputation of other system objects, apart from files and connections.
The Symantec reputation Insight “thingy” is designed to be a fully unsupervised system.
That’s how the Zero Phishing is designed, the analysis is rather complicated so it starts when you interact with a form. If you don’t interact with the site, then it can’t steal your credentials and cloud resources can be saved.
It is possible to bypass pretty much all ransomware protections out there. The full product with all capabilities is difficult to bypass.
It uses a lot more than just honeypots, the CP Harmony one is always newer. Anti-ransomware can be configured in detail in Harmony, you can increase the size of the database and change the backup interval and file formats.Actually partially reminds of how surf right designed their anti ransomware but checkpoint is more advanced and uses honeypots as well but eh still not perfect
Members who viewed this thread in the last 5 minutes